This view organizes weaknesses around concepts that are frequently used or encountered in hardware design. Accordingly, this view can align closely with the perspectives of designers, manufacturers, educators, and assessment vendors. It provides a variety of categories that are intended to simplify navigation, browsing, and mapping.
Audience
Stakeholder
Description
Hardware Designers
Hardware Designers use this view to better understand potential mistakes that can be made in specific areas of their IP design. The use of concepts with which hardware designers are familiar makes it easier to navigate.
Educators
Educators use this view to teach future professionals about the types of mistakes that are commonly made in hardware design.
Relationships
The following graph shows the tree-like relationships between
weaknesses that exist at different levels of abstraction. At the highest level, categories
and pillars exist to group weaknesses. Categories (which are not technically weaknesses) are
special CWE entries used to group weaknesses that share a common characteristic. Pillars are
weaknesses that are described in the most abstract fashion. Below these top-level entries
are weaknesses are varying levels of abstraction. Classes are still very abstract, typically
independent of any specific language or technology. Base level weaknesses are used to
present a more specific type of weakness. A variant is a weakness that is described at a
very low level of detail, typically limited to a specific language or technology. A chain is
a set of weaknesses that must be reachable consecutively in order to produce an exploitable
vulnerability. While a composite is a set of weaknesses that must all be present
simultaneously in order to produce an exploitable vulnerability.
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns)
Weaknesses in this category are root-caused to defects that arise in the semiconductor-manufacturing process or during the life cycle and supply chain.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Insufficient Technical Documentation
- (1059)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1059(Insufficient Technical Documentation)
The product does not contain sufficient
technical or engineering documentation (whether on paper or
in electronic form) that contains descriptions of all of the
relevant software/hardware elements of the product.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Semiconductor Defects in Hardware Logic with Security-Sensitive Implications
- (1248)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1248(Semiconductor Defects in Hardware Logic with Security-Sensitive Implications)
The security-sensitive hardware module contains semiconductor defects.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Scrubbing of Sensitive Data from Decommissioned Device
- (1266)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1266(Improper Scrubbing of Sensitive Data from Decommissioned Device)
The product does not properly provide a capability for the product administrator to remove sensitive data at the time the product is decommissioned. A scrubbing capability could be missing, insufficient, or incorrect.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Product Released in Non-Release Configuration
- (1269)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1269(Product Released in Non-Release Configuration)
The product released to market is released in pre-production or manufacturing configuration.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Device Unlock Credential Sharing
- (1273)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1273(Device Unlock Credential Sharing)
The credentials necessary for unlocking a device are shared across multiple parties and may expose sensitive information.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Unprotected Confidential Information on Device is Accessible by OSAT Vendors
- (1297)
1194(Hardware Design) >
1195(Manufacturing and Life Cycle Management Concerns) >
1297(Unprotected Confidential Information on Device is Accessible by OSAT Vendors)
The product does not adequately protect confidential information on the device from being accessed by Outsourced Semiconductor Assembly and Test (OSAT) vendors.
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Security Flow Issues
- (1196)
Weaknesses in this category are related to improper design of full-system security flows, including but not limited to secure boot, secure update, and hardware-device attestation.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
DMA Device Enabled Too Early in Boot Phase
- (1190)
1194(Hardware Design) >
1196(Security Flow Issues) >
1190(DMA Device Enabled Too Early in Boot Phase)
The product enables a Direct Memory Access (DMA) capable device before the security configuration settings are established, which allows an attacker to extract data from or gain privileges on the product.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Power-On of Untrusted Execution Core Before Enabling Fabric Access Control
- (1193)
1194(Hardware Design) >
1196(Security Flow Issues) >
1193(Power-On of Untrusted Execution Core Before Enabling Fabric Access Control)
The product enables components that contain untrusted firmware before memory and fabric access controls have been enabled.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Logic with Insecure De-Synchronization between Control and Data Channels
- (1264)
1194(Hardware Design) >
1196(Security Flow Issues) >
1264(Hardware Logic with Insecure De-Synchronization between Control and Data Channels)
The hardware logic for error handling and security checks can incorrectly forward data before the security check is complete.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Access Control for Volatile Memory Containing Boot Code
- (1274)
1194(Hardware Design) >
1196(Security Flow Issues) >
1274(Improper Access Control for Volatile Memory Containing Boot Code)
The product conducts a secure-boot process that transfers bootloader code from Non-Volatile Memory (NVM) into Volatile Memory (VM), but it does not have sufficient access control or other protections for the Volatile Memory.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Mutable Attestation or Measurement Reporting Data
- (1283)
The register contents used for attestation or measurement reporting data to verify boot flow are modifiable by an adversary.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Ability to Patch ROM Code
- (1310)
1194(Hardware Design) >
1196(Security Flow Issues) >
1310(Missing Ability to Patch ROM Code)
Missing an ability to patch ROM code may leave a System or System-on-Chip (SoC) in a vulnerable state.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Immutable Root of Trust in Hardware
- (1326)
1194(Hardware Design) >
1196(Security Flow Issues) >
1326(Missing Immutable Root of Trust in Hardware)
A missing immutable root of trust in the hardware results in the ability to bypass secure boot or execute untrusted or adversarial boot code.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Security Version Number Mutable to Older Versions
- (1328)
1194(Hardware Design) >
1196(Security Flow Issues) >
1328(Security Version Number Mutable to Older Versions)
The security version number in the hardware product is mutable, resulting in the ability to downgrade (roll-back) the boot firmware to vulnerable code versions.
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Integration Issues
- (1197)
1194(Hardware Design) >
1197(Integration Issues)
Weaknesses in this category are those that arise due to integration of multiple hardware Intellectual Property (IP) cores, from System-on-a-Chip (SoC) subsystem interactions, or from hardware platform subsystem interactions.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Child Block Incorrectly Connected to Parent System
- (1276)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues)
Weaknesses in this category are related to features and mechanisms providing hardware-based isolation and access control (e.g., identity, policy, locking control) of sensitive shared hardware resources such as registers and fuses.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
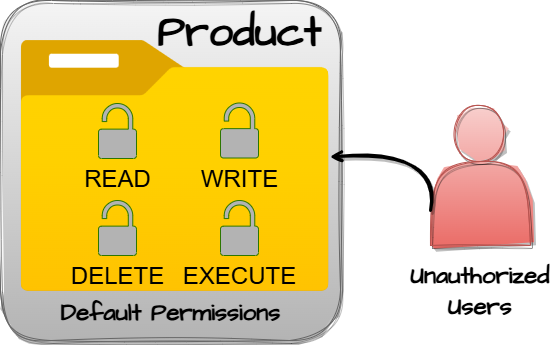
Incorrect Default Permissions
- (276)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
276(Incorrect Default Permissions)
During installation, installed file permissions are set to allow anyone to modify those files.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Unintended Proxy or Intermediary
- (441)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
441(Unintended Proxy or Intermediary)
The product receives a request, message, or directive from an upstream component, but the product does not sufficiently preserve the original source of the request before forwarding the request to an external actor that is outside of the product's control sphere.
Confused Deputy
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Isolation of Shared Resources on System-on-a-Chip (SoC)
- (1189)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1189(Improper Isolation of Shared Resources on System-on-a-Chip (SoC))
The System-On-a-Chip (SoC) does not properly isolate shared resources between trusted and untrusted agents.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Identifier for IP Block used in System-On-Chip (SOC)
- (1192)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1192(Improper Identifier for IP Block used in System-On-Chip (SOC))
The System-on-Chip (SoC) does not have unique, immutable identifiers for each of its components.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient Granularity of Access Control
- (1220)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1220(Insufficient Granularity of Access Control)
The product implements access controls via a policy or other feature with the intention to disable or restrict accesses (reads and/or writes) to assets in a system from untrusted agents. However, implemented access controls lack the required granularity
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient Granularity of Address Regions Protected by Register Locks
- (1222)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1222(Insufficient Granularity of Address Regions Protected by Register Locks)
The product defines a large address region protected from modification by the same register lock control bit. This results in a conflict between the functional requirement that some addresses need to be writable by software during operation and the security requirement that the system configuration lock bit must be set during the boot process.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Inclusion of Undocumented Features or Chicken Bits
- (1242)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1242(Inclusion of Undocumented Features or Chicken Bits)
The device includes chicken bits or undocumented features that can create entry points for unauthorized actors.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Restriction of Security Token Assignment
- (1259)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1259(Improper Restriction of Security Token Assignment)
The System-On-A-Chip (SoC) implements a Security Token mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Tokens are improperly protected, such as improperly restricting the assignment to trusted components.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Overlap Between Protected Memory Ranges
- (1260)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1260(Improper Handling of Overlap Between Protected Memory Ranges)
The product allows address regions to overlap, which can result in the bypassing of intended memory protection.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Access Control for Register Interface
- (1262)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1262(Improper Access Control for Register Interface)
The product uses memory-mapped I/O registers that act as an interface to hardware functionality from software, but there is improper access control to those registers.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Policy Uses Obsolete Encoding
- (1267)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1267(Policy Uses Obsolete Encoding)
The product uses an encoding mechanism that is no longer trusted, i.e., an obsolete encoding, to implement access controls.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Policy Privileges are not Assigned Consistently Between Control and Data Agents
- (1268)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1268(Policy Privileges are not Assigned Consistently Between Control and Data Agents)
The product's hardware-enforced access control for a particular resource improperly accounts for privilege discrepancies between control and write policies.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Generation of Incorrect Security Tokens
- (1270)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1270(Generation of Incorrect Security Tokens)
The product implements a Security Token mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Tokens generated in the system are incorrect.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Access Control Check Implemented After Asset is Accessed
- (1280)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1280(Access Control Check Implemented After Asset is Accessed)
A product's hardware-based access control check occurs after the asset has been accessed.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Decoding of Security Identifiers
- (1290)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1290(Incorrect Decoding of Security Identifiers)
The product implements a decoding mechanism to decode certain bus-transaction signals to security identifiers, but it decodes an untrusted agent's security identifier into a trusted agent's security identifier.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Conversion of Security Identifiers
- (1292)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1292(Incorrect Conversion of Security Identifiers)
The product implements a conversion mechanism to map certain bus-transaction signals to security identifiers, but this conversion between protocols is incorrectly implemented.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Insecure Security Identifier Mechanism
- (1294)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1294(Insecure Security Identifier Mechanism)
The System-on-Chip (SoC) implements a Security Identifier mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Identifiers are not correctly implemented.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Protection Mechanism for Alternate Hardware Interface
- (1299)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1299(Missing Protection Mechanism for Alternate Hardware Interface)
The lack of protections on alternate paths to access
control-protected assets (such as unprotected shadow registers
and other external facing unguarded interfaces) allows an
attacker to bypass existing protections to the asset that are
only performed against the primary path.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Source Identifier in Entity Transactions on a System-On-Chip (SOC)
- (1302)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1302(Missing Source Identifier in Entity Transactions on a System-On-Chip (SOC))
The product implements a security identifier mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity, but the entity does not consistently include the necessary Security Identifier with a security-critical transaction.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Non-Transparent Sharing of Microarchitectural Resources
- (1303)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1303(Non-Transparent Sharing of Microarchitectural Resources)
Hardware structures shared across execution contexts (e.g., caches and branch predictors) can violate the expected architecture isolation between contexts.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Write Protection for Parametric Data Values
- (1314)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1314(Missing Write Protection for Parametric Data Values)
The device does not write-protect the parametric data values for sensors that scale the sensor value, allowing untrusted software to manipulate the apparent result and potentially damage hardware or cause operational failure.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Support for Security Features in On-chip Fabrics or Buses
- (1318)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1318(Missing Support for Security Features in On-chip Fabrics or Buses)
On-chip fabrics or buses either do not support or are not configured to support privilege separation or other security features, such as access control.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Unauthorized Error Injection Can Degrade Hardware Redundancy
- (1334)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1334(Unauthorized Error Injection Can Degrade Hardware Redundancy)
An unauthorized agent can inject errors into a redundant block to deprive the system of redundancy or put the system in a degraded operating mode.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
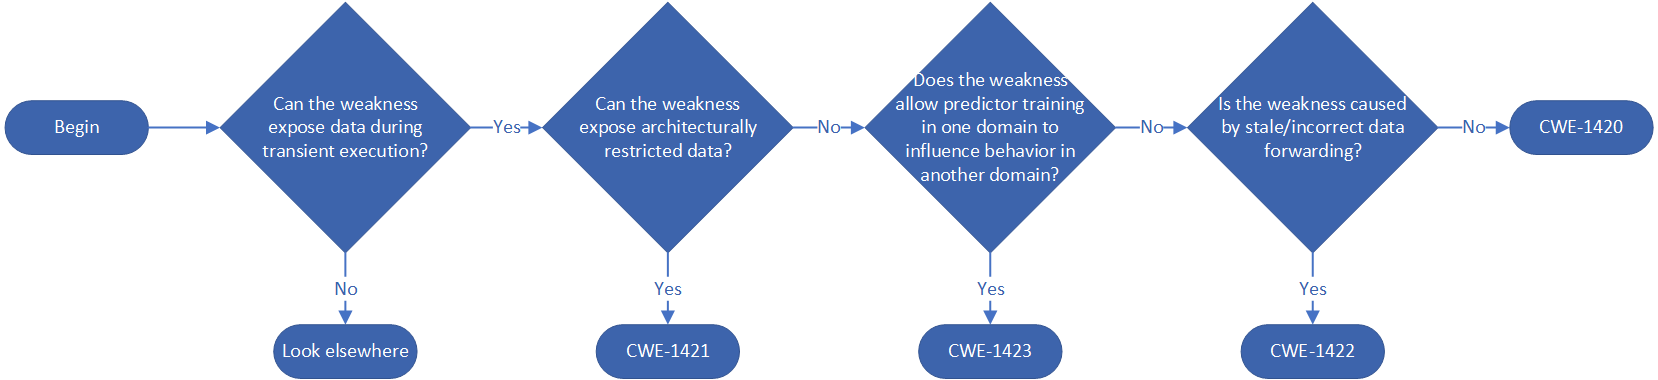
Exposure of Sensitive Information during Transient Execution
- (1420)
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1420(Exposure of Sensitive Information during Transient Execution)
A processor event or prediction may allow incorrect operations (or correct operations with incorrect data) to execute transiently, potentially exposing data over a covert channel.
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1421(Exposure of Sensitive Information in Shared Microarchitectural Structures during Transient Execution)
A processor event may allow transient operations to access
architecturally restricted data (for example, in another address
space) in a shared microarchitectural structure (for example, a CPU
cache), potentially exposing the data over a covert channel.
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1422(Exposure of Sensitive Information caused by Incorrect Data Forwarding during Transient Execution)
A processor event or prediction may allow incorrect or stale data to
be forwarded to transient operations, potentially exposing data over a
covert channel.
1194(Hardware Design) >
1198(Privilege Separation and Access Control Issues) >
1423(Exposure of Sensitive Information caused by Shared Microarchitectural Predictor State that Influences Transient Execution)
Shared microarchitectural predictor state may allow code to influence
transient execution across a hardware boundary, potentially exposing
data that is accessible beyond the boundary over a covert channel.
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns)
Weaknesses in this category are related to hardware-circuit design and logic (e.g., CMOS transistors, finite state machines, and registers) as well as issues related to hardware description languages such as System Verilog and VHDL.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Failure to Disable Reserved Bits
- (1209)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1209(Failure to Disable Reserved Bits)
The reserved bits in a hardware design are not disabled prior to production.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Register Defaults or Module Parameters
- (1221)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1221(Incorrect Register Defaults or Module Parameters)
Hardware description language code incorrectly defines register defaults or hardware Intellectual Property (IP) parameters to insecure values.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Race Condition for Write-Once Attributes
- (1223)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1223(Race Condition for Write-Once Attributes)
A write-once register in hardware design is programmable by an untrusted software component earlier than the trusted software component, resulting in a race condition issue.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Restriction of Write-Once Bit Fields
- (1224)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1224(Improper Restriction of Write-Once Bit Fields)
The hardware design control register "sticky bits" or write-once bit fields are improperly implemented, such that they can be reprogrammed by software.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Prevention of Lock Bit Modification
- (1231)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1231(Improper Prevention of Lock Bit Modification)
The product uses a trusted lock bit for restricting access to registers, address regions, or other resources, but the product does not prevent the value of the lock bit from being modified after it has been set.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Lock Behavior After Power State Transition
- (1232)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1232(Improper Lock Behavior After Power State Transition)
Register lock bit protection disables changes to system configuration once the bit is set. Some of the protected registers or lock bits become programmable after power state transitions (e.g., Entry and wake from low power sleep modes) causing the system configuration to be changeable.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Security-Sensitive Hardware Controls with Missing Lock Bit Protection
- (1233)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1233(Security-Sensitive Hardware Controls with Missing Lock Bit Protection)
The product uses a register lock bit protection mechanism, but it does not ensure that the lock bit prevents modification of system registers or controls that perform changes to important hardware system configuration.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Internal or Debug Modes Allow Override of Locks
- (1234)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1234(Hardware Internal or Debug Modes Allow Override of Locks)
System configuration protection may be bypassed during debug mode.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Finite State Machines (FSMs) in Hardware Logic
- (1245)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1245(Improper Finite State Machines (FSMs) in Hardware Logic)
Faulty finite state machines (FSMs) in the hardware logic allow an attacker to put the system in an undefined state, to cause a denial of service (DoS) or gain privileges on the victim's system.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Improper Preservation of Consistency Between Independent Representations of Shared State
- (1250)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1250(Improper Preservation of Consistency Between Independent Representations of Shared State)
The product has or supports multiple distributed components or sub-systems that are each required to keep their own local copy of shared data - such as state or cache - but the product does not ensure that all local copies remain consistent with each other.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Selection of Fuse Values
- (1253)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1253(Incorrect Selection of Fuse Values)
The logic level used to set a system to a secure state relies on a fuse being unblown.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Comparison Logic Granularity
- (1254)
The product's comparison logic is performed over a series of steps rather than across the entire string in one operation. If there is a comparison logic failure on one of these steps, the operation may be vulnerable to a timing attack that can result in the interception of the process for nefarious purposes.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Single Event Upsets
- (1261)
1194(Hardware Design) >
1199(General Circuit and Logic Design Concerns) >
1261(Improper Handling of Single Event Upsets)
The hardware logic does not effectively handle when single-event upsets (SEUs) occur.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Logic Contains Race Conditions
- (1298)
A race condition in the hardware logic results in undermining security guarantees of the system.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Simulation / Synthesis Mismatch
- (1461)
The hardware design contains structures that are interpreted
differently during synthesis than during simulation, which
cause inconsistencies in security-relevant behavior between
the synthesized implementation and the simulation.
1194(Hardware Design) >
1201(Core and Compute Issues)
Weaknesses in this category are typically associated with CPUs, Graphics, Vision, AI, FPGA, and microcontrollers.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
CPU Hardware Not Configured to Support Exclusivity of Write and Execute Operations
- (1252)
1194(Hardware Design) >
1201(Core and Compute Issues) >
1252(CPU Hardware Not Configured to Support Exclusivity of Write and Execute Operations)
The CPU is not configured to provide hardware support for exclusivity of write and execute operations on memory. This allows an attacker to execute data from all of memory.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sequence of Processor Instructions Leads to Unexpected Behavior
- (1281)
1194(Hardware Design) >
1201(Core and Compute Issues) >
1281(Sequence of Processor Instructions Leads to Unexpected Behavior)
Specific combinations of processor instructions lead to undesirable behavior such as locking the processor until a hard reset performed.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Information Exposure through Microarchitectural State after Transient Execution
- (1342)
1194(Hardware Design) >
1201(Core and Compute Issues) >
1342(Information Exposure through Microarchitectural State after Transient Execution)
The processor does not properly clear microarchitectural state after incorrect microcode assists or speculative execution, resulting in transient execution.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive Information during Transient Execution
- (1420)
1194(Hardware Design) >
1201(Core and Compute Issues) >
1420(Exposure of Sensitive Information during Transient Execution)
A processor event or prediction may allow incorrect operations (or correct operations with incorrect data) to execute transiently, potentially exposing data over a covert channel.
1194(Hardware Design) >
1201(Core and Compute Issues) >
1421(Exposure of Sensitive Information in Shared Microarchitectural Structures during Transient Execution)
A processor event may allow transient operations to access
architecturally restricted data (for example, in another address
space) in a shared microarchitectural structure (for example, a CPU
cache), potentially exposing the data over a covert channel.
1194(Hardware Design) >
1201(Core and Compute Issues) >
1422(Exposure of Sensitive Information caused by Incorrect Data Forwarding during Transient Execution)
A processor event or prediction may allow incorrect or stale data to
be forwarded to transient operations, potentially exposing data over a
covert channel.
1194(Hardware Design) >
1201(Core and Compute Issues) >
1423(Exposure of Sensitive Information caused by Shared Microarchitectural Predictor State that Influences Transient Execution)
Shared microarchitectural predictor state may allow code to influence
transient execution across a hardware boundary, potentially exposing
data that is accessible beyond the boundary over a covert channel.
1194(Hardware Design) >
1202(Memory and Storage Issues)
Weaknesses in this category are typically associated with memory (e.g., DRAM, SRAM) and storage technologies (e.g., NAND Flash, OTP, EEPROM, and eMMC).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information in Resource Not Removed Before Reuse
- (226)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
226(Sensitive Information in Resource Not Removed Before Reuse)
The product releases a resource such as memory or a file so that it can be made available for reuse, but it does not clear or "zeroize" the information contained in the resource before the product performs a critical state transition or makes the resource available for reuse by other entities.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Improper Zeroization of Hardware Register
- (1239)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1239(Improper Zeroization of Hardware Register)
The hardware product does not properly clear sensitive information from built-in registers when the user of the hardware block changes.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Write Handling in Limited-write Non-Volatile Memories
- (1246)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1246(Improper Write Handling in Limited-write Non-Volatile Memories)
The product does not implement or incorrectly implements wear leveling operations in limited-write non-volatile memories.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Mirrored Regions with Different Values
- (1251)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1251(Mirrored Regions with Different Values)
The product's architecture mirrors regions without ensuring that their contents always stay in sync.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Access Control Applied to Mirrored or Aliased Memory Regions
- (1257)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1257(Improper Access Control Applied to Mirrored or Aliased Memory Regions)
Aliased or mirrored memory regions in hardware designs may have inconsistent read/write permissions enforced by the hardware.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Assumed-Immutable Data is Stored in Writable Memory
- (1282)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1282(Assumed-Immutable Data is Stored in Writable Memory)
Immutable data, such as a first-stage bootloader, device identifiers, and "write-once" configuration settings are stored in writable memory that can be re-programmed or updated in the field.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Information Exposure through Microarchitectural State after Transient Execution
- (1342)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1342(Information Exposure through Microarchitectural State after Transient Execution)
The processor does not properly clear microarchitectural state after incorrect microcode assists or speculative execution, resulting in transient execution.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive Information during Transient Execution
- (1420)
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1420(Exposure of Sensitive Information during Transient Execution)
A processor event or prediction may allow incorrect operations (or correct operations with incorrect data) to execute transiently, potentially exposing data over a covert channel.
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1421(Exposure of Sensitive Information in Shared Microarchitectural Structures during Transient Execution)
A processor event may allow transient operations to access
architecturally restricted data (for example, in another address
space) in a shared microarchitectural structure (for example, a CPU
cache), potentially exposing the data over a covert channel.
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1422(Exposure of Sensitive Information caused by Incorrect Data Forwarding during Transient Execution)
A processor event or prediction may allow incorrect or stale data to
be forwarded to transient operations, potentially exposing data over a
covert channel.
1194(Hardware Design) >
1202(Memory and Storage Issues) >
1423(Exposure of Sensitive Information caused by Shared Microarchitectural Predictor State that Influences Transient Execution)
Shared microarchitectural predictor state may allow code to influence
transient execution across a hardware boundary, potentially exposing
data that is accessible beyond the boundary over a covert channel.
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems)
Weaknesses in this category are related to hardware
security problems that apply to peripheral devices, IO
interfaces, on-chip interconnects, network-on-chip (NoC),
and buses. For example, this category includes issues
related to design of hardware interconnect and/or protocols
such as PCIe, USB, SMBUS, general-purpose IO pins, and
user-input peripherals such as mouse and keyboard.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Translation of Security Attributes by Fabric Bridge
- (1311)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1311(Improper Translation of Security Attributes by Fabric Bridge)
The fabric bridge incorrectly translates security attributes from either trusted to untrusted or from untrusted to trusted when converting from one fabric protocol to another.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Protection for Mirrored Regions in On-Chip Fabric Firewall
- (1312)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1312(Missing Protection for Mirrored Regions in On-Chip Fabric Firewall)
The firewall in an on-chip fabric protects the main addressed region, but it does not protect any mirrored memory or memory-mapped-IO (MMIO) regions.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Setting of Bus Controlling Capability in Fabric End-point
- (1315)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1315(Improper Setting of Bus Controlling Capability in Fabric End-point)
The bus controller enables bits in the fabric end-point to allow responder devices to control transactions on the fabric.
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1316(Fabric-Address Map Allows Programming of Unwarranted Overlaps of Protected and Unprotected Ranges)
The address map of the on-chip fabric has protected and unprotected regions overlapping, allowing an attacker to bypass access control to the overlapping portion of the protected region.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Access Control in Fabric Bridge
- (1317)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1317(Improper Access Control in Fabric Bridge)
The product uses a fabric bridge for transactions between two Intellectual Property (IP) blocks, but the bridge does not properly perform the expected privilege, identity, or other access control checks between those IP blocks.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Isolation of Shared Resources in Network On Chip (NoC)
- (1331)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1331(Improper Isolation of Shared Resources in Network On Chip (NoC))
The Network On Chip (NoC) does not isolate or incorrectly isolates its on-chip-fabric and internal resources such that they are shared between trusted and untrusted agents, creating timing channels.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
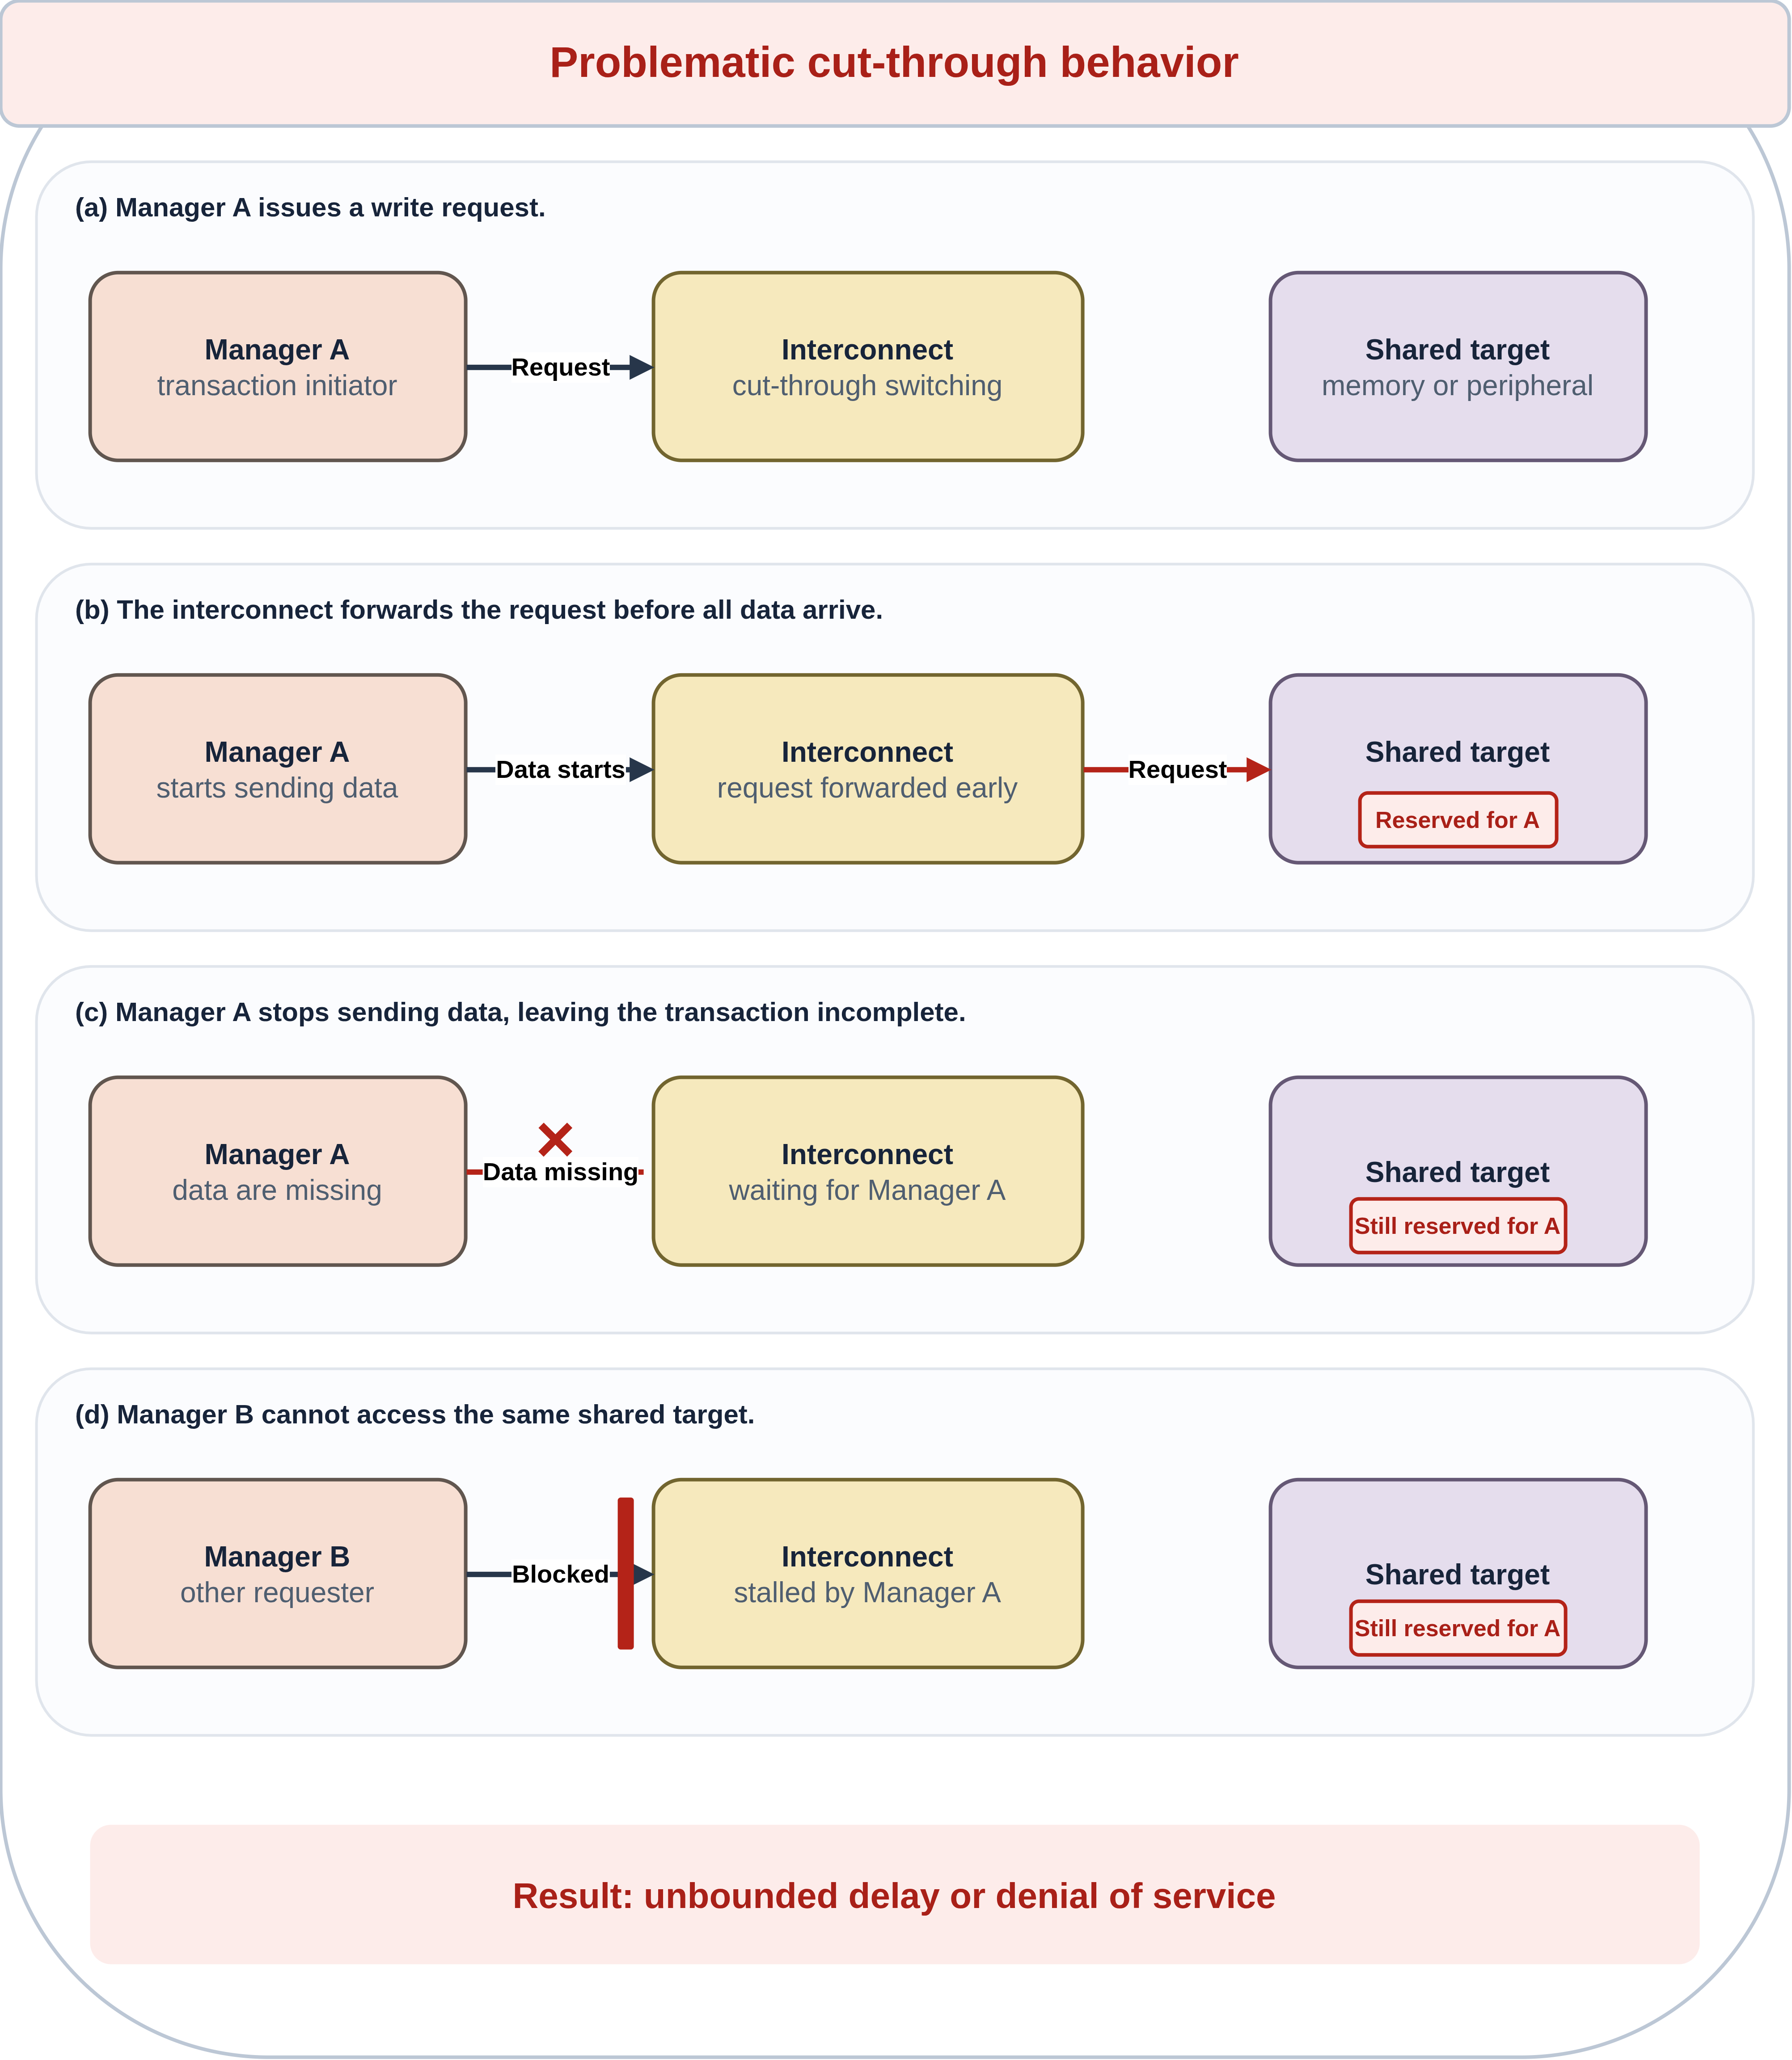
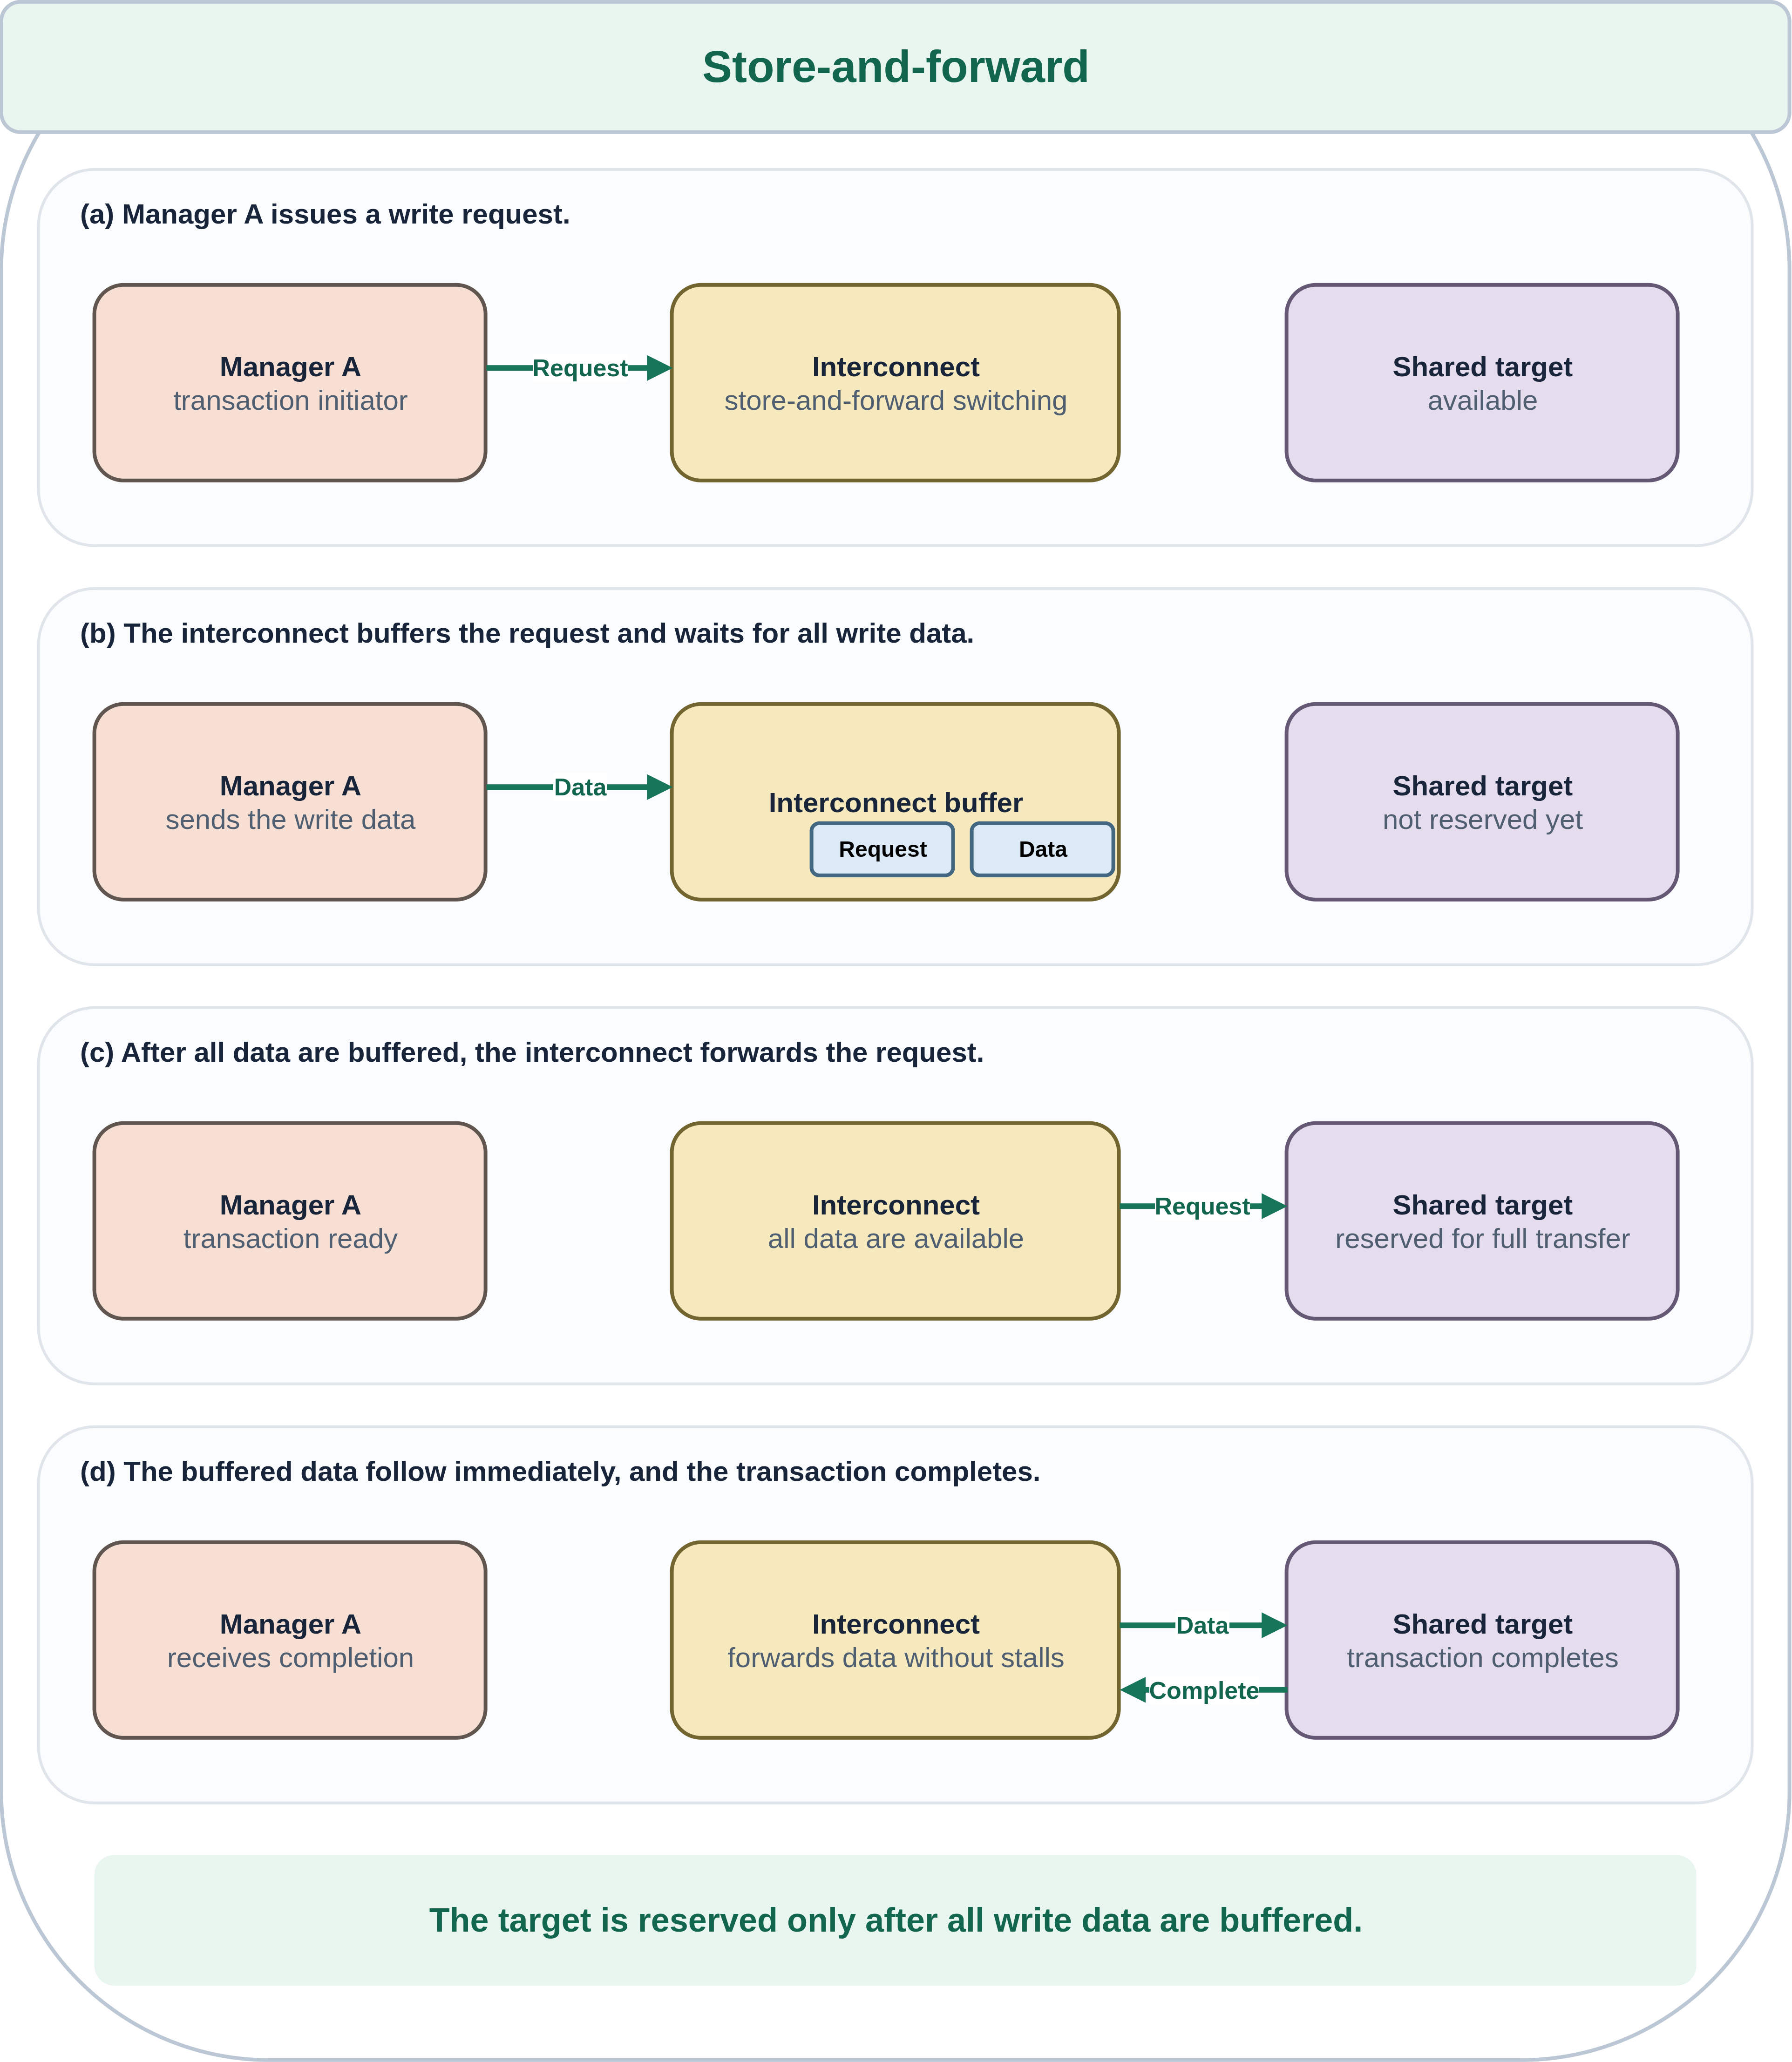
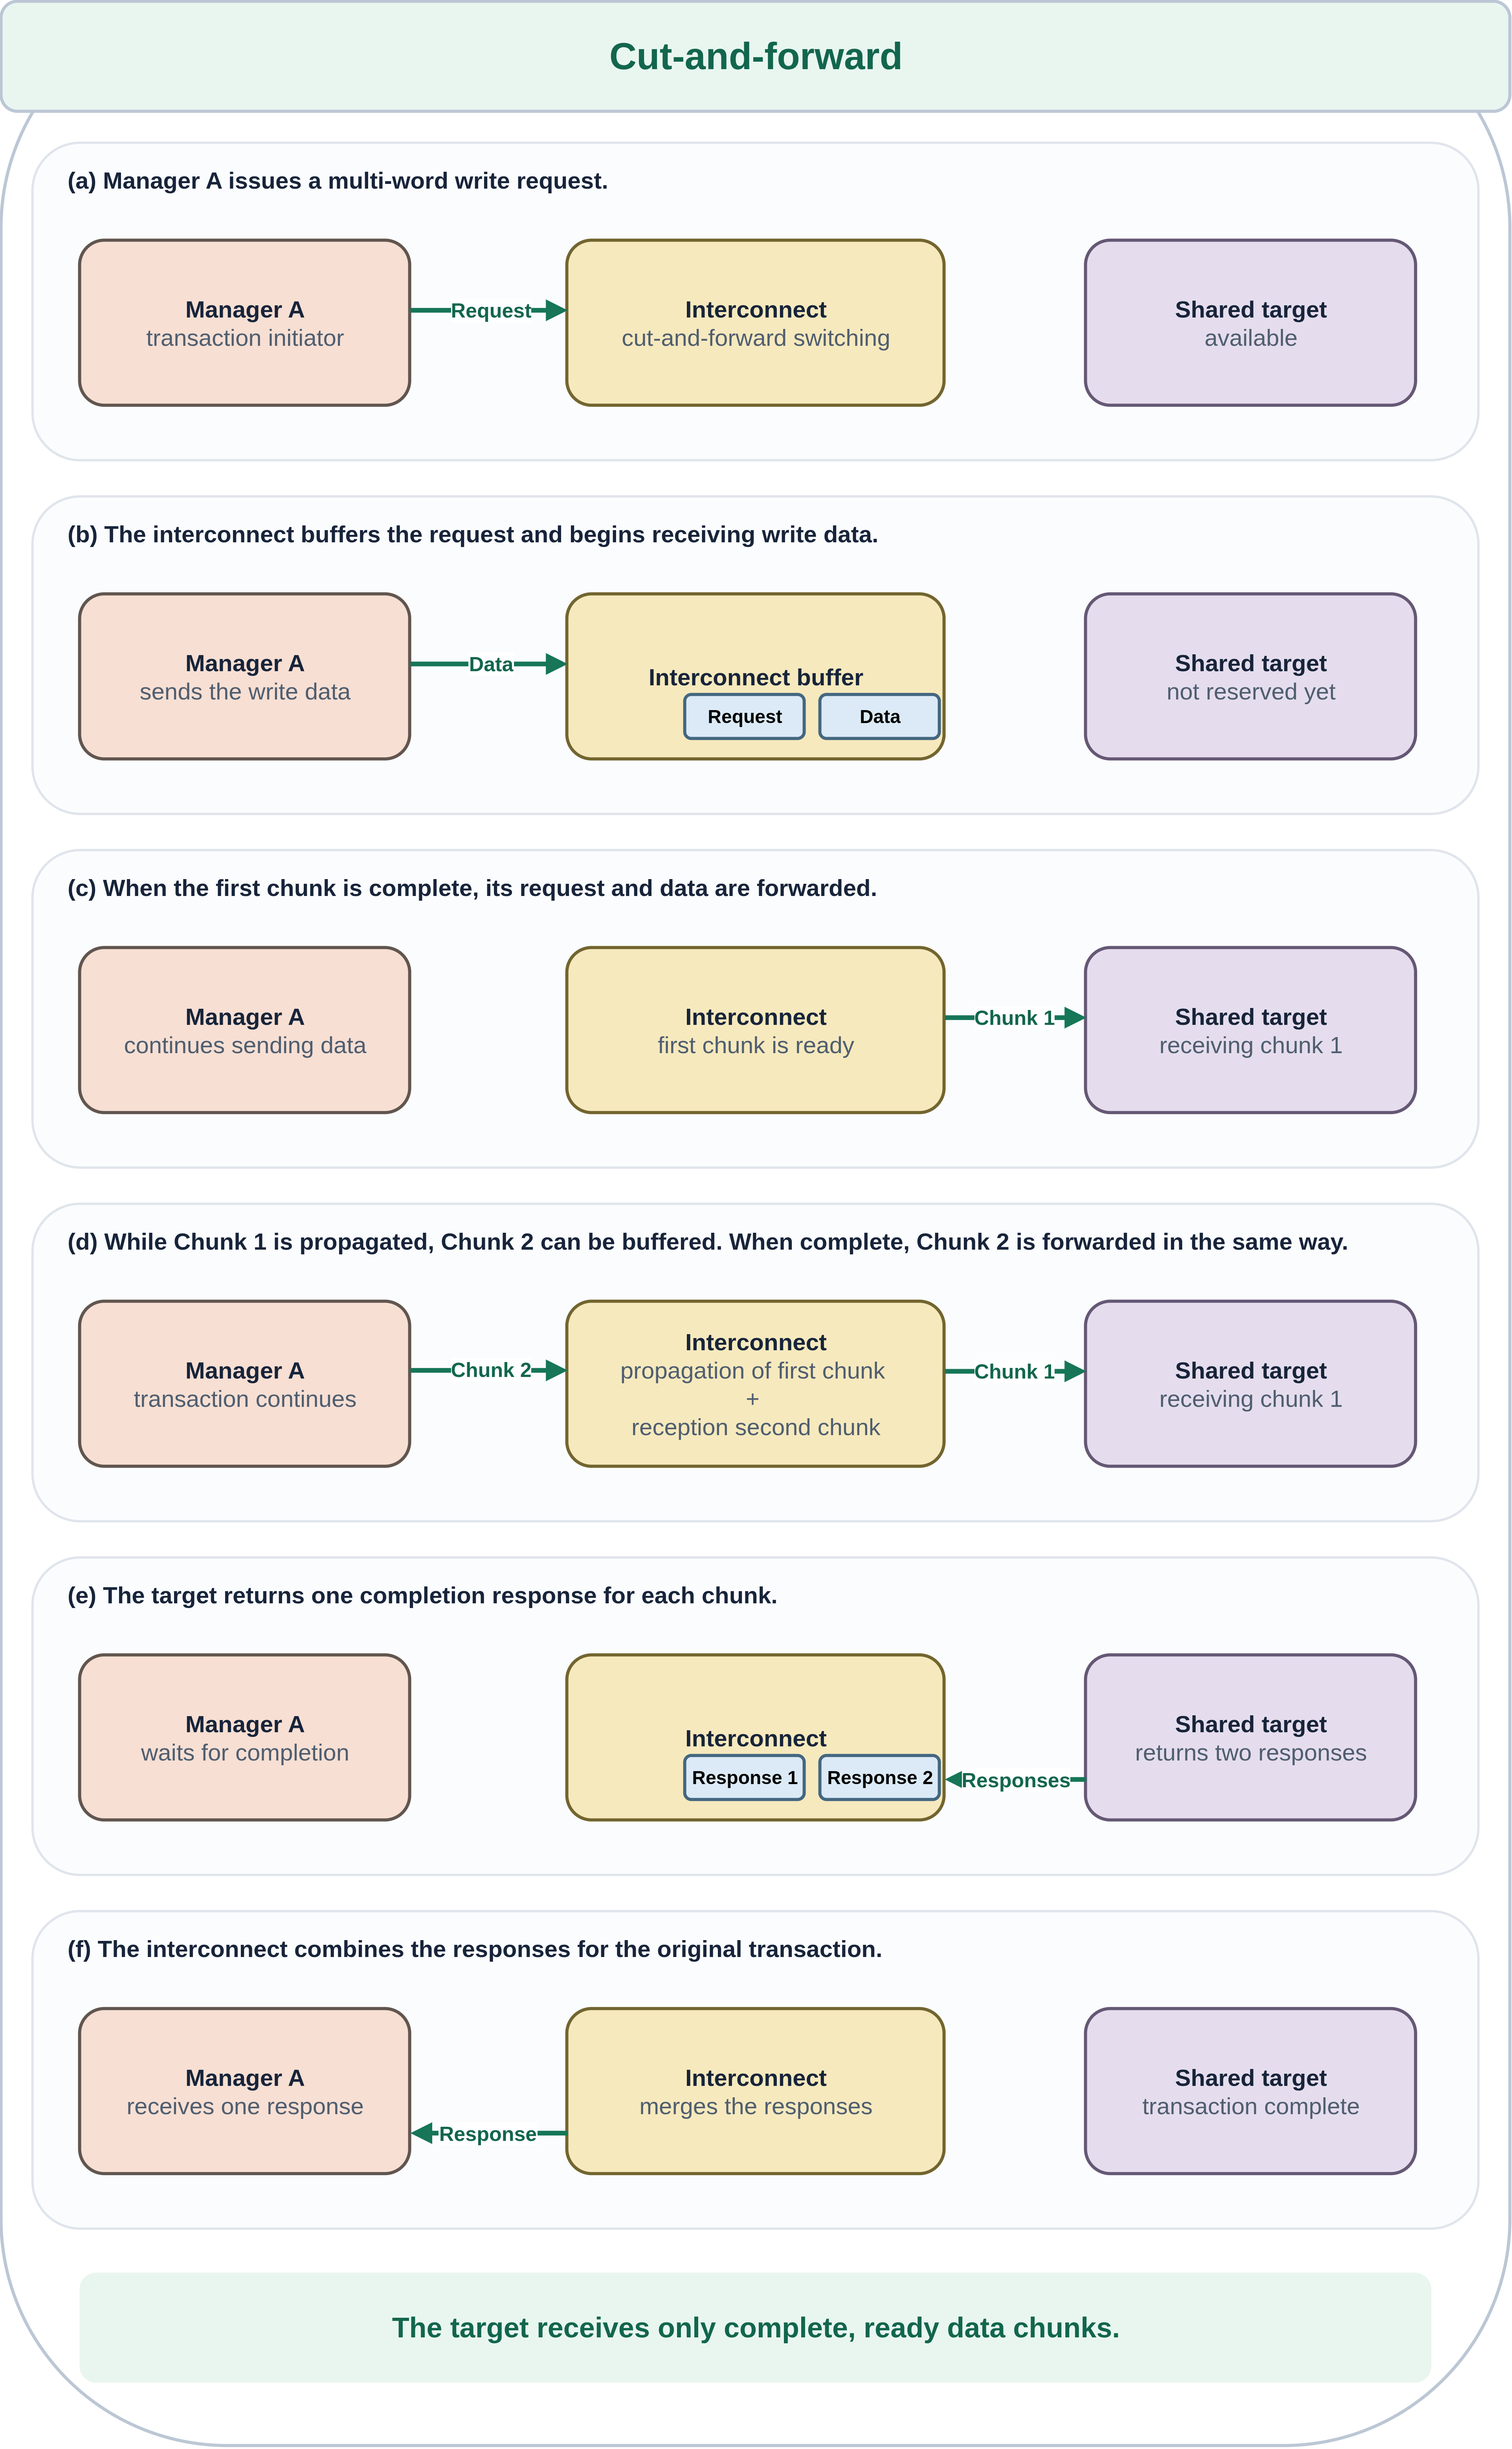
Improper Request Propagation before Data Reception in Write Transactions in a Bus Architecture
- (1476)
1194(Hardware Design) >
1203(Peripherals, On-chip Fabric, and Interface/IO Problems) >
1476(Improper Request Propagation before Data Reception in Write Transactions in a Bus Architecture)
The product uses a multi-manager shared bus architecture
with an on-chip interconnect that speculatively propagates
a request for a write transaction, but it does not ensure
that the remaining steps required by the manager module to
complete the request are fulfilled in a timely manner.
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues)
Weaknesses in this category are related to hardware implementations of cryptographic protocols and other hardware-security primitives such as physical unclonable functions (PUFs) and random number generators (RNGs).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
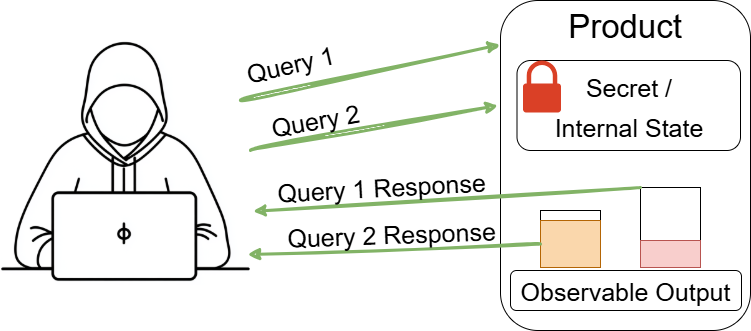
Observable Discrepancy
- (203)
The product behaves differently or sends different responses under different circumstances in a way that is observable to an unauthorized actor.
Side Channel Attack
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Cryptographic Step
- (325)
The product does not implement a required step in a cryptographic algorithm, resulting in weaker encryption than advertised by the algorithm.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Use of a Cryptographic Primitive with a Risky Implementation
- (1240)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1240(Use of a Cryptographic Primitive with a Risky Implementation)
To fulfill the need for a cryptographic primitive, the product implements a cryptographic algorithm using a non-standard, unproven, or disallowed/non-compliant cryptographic implementation.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Use of Predictable Algorithm in Random Number Generator
- (1241)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1241(Use of Predictable Algorithm in Random Number Generator)
The device uses an algorithm that is predictable and generates a pseudo-random number.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Cryptographic Operations are Run Before Supporting Units are Ready
- (1279)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1279(Cryptographic Operations are Run Before Supporting Units are Ready)
Performing cryptographic operations without ensuring that the supporting inputs are ready to supply valid data may compromise the cryptographic result.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection of Physical Side Channels
- (1300)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1300(Improper Protection of Physical Side Channels)
The device does not contain sufficient protection
mechanisms to prevent physical side channels from exposing
sensitive information due to patterns in physically observable
phenomena such as variations in power consumption,
electromagnetic emissions (EME), or acoustic emissions.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Hardware Behavior in Exceptionally Cold Environments
- (1351)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1351(Improper Handling of Hardware Behavior in Exceptionally Cold Environments)
The hardware device, or the firmware running on it, is
missing or has incorrect protection mechanisms to maintain
goals of security primitives when the device is cooled below
standard operating temperatures.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Driving Intermediate Cryptographic State/Results to Hardware Module Outputs
- (1431)
1194(Hardware Design) >
1205(Security Primitives and Cryptography Issues) >
1431(Driving Intermediate Cryptographic State/Results to Hardware Module Outputs)
The product uses a hardware module implementing a cryptographic
algorithm that writes sensitive information about the intermediate
state or results of its cryptographic operations via one of its output
wires (typically the output port containing the final result).
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns)
Weaknesses in this category are related to system power, voltage, current, temperature, clocks, system state saving/restoring, and resets at the platform and SoC level.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Lock Behavior After Power State Transition
- (1232)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1232(Improper Lock Behavior After Power State Transition)
Register lock bit protection disables changes to system configuration once the bit is set. Some of the protected registers or lock bits become programmable after power state transitions (e.g., Entry and wake from low power sleep modes) causing the system configuration to be changeable.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection Against Voltage and Clock Glitches
- (1247)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1247(Improper Protection Against Voltage and Clock Glitches)
The device does not contain or contains incorrectly implemented circuitry or sensors to detect and mitigate voltage and clock glitches and protect sensitive information or software contained on the device.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Semiconductor Defects in Hardware Logic with Security-Sensitive Implications
- (1248)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1248(Semiconductor Defects in Hardware Logic with Security-Sensitive Implications)
The security-sensitive hardware module contains semiconductor defects.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Comparison Logic is Vulnerable to Power Side-Channel Attacks
- (1255)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1255(Comparison Logic is Vulnerable to Power Side-Channel Attacks)
A device's real time power consumption may be monitored during security token evaluation and the information gleaned may be used to determine the value of the reference token.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Restriction of Software Interfaces to Hardware Features
- (1256)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1256(Improper Restriction of Software Interfaces to Hardware Features)
The product provides software-controllable
device functionality for capabilities such as power and
clock management, but it does not properly limit
functionality that can lead to modification of
hardware memory or register bits, or the ability to
observe physical side channels.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Uninitialized Value on Reset for Registers Holding Security Settings
- (1271)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1271(Uninitialized Value on Reset for Registers Holding Security Settings)
Security-critical logic is not set to a known value on reset.
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1304(Improperly Preserved Integrity of Hardware Configuration State During a Power Save/Restore Operation)
The product performs a power save/restore
operation, but it does not ensure that the integrity of
the configuration state is maintained and/or verified between
the beginning and ending of the operation.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Write Protection for Parametric Data Values
- (1314)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1314(Missing Write Protection for Parametric Data Values)
The device does not write-protect the parametric data values for sensors that scale the sensor value, allowing untrusted software to manipulate the apparent result and potentially damage hardware or cause operational failure.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection for Outbound Error Messages and Alert Signals
- (1320)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1320(Improper Protection for Outbound Error Messages and Alert Signals)
Untrusted agents can disable alerts about signal conditions exceeding limits or the response mechanism that handles such alerts.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Faults that Lead to Instruction Skips
- (1332)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1332(Improper Handling of Faults that Lead to Instruction Skips)
The device is missing or incorrectly implements circuitry or sensors that detect and mitigate the skipping of security-critical CPU instructions when they occur.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protections Against Hardware Overheating
- (1338)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1338(Improper Protections Against Hardware Overheating)
A hardware device is missing or has inadequate protection features to prevent overheating.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Hardware Behavior in Exceptionally Cold Environments
- (1351)
1194(Hardware Design) >
1206(Power, Clock, Thermal, and Reset Concerns) >
1351(Improper Handling of Hardware Behavior in Exceptionally Cold Environments)
The hardware device, or the firmware running on it, is
missing or has incorrect protection mechanisms to maintain
goals of security primitives when the device is cooled below
standard operating temperatures.
1194(Hardware Design) >
1207(Debug and Test Problems)
Weaknesses in this category are related to hardware debug and test interfaces such as JTAG and scan chain.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
On-Chip Debug and Test Interface With Improper Access Control
- (1191)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1191(On-Chip Debug and Test Interface With Improper Access Control)
The chip does not implement or does not correctly perform access control to check whether users are authorized to access internal registers and test modes through the physical debug/test interface.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Internal or Debug Modes Allow Override of Locks
- (1234)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1234(Hardware Internal or Debug Modes Allow Override of Locks)
System configuration protection may be bypassed during debug mode.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Non-Volatile Information Not Protected During Debug
- (1243)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1243(Sensitive Non-Volatile Information Not Protected During Debug)
Access to security-sensitive information stored in fuses is not limited during debug.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Internal Asset Exposed to Unsafe Debug Access Level or State
- (1244)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1244(Internal Asset Exposed to Unsafe Debug Access Level or State)
The product uses physical debug or test
interfaces with support for multiple access levels, but it
assigns the wrong debug access level to an internal asset,
providing unintended access to the asset from untrusted debug
agents.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive System Information Due to Uncleared Debug Information
- (1258)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1258(Exposure of Sensitive System Information Due to Uncleared Debug Information)
The hardware product enters debug mode but does not fully clear security-sensitive values, such as keys and intermediate values in cryptographic operations.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information Uncleared Before Debug/Power State Transition
- (1272)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1272(Sensitive Information Uncleared Before Debug/Power State Transition)
The product performs a power or debug state transition, but it does not clear sensitive information that should no longer be accessible due to changes to information access restrictions.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Public Key Re-Use for Signing both Debug and Production Code
- (1291)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1291(Public Key Re-Use for Signing both Debug and Production Code)
The same public key is used for signing both debug and production code.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Debug Messages Revealing Unnecessary Information
- (1295)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1295(Debug Messages Revealing Unnecessary Information)
The product fails to adequately prevent the revealing of unnecessary and potentially sensitive system information within debugging messages.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Incorrect Chaining or Granularity of Debug Components
- (1296)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1296(Incorrect Chaining or Granularity of Debug Components)
The product's debug components contain incorrect chaining or granularity of debug components.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Allows Activation of Test or Debug Logic at Runtime
- (1313)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1313(Hardware Allows Activation of Test or Debug Logic at Runtime)
During runtime, the hardware allows for test or debug logic (feature) to be activated, which allows for changing the state of the hardware. This feature can alter the intended behavior of the system and allow for alteration and leakage of sensitive data by an adversary.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Management of Sensitive Trace Data
- (1323)
1194(Hardware Design) >
1207(Debug and Test Problems) >
1323(Improper Management of Sensitive Trace Data)
Trace data collected from several sources on the
System-on-Chip (SoC) is stored in unprotected locations or
transported to untrusted agents.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Cleartext Transmission of Sensitive Information
- (319)
1194(Hardware Design) >
1207(Debug and Test Problems) >
319(Cleartext Transmission of Sensitive Information)
The product transmits sensitive or security-critical data in cleartext in a communication channel that can be sniffed by unauthorized actors.
Weaknesses in this category can arise in multiple areas of hardware design or can apply to a wide cross-section of components.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Expected Behavior Violation
- (440)
A feature, API, or function does not perform according to its specification.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Documentation for Design
- (1053)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1053(Missing Documentation for Design)
The product does not have documentation that represents how it is designed.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Insufficient Technical Documentation
- (1059)
The product does not contain sufficient
technical or engineering documentation (whether on paper or
in electronic form) that contains descriptions of all of the
relevant software/hardware elements of the product.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Improper Physical Access Control
- (1263)
The product is designed with access restricted to certain information, but it does not sufficiently protect against an unauthorized actor with physical access to these areas.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Firmware Not Updateable
- (1277)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1277(Firmware Not Updateable)
The product does not provide its
users with the ability to update or patch its
firmware to address any vulnerabilities or
weaknesses that may be present.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient or Incomplete Data Removal within Hardware Component
- (1301)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1301(Insufficient or Incomplete Data Removal within Hardware Component)
The product's data removal process does not completely delete all data and potentially sensitive information within hardware components.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Reliance on Component That is Not Updateable
- (1329)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1329(Reliance on Component That is Not Updateable)
The product contains a component that cannot be updated or patched in order to remove vulnerabilities or significant bugs.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Remanent Data Readable after Memory Erase
- (1330)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1330(Remanent Data Readable after Memory Erase)
Confidential information stored in memory circuits is readable or recoverable after being cleared or erased, i.e., there is data remanence.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Reliance on Insufficiently Trustworthy Component
- (1357)
The product is built from multiple separate components, but it uses a component that is not sufficiently trusted to meet expectations for security, reliability, updateability, and maintainability.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Security-Relevant Feedback for Unexecuted Operations in Hardware Interface
- (1429)
1194(Hardware Design) >
1208(Cross-Cutting Problems) >
1429(Missing Security-Relevant Feedback for Unexecuted Operations in Hardware Interface)
The product has a hardware interface that silently discards operations
in situations for which feedback would be security-relevant, such as
the timely detection of failures or attacks.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware Simulation / Synthesis Mismatch
- (1461)
The hardware design contains structures that are interpreted
differently during synthesis than during simulation, which
cause inconsistencies in security-relevant behavior between
the synthesized implementation and the simulation.
1194(Hardware Design) >
1388(Physical Access Issues and Concerns)
Weaknesses in this category are related to concerns of physical access.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Improper Handling of Physical or Environmental Conditions
- (1384)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1384(Improper Handling of Physical or Environmental Conditions)
The product does not properly handle unexpected physical or environmental conditions that occur naturally or are artificially induced.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection against Electromagnetic Fault Injection (EM-FI)
- (1319)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1319(Improper Protection against Electromagnetic Fault Injection (EM-FI))
The device is susceptible to electromagnetic fault injection attacks, causing device internal information to be compromised or security mechanisms to be bypassed.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection Against Voltage and Clock Glitches
- (1247)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1247(Improper Protection Against Voltage and Clock Glitches)
The device does not contain or contains incorrectly implemented circuitry or sensors to detect and mitigate voltage and clock glitches and protect sensitive information or software contained on the device.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Single Event Upsets
- (1261)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1261(Improper Handling of Single Event Upsets)
The hardware logic does not effectively handle when single-event upsets (SEUs) occur.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Faults that Lead to Instruction Skips
- (1332)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1332(Improper Handling of Faults that Lead to Instruction Skips)
The device is missing or incorrectly implements circuitry or sensors that detect and mitigate the skipping of security-critical CPU instructions when they occur.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Hardware Behavior in Exceptionally Cold Environments
- (1351)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1351(Improper Handling of Hardware Behavior in Exceptionally Cold Environments)
The hardware device, or the firmware running on it, is
missing or has incorrect protection mechanisms to maintain
goals of security primitives when the device is cooled below
standard operating temperatures.
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1278(Missing Protection Against Hardware Reverse Engineering Using Integrated Circuit (IC) Imaging Techniques)
Information stored in hardware may be recovered by an attacker with the capability to capture and analyze images of the integrated circuit using techniques such as scanning electron microscopy.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Comparison Logic is Vulnerable to Power Side-Channel Attacks
- (1255)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1255(Comparison Logic is Vulnerable to Power Side-Channel Attacks)
A device's real time power consumption may be monitored during security token evaluation and the information gleaned may be used to determine the value of the reference token.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection of Physical Side Channels
- (1300)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1300(Improper Protection of Physical Side Channels)
The device does not contain sufficient protection
mechanisms to prevent physical side channels from exposing
sensitive information due to patterns in physically observable
phenomena such as variations in power consumption,
electromagnetic emissions (EME), or acoustic emissions.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Semiconductor Defects in Hardware Logic with Security-Sensitive Implications
- (1248)
1194(Hardware Design) >
1388(Physical Access Issues and Concerns) >
1248(Semiconductor Defects in Hardware Logic with Security-Sensitive Implications)
The security-sensitive hardware module contains semiconductor defects.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
View
Rationale
This entry is a View. Views are not weaknesses and therefore inappropriate to describe the root causes of vulnerabilities.
Comments
Use this View or other Views to search and navigate for the appropriate weakness.
Notes
Relationship
This view attempts to present hardware weaknesses in a simple and intuitive way. As such it uses a single level of abstraction. The same category could contain weaknesses that have parent/child relationships within View-1000. By exploring View-1000 relationships for the weaknesses that are included, one can find deeper relationships between some hardware weaknesses.
Other
The top level categories in this view represent commonly understood areas/terms within hardware design, and are meant to aid the user in identifying potential related weaknesses. It is possible for the same weakness to exist within multiple different categories.
View Metrics
CWEs in this view
Total CWEs
Weaknesses
112
out of
956
Categories
13
out of
396
Views
0
out of
58
Total
125
out of
1410
Content
History
Submissions
Submission Date
Submitter
Organization
2019-12-27
(CWE 4.0, 2020-02-24)
CWE Content Team
MITRE
Contributions
Contribution Date
Contributor
Organization
2026-07-17
(CWE 5.0, 2026-10-28)
Hardware CWE Special Interest Group (HW CWE SIG)
Discussed pros and cons of
deeper versus shallower trees for this view,
ultimately choosing the shallower
tree.
CWE-1280: Access Control Check Implemented After Asset is Accessed
Weakness ID: 1280
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A product's hardware-based access control check occurs after the asset has been accessed.
Extended Description
The product implements a hardware-based access control check. The asset should be accessible only after the check is successful. If, however, this operation is not atomic and the asset is accessed before the check is complete, the security of the system may be compromised.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Access Control Check
Behavior-Property
After Asset is Accessed
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Modify Application Data; Read Application Data; Gain Privileges or Assume Identity; Bypass Protection Mechanism
Scope: Access Control, Confidentiality, Integrity
Potential Mitigations
Phase(s)
Mitigation
Implementation
Implement the access control check first. Access should only be given to asset if agent is authorized.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Assume that the module foo_bar implements a protected register. The register content is the asset. Only transactions made by user id (indicated by signal usr_id) 0x4 are allowed to modify the register contents. The signal grant_access is used to provide access.
This code uses Verilog blocking assignments for data_out and grant_access. Therefore, these assignments happen sequentially (i.e., data_out is updated to new value first, and grant_access is updated the next cycle) and not in parallel. Therefore, the asset data_out is allowed to be modified even before the access control check is complete and grant_access signal is set. Since grant_access does not have a reset value, it will be meta-stable and will randomly go to either 0 or 1.
Flipping the order of the assignment of data_out and grant_access should solve the problem. The correct snippet of code is shown below.
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Insufficient Control Flow Management
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1282: Assumed-Immutable Data is Stored in Writable Memory
Weakness ID: 1282
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Immutable data, such as a first-stage bootloader, device identifiers, and "write-once" configuration settings are stored in writable memory that can be re-programmed or updated in the field.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Integrity
Security is lost if assets assumed to be immutable can be modified.
Potential Mitigations
Phase(s)
Mitigation
Implementation
Storing immutable code or data in read-only memory
(ROM), fuses, or one-time programmable (OTP) memory
provides strong integrity guarantees and provides a
root of trust for securing the rest of the system.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Security services such as secure boot, authentication
of code and data, and device attestation all require
assets such as the first stage bootloader, public
keys, golden hash digests, etc. which are implicitly
trusted.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Keys, code, configuration settings, and other data should be programmed in write-once or read-only memory instead of writable memory.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Cryptographic hash functions are commonly used to create unique fixed-length digests used to ensure the integrity of code and keys. A golden digest is stored on the device and compared to the digest computed from the data to be verified. If the digests match, the data has not been maliciously modified. If an attacker can modify the golden digest they then have the ability to store arbitrary data that passes the verification check. Hash digests used to verify public keys and early stage boot code should be immutable, with the strongest protection offered by hardware immutability.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to
see updates and content improvements.
Maintenance
As of CWE 4.3, CWE-1282 and CWE-1233 are being investigated
for potential duplication or overlap.
CWE-319: Cleartext Transmission of Sensitive Information
Weakness ID: 319
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product transmits sensitive or security-critical data in cleartext in a communication channel that can be sniffed by unauthorized actors.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data; Modify Files or Directories
Scope: Integrity, Confidentiality
Anyone can read the information by gaining access to the channel being used for communication. Many communication channels can be "sniffed" (monitored) by adversaries during data transmission. For example, in networking, packets can traverse many intermediary nodes from the source to the destination, whether across the internet, an internal network, the cloud, etc. Some actors might have privileged access to a network interface or any link along the channel, such as a router, but they might not be authorized to collect the underlying data. As a result, network traffic could be sniffed by adversaries, spilling security-critical data.
Read Application Data; Modify Files or Directories; Other
Scope: Integrity, Confidentiality
When full communications are recorded or logged, such as with a packet dump, an adversary could attempt to obtain the dump long after the transmission has occurred and try to "sniff" the cleartext from the recorded communications in the dump itself. Even if the information is encoded in a way that is not human-readable, certain techniques could determine which encoding is being used, then decode the information.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Before transmitting, encrypt the data using reliable, confidentiality-protecting cryptographic protocols.
Implementation
When using web applications with SSL, use SSL for the entire session from login to logout, not just for the initial login page.
Implementation
When designing hardware platforms, ensure that approved encryption algorithms (such as those recommended by NIST) protect paths from security critical data to trusted user applications.
Testing
Use tools and techniques that require manual (human) analysis, such as penetration testing, threat modeling, and interactive tools that allow the tester to record and modify an active session. These may be more effective than strictly automated techniques. This is especially the case with weaknesses that are related to design and business rules.
Operation
Configure servers to use encrypted channels for communication, which may include SSL or other secure protocols.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
J2EE Misconfiguration: Data Transmission Without Encryption
ParentOf
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Cookie in HTTPS Session Without 'Secure' Attribute
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Relevant to the view "Weaknesses for Simplified Mapping of Published Vulnerabilities" (View-1003)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.
Architecture and Design
For hardware, this may be introduced when design does not plan for an attacker having physical access while a legitimate user is remotely operating the device.
Operation
System Configuration
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Go
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: Cloud Computing
(Undetermined Prevalence)
Class: Mobile
(Undetermined Prevalence)
Class: ICS/OT
(Often Prevalent)
Class: System on Chip
(Undetermined Prevalence)
Test/Debug Hardware
(Often Prevalent)
Likelihood Of Exploit
High
Demonstrative Examples
Example 1
The following code attempts to establish a connection to a site to communicate sensitive information.
(bad code)
Example Language: Java
try {
URL u = new URL("http://www.secret.example.org/"); HttpURLConnection hu = (HttpURLConnection) u.openConnection(); hu.setRequestMethod("PUT"); hu.connect(); OutputStream os = hu.getOutputStream(); hu.disconnect();
} catch (IOException e) {
//...
}
Though a connection is successfully made, the connection is unencrypted and it is possible that all sensitive data sent to or received from the server will be read by unintended actors.
Example 2
In 2022, the OT:ICEFALL study examined products by 10 different Operational Technology (OT) vendors. The researchers reported 56 vulnerabilities and said that the products were "insecure by design" [REF-1283]. If exploited, these vulnerabilities often allowed adversaries to change how the products operated, ranging from denial of service to changing the code that the products executed. Since these products were often used in industries such as power, electrical, water, and others, there could even be safety implications.
Multiple vendors used cleartext transmission of sensitive information in their OT products.
Example 3
A TAP accessible register is read/written by a JTAG based tool, for internal use by authorized users. However, an adversary can connect a probing device and collect the values from the unencrypted channel connecting the JTAG interface to the authorized user, if no additional protections are employed.
Example 4
The following Azure CLI command lists the properties of a particular storage account:
(informative)
Example Language: Shell
az storage account show -g {ResourceGroupName} -n {StorageAccountName}
The enableHttpsTrafficOnly value is set to false, because the default setting for Secure transfer is set to Disabled. This allows cloud storage resources to successfully connect and transfer data without the use of encryption (e.g., HTTP, SMB 2.1, SMB 3.0, etc.).
Azure's storage accounts can be configured to only accept requests from secure connections made over HTTPS. The secure transfer setting can be enabled using Azure's Portal (GUI) or programmatically by setting the enableHttpsTrafficOnly property to True on the storage account, such as:
(good code)
Example Language: Shell
az storage account update -g {ResourceGroupName} -n {StorageAccountName} --https-only true
The change can be confirmed from the result by verifying that the enableHttpsTrafficOnly value is true:
Note: to enable secure transfer using Azure's Portal instead of the command line:
Open the Create storage account pane in the Azure portal.
In the Advanced page, select the Enable secure transfer checkbox.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Product sends file with cleartext passwords in e-mail message intended for diagnostic purposes.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Black Box
Use monitoring tools that examine the software's process as it interacts with the operating system and the network. This technique is useful in cases when source code is unavailable, if the software was not developed by you, or if you want to verify that the build phase did not introduce any new weaknesses. Examples include debuggers that directly attach to the running process; system-call tracing utilities such as truss (Solaris) and strace (Linux); system activity monitors such as FileMon, RegMon, Process Monitor, and other Sysinternals utilities (Windows); and sniffers and protocol analyzers that monitor network traffic.
Attach the monitor to the process, trigger the feature that sends the data, and look for the presence or absence of common cryptographic functions in the call tree. Monitor the network and determine if the data packets contain readable commands. Tools exist for detecting if certain encodings are in use. If the traffic contains high entropy, this might indicate the usage of encryption.
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
The CERT Oracle Secure Coding Standard for Java (2011) Chapter 16 - Platform Security (SEC)
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
OWASP Top Ten 2025 Category A04:2025 - Cryptographic Failures
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses Addressed by the OWASP Golang Secure Coding Practices Guide
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Other
Applicable communication channels are not limited to software products. Applicable channels include hardware-specific technologies such as internal hardware networks and external debug channels, supporting remote JTAG debugging. When mitigations are not applied to combat adversaries within the product's threat model, this weakness significantly lowers the difficulty of exploitation by such adversaries.
Taxonomy
Mappings
Mapped Taxonomy Name
Node ID
Fit
Mapped Node Name
PLOVER
Plaintext Transmission of Sensitive Information
The CERT Oracle Secure Coding Standard for Java (2011)
SEC06-J
Do not rely on the default automatic signature verification provided by URLClassLoader and java.util.jar
The CERT Oracle Secure Coding Standard for Java (2011)
SER02-J
Sign then seal sensitive objects before sending them outside a trust boundary
Michael Howard, David LeBlanc and John Viega. "24 Deadly Sins of Software Security". "Sin 22: Failing to Protect Network Traffic." Page 337. McGraw-Hill. 2010.
Center for Internet Security. "CIS Microsoft Azure Foundations Benchmark version 1.5.0". Sections 3.1 and 3.10. 2022-08-16.
<https://www.cisecurity.org/benchmark/azure>.
(URL validated: 2023-01-19)
CWE-1255: Comparison Logic is Vulnerable to Power Side-Channel Attacks
Weakness ID: 1255
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
VariantVariant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A device's real time power consumption may be monitored during security token evaluation and the information gleaned may be used to determine the value of the reference token.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Read Files or Directories; Modify Files or Directories; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Read Application Data; Modify Application Data; Hide Activities
The power consumed by a device may be instrumented and monitored in real time. If the algorithm for evaluating security tokens is not sufficiently robust, the power consumption may vary by token entry comparison against the reference value. Further, if retries are unlimited, the power difference between a "good" entry and a "bad" entry may be observed and used to determine whether each entry itself is correct thereby allowing unauthorized parties to calculate the reference value. As compromising a security token may result in complete system control, the impacts are relatively universal.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The design phase must consider each check of a security token against a standard and the amount of power consumed during the check of a good token versus a bad token. The alternative is an all at once check where a retry counter is incremented PRIOR to the check.
Architecture and Design
Another potential mitigation is to parallelize shifting of secret data (see example 2 below). Note that the wider the bus the more effective the result.
Architecture and Design
An additional potential mitigation is to add random data to each crypto operation then subtract it out afterwards. This is highly effective but costly in performance, area, and power consumption. It also requires a random number generator.
Implementation
If the architecture is unable to prevent the attack, using filtering components may reduce the ability to implement an attack, however, consideration must be given to the physical removal of the filter elements.
Integration
During integration, avoid use of a single secret for an extended period (e.g. frequent key updates). This limits the amount of data compromised but at the cost of complexity of use.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
The design of the algorithm itself may intrinsically allow the power side channel attack to be effective.
Implementation
This weakness may be introduced during implementation despite a robust design that otherwise prevents exploitation.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider an example hardware module that checks a user-provided password (or PIN) to grant access to a user. The user-provided password is compared against a stored value byte-by-byte.
(bad code)
Example Language: C
static nonvolatile password_tries = NUM_RETRIES;
do
while (password_tries == 0) ; // Hang here if no more password tries
password_ok = 0;
for (i = 0; i < NUM_PW_DIGITS; i++)
if (GetPasswordByte() == stored_password([i])
password_ok |= 1; // Power consumption is different here
Since the algorithm uses a different number of 1's and 0's for password validation, a different amount of power is consumed for the good byte versus the bad byte comparison. Using this information, an attacker may be able to guess the correct password for that byte-by-byte iteration with several repeated attempts by stopping the password evaluation before it completes.
Among various options for mitigating the string comparison is obscuring the power consumption by having opposing bit flips during bit operations. Note that in this example, the initial change of the bit values could still provide power indication depending upon the hardware itself. This possibility needs to be measured for verification.
(good code)
Example Language: C
static nonvolatile password_tries = NUM_RETRIES;
do
while (password_tries == 0) ; // Hang here if no more password tries
password_tries--; // Put retry code here to catch partial retries
password_ok = 0;
for (i = 0; i < NUM_PW_DIGITS; i++)
This code demonstrates the transfer of a secret key using Serial-In/Serial-Out shift. It's easy to extract the secret using simple power analysis as each shift gives data on a single bit of the key.
(bad code)
Example Language: Verilog
module siso(clk,rst,a,q);
input a;
input clk,rst;
output q;
reg q;
always@(posedge clk,posedge rst)
begin
if(rst==1'b1)
q<1'b0;
else
q<a;
end
endmodule
This code demonstrates the transfer of a secret key using a Parallel-In/Parallel-Out shift. In a parallel shift, data confounded by multiple bits of the key, not just one.
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
CMAC verification vulnerable to timing and power attacks.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Functional Areas
Power
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Sensitive Information Exposure
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Variant level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Accellera IP Security Assurance (IPSA) Working Group
Accellera Systems Initiative
Submitted new material that could be added to already-existing entry CWE-1255. Added new Potential Mitigations, a new example, an observed example, and an additional reference.
Modifications
Modification Date
Modifier
Organization
2026-10-28
(CWE 5.0, 2026-10-28)
CWE Content Team
MITRE
updated Common_Consequences, Description
2025-12-11
(CWE 4.19, 2025-12-11)
CWE Content Team
MITRE
updated Weakness_Ordinalities
2024-02-29
(CWE 4.14, 2024-02-29)
CWE Content Team
MITRE
updated Demonstrative_Examples
2023-06-29
(CWE 4.12, 2023-06-29)
CWE Content Team
MITRE
updated Mapping_Notes
2023-04-27
(CWE 4.11, 2023-04-27)
CWE Content Team
MITRE
updated Relationships
2022-10-13
(CWE 4.9, 2022-10-13)
CWE Content Team
MITRE
updated Demonstrative_Examples
2022-06-28
(CWE 4.8, 2022-06-28)
CWE Content Team
MITRE
updated Relationships
2021-10-28
(CWE 4.6, 2021-10-28)
CWE Content Team
MITRE
updated Maintenance_Notes, References, Relationships, Type
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are typically associated with CPUs, Graphics, Vision, AI, FPGA, and microcontrollers.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1252: CPU Hardware Not Configured to Support Exclusivity of Write and Execute Operations
Weakness ID: 1252
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The CPU is not configured to provide hardware support for exclusivity of write and execute operations on memory. This allows an attacker to execute data from all of memory.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Execute Unauthorized Code or Commands
Scope: Confidentiality, Integrity
Without configuring exclusivity of operations via segregated areas of memory, an attacker may be able to inject malicious code onto memory and later execute it.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Implement a dedicated bit that can be leveraged by the Operating System to mark data areas as non-executable. If such a bit is not available in the CPU, implement MMU/MPU (memory management unit / memory protection unit).
Integration
If MMU/MPU are not available, then the firewalls need to be implemented in the SoC interconnect to mimic the write-exclusivity operation.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
CPUs provide a special bit that supports exclusivity of write and execute operations. This bit is used to segregate areas of memory to either mark them as code (instructions, which can be executed) or data (which should not be executed). In this way, if a user can write to a region of memory, the user cannot execute from that region and vice versa. This exclusivity provided by special hardware bit is leveraged by the operating system to protect executable space. While this bit is available in most modern processors by default, in some CPUs the exclusivity is implemented via a memory-protection unit (MPU) and memory-management unit (MMU) in which memory regions can be carved out with exact read, write, and execute permissions.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
If the CPU does not have an MMU/MPU, then there is no write exclusivity.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
MCS51 Microcontroller (based on 8051) does not have a special bit to support write exclusivity. It also does not have an MMU/MPU support. The Cortex-M CPU has an optional MPU that supports up to 8 regions.
(bad code)
Example Language: Other
The optional MPU is not configured.
If the MPU is not configured, then an attacker will be able to inject malicious data into memory and execute it.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category can arise in multiple areas of hardware design or can apply to a wide cross-section of components.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1279: Cryptographic Operations are Run Before Supporting Units are Ready
Weakness ID: 1279
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Performing cryptographic operations without ensuring that the supporting inputs are ready to supply valid data may compromise the cryptographic result.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Best practices should be used to design cryptographic systems. If a cryptographic unit retrieves a private encryption key from a fuse unit, the fuse unit must be up and running before a key may be supplied.
Implementation
Continuously ensuring that cryptographic inputs are supplying valid information is necessary to ensure that the encrypted output is secure.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Many cryptographic hardware units depend upon other hardware units to supply information to them to produce a securely encrypted result. For example, a cryptographic unit that depends on an external random-number-generator (RNG) unit for entropy must wait until the RNG unit is producing random numbers.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
The decision to continue using a cryptographic unit even though the input units to it are not producing valid data will compromise the encrypted result.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following pseudocode illustrates the weak encryption resulting from the use of a pseudo-random-number generator output.
(bad code)
Example Language: Pseudocode
If random_number_generator_self_test_passed() == TRUE
then Seed = get_random_number_from_RNG()
else Seed = hardcoded_number
In the example above, first a check of RNG ready is performed. If the check fails, the RNG is ignored and a hard coded value is used instead. The hard coded value severely weakens the encrypted output.
(good code)
Example Language: Pseudocode
If random_number_generator_self_test_passed() == TRUE
then Seed = get_random_number_from_RNG()
else enter_error_state()
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to hardware debug and test interfaces such as JTAG and scan chain.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1295: Debug Messages Revealing Unnecessary Information
Weakness ID: 1295
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product fails to adequately prevent the revealing of unnecessary and potentially sensitive system information within debugging messages.
Extended Description
Debug messages are messages that help troubleshoot an issue by revealing the internal state of the system. For example, debug data in design can be exposed through internal memory array dumps or boot logs through interfaces like UART via TAP commands, scan chain, etc. Thus, the more information contained in a debug message, the easier it is to debug. However, there is also the risk of revealing information that could help an attacker either decipher a vulnerability, and/or gain a better understanding of the system. Thus, this extra information could lower the "security by obscurity" factor. While "security by obscurity" alone is insufficient, it can help as a part of "Defense-in-depth".
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Bypass Protection Mechanism; Gain Privileges or Assume Identity; Varies by Context
Ensure that a debug message does not reveal any unnecessary information during the debug process for the intended response.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Insertion of Sensitive Information Into Debugging Code
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example here shows how an attacker can take advantage of unnecessary information in debug messages.
Example 1: Suppose in response to a Test Access Port (TAP) chaining request the debug message also reveals the current TAP hierarchy (the full topology) in addition to the success/failure message.
Example 2: In response to a password-filling request, the debug message, instead of a simple Granted/Denied response, prints an elaborate message, "The user-entered password does not match the actual password stored in <directory name>."
The result of the above examples is that the user is able to gather additional unauthorized information about the system from the debug messages.
The solution is to ensure that Debug messages do not reveal additional details.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Sensitive Information Exposure
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The credentials necessary for unlocking a device are shared across multiple parties and may expose sensitive information.
Extended Description
"Unlocking a device" often means activating certain unadvertised debug and manufacturer-specific capabilities of a device using sensitive credentials. Unlocking a device might be necessary for the purpose of troubleshooting device problems. For example, suppose a device contains the ability to dump the content of the full system memory by disabling the memory-protection mechanisms. Since this is a highly security-sensitive capability, this capability is "locked" in the production part. Unless the device gets unlocked by supplying the proper credentials, the debug capabilities are not available. For cases where the chip designer, chip manufacturer (fabricator), and manufacturing and assembly testers are all employed by the same company, the risk of compromise of the credentials is greatly reduced. However, the risk is greater when the chip designer is employed by one company, the chip manufacturer is employed by another company (a foundry), and the assemblers and testers are employed by yet a third company. Since these different companies will need to perform various tests on the device to verify correct device function, they all need to share the unlock key. Unfortunately, the level of secrecy and policy might be quite different at each company, greatly increasing the risk of sensitive credentials being compromised.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Modify Files or Directories; Read Files or Directories; Modify Application Data; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism
Once unlock credentials are compromised, an attacker can use the credentials to unlock the device and gain unauthorized access to the hidden functionalities protected by those credentials.
Potential Mitigations
Phase(s)
Mitigation
Integration
Ensure the unlock credentials are shared with the minimum number of parties and with utmost secrecy. To limit the risk associated with compromised credentials, where possible, the credentials should be part-specific.
Manufacturing
Ensure the unlock credentials are shared with the minimum number of parties and with utmost secrecy. To limit the risk associated with compromised credentials, where possible, the credentials should be part-specific.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Integration
Manufacturing
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
VHDL
(Undetermined Prevalence)
Verilog
(Undetermined Prevalence)
Class: Compiled
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Other
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example shows how an attacker can take advantage of compromised credentials.
(bad code)
Example Language: Other
Suppose a semiconductor chipmaker, "C", uses the foundry "F" for fabricating its chips. Now, F has many other customers in addition to C, and some of the other customers are much smaller companies. F has dedicated teams for each of its customers, but somehow it mixes up the unlock credentials and sends the unlock credentials of C to the wrong team. This other team does not take adequate precautions to protect the credentials that have nothing to do with them, and eventually the unlock credentials of C get leaked.
When the credentials of multiple organizations are stored together, exposure to third parties occurs frequently.
(good code)
Example Language: Other
Vertical integration of a production company is one effective method of protecting sensitive credentials. Where vertical integration is not possible, strict access control and need-to-know are methods which can be implemented to reduce these risks.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Sensitive Information Exposure
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
CWE-1190: DMA Device Enabled Too Early in Boot Phase
Weakness ID: 1190
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product enables a Direct Memory Access (DMA) capable device before the security configuration settings are established, which allows an attacker to extract data from or gain privileges on the product.
Extended Description
Several virtualization-based mitigations have been introduced to thwart DMA attacks. These are usually
configured/setup during boot time. However, certain IPs that are
powered up before boot is complete (known as early boot IPs) may
be DMA capable. Such IPs, if not trusted, could launch DMA
attacks and gain access to assets that should otherwise be
protected.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism; Modify Memory
Scope: Access ControlLikelihood: High
An attacker could exploit this to
access secrets. DMA devices have direct write access to main memory and
due to time of attack will be able to bypass OS or Bootloader
access control.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Utilize an IOMMU to orchestrate IO access from
the start of the boot process.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
DMA is included in a number of devices because it allows
data transfer between the computer and the connected device, using
direct hardware access to read or write directly to main memory
without any OS interaction.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Insufficient Control Flow Management
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1431: Driving Intermediate Cryptographic State/Results to Hardware Module Outputs
Weakness ID: 1431
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses a hardware module implementing a cryptographic
algorithm that writes sensitive information about the intermediate
state or results of its cryptographic operations via one of its output
wires (typically the output port containing the final result).
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data
Scope: ConfidentialityLikelihood: Unknown
Mathematically sound cryptographic algorithms rely on their
correct implementation for security. These assumptions might break when a
hardware crypto module leaks intermediate encryption states or results
such that they can be observed by an adversary. If intermediate state
is observed, it might be possible for an attacker to identify the
secrets used in the cryptographic operation.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Designers/developers
should add or modify existing control flow
logic along any data flow paths that
connect "sources" (signals with
intermediate cryptographic state/results)
with "sinks" (hardware module outputs and
other signals outside of trusted
cryptographic zone). The control flow
logic should only allow cryptographic
results to be driven to "sinks" when
appropriate conditions are satisfied
(typically when the final result for a
cryptographic operation has been
generated). When the appropriate
conditions are not satisfied (i.e., before
or during a cryptographic operation), the
control flow logic should drive a safe
default value to
"sinks".
Effectiveness: High
Implementation
Designers/developers
should add or modify existing control flow
logic along any data flow paths that
connect "sources" (signals with
intermediate cryptographic state/results)
with "sinks" (hardware module outputs and
other signals outside of trusted
cryptographic zone). The control flow
logic should only allow cryptographic
results to be driven to "sinks" when
appropriate conditions are satisfied
(typically when the final result for a
cryptographic operation has been
generated). When the appropriate
conditions are not satisfied (i.e., before
or during a cryptographic operation), the
control flow logic should drive a safe
default value to
"sinks".
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive System Information to an Unauthorized Control Sphere
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive System Information Due to Uncleared Debug Information
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
This can occur when intermediate cryptographic states are
directly assigned to output wires or ports.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following SystemVerilog code is a crypto module that takes input
data and encrypts it by processing the data through multiple
encryption rounds. Note: this example is derived from [REF-1469].
In line 50 above, data_state_q is assigned to data_o. Since data_state_q
contains intermediate state/results, this allows an attacker to obtain
these results through data_o.
In line 50 of the fixed logic below,
while "data_state_q" does not contain the final result,
a "sanitizing" mechanism drives a safe default value (i.e., 0) to
"data_o" instead of the value of "data_state_q".
In doing so, the mechanism prevents
the exposure of intermediate state/results which could be used to
break soundness of the cryptographic operation being performed. A
real-world example of this weakness and mitigation can be seen in a
pull request that was submitted to the OpenTitan Github repository
[REF-1469].
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis - Source Code
Automated static analysis can find some instances of this
weakness by analyzing source register-transfer level (RTL) code
without having to simulate it or analyze it with a formal verification
engine. Typically, this is done by building a model of data flow and
control flow, then searching for potentially-vulnerable patterns that
connect "sources" (signals with intermediate cryptographic
state/results) with "sinks" (hardware module outputs and other signals
outside of trusted cryptographic zone) without any control flow.
Effectiveness: High
Note:
Static code analysis can sometimes lead to false positives.
Simulation / Emulation
Simulation/emulation based analysis can find some instances of
this weakness by simulating source register-transfer level (RTL) code
along with a set of assertions that incorporate the simulated values
of relevant design signals. Typically, these assertions will capture
desired or undesired behavior. Analysis can be improved by using
simulation-based information flow tracking (IFT) to more precisely
detect unexpected results.
Effectiveness: High
Note:
Simulation/emulation based analysis can sometimes lead to false
negatives if the testbench does not drive the design to a design state
in which the assertion would fail.
Formal Verification
Formal verification can find some instances of this weakness by
exhaustively analyzing whether a given assertion holds true for a
given hardware design specified in register-transfer level (RTL)
code. Typically, these assertions will capture desired or undesired
behavior. For this weakness, an assertion should check for undesired
behavior in which one output is a signal that captures when a
cryptographic algorithm has completely finished; another output is a
signal with intermediate cryptographic state/results; and there is an
assignment to a hardware module output or other signal outside of a
trusted cryptographic zone.
Alternatively, when using a formal IFT verification, the same
undesired behavior can be detected by checking if computation results
can ever leak to an output when the cryptographic result is not
complete.
Effectiveness: High
Note:
Formal verification may not scale for RTL designs with a large state space.
Manual Analysis
Manual analysis can find some instances of this weakness by
manually reviewing relevant lines of source register-transfer level
(RTL) code to detect potentially-vulnerable patterns. Typically, the
reviewer will trace the sequence of assignments that connect "sources"
(signals with intermediate cryptographic state/results) with "sinks"
(hardware module outputs and other signals outside of trusted
cryptographic zone). If this sequence of assignments is missing
adequate control flow, then the weakness is likely to exist.
Effectiveness: Opportunistic
Note:
Manual analysis of source code is prone to errors (false
positives and false negatives) and highly opportunistic.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
References
[REF-1469]
Andres Meza. "OpenTitan issue: [otp_ctrl] Prevent broadcast of scrambler's input/intermediate values #13043". 2022-06-03.
<https://github.com/lowRISC/opentitan/pull/13043>.
(URL validated: 2025-04-02)
[REF-1470]
Andres Meza, Francesco Restuccia, Jason Oberg, Dominic Rizzo and Ryan Kastner. "Security Verification of the OpenTitan Hardware Root of Trust". 2023-04-20.
<https://ieeexplore.ieee.org/document/10106105>.
(URL validated: 2025-04-02)
Christophe Clavier, Quentin Isorez, Damien Marion and Antoine Wurcker. "Complete reverse-engineering of AES-like block ciphers by SCARE and FIRE attacks". 2014-10-23.
<https://doi.org/10.1007/s12095-014-0112-7>.
(URL validated: 2025-04-02)
[REF-1473]
Dirmanto Jap and Shivam Bhasin. "Practical Reverse Engineering of Secret Sboxes by Side-Channel Analysis". 2020-10.
<https://doi.org/10.1109/ISCAS45731.2020.9180848>.
(URL validated: 2025-04-02)
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A feature, API, or function does not perform according to its specification.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Quality Degradation; Varies by Context
Scope: Other
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Operation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: ICS/OT
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The provided code is extracted from the Control and Status Register (CSR), csr_regfile, module within the Hack@DAC'21 OpenPiton System-on-Chip (SoC). This module is designed to implement CSR registers in accordance with the RISC-V specification. The mie (machine interrupt enable) register is a 64-bit register [REF-1384], where bits correspond to different interrupt sources. As the name suggests, mie is a machine-level register that determines which interrupts are enabled. Note that in the example below the mie_q and mie_d registers represent the conceptual mie register in the RISC-V specification. The mie_d register is the value to be stored in the mie register while the mie_q register holds the current value of the mie register [REF-1385].
The mideleg (machine interrupt delegation) register, also 64-bit wide, enables the delegation of specific interrupt sources from machine privilege mode to lower privilege levels. By setting specific bits in the mideleg register, the handling of certain interrupts can be delegated to lower privilege levels without engaging the machine-level privilege mode. For example, in supervisor mode, the mie register is limited to a specific register called the sie (supervisor interrupt enable) register. If delegated, an interrupt becomes visible in the sip (supervisor interrupt pending) register and can be enabled or blocked using the sie register. If no delegation occurs, the related bits in sip and sie are set to zero.
The sie register value is computed based on the current value of mie register, i.e., mie_q, and the mideleg register.
// the mideleg makes sure only delegate-able register
//(and therefore also only implemented registers) are written mie_d = (mie_q & ~mideleg_q) | (csr_wdata & mideleg_q) | utval_q;
end
...
endcase
end
endmodule
The above code snippet illustrates an instance of a vulnerable implementation of the sie register update logic, where users can tamper with the mie_d register value through the utval (user trap value) register. This behavior violates the RISC-V specification.
The code shows that the value of utval, among other signals, is used in updating the mie_d value within the sie update logic. While utval is a register accessible to users, it should not influence or compromise the integrity of sie. Through manipulation of the utval register, it becomes feasible to manipulate the sie register's value. This opens the door for potential attacks, as an adversary can gain control over or corrupt the sie value. Consequently, such manipulation empowers an attacker to enable or disable critical supervisor-level interrupts, resulting in various security risks such as privilege escalation or denial-of-service attacks.
A fix to this issue is to remove the utval from the right-hand side of the assignment. That is the value of the mie_d should be updated as shown in the good code example [REF-1386].
// the mideleg makes sure only delegate-able register
//(and therefore also only implemented registers) are written mie_d = (mie_q & ~mideleg_q) | (csr_wdata & mideleg_q);
end
...
endcase
end
endmodule
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Buffer overflow in product stems the use of a third party library function that is expected to have internal protection against overflows, but doesn't.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Theoretical
The behavior of an application that is not consistent with the expectations of the developer may lead to incorrect use of the software.
CWE-1422: Exposure of Sensitive Information caused by Incorrect Data Forwarding during Transient Execution
Weakness ID: 1422
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A processor event or prediction may allow incorrect or stale data to
be forwarded to transient operations, potentially exposing data over a
covert channel.
Extended Description
Software may use a variety of techniques to preserve the
confidentiality of private data that is accessible within the current
processor context. For example, the memory safety and type safety
properties of some high-level programming languages help to prevent
software written in those languages from exposing private data. As a
second example, software sandboxes may co-locate multiple users'
software within a single process. The processor's Instruction Set
Architecture (ISA) may permit one user's software to access another
user's data (because the software shares the same address space), but
the sandbox prevents these accesses by using software techniques such
as bounds checking.
If incorrect or stale data can be forwarded (for example, from a
cache) to transient operations, then the operations'
microarchitectural side effects may correspond to the data. If an
attacker can trigger these transient operations and observe their side
effects through a covert channel, then the attacker may be able to
infer the data. For example, an attacker process may induce transient
execution in a victim process that causes the victim to inadvertently
access and then expose its private data via a covert channel. In the
software sandbox example, an attacker sandbox may induce transient
execution in its own code, allowing it to transiently access and
expose data in a victim sandbox that shares the same address space.
Consequently, weaknesses that arise from incorrect/stale data
forwarding might violate users' expectations of software-based memory
safety and isolation techniques. If the data forwarding behavior is
not properly documented by the hardware vendor, this might violate the
software vendor's expectation of how the hardware should behave.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: ConfidentialityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The hardware designer can attempt to prevent transient
execution from causing observable discrepancies in specific covert
channels.
Effectiveness: Limited
Note: Instructions or features that constrain transient execution or suppress its side effects may impact performance.
Requirements
Processor designers, system software vendors, or other
agents may choose to restrict the ability of unprivileged software to
access to high-resolution timers that are commonly used to monitor
covert channels.
Effectiveness: Defense in Depth
Note: Disabling specific predictors or other hardware features may result in significant performance overhead.
Requirements
Processor designers may expose instructions or other
architectural features that allow software to mitigate the effects of
transient execution, but without disabling predictors. These features
may also help to limit opportunities for data exposure.
Effectiveness: Moderate
Note:
Instructions or features that constrain transient
execution or suppress its side effects may impact performance.
Requirements
Processor designers may expose registers (for example,
control registers or model-specific registers) that allow privileged
and/or user software to disable specific predictors or other hardware
features that can cause confidential data to be exposed during
transient execution.
Effectiveness: Limited
Note:
Disabling specific predictors or other hardware
features may result in significant performance overhead.
Build and Compilation
Use software techniques (including the use of
serialization instructions) that are intended to reduce the number of
instructions that can be executed transiently after a processor event
or misprediction.
Effectiveness: Incidental
Note:
Some transient execution weaknesses can be
exploited even if a single instruction is executed transiently after a
processor event or mis-prediction. This mitigation strategy has many
other pitfalls that prevent it from eliminating this weakness
entirely. For example, see [REF-1389].
Build and Compilation
Isolate sandboxes or managed runtimes in separate address
spaces (separate processes).
Effectiveness: High
Note:
Process isolation is also an effective strategy
to mitigate many other kinds of weaknesses.
Build and Compilation
Include serialization instructions (for example, LFENCE)
that prevent processor events or mis-predictions prior to the
serialization instruction from causing transient execution after the
serialization instruction. For some weaknesses, a serialization
instruction can also prevent a processor event or a mis-prediction
from occurring after the serialization instruction (for example,
CVE-2018-3639 can allow a processor to predict that a load will not
depend on an older store; a serialization instruction between the
store and the load may allow the store to update memory and prevent
the mis-prediction from happening at all).
Effectiveness: Moderate
Note:
When used to comprehensively mitigate a transient
execution weakness, serialization instructions can introduce
significant performance overhead.
Build and Compilation
Use software techniques that can mitigate the
consequences of transient execution. For example, address masking can
be used in some circumstances to prevent out-of-bounds transient
reads.
Effectiveness: Limited
Note:
Address masking and related software mitigation
techniques have been used to harden specific code sequences that could
potentially be exploited via transient execution. For example, the
Linux kernel makes limited use of this technique to mitigate
bounds-check bypass [REF-1390].
Build and Compilation
If the weakness is exposed by a single instruction (or a
small set of instructions), then the compiler (or JIT, etc.) can be
configured to prevent the affected instruction(s) from being
generated, and instead generate an alternate sequence of instructions
that is not affected by the weakness.
Effectiveness: Limited
Note:
This technique is only effective for software
that is compiled with this mitigation.
Documentation
If a hardware feature can allow incorrect or stale data
to be forwarded to transient operations, the hardware designer may opt
to disclose this behavior in architecture documentation. This
documentation can inform users about potential consequences and
effective mitigations.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced by data speculation techniques,
or when the processor pipeline is designed to check exception
conditions concurrently with other operations. This weakness can also
persist after a CWE-1421 weakness has been mitigated. For example,
suppose that a processor can forward stale data from a shared
microarchitectural buffer to dependent transient operations, and
furthermore suppose that the processor has been patched to flush the
buffer on context switches. This mitigates the CWE-1421 weakness, but the
stale-data forwarding behavior may persist as a CWE-1422 weakness unless
this behavior is also patched.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Faulting loads in a victim domain may trigger incorrect transient
forwarding, which leaves secret-dependent traces in the
microarchitectural state. Consider this code sequence example from
[REF-1391].
A processor with this weakness will store the value of untrusted_arg
(which may be provided by an attacker) to the stack, which is trusted
memory. Additionally, this store operation will save this value in
some microarchitectural buffer, for example, the store buffer.
In this code sequence, trusted_ptr is dereferenced while the attacker
forces a page fault. The faulting load causes the processor to
mis-speculate by forwarding untrusted_arg as the (transient) load
result. The processor then uses untrusted_arg for the pointer
dereference. After the fault has been handled and the load has been
re-issued with the correct argument, secret-dependent information
stored at the address of trusted_ptr remains in microarchitectural
state and can be extracted by an attacker using a vulnerable code
sequence.
Example 2
Some processors try to predict when a store will forward data to a
subsequent load, even when the address of the store or the load is not
yet known. For example, on Intel processors this feature is called a
Fast Store Forwarding Predictor [REF-1392], and on AMD processors the
feature is called Predictive Store Forwarding [REF-1393]. A
misprediction can cause incorrect or stale data to be forwarded from a
store to a load, as illustrated in the following code snippet from
[REF-1393]:
In this example, assume that the parameter idx can only be 0 or 1, and
assume that idx_array initially contains all 0s. Observe that the
assignment to v in line 4 will be array[0], regardless of whether
idx=0 or idx=1. Now suppose that an attacker repeatedly invokes fn
with idx=0 to train the store forwarding predictor to predict that the
store in line 3 will forward the data 4096 to the load idx_array[idx]
in line 4. Then, when the attacker invokes fn with idx=1 the predictor
may cause idx_array[idx] to transiently produce the incorrect value
4096, and therefore v will transiently be assigned the value
array[4096], which otherwise would not have been accessible in line 4.
Although this toy example is benign (it doesn't transmit array[4096]
over a covert channel), an attacker may be able to use similar
techniques to craft and train malicious code sequences to, for
example, read data beyond a software sandbox boundary.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
A fault, microcode assist, or abort may allow transient
load operations to forward malicious stale data to dependent
operations executed by a victim, causing the victim to unintentionally
access and potentially expose its own data over a covert channel.
A fast store forwarding predictor may allow store
operations to forward incorrect data to transient load operations,
potentially exposing data over a covert channel.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis
A variety of automated static analysis tools can identify
potentially exploitable code sequences in software. These tools may
perform the analysis on source code, on binary code, or on an
intermediate code representation (for example, during compilation).
Effectiveness: Moderate
Note:Automated static analysis may not reveal all weaknesses in a processor
specification and should be combined with other detection methods to improve coverage.
Manual Analysis
This weakness can be detected in hardware by manually
inspecting processor specifications. Features that exhibit this
weakness may include microarchitectural predictors, access control
checks that occur out-of-order, or any other features that can allow
operations to execute without committing to architectural state.Hardware designers can also scrutinize aspects
of the instruction set architecture that have undefined
behavior; these can become a focal point
when applying other detection methods.
Effectiveness: Moderate
Note:Manual analysis may not reveal all weaknesses in a processor specification
and should be combined with other detection methods to improve coverage.
Automated Analysis
Software vendors can release tools that detect presence of known
weaknesses on a processor. For example, some of these tools can
attempt to transiently execute a vulnerable code sequence and detect
whether code successfully leaks data in a manner consistent with the
weakness under test. Alternatively, some hardware vendors provide
enumeration for the presence of a weakness (or lack of a
weakness). These enumeration bits can be checked and reported by
system software. For example, Linux supports these checks for many
commodity processors:
Note:This method can be useful for detecting whether a processor if affected by known weaknesses, but it may not be useful for detecting unknown weaknesses.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities
Comments
Use only when the weakness arises from forwarding of
incorrect/stale data, and the data is not architecturally
restricted (that is, the forwarded data is accessible within the current processor context).
If a weakness arises from forwarding of
incorrect/stale data that is not accessible within the current
processor context, then CWE-1421 may be more appropriate for
the mapping task.
References
[REF-1389]
Alyssa Milburn, Ke Sun and Henrique Kawakami. "You Cannot Always Win the Race: Analyzing the LFENCE/JMP Mitigation for Branch Target Injection". 2022-03-08.
<https://arxiv.org/abs/2203.04277>.
(URL validated: 2024-02-22)
Jo Van Bulck, Daniel Moghimi, Michael Schwarz, Moritz Lipp, Marina Minkin, Daniel Genkin, Yuval Yarom, Berk Sunar, Daniel Gruss and Frank Piessens. "LVI : Hijacking Transient Execution through Microarchitectural Load Value Injection". 2020-01-09.
<https://lviattack.eu/lvi.pdf>.
(URL validated: 2024-02-04)
CWE-1423: Exposure of Sensitive Information caused by Shared Microarchitectural Predictor State that Influences Transient Execution
Weakness ID: 1423
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Shared microarchitectural predictor state may allow code to influence
transient execution across a hardware boundary, potentially exposing
data that is accessible beyond the boundary over a covert channel.
Extended Description
Many commodity processors have Instruction Set Architecture (ISA)
features that protect software components from one another. These
features can include memory segmentation, virtual memory, privilege
rings, trusted execution environments, and virtual machines, among
others. For example, virtual memory provides each process with its own
address space, which prevents processes from accessing each other's
private data. Many of these features can be used to form
hardware-enforced security boundaries between software components.
When separate software components (for example, two processes) share
microarchitectural predictor state across a hardware boundary, code in
one component may be able to influence microarchitectural predictor
behavior in another component. If the predictor can cause transient
execution, the shared predictor state may allow an attacker to
influence transient execution in a victim, and in a manner that could
allow the attacker to infer private data from the victim by monitoring
observable discrepancies (CWE-203) in a covert channel [REF-1400].
Predictor state may be shared when the processor transitions from one
component to another (for example, when a process makes a system call
to enter the kernel). Many commodity processors have features which
prevent microarchitectural predictions that occur before a boundary
from influencing predictions that occur after the boundary.
Predictor state may also be shared between hardware threads, for
example, sibling hardware threads on a processor that supports
simultaneous multithreading (SMT). This sharing may be benign if the
hardware threads are simultaneously executing in the same software
component, or it could expose a weakness if one sibling is a malicious
software component, and the other sibling is a victim software
component. Processors that share microarchitectural predictors between
hardware threads may have features which prevent microarchitectural
predictions that occur on one hardware thread from influencing
predictions that occur on another hardware thread.
Features that restrict predictor state sharing across transitions or
between hardware threads may be always-on, on by default, or may
require opt-in from software.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: ConfidentialityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The hardware designer can attempt to prevent transient
execution from causing observable discrepancies in specific covert
channels.
Architecture and Design
Hardware designers may choose to use microarchitectural
bits to tag predictor entries. For example, each predictor entry may
be tagged with a kernel-mode bit which, when set, indicates that the
predictor entry was created in kernel mode. The processor can use this
bit to enforce that predictions in the current mode must have been
trained in the current mode. This can prevent malicious cross-mode
training, such as when user-mode software attempts to create predictor
entries that influence transient execution in the kernel. Predictor
entry tags can also be used to associate each predictor entry with the
SMT thread that created it, and thus the processor can enforce that
each predictor entry can only be used by the SMT thread that created
it. This can prevent an SMT thread from using predictor entries
crafted by a malicious sibling SMT thread.
Effectiveness: Moderate
Note:
Tagging can be highly effective for predictor
state that is comprised of discrete elements, such as an array of
recently visited branch targets. Predictor state can also have
different representations that are not conducive to tagging. For
example, some processors keep a compressed digest of branch history
which does not contain discrete elements that can be individually
tagged.
Architecture and Design
Hardware designers may choose to sanitize
microarchitectural predictor state (for example, branch prediction
history) when the processor transitions to a different context, for
example, whenever a system call is invoked. Alternatively, the
hardware may expose instruction(s) that allow software to sanitize
predictor state according to the user's threat model. For example,
this can allow operating system software to sanitize predictor state
when performing a context switch from one process to another.
Effectiveness: Moderate
Note:
This technique may not be able to mitigate
weaknesses that arise from predictor state that is shared across SMT
threads. Sanitizing predictor state on context switches may also
negatively impact performance, either by removing predictor entries
that could be reused when returning to the previous context, or by
slowing down the context switch itself.
Implementation
System software can mitigate this weakness by invoking
predictor-state-sanitizing operations (for example, the indirect
branch prediction barrier on Intel x86) when switching from one
context to another, according to the hardware vendor's
recommendations.
Effectiveness: Moderate
Note:
This technique may not be able to mitigate
weaknesses that arise from predictor state shared across SMT
threads. Sanitizing predictor state may also negatively impact
performance in some circumstances.
Build and Compilation
If the weakness is exposed by a single instruction (or a
small set of instructions), then the compiler (or JIT, etc.) can be
configured to prevent the affected instruction(s) from being
generated. One prominent example of this mitigation is retpoline
([REF-1414]).
Effectiveness: Limited
Note:
This technique is only effective for software
that is compiled with this mitigation. Additionally, an alternate
instruction sequence may mitigate the weakness on some processors but
not others, even when the processors share the same ISA. For example,
retpoline has been documented as effective on some x86 processors, but
not fully effective on other x86 processors.
Build and Compilation
Use control-flow integrity (CFI) techniques to constrain
the behavior of instructions that redirect the instruction pointer,
such as indirect branch instructions.
Effectiveness: Moderate
Note:
Some CFI techniques may not be able to constrain
transient execution, even though they are effective at constraining
architectural execution. Or they may be able to provide some
additional protection against a transient execution weakness, but
without comprehensively mitigating the weakness. For example,
Clang-CFI provides strong architectural CFI properties and can make
some transient execution weaknesses more difficult to exploit [REF-1398].
Build and Compilation
Use software techniques (including the use of
serialization instructions) that are intended to reduce the number of
instructions that can be executed transiently after a processor event
or misprediction.
Effectiveness: Incidental
Note:
Some transient execution weaknesses can be
exploited even if a single instruction is executed transiently after a
processor event or mis-prediction. This mitigation strategy has many
other pitfalls that prevent it from eliminating this weakness
entirely. For example, see [REF-1389].
System Configuration
Some systems may allow the user to disable predictor
sharing. For example, this could be a BIOS configuration, or a
model-specific register (MSR) that can be configured by the operating
system or virtual machine monitor.
Effectiveness: Moderate
Note:
Disabling predictor sharing can negatively impact
performance for some workloads that benefit from shared predictor
state.
Patching and Maintenance
The hardware vendor may provide a patch to, for example,
sanitize predictor state when the processor transitions to a different
context, or to prevent predictor entries from being shared across SMT
threads. A patch may also introduce new ISA that allows software to
toggle a mitigation.
Effectiveness: Moderate
Note:
This mitigation may only be fully effective if
the patch prevents predictor sharing across all contexts that are
affected by the weakness. Additionally, sanitizing predictor state
and/or preventing shared predictor state can negatively impact
performance in some circumstances.
Documentation
If a hardware feature can allow microarchitectural
predictor state to be shared between contexts, SMT threads, or other
architecturally defined boundaries, the hardware designer may opt to
disclose this behavior in architecture documentation. This
documentation can inform users about potential consequences and
effective mitigations.
Effectiveness: High
Requirements
Processor designers, system software vendors, or other
agents may choose to restrict the ability of unprivileged software to
access to high-resolution timers that are commonly used to monitor
covert channels.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced during hardware architecture and
design if predictor state is not properly isolated between modes (for
example, user mode and kernel mode), if predictor state is not
isolated between hardware threads, or if it is not isolated between
other kinds of execution contexts supported by the processor.
Implementation
This weakness can be introduced during system software
implementation if predictor-state-sanitizing operations (for example,
the indirect branch prediction barrier on Intel x86) are not invoked
when switching from one context to another.
System Configuration
This weakness can be introduced if the system has not been
configured according to the hardware vendor's recommendations for
mitigating the weakness.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Branch Target Injection (BTI) is a vulnerability that can allow an SMT
hardware thread to maliciously train the indirect branch predictor
state that is shared with its sibling hardware thread. A cross-thread
BTI attack requires the attacker to find a vulnerable code sequence
within the victim software. For example, the authors of [REF-1415]
identified the following code sequence in the Windows library
ntdll.dll:
jmp dword ptr [rsi] # at this point attacker knows edx, controls edi and ebx
To successfully exploit this code sequence to disclose the victim's
private data, the attacker must also be able to find an indirect
branch site within the victim, where the attacker controls the values
in edi and ebx, and the attacker knows the value in edx as shown above
at the indirect branch site.
A proof-of-concept cross-thread BTI attack might proceed as follows:
The attacker thread and victim thread must be co-scheduled on the same physical processor core.
The attacker thread must train the shared branch predictor so that
when the victim thread reaches indirect_branch_site, the jmp
instruction will be predicted to target example_code_sequence instead
of the correct architectural target. The training procedure may vary
by processor, and the attacker may need to reverse-engineer the branch
predictor to identify a suitable training algorithm.
This step assumes that the attacker can control some values in the
victim program, specifically the values in edi and ebx at
indirect_branch_site. When the victim reaches indirect_branch_site the
processor will (mis)predict example_code_sequence as the target and
(transiently) execute the adc instructions. If the attacker chooses
ebx so that `ebx = m
0x13BE13BD - edx, then the first adc will load 32 bits from
address m in the victim's address space and add *m (the data loaded from)
to the attacker-controlled base address in edi. The second
adc instruction accesses a location in memory whose address corresponds
to *m`.
The adversary uses a covert channel analysis technique such as
Flush+Reload ([REF-1416]) to infer the value of the victim's private data
*m.
Example 2
BTI can also allow software in one execution context to maliciously
train branch predictor entries that can be used in another
context. For example, on some processors user-mode software may be
able to train predictor entries that can also be used after
transitioning into kernel mode, such as after invoking a system
call. This vulnerability does not necessarily require SMT and may
instead be performed in synchronous steps, though it does require the
attacker to find an exploitable code sequence in the victim's code,
for example, in the kernel.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
(Branch Target Injection, BTI, Spectre v2). Shared
microarchitectural indirect branch predictor state may allow code to
influence transient execution across a process, VM, or privilege
boundary, potentially exposing data that is accessible beyond the
boundary.
(Branch History Injection, BHI, Spectre-BHB). Shared
branch history state may allow user-mode code to influence transient
execution in the kernel, potentially exposing kernel data over a
covert channel.
(RSB underflow, Retbleed). Shared return stack buffer
state may allow code that executes before a prediction barrier to
influence transient execution after the prediction barrier,
potentially exposing data that is accessible beyond the barrier over a
covert channel.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
This weakness can be detected in hardware by manually
inspecting processor specifications. Features that exhibit this
weakness may have microarchitectural predictor state that is shared
between hardware threads, execution contexts (for example, user and
kernel), or other components that may host mutually distrusting
software (or firmware, etc.).
Effectiveness: Moderate
Note:Manual analysis may not reveal all weaknesses in a processor specification and should be combined with other detection methods to improve coverage.
Automated Analysis
Software vendors can release tools that detect presence of
known weaknesses on a processor. For example, some of these tools can
attempt to transiently execute a vulnerable code sequence and detect
whether code successfully leaks data in a manner consistent with the
weakness under test. Alternatively, some hardware vendors provide
enumeration for the presence of a weakness (or lack of a
weakness). These enumeration bits can be checked and reported by
system software. For example, Linux supports these checks for many
commodity processors:
Note:This method can be useful for detecting whether a processor if affected by known weaknesses, but it may not be useful for detecting unknown weaknesses
Automated Analysis
This weakness can be detected in hardware by employing static
or dynamic taint analysis methods [REF-1401]. These methods can label
each predictor entry (or prediction history, etc.) according to the
processor context that created it. Taint analysis or information flow
analysis can then be applied to detect when predictor state created in
one context can influence predictions made in another context.
Effectiveness: Moderate
Note:Automated static or dynamic taint analysis may not reveal all weaknesses in a processor specification and should be combined with other detection methods to improve coverage.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities
Comments
Use only when the weakness allows code in one processor context to influence the predictions of code in another processor context via predictor state that is shared between the two contexts. For example, Branch Target Injection, an instance of CWE-1423, can be mitigated by tagging each indirect branch predictor entry according to the processor context in which the entry was created, thus preventing entries created in one context from being used in a different context. However, the mitigated indirect branch predictor can still expose different weaknesses where malicious predictor entries created in one context are used later in the same context (context tags cannot prevent this). One such example is Intra-mode Branch Target Injection. Weaknesses of this sort can map to CWE-1420.
If a weakness involves a microarchitectural predictor whose state is not shared across processor contexts, then CWE-1420 may be more appropriate for the mapping task.
Paul Kocher, Jann Horn, Anders Fogh, Daniel Genkin, Daniel Gruss, Werner Haas, Mike Hamburg, Moritz Lipp, Stefan Mangard, Thomas Prescher, Michael Schwarz and Yuval Yarom. "Spectre Attacks: Exploiting Speculative Execution". 2019-05.
<https://spectreattack.com/spectre.pdf>.
(URL validated: 2024-02-14)
Alyssa Milburn, Ke Sun and Henrique Kawakami. "You Cannot Always Win the Race: Analyzing the LFENCE/JMP Mitigation for Branch Target Injection". 2022-03-08.
<https://arxiv.org/abs/2203.04277>.
(URL validated: 2024-02-22)
Neta Bar Kama and Roope Kaivola. "Hardware Security Leak Detection by Symbolic Simulation". 2021-11.
<https://ieeexplore.ieee.org/document/9617727>.
(URL validated: 2024-02-13)
Content
History
Submissions
Submission Date
Submitter
Organization
2023-09-19
(CWE 4.14, 2024-02-29)
Scott D. Constable
Intel Corporation
Contributions
Contribution Date
Contributor
Organization
2024-01-22
(CWE 4.14, 2024-02-29)
David Kaplan
AMD
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Rafael Dossantos, Abraham Fernandez Rubio, Alric Althoff, Lyndon Fawcett
Arm
Members of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Jason Oberg
Cycuity
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Priya B. Iyer
Intel Corporation
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Nicole Fern
Riscure
Member of Microarchitectural Weaknesses Working Group
CWE-1420: Exposure of Sensitive Information during Transient Execution
Weakness ID: 1420
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A processor event or prediction may allow incorrect operations (or correct operations with incorrect data) to execute transiently, potentially exposing data over a covert channel.
Extended Description
When operations execute but do not commit to the processor's
architectural state, this is commonly referred to as transient
execution. This behavior can occur when the processor mis-predicts an
outcome (such as a branch target), or when a processor event (such as
an exception or microcode assist, etc.) is handled after younger
operations have already executed. Operations that execute transiently
may exhibit observable discrepancies (CWE-203) in covert channels
[REF-1400] such as data caches. Observable discrepancies of this kind
can be detected and analyzed using timing or power analysis
techniques, which may allow an attacker to infer information about the
operations that executed transiently. For example, the attacker may be
able to infer confidential data that was accessed or used by those
operations.
Transient execution weaknesses may be exploited using one of two
methods. In the first method, the attacker generates a code sequence
that exposes data through a covert channel when it is executed
transiently (the attacker must also be able to trigger transient
execution). Some transient execution weaknesses can only expose data
that is accessible within the attacker's processor context. For
example, an attacker executing code in a software sandbox may be able
to use a transient execution weakness to expose data within the same
address space, but outside of the attacker's sandbox. Other transient
execution weaknesses can expose data that is architecturally
inaccessible, that is, data protected by hardware-enforced boundaries
such as page tables or privilege rings. These weaknesses are the
subject of CWE-1421.
In the second exploitation method, the attacker first identifies a
code sequence in a victim program that, when executed transiently, can
expose data that is architecturally accessible within the victim's
processor context. For instance, the attacker may search the victim
program for code sequences that resemble a bounds-check bypass
sequence (see Demonstrative Example 1). If the attacker can trigger a
mis-prediction of the conditional branch and influence the index of
the out-of-bounds array access, then the attacker may be able to infer
the value of out-of-bounds data by monitoring observable discrepancies
in a covert channel.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: ConfidentialityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The hardware designer can attempt to prevent transient execution from causing observable discrepancies in specific covert channels.
Effectiveness: Limited
Note:
This technique has many pitfalls. For example,
InvisiSpec was an early attempt to mitigate this weakness by blocking
"micro-architectural covert and side channels through the
multiprocessor data cache hierarchy due to speculative loads" [REF-1417].
Commodity processors and SoCs have many covert and side channels that
exist outside of the data cache hierarchy. Even when some of these
channels are blocked, others (such as execution ports [REF-1418]) may
allow an attacker to infer confidential data. Mitigation strategies
that attempt to prevent transient execution from causing observable
discrepancies also have other pitfalls, for example, see [REF-1419].
Requirements
Processor designers may expose instructions or other architectural features that allow software to mitigate the effects of transient execution, but without disabling predictors. These features may also help to limit opportunities for data exposure.
Effectiveness: Moderate
Note:
Instructions or features that constrain transient execution or suppress its side effects may impact performance.
Requirements
Processor designers may expose registers (for example, control registers or model-specific registers) that allow privileged and/or user software to disable specific predictors or other hardware features that can cause confidential data to be exposed during transient execution.
Effectiveness: Limited
Note:
Disabling specific predictors or other hardware features may result in significant performance overhead.
Requirements
Processor designers, system software vendors, or other agents may choose to restrict the ability of unprivileged software to access to high-resolution timers that are commonly used to monitor covert channels.
Effectiveness: Defense in Depth
Note:
Specific software algorithms can be used by an attacker to compensate for a lack of a high-resolution time source [REF-1420].
Build and Compilation
Isolate sandboxes or managed runtimes in separate address spaces (separate processes). For examples, see [REF-1421].
Effectiveness: High
Build and Compilation
Include serialization instructions (for example, LFENCE) that prevent processor events or mis-predictions prior to the serialization instruction from causing transient execution after the serialization instruction. For some weaknesses, a serialization instruction can also prevent a processor event or a mis-prediction from occurring after the serialization instruction (for example, CVE-2018-3639 can allow a processor to predict that a load will not depend on an older store; a serialization instruction between the store and the load may allow the store to update memory and prevent the prediction from happening at all).
Effectiveness: Moderate
Note:
When used to comprehensively mitigate a transient execution weakness (for example, by inserting an LFENCE after every instruction in a program), serialization instructions can introduce significant performance overhead. On the other hand, when used to mitigate only a relatively small number of high-risk code sequences, serialization instructions may have a low or negligible impact on performance.
Build and Compilation
Use control-flow integrity (CFI) techniques to constrain the behavior of instructions that redirect the instruction pointer, such as indirect branch instructions.
Effectiveness: Moderate
Note:
Some CFI techniques may not be able to constrain transient execution, even though they are effective at constraining architectural execution. Or they may be able to provide some additional protection against a transient execution weakness, but without comprehensively mitigating the weakness. For example, Clang-CFI provides strong architectural CFI properties and can make some transient execution weaknesses more difficult to exploit [REF-1398].
Build and Compilation
If the weakness is exposed by a single instruction (or a small set of instructions), then the compiler (or JIT, etc.) can be configured to prevent the affected instruction(s) from being generated, and instead generate an alternate sequence of instructions that is not affected by the weakness. One prominent example of this mitigation is retpoline ([REF-1414]).
Effectiveness: Limited
Note:
This technique may only be effective for software that is compiled with this mitigation. For some transient execution weaknesses, this technique may not be sufficient to protect software that is compiled without the affected instruction(s). For example, see CWE-1421.
Build and Compilation
Use software techniques that can mitigate the consequences of transient execution. For example, address masking can be used in some circumstances to prevent out-of-bounds transient reads.
Effectiveness: Limited
Note:
Address masking and related software mitigation techniques have been used to harden specific code sequences that could potentially be exploited via transient execution. For example, the Linux kernel makes limited use of manually inserted address masks to mitigate bounds-check bypass [REF-1390]. Compiler-based techniques have also been used to automatically harden software [REF-1425].
Build and Compilation
Use software techniques (including the use of serialization instructions) that are intended to reduce the number of instructions that can be executed transiently after a processor event or misprediction.
Effectiveness: Incidental
Note:
Some transient execution weaknesses can be exploited even if a single instruction is executed transiently after a processor event or mis-prediction. This mitigation strategy has many other pitfalls that prevent it from eliminating this weakness entirely. For example, see [REF-1389].
Documentation
If a hardware feature can allow incorrect operations (or correct operations with incorrect data) to execute transiently, the hardware designer may opt to disclose this behavior in architecture documentation. This documentation can inform users about potential consequences and effective mitigations.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive Information in Shared Microarchitectural Structures during Transient Execution
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive Information caused by Incorrect Data Forwarding during Transient Execution
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive Information caused by Shared Microarchitectural Predictor State that Influences Transient Execution
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced when a computing unit (such as a CPU, GPU, accelerator, or any other processor) uses out-of-order execution, speculation, or any other microarchitectural feature that can allow microarchitectural operations to execute without committing to architectural state.
Implementation
This weakness can be introduced when sandboxes or managed runtimes are not properly isolated by using hardware-enforced boundaries. Developers of sandbox or managed runtime software should exercise caution when relying on software techniques (such as bounds checking) to prevent code in one sandbox from accessing confidential data in another sandbox. For example, an attacker sandbox may be able to trigger a processor event or mis-prediction in a manner that allows it to transiently read a victim sandbox's private data.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Secure programs perform bounds checking before accessing an array if the source of the array index is provided by an untrusted source such as user input. In the code below, data from array1 will not be accessed if x is out of bounds. The following code snippet is from [REF-1415]:
(bad code)
Example Language: C
if (x < array1_size)
y = array2[array1[x] * 4096];
However, if this code executes on a processor that performs
conditional branch prediction the outcome of the if statement could be
mis-predicted and the access on the next line will occur with a value
of x that can point to an out-of-bounds location (within the program's
memory).
Even though the processor does not commit the architectural effects of
the mis-predicted branch, the memory accesses alter data cache state,
which is not rolled back after the branch is resolved. The cache state
can reveal array1[x] thereby providing a mechanism to recover the data
value located at address array1 + x.
Example 2
Some managed runtimes or just-in-time (JIT) compilers may overwrite recently executed code with new code. When the instruction pointer enters the new code, the processor may inadvertently execute the stale code that had been overwritten. This can happen, for instance, when the processor issues a store that overwrites a sequence of code, but the processor fetches and executes the (stale) code before the store updates memory. Similar to the first example, the processor does not commit the stale code's architectural effects, though microarchitectural side effects can persist. Hence, confidential information accessed or used by the stale code may be inferred via an observable discrepancy in a covert channel. This vulnerability is described in more detail in [REF-1427].
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Microarchitectural conditional branch predictors may allow operations to execute transiently after a misprediction, potentially exposing data over a covert channel.
A machine clear triggered by self-modifying code may allow incorrect operations to execute transiently, potentially exposing data over a covert channel.
Microarchitectural indirect branch predictors may allow incorrect operations to execute transiently after a misprediction, potentially exposing data over a covert channel.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
This weakness can be detected in hardware by manually inspecting processor specifications. Features that exhibit this weakness may include microarchitectural predictors, access control checks that occur out-of-order, or any other features that can allow operations to execute without committing to architectural state. Academic researchers have demonstrated that new hardware weaknesses can be discovered by exhaustively analyzing a processor's machine clear (or nuke) conditions ([REF-1427]).
Effectiveness: Moderate
Note:
Hardware designers can also scrutinize aspects of the instruction set architecture
that have undefined behavior; these can become a focal point when applying other
detection methods.
Manual analysis may not reveal all weaknesses in a processor specification
and should be combined with other detection methods to improve coverage.
Fuzzing
Academic researchers have demonstrated that this weakness can be detected in hardware using software fuzzing tools that treat the underlying hardware as a black box ([REF-1428]).
Effectiveness: Opportunistic
Note:
Fuzzing may not reveal all weaknesses in a processor specification and should
be combined with other detection methods to improve coverage.
Fuzzing
Academic researchers have demonstrated that this weakness can be detected in software using software fuzzing tools ([REF-1429]).
Effectiveness: Opportunistic
Note:
At the time of this writing, publicly available software fuzzing tools can only
detect a subset of transient execution weaknesses in software (for example, [REF-1429] can only
detect instances of Spectre v1) and may produce false positives.
Automated Static Analysis
A variety of automated static analysis tools can identify
potentially exploitable code sequences in software. These tools may
perform the analysis on source code, on binary code, or on an
intermediate code representation (for example, during compilation).
Effectiveness: Limited
Note:
At the time of this writing, publicly available software static analysis tools can
only detect a subset of transient execution weaknesses in software and may produce false
positives.
Automated Analysis
Software vendors can release tools that detect presence of
known weaknesses on a processor. For example, some of these tools can
attempt to transiently execute a vulnerable code sequence and detect
whether code successfully leaks data in a manner consistent with the
weakness under test. Alternatively, some hardware vendors provide
enumeration for the presence of a weakness (or lack of a
weakness). These enumeration bits can be checked and reported by
system software. For example, Linux supports these checks for many
commodity processors:
This method can be useful for detecting whether a processor is affected by
known weaknesses, but it may not be useful for detecting unknown weaknesses.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
A vulnerability should only map to CWE-1420 if it cannot map to any of CWE-1420's child weaknesses. Follow this diagram:
References
[REF-1389]
Alyssa Milburn, Ke Sun and Henrique Kawakami. "You Cannot Always Win the Race: Analyzing the LFENCE/JMP Mitigation for Branch Target Injection". 2022-03-08.
<https://arxiv.org/abs/2203.04277>.
(URL validated: 2024-02-22)
[REF-1417]
Mengjia Yan, Jiho Choi, Dimitrios Skarlatos, Adam Morrison, Christopher W. Fletcher and Josep Torrella. "InvisiSpec: making speculative execution invisible in the cache hierarchy.". 2019-05.
<https://iacoma.cs.uiuc.edu/iacoma-papers/micro18.pdf>.
(URL validated: 2025-08-04)
[REF-1418]
Alejandro Cabrera Aldaya, Billy Bob Brumley, Sohaib ul Hassan, Cesar Pereida García and Nicola Tuveri. "Port Contention for Fun and Profit". 2019-05.
<https://eprint.iacr.org/2018/1060.pdf>.
(URL validated: 2024-02-14)
[REF-1419]
Mohammad Behnia, Prateek Sahu, Riccardo Paccagnella, Jiyong Yu, Zirui Zhao, Xiang Zou, Thomas Unterluggauer, Josep Torrellas, Carlos Rozas, Adam Morrison, Frank Mckeen, Fangfei Liu, Ron Gabor, Christopher W. Fletcher, Abhishek Basak and Alaa Alameldeen. "Speculative Interference Attacks: Breaking Invisible Speculation Schemes". 2021-04.
<https://arxiv.org/abs/2007.11818>.
(URL validated: 2024-02-14)
[REF-1420]
Ross Mcilroy, Jaroslav Sevcik, Tobias Tebbi, Ben L. Titzer and Toon Verwaest. "Spectre is here to stay: An analysis of side-channels and speculative execution". 2019-02-14.
<https://arxiv.org/pdf/1902.05178>.
(URL validated: 2025-08-04)
Hany Ragab, Enrico Barberis, Herbert Bos and Cristiano Giuffrida. "Rage Against the Machine Clear: A Systematic Analysis of Machine Clears and Their Implications for Transient Execution Attacks". 2021-08.
<https://www.usenix.org/system/files/sec21-ragab.pdf>.
(URL validated: 2024-02-14)
[REF-1428]
Oleksii Oleksenko, Marco Guarnieri, Boris Köpf and Mark Silberstein. "Hide and Seek with Spectres: Efficient discovery of speculative information leaks with random testing". 2023-01-18.
<https://arxiv.org/pdf/2301.07642>.
(URL validated: 2025-08-04)
[REF-1429]
Oleksii Oleksenko, Bohdan Trach, Mark Silberstein and Christof Fetzer. "SpecFuzz: Bringing Spectre-type vulnerabilities to the surface". 2020-08.
<https://www.usenix.org/system/files/sec20-oleksenko.pdf>.
(URL validated: 2024-02-14)
[REF-1415]
Paul Kocher, Jann Horn, Anders Fogh, Daniel Genkin, Daniel Gruss, Werner Haas, Mike Hamburg, Moritz Lipp, Stefan Mangard, Thomas Prescher, Michael Schwarz and Yuval Yarom. "Spectre Attacks: Exploiting Speculative Execution". 2019-05.
<https://spectreattack.com/spectre.pdf>.
(URL validated: 2024-02-14)
CWE-1421: Exposure of Sensitive Information in Shared Microarchitectural Structures during Transient Execution
Weakness ID: 1421
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A processor event may allow transient operations to access
architecturally restricted data (for example, in another address
space) in a shared microarchitectural structure (for example, a CPU
cache), potentially exposing the data over a covert channel.
Extended Description
Many commodity processors have Instruction Set Architecture (ISA)
features that protect software components from one another. These
features can include memory segmentation, virtual memory, privilege
rings, trusted execution environments, and virtual machines, among
others. For example, virtual memory provides each process with its own
address space, which prevents processes from accessing each other's
private data. Many of these features can be used to form
hardware-enforced security boundaries between software components.
Many commodity processors also share microarchitectural resources that
cache (temporarily store) data, which may be confidential. These
resources may be shared across processor contexts, including across
SMT threads, privilege rings, or others.
When transient operations allow access to ISA-protected data in a
shared microarchitectural resource, this might violate users'
expectations of the ISA feature that is bypassed. For example, if
transient operations can access a victim's private data in a shared
microarchitectural resource, then the operations' microarchitectural
side effects may correspond to the accessed data. If an attacker can
trigger these transient operations and observe their side effects
through a covert channel [REF-1400], then the attacker may be able to infer the
victim's private data. Private data could include sensitive program
data, OS/VMM data, page table data (such as memory addresses), system
configuration data (see Demonstrative Example 3), or any other data
that the attacker does not have the required privileges to access.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: ConfidentialityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Hardware designers may choose to engineer the processor's
pipeline to prevent architecturally restricted data from being used by
operations that can execute transiently.
Effectiveness: High
Architecture and Design
Hardware designers may choose not to share
microarchitectural resources that can contain sensitive data, such as
fill buffers and store buffers.
Effectiveness: Moderate
Note:
This can be highly effective at preventing this
weakness from being exposed across different SMT threads or different
processor cores. It is generally less practical to isolate these
resources between different contexts (for example, user and kernel)
that may execute on the same SMT thread or processor core.
Architecture and Design
Hardware designers may choose to sanitize specific
microarchitectural state (for example, store buffers) when the
processor transitions to a different context, such as whenever a
system call is invoked. Alternatively, the hardware may expose
instruction(s) that allow software to sanitize microarchitectural
state according to the user or system administrator's threat
model. These mitigation approaches are similar to those that address
CWE-226; however, sanitizing microarchitectural state may not be the
optimal or best way to mitigate this weakness on every processor
design.
Effectiveness: Moderate
Note:
Sanitizing shared state on context transitions
may not be practical for all processors, especially when the amount of
shared state affected by the weakness is relatively
large. Additionally, this technique may not be practical unless there
is a synchronous transition between two processor contexts that would
allow the affected resource to be sanitized. For example, this
technique alone may not suffice to mitigate asynchronous access to a
resource that is shared by two SMT threads.
Architecture and Design
The hardware designer can attempt to prevent transient
execution from causing observable discrepancies in specific covert
channels.
Effectiveness: Limited
Note:
This technique has many pitfalls. For example,
InvisiSpec was an early attempt to mitigate this weakness by blocking
"micro-architectural covert and side channels through the
multiprocessor data cache hierarchy due to speculative loads" [REF-1417].
Commodity processors and SoCs have many covert and side channels that
exist outside of the data cache hierarchy. Even when some of these
channels are blocked, others (such as execution ports [REF-1418]) may
allow an attacker to infer confidential data. Mitigation strategies
that attempt to prevent transient execution from causing observable
discrepancies also have other pitfalls, for example, see [REF-1419].
Architecture and Design
Software architects may design software to enforce strong
isolation between different contexts. For example, kernel page table
isolation (KPTI) mitigates the Meltdown vulnerability [REF-1401] by
separating user-mode page tables from kernel-mode page tables, which
prevents user-mode processes from using Meltdown to transiently access
kernel memory [REF-1404].
Effectiveness: Limited
Note:
Isolating different contexts across a process
boundary (or another kind of architectural boundary) may only be
effective for some weaknesses.
Build and Compilation
If the weakness is exposed by a single instruction (or a
small set of instructions), then the compiler (or JIT, etc.) can be
configured to prevent the affected instruction(s) from being
generated, and instead generate an alternate sequence of instructions
that is not affected by the weakness.
Effectiveness: Limited
Note:
This technique may only be fully effective if it
is applied to all software that runs on the system. Also, relatively
few observed examples of this weakness have exposed data through only
a single instruction.
Build and Compilation
Use software techniques (including the use of
serialization instructions) that are intended to reduce the number of
instructions that can be executed transiently after a processor event
or misprediction.
Effectiveness: Incidental
Note:
Some transient execution weaknesses can be
exploited even if a single instruction is executed transiently after a
processor event or mis-prediction. This mitigation strategy has many
other pitfalls that prevent it from eliminating this weakness
entirely. For example, see [REF-1389].
Implementation
System software can mitigate this weakness by invoking
state-sanitizing operations when switching from one context to
another, according to the hardware vendor's recommendations.
Effectiveness: Limited
Note:
This technique may not be able to mitigate
weaknesses that arise from resource sharing across SMT threads.
System Configuration
Some systems may allow the user to disable (for example,
in the BIOS) sharing of the affected resource.
Effectiveness: Limited
Note:
Disabling resource sharing (for example, by
disabling SMT) may result in significant performance overhead.
System Configuration
Some systems may allow the user to disable (for example,
in the BIOS) microarchitectural features that allow transient access
to architecturally restricted data.
Effectiveness: Limited
Note:
Disabling microarchitectural features such as
predictors may result in significant performance overhead.
Patching and Maintenance
The hardware vendor may provide a patch to sanitize the
affected shared microarchitectural state when the processor
transitions to a different context.
Effectiveness: Moderate
Note:
This technique may not be able to mitigate
weaknesses that arise from resource sharing across SMT threads.
Patching and Maintenance
This kind of patch may not be feasible or
implementable for all processors or all weaknesses.
Effectiveness: Limited
Requirements
Processor designers, system software vendors, or other
agents may choose to restrict the ability of unprivileged software to
access to high-resolution timers that are commonly used to monitor
covert channels.
Effectiveness: Defense in Depth
Note:
Specific software algorithms can be used by an attacker to compensate for a lack of a high-resolution time source [REF-1420].
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced during hardware architecture and
design if a data path allows architecturally restricted data to
propagate to operations that execute before an older mis-prediction or
processor event (such as an exception) is caught.
Implementation
This weakness can be introduced during system software
implementation if state-sanitizing operations are not invoked when
switching from one context to another, according to the hardware
vendor's recommendations for mitigating the weakness.
System Configuration
This weakness can be introduced if the system has not been
configured according to the hardware vendor's recommendations for
mitigating the weakness.
Architecture and Design
This weakness can be introduced when an access control check
(for example, checking page permissions) can proceed in parallel with
the access operation (for example, a load) that is being checked. If
the processor can allow the access operation to execute before the
check completes, this race condition may allow subsequent transient
operations to expose sensitive information.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Some processors may perform access control checks in parallel with
memory read/write operations. For example, when a user-mode program
attempts to read data from memory, the processor may also need to
check whether the memory address is mapped into user space or kernel
space. If the processor performs the access concurrently with the
check, then the access may be able to transiently read kernel data
before the check completes. This race condition is demonstrated in the
following code snippet from [REF-1408], with additional annotations:
(bad code)
Example Language: x86 Assembly
1 ; rcx = kernel address, rbx = probe array
2 xor rax, rax # set rax to 0
3 retry:
4 mov al, byte [rcx] # attempt to read kernel memory
5 shl rax, 0xc # multiply result by page size (4KB)
6 jz retry # if the result is zero, try again
7 mov rbx, qword [rbx + rax] # transmit result over a cache covert channel
Vulnerable processors may return kernel data from a shared
microarchitectural resource in line 4, for example, from the
processor's L1 data cache. Since this vulnerability involves a race
condition, the mov in line 4 may not always return kernel data (that
is, whenever the check "wins" the race), in which case this
demonstration code re-attempts the access in line 6. The accessed data
is multiplied by 4KB, a common page size, to make it easier to observe
via a cache covert channel after the transmission in line 7. The use
of cache covert channels to observe the side effects of transient
execution has been described in [REF-1408].
Example 2
Many commodity processors share microarchitectural fill buffers
between sibling hardware threads on simultaneous multithreaded (SMT)
processors. Fill buffers can serve as temporary storage for data that
passes to and from the processor's caches. Microarchitectural Fill
Buffer Data Sampling (MFBDS) is a vulnerability that can allow a
hardware thread to access its sibling's private data in a shared fill
buffer. The access may be prohibited by the processor's ISA, but MFBDS
can allow the access to occur during transient execution, in
particular during a faulting operation or an operation that triggers a
microcode assist.
More information on MFBDS can be found in [REF-1405] and [REF-1409].
Example 3
Some processors may allow access to system registers (for example,
system coprocessor registers or model-specific registers) during
transient execution. This scenario is depicted in the code snippet
below. Under ordinary operating circumstances, code in exception level
0 (EL0) is not permitted to access registers that are restricted to
EL1, such as TTBR0_EL1. However, on some processors an earlier
mis-prediction can cause the MRS instruction to transiently read the
value in an EL1 register. In this example, a conditional branch (line
2) can be mis-predicted as "not taken" while waiting for a slow load
(line 1). This allows MRS (line 3) to transiently read the value in
the TTBR0_EL1 register. The subsequent memory access (line 6) can
allow the restricted register's value to become observable, for
example, over a cache covert channel.
1 LDR X1, [X2] ; arranged to miss in the cache
2 CBZ X1, over ; This will be taken
3 MRS X3, TTBR0_EL1;
4 LSL X3, X3, #imm
5 AND X3, X3, #0xFC0
6 LDR X5, [X6,X3] ; X6 is an EL0 base address
7 over
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
A TSX Asynchronous Abort may allow transient operations
to access architecturally restricted data, potentially exposing the
data over a covert channel.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
This weakness can be detected in hardware by
manually inspecting processor specifications. Features that exhibit
this weakness may include microarchitectural predictors, access
control checks that occur out-of-order, or any other features that can
allow operations to execute without committing to architectural
state. Academic researchers have demonstrated that new hardware
weaknesses can be discovered by examining publicly available patent
filings, for example [REF-1405] and [REF-1406]. Hardware designers can also scrutinize aspects of the instruction set
architecture that have undefined behavior; these can become a focal point when applying other
detection methods.
Effectiveness: Moderate
Note:Manual analysis may not reveal all
weaknesses in a processor specification
and should be combined with other detection methods
to improve coverage.
Automated Analysis
This weakness can be detected (pre-discovery) in hardware by
employing static or dynamic taint analysis methods [REF-1401]. These
methods can label data in one context (for example, kernel data) and
perform information flow analysis (or a simulation, etc.) to determine
whether tainted data can appear in another context (for example, user
mode). Alternatively, stale or invalid data in shared
microarchitectural resources can be marked as tainted, and the taint
analysis framework can identify when transient operations encounter
tainted data.
Effectiveness: Moderate
Note:Automated static or dynamic taint
analysis may not reveal all weaknesses in a processor
specification and should be combined with other detection
methods to improve coverage.
Automated Analysis
Software vendors can release tools that detect
presence of known weaknesses (post-discovery) on a processor. For example, some of
these tools can attempt to transiently execute a vulnerable code
sequence and detect whether code successfully leaks data in a manner
consistent with the weakness under test. Alternatively, some hardware
vendors provide enumeration for the presence of a weakness (or lack of
a weakness). These enumeration bits can be checked and reported by
system software. For example, Linux supports these checks for many
commodity processors:
Note:This method can be useful for detecting
whether a processor if affected by known weaknesses, but it
may not be useful for detecting unknown weaknesses.
Fuzzing
Academic researchers have demonstrated that this
weakness can be detected in hardware using software fuzzing
tools that treat the underlying hardware as a black box
([REF-1406], [REF-1430])
Effectiveness: Opportunistic
Note:Fuzzing may not reveal all weaknesses
in a processor specification and should be combined with
other detection methods to improve coverage.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities
Comments
If a weakness can potentially be exploited to
infer data that is accessible inside or outside the current
processor context, then the weakness could map to CWE-1421 and
to another CWE such as CWE-1420.
Stephan van Schaik, Alyssa Milburn, Sebastian Österlund, Pietro Frigo, Giorgi Maisuradze, Kaveh Razavi, Herbert Bos and Cristiano Giuffrida. "RIDL: Rogue In-Flight Data Load". 2019-05-19.
<https://mdsattacks.com/files/ridl.pdf>.
(URL validated: 2024-02-13)
Neta Bar Kama and Roope Kaivola. "Hardware Security Leak Detection by Symbolic Simulation". 2021-11.
<https://ieeexplore.ieee.org/document/9617727>.
(URL validated: 2024-02-13)
[REF-1408]
Moritz Lipp, Michael Schwarz, Daniel Gruss, Thomas Prescher, Werner Haas, Stefan Mangard, Paul Kocher, Daniel Genkin, Yuval Yarom and Mike Hamburg. "Meltdown: Reading Kernel Memory from User Space". 2020-05-21.
<https://meltdownattack.com/meltdown.pdf>.
(URL validated: 2024-02-13)
Alyssa Milburn, Ke Sun and Henrique Kawakami. "You Cannot Always Win the Race: Analyzing the LFENCE/JMP Mitigation for Branch Target Injection". 2022-03-08.
<https://arxiv.org/abs/2203.04277>.
(URL validated: 2024-02-22)
Mengjia Yan, Jiho Choi, Dimitrios Skarlatos, Adam Morrison, Christopher W. Fletcher and Josep Torrella. "InvisiSpec: making speculative execution invisible in the cache hierarchy.". 2019-05.
<https://iacoma.cs.uiuc.edu/iacoma-papers/micro18.pdf>.
(URL validated: 2025-08-04)
[REF-1418]
Alejandro Cabrera Aldaya, Billy Bob Brumley, Sohaib ul Hassan, Cesar Pereida García and Nicola Tuveri. "Port Contention for Fun and Profit". 2019-05.
<https://eprint.iacr.org/2018/1060.pdf>.
(URL validated: 2024-02-14)
[REF-1419]
Mohammad Behnia, Prateek Sahu, Riccardo Paccagnella, Jiyong Yu, Zirui Zhao, Xiang Zou, Thomas Unterluggauer, Josep Torrellas, Carlos Rozas, Adam Morrison, Frank Mckeen, Fangfei Liu, Ron Gabor, Christopher W. Fletcher, Abhishek Basak and Alaa Alameldeen. "Speculative Interference Attacks: Breaking Invisible Speculation Schemes". 2021-04.
<https://arxiv.org/abs/2007.11818>.
(URL validated: 2024-02-14)
[REF-1420]
Ross Mcilroy, Jaroslav Sevcik, Tobias Tebbi, Ben L. Titzer and Toon Verwaest. "Spectre is here to stay: An analysis of side-channels and speculative execution". 2019-02-14.
<https://arxiv.org/pdf/1902.05178>.
(URL validated: 2025-08-04)
Content
History
Submissions
Submission Date
Submitter
Organization
2023-09-19
(CWE 4.14, 2024-02-29)
Scott D. Constable
Intel Corporation
Contributions
Contribution Date
Contributor
Organization
2024-01-22
(CWE 4.14, 2024-02-29)
David Kaplan
AMD
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Rafael Dossantos, Abraham Fernandez Rubio, Alric Althoff, Lyndon Fawcett
Arm
Members of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Jason Oberg
Cycuity
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Priya B. Iyer
Intel Corporation
Member of Microarchitectural Weaknesses Working Group
2024-01-22
(CWE 4.14, 2024-02-29)
Nicole Fern
Riscure
Member of Microarchitectural Weaknesses Working Group
CWE-1258: Exposure of Sensitive System Information Due to Uncleared Debug Information
Weakness ID: 1258
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware product enters debug mode but does not fully clear security-sensitive values, such as keys and intermediate values in cryptographic operations.
Extended Description
Security sensitive values, keys, intermediate steps of cryptographic operations, etc. are stored in temporary registers in the hardware.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: Confidentiality
Sensitive data could be accessed by a debugger, allowing sensitive information to be accessible by untrusted parties.
Bypass Protection Mechanism
Scope: Access Control
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Whenever debug mode is enabled, all registers containing sensitive assets must be cleared.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information Uncleared Before Debug/Power State Transition
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Driving Intermediate Cryptographic State/Results to Hardware Module Outputs
CanAlsoBe
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A cryptographic core in a System-On-a-Chip (SoC) is used for cryptographic acceleration and implements several cryptographic operations (e.g., computation of AES encryption and decryption, SHA-256, HMAC, etc.). The keys for these operations or the intermediate values are stored in registers internal to the cryptographic core. These internal registers are in the Memory Mapped Input Output (MMIO) space and are blocked from access by software and other untrusted agents on the SoC. These registers are accessible through the debug and test interface.
(bad code)
Example Language: Other
In the above scenario, registers that store keys and intermediate values of cryptographic operations are not cleared when system enters debug mode. An untrusted actor running a debugger may read the contents of these registers and gain access to secret keys and other sensitive cryptographic information.
(good code)
Example Language: Other
Whenever the chip enters debug mode, all registers containing security-sensitive data are cleared, rendering them unreadable.
Example 2
The following code example is extracted from the AES wrapper module, aes1_wrapper, of the Hack@DAC'21 buggy OpenPiton System-on-Chip (SoC). Within this wrapper module are four memory-mapped registers: core_key, core_key0, core_key1, and core_key2. Core_key0, core_key1, and core_key2 hold encryption/decryption keys. The core_key register selects a key and sends it to the underlying AES module to execute encryption/decryption operations.
Debug mode in processors and SoCs facilitates design debugging by granting access to internal signal/register values, including physical pin values of peripherals/core, fabric bus data transactions, and inter-peripheral registers. Debug mode allows users to gather detailed, low-level information about the design to diagnose potential issues. While debug mode is beneficial for diagnosing processors or SoCs, it also introduces a new attack surface for potential attackers. For instance, if an attacker gains access to debug mode, they could potentially read any content transmitted through the fabric bus or access encryption/decryption keys stored in cryptographic peripherals.
Therefore, it is crucial to clear the contents of secret registers upon entering debug mode. In the provided example of flawed code below, when debug_mode_i is activated, the register core_key0 is set to zero to prevent AES key leakage during debugging. However, this protective measure is not applied to the core_key1 register [REF-1435], leaving its contents uncleared during debug mode. This oversight enables a debugger to access sensitive information. Failing to clear sensitive data during debug mode may lead to unauthorized access to secret keys and compromise system security.
To address the issue, it is essential to ensure that the register is cleared and zeroized after activating debug mode on the SoC. In the correct implementation illustrated in the good code below, core_keyx registers are set to zero when debug mode is activated [REF-1436].
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Rust library leaks Oauth client details in application debug logs
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1316: Fabric-Address Map Allows Programming of Unwarranted Overlaps of Protected and Unprotected Ranges
Weakness ID: 1316
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The address map of the on-chip fabric has protected and unprotected regions overlapping, allowing an attacker to bypass access control to the overlapping portion of the protected region.
Extended Description
Occasionally, ranges in the address map could overlap. The overlap could either be intentional (e.g. due to a limited number of range registers or limited choice in choosing size of the range) or unintentional (e.g. introduced by errors). Some hardware designs allow dynamic remapping of address ranges assigned to peripheral MMIO ranges. In such designs, intentional address overlaps can be created through misconfiguration by malicious software.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Scope: Confidentiality, Integrity, Access Control, AuthorizationLikelihood: Medium
When protected and unprotected ranges overlap, an attacker could send a transaction and potentially compromise the protections in place, violating the principle of least privilege.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
When architecting the address map of the chip, ensure that protected and unprotected ranges are isolated and do not overlap. When designing, ensure that ranges hardcoded in Register-Transfer Level (RTL) do not overlap.
Implementation
Ranges configured by firmware should not overlap. If overlaps are mandatory because of constraints such as a limited number of registers, then ensure that no assets are present in the overlapped portion.
Testing
Validate mitigation actions with robust testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Peripherals, On-chip Fabric, and Interface/IO Problems
Background Details
Various ranges can be defined in the system-address map, either in the memory or in Memory-Mapped-IO (MMIO) space. These ranges are usually defined using special range registers that contain information, such as base address and size. Address decoding is the process of determining for which range the incoming transaction is destined. To ensure isolation, ranges containing secret data are access-control protected.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Bus/Interface Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
An on-chip fabric supports a 64KB address space that is memory-mapped. The fabric has two range registers that support creation of two protected ranges with specific size constraints--4KB, 8KB, 16KB or 32KB. Assets that belong to user A require 4KB, and those of user B require 20KB. Registers and other assets that are not security-sensitive require 40KB. One range register is configured to program 4KB to protect user A's assets. Since a 20KB range cannot be created with the given size constraints, the range register for user B's assets is configured as 32KB. The rest of the address space is left as open. As a result, some part of untrusted and open-address space overlaps with user B range.
The fabric does not support least privilege, and an attacker can send a transaction to the overlapping region to tamper with user B data.
Since range B only requires 20KB but is allotted 32KB, there is 12KB of reserved space. Overlapping this region of user B data, where there are no assets, with the untrusted space will prevent an attacker from tampering with user B data.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Attacker can modify MCHBAR register to overlap with an attacker-controlled region, which modification prevents the SENTER instruction from properly applying VT-d protection while a Measured Launch Environment is being launched.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Automated Dynamic Analysis
Review address map in specification to see if there are any overlapping ranges.
Effectiveness: High
Manual Static Analysis
Negative testing of access control on overlapped ranges.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.6, CWE-1260 and CWE-1316 are siblings under view 1000, but CWE-1260 might be a parent of CWE-1316. More analysis is warranted.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The reserved bits in a hardware design are not disabled prior to production.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
If the logic being controlled by these bits
is still enabled in production, an adversary could
use the logic to induce unwanted/unsupported
behavior in the hardware. Adversaries with access
to these bits will write to them in hopes of
compromising hardware state. This type of weakness
all depends on the capabilities of the logic being
controlled or configured by the reserved
bits.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Include a feature to disable reserved bits.
Integration
Any writes to these reserve bits are blocked (e.g., ignored, access-protected, etc.), or an exception can be asserted.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Reserved bits are labeled as such so they can be
allocated for a later purpose. Typically, reserved
bits are used for future capabilities and should not
support any functional logic in the design. They are
not supposed to do anything in the current design.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design; Implementation
The Designer and Implementer have to make a
conscious choice to do this. Designers might
covertly use reserved bits to debug or further
develop new capabilities in production
hardware. Designers might want to use these bits
to debug or control/configure a future capability
to help minimize time to market (TTM).
Documentation
If documentation labels anything "for future use", "reserved", or the like, such labeling could indicate to an attacker a potential attack point.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Assume a hardware Intellectual Property (IP) has address space 0x0-0x0F for its configuration registers, with the last one labeled reserved (i.e. 0x0F). Therefore inside the Finite State Machine (FSM), the code is as follows:
(bad code)
Example Language: Verilog
reg gpio_out = 0; //gpio should remain low for normal operation
case (register_address)
4'b1111 : //0x0F
begin
gpio_out = 1;
end
An adversary may perform writes to reserved address space in hopes of changing the behavior of the hardware. In the code above, the GPIO pin should remain low for normal operation. However, it can be asserted by accessing the reserved address space (0x0F). This may be a concern if the GPIO state is being used as an indicator of health (e.g. if asserted the hardware may respond by shutting down or resetting the system, which may not be the correct action the system should perform).
In the code below, the condition "register_address = 0X0F" is commented out, and a default is provided that will catch any values of register_address not explicitly accounted for and take no action with regards to gpio_out. This means that an attacker who is able to write 0X0F to register_address will not enable any undocumented "features" in the process.
(good code)
Example Language: Verilog
reg gpio_out = 0; //gpio should remain low for normal operation
case (register_address)
//4'b1111 : //0x0F
default: gpio_out = gpio_out;
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not provide its
users with the ability to update or patch its
firmware to address any vulnerabilities or
weaknesses that may be present.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands; DoS: Crash, Exit, or Restart
Scope: Confidentiality, Integrity, Access Control, Authentication, AuthorizationLikelihood: Medium
Without the ability to
patch or update firmware, consumers will be
left vulnerable to exploitation of any known
vulnerabilities, or any vulnerabilities that
are discovered in the future. This can expose
consumers to permanent risk throughout the
entire lifetime of the device, which could be
years or decades. It may be possible for the attack
to be used against an entire class of devices.
Some external protective
measures and mitigations might be employed to
aid in preventing or reducing the risk of
malicious attack, but the root weakness cannot
be corrected.
Potential Mitigations
Phase(s)
Mitigation
Requirements
Specify requirements to include the ability to update the firmware. Include integrity checks and authentication to ensure that untrusted firmware cannot be installed.
Architecture and Design
Design the device to allow for updating the firmware. Ensure that the design specifies how to distribute the updates and ensure their integrity and authentication.
Implementation
Implement the necessary functionality to allow the firmware to be updated.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Requirements
Requirements development might not consider the importance of updates over the lifetime of the product, or might not choose the ability due to concerns such as expense or speed to market.
Architecture and Design
Lack of planning during architecture development and design, or external pressures such as speed to market, could ignore the capability to update.
Implementation
The weakness can appear through oversight during implementation.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A refrigerator has an Internet interface for the official purpose of alerting the manufacturer when that refrigerator detects a fault. Because the device is attached to the Internet, the refrigerator is a target for hackers who may wish to use the device other potentially more nefarious purposes.
(bad code)
Example Language: Other
The refrigerator has no means of patching and is hacked, becoming a spewer of email spam.
(good code)
Example Language: Other
The device automatically patches itself and provides considerable more protection against being hacked.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: network-attached storage (NAS) device has a critical OS command injection (CWE-78) vulnerability that is actively exploited to place IoT devices into a botnet, but some products are "end-of-support" and cannot be patched (CWE-1277). [REF-1097]
A hardware "smart lock" has weak key generation that allows attackers to steal the key by BLE sniffing, but the device's firmware cannot be upgraded and hence remains vulnerable [REF-1095].
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Create a new installable boot image of the current build with a minor version number change. Use the standard installation method to update the boot image. Verify that the minor version number has changed. Create a fake image. Verify that the boot updater will not install the fake image and generates an "invalid image" error message or equivalent.
Effectiveness: High
Architecture or Design Review
Check the consumer or maintainer documentation, the architecture/design documentation, or the original requirements to ensure that the documentation includes details for how to update the firmware.
Effectiveness: Moderate
Manual Dynamic Analysis
Determine if there is a lack of a capability to update read-only memory (ROM) structure. This could manifest as a difference between the latest firmware version and the current version within the device.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Terminology
The "firmware" term does not have a single commonly-shared definition, so there may be variations in how this CWE entry is interpreted during mapping.
CWE Grouping: General Circuit and Logic Design Concerns
Grouping ID: 1199
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to hardware-circuit design and logic (e.g., CMOS transistors, finite state machines, and registers) as well as issues related to hardware description languages such as System Verilog and VHDL.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product implements a Security Token mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Tokens generated in the system are incorrect.
Extended Description
Systems-On-a-Chip (SoC) (Integrated circuits and hardware engines) implement Security Tokens to differentiate and identify actions originated from various agents. These actions could be "read", "write", "program", "reset", "fetch", "compute", etc. Security Tokens are generated and assigned to every agent on the SoC that is either capable of generating an action or receiving an action from another agent. Every agent could be assigned a unique Security Token based on its trust level or privileges.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Files or Directories; Execute Unauthorized Code or Commands; Bypass Protection Mechanism; Gain Privileges or Assume Identity; Read Memory; Modify Memory; DoS: Crash, Exit, or Restart
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
Incorrectly generated Security Tokens could result in the same token used for multiple agents or multiple tokens being used for the same agent. This condition could result in a Denial-of-Service (DoS) or the execution of an action that in turn could result in privilege escalation or unintended access.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Generation of Security Tokens should be reviewed for design inconsistency and common weaknesses.
Security-Token definition and programming flow should be tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a system with a register for storing an AES key for encryption or decryption. The key is 128 bits long implemented as a set of four 32-bit registers. The key registers are assets, and register, AES_KEY_ACCESS_POLICY, is defined to provide necessary access controls. The access-policy register defines which agents, using a Security Token, may access the AES-key registers. Each bit in this 32-bit register is used to define a Security Token. There could be a maximum of 32 Security Tokens that are allowed access to the AES-key registers. When set (bit = "1") bit number allows action from an agent whose identity matches that bit number. If Clear (bit = "0") the action is disallowed for the corresponding agent.
Assume the system has two agents: a Main-controller and an Aux-controller. The respective Security Tokens are "1" and "2".
Register
Description
Default
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_3
AES key [96:127] for encryption or decryption
0x00000000
AES_KEY_ACCESS_POLICY
AES key access register [31:0]
0x00000002
An agent with a Security Token "1" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_3 registers. As per the above access policy, the AES-Key-access policy allows access to the AES-key registers if the security Token is "1".
(bad code)
Example Language: Other
The SoC incorrectly generates Security Token "1" for every agent. In other words, both Main-controller and Aux-controller are assigned Security Token "1".
Both agents have access to the AES-key registers.
(good code)
Example Language: Other
The SoC should correctly generate Security Tokens, assigning "1" to the Main-controller and "2" to the Aux-controller
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1313: Hardware Allows Activation of Test or Debug Logic at Runtime
Weakness ID: 1313
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
During runtime, the hardware allows for test or debug logic (feature) to be activated, which allows for changing the state of the hardware. This feature can alter the intended behavior of the system and allow for alteration and leakage of sensitive data by an adversary.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Crash, Exit, or Restart; DoS: Instability; DoS: Resource Consumption (CPU); DoS: Resource Consumption (Memory); DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Alter Execution Logic; Quality Degradation; Unexpected State; Reduce Performance; Reduce Reliability
Scope: Confidentiality, Integrity, Availability
An adversary can take advantage of test or debug logic that is made accessible through the hardware during normal operation to modify the intended behavior of the system. For example, an accessible Test/debug mode may allow read/write access to any system data. Using error injection (a common test/debug feature) during a transmit/receive operation on a bus, data may be modified to produce an unintended message. Similarly, confidentiality could be compromised by such features allowing access to secrets.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Insert restrictions on when the hardware's test or debug features can be activated. For example, during normal operating modes, the hardware's privileged modes that allow access to such features cannot be activated. Configuring the hardware to only enter a test or debug mode within a window of opportunity such as during boot or configuration stage. The result is disablement of such test/debug features and associated modes during normal runtime operations.
Implementation
Insert restrictions on when the hardware's test or debug features can be activated. For example, during normal operating modes, the hardware's privileged modes that allow access to such features cannot be activated. Configuring the hardware to only enter a test or debug mode within a window of opportunity such as during boot or configuration stage. The result is disablement of such test/debug features and associated modes during normal runtime operations.
Integration
Insert restrictions on when the hardware's test or debug features can be activated. For example, during normal operating modes, the hardware's privileged modes that allow access to such features cannot be activated. Configuring the hardware to only enter a test or debug mode within a window of opportunity such as during boot or configuration stage. The result is disablement of such test/debug features and associated modes during normal runtime operations.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Integration
Such issues could be introduced during integration and identified later during Testing or System configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Processor allows the activation of test or debug logic at runtime, allowing escalation of privileges
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1276: Hardware Child Block Incorrectly Connected to Parent System
Weakness ID: 1276
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Signals between a hardware IP and the parent system design are incorrectly connected.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Confidentiality, Integrity, Availability
This may cause security risks. For example, if the IP should only be reset by a system-wide hard reset, but instead the reset input is connected to a software-triggered debug mode reset (which is also asserted during a hard reset), integrity of data inside the IP can be violated.
Potential Mitigations
Phase(s)
Mitigation
Testing
System-level verification may be used to ensure that components are correctly connected and that design security requirements are not violated due to interactions between various IP blocks.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Individual hardware IP must communicate with the parent system in order for the product to function correctly and as intended. If implemented incorrectly, while not causing any apparent functional issues, it may cause security issues.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
This weakness is introduced when integrating IP into a parent design.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Many SoCs use hardware to partition system resources between trusted and untrusted entities. One example of this concept is the Arm TrustZone, in which the processor and all security-aware IP attempt to isolate resources based on the status of a privilege bit. This privilege bit is part of the input interface in all TrustZone-aware IP. If this privilege bit is accidentally grounded or left unconnected when the IP is instantiated, privilege escalation of all input data may occur.
(bad code)
Example Language: Verilog
// IP definition
module tz_peripheral(clk, reset, data_in, data_in_security_level, ...);
endmodule
// Instantiation of IP in a parent system
module soc(...)
...
tz_peripheral u_tz_peripheral(
.clk(clk),
.rst(rst),
.data_in(rdata),
//Copy-and-paste error or typo grounds data_in_security_level (in this example 0=secure, 1=non-secure) effectively promoting all data to "secure")
.data_in_security_level(1'b0),
);
...
endmodule
In the Verilog code below, the security level input to the TrustZone aware peripheral is correctly driven by an appropriate signal instead of being grounded.
(good code)
Example Language: Verilog
// Instantiation of IP in a parent system
module soc(...)
...
tz_peripheral u_tz_peripheral(
.clk(clk),
.rst(rst),
.data_in(rdata),
// This port is no longer grounded, but instead driven by the appropriate signal
.data_in_security_level(rdata_security_level),
);
...
endmodule
Example 2
Here is a code snippet from the Ariane core module in the HACK@DAC'21 Openpiton SoC [REF-1362].
To ensure full functional correctness, developers connect the ports with names. However, in some cases developers forget to connect some of these ports to the desired signals in the parent module. These mistakes by developers can lead to incorrect functional behavior or, in some cases, introduce security vulnerabilities.
In the above example from HACK@DAC'21, since interrupt signals are not properly connected, the CSR module will fail to send notifications in the event of interrupts. Consequently, critical information in CSR registers that should be flushed or modified in response to an interrupt won't be updated. These vulnerabilities can potentially result in information leakage across various privilege levels.
To address the aforementioned vulnerability, developers must follow a two-step approach. First, they should ensure that all module signals are properly connected. This can often be facilitated using automated tools, and many simulators and sanitizer tools issue warnings when a signal remains unconnected or floats. Second, it is imperative to validate that the signals connected to a module align with the specifications. In the provided example, the developer should establish the correct connection of interrupt signals from the parent module (Ariane core) to the child module (csr_regfile) [REF-1363].
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1234: Hardware Internal or Debug Modes Allow Override of Locks
Weakness ID: 1234
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
System configuration protection may be bypassed during debug mode.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access ControlLikelihood: High
Bypass of the lock bit protection may allow access and modification of system configuration information, even when the lock bit is set.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Security Lock bit protections should be reviewed for any bypass/override modes supported.
Any supported override modes either should be removed or protected using authenticated debug modes.
Security lock programming flow and lock properties should be tested in pre-silicon and post-silicon testing.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Device configuration controls are commonly programmed after a device power reset by a trusted firmware or software module (e.g., BIOS/bootloader) and then locked from any further modification. This is commonly implemented using a trusted lock bit, which when set, disables writes to a protected set of registers or address regions. The lock protection is intended to prevent modification of certain system configuration (e.g., memory/memory protection unit configuration).
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Debug features supported by hardware or internal modes/system states might be supported in the hardware design.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
For example, consider the example Locked_override_register example. This register module supports a lock mode that blocks any writes after lock is set to 1.
However, it also allows override of the lock protection when scan_mode or debug_unlocked modes are active.
end
else if (write & (~lock_status | scan_mode | debug_unlocked) ) // Register protected by Lock bit input, overrides supported for scan_mode & debug_unlocked
begin
Data_out <= Data_in;
end
else if (~write)
begin
Data_out <= Data_out;
end
endmodule
If either the scan_mode or the debug_unlocked modes can be triggered by software, then the lock protection may be bypassed.
(good code)
Example Language: Other
Either remove the debug and scan mode overrides or protect enabling of these modes so that only trusted and authorized users may enable these modes.
Example 2
The following example code [REF-1375] is taken from the register lock security peripheral of the HACK@DAC'21 buggy OpenPiton SoC. It demonstrates how to lock read or write access to security-critical hardware registers (e.g., crypto keys, system integrity code, etc.). The configuration to lock all the sensitive registers in the SoC is managed through the reglk_mem registers. These reglk_mem registers are reset when the hardware powers up and configured during boot up. Malicious users, even with kernel-level software privilege, do not get access to the sensitive contents that are locked down. Hence, the security of the entire system can potentially be compromised if the register lock configurations are corrupted or if the register locks are disabled.
(bad code)
Example Language: SystemVerilog
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~jtag_unlock && ~rst_9))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'h0;
end
end
...
The example code [REF-1375] illustrates an instance of a vulnerable implementation of register locks in the SoC. In this flawed implementation [REF-1375], the reglk_mem registers are also being reset when the system enters debug mode (indicated by the jtag_unlock signal). Consequently, users can simply put the processor in debug mode to access sensitive contents that are supposed to be protected by the register lock feature.
This can be mitigated by excluding debug mode signals from the reset logic of security-critical register locks as demonstrated in the following code snippet [REF-1376].
(good code)
Example Language: SystemVerilog
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~rst_9))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'h0;
end
end
...
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A race condition in the hardware logic results in undermining security guarantees of the system.
Extended Description
A race condition in logic circuits typically occurs when a logic gate gets inputs from signals that have traversed different paths while originating from the same source. Such inputs to the gate can change at slightly different times in response to a change in the source signal. This results in a timing error or a glitch (temporary or permanent) that causes the output to change to an unwanted state before settling back to the desired state.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism; Gain Privileges or Assume Identity; Alter Execution Logic
Scope: Access Control
If timing errors occur in access control logic or finite state machines that are implemented in security sensitive flows, an attacker might exploit them to circumvent existing protections.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Adopting design practices that encourage designers to recognize and eliminate race conditions, such as Karnaugh maps, could result in the decrease in occurrences of race conditions.
Implementation
Logic redundancy can be implemented along security critical paths to prevent race conditions. To avoid metastability, it is a good practice in general to default to a secure state in which access is not given to untrusted agents.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The code below shows a 2x1 multiplexor using logic gates. Though the code shown below results in the minimum gate solution, it is disjoint and causes glitches.
// Buggy line of code:
assign z = and_out1 | and_out2; // glitch in signal z
endmodule
The buggy line of code, commented above, results in signal 'z' periodically changing to an unwanted state. Thus, any logic that references signal 'z' may access it at a time when it is in this unwanted state. This line should be replaced with the line shown below in the Good Code Snippet which results in signal 'z' remaining in a continuous, known, state. Reference for the above code, along with waveforms for simulation can be found in the references below.
(good code)
Example Language: Verilog
assign z <= and_out1 or and_out2 or (in0 and in1);
This line of code removes the glitch in signal z.
Example 2
The example code is taken from the DMA (Direct Memory Access) module of the buggy OpenPiton SoC of HACK@DAC'21. The DMA contains a finite-state machine (FSM) for accessing the permissions using the physical memory protection (PMP) unit.
PMP provides secure regions of physical memory against unauthorized access. It allows an operating system or a hypervisor to define a series of physical memory regions and then set permissions for those regions, such as read, write, and execute permissions. When a user tries to access a protected memory area (e.g., through DMA), PMP checks the access of a PMP address (e.g., pmpaddr_i) against its configuration (pmpcfg_i). If the access violates the defined permissions (e.g., CTRL_ABORT), the PMP can trigger a fault or an interrupt. This access check is implemented in the pmp parameterized module in the below code snippet. The below code assumes that the state of the pmpaddr_i and pmpcfg_i signals will not change during the different DMA states (i.e., CTRL_IDLE to CTRL_DONE) while processing a DMA request (via dma_ctrl_reg). The DMA state machine is implemented using a case statement (not shown in the code snippet).
(bad code)
Example Language: SystemVerilog
module dma # (...)(...);
...
input [7:0] [16-1:0] pmpcfg_i;
input logic [16-1:0][53:0] pmpaddr_i;
...
//// Save the input command
always @ (posedge clk_i or negedge rst_ni)
begin: save_inputs
if (!rst_ni)
begin
...
end
else
begin
if (dma_ctrl_reg == CTRL_IDLE || dma_ctrl_reg == CTRL_DONE)
begin
...
end
end
end // save_inputs
...
// Load/store PMP check
pmp #(
However, the above code [REF-1394] allows the values of pmpaddr_i and pmpcfg_i to be changed through DMA's input ports. This causes a race condition and will enable attackers to access sensitive addresses that the configuration is not associated with.
Attackers can initialize the DMA access process (CTRL_IDLE) using pmpcfg_i for a non-privileged PMP address (pmpaddr_i). Then during the loading state (CTRL_LOAD), attackers can replace the non-privileged address in pmpaddr_i with a privileged address without the requisite authorized access configuration.
To fix this issue (see [REF-1395]), the value of the pmpaddr_i and pmpcfg_i signals should be stored in local registers (pmpaddr_reg and pmpcfg_reg at the start of the DMA access process and the pmp module should reference those registers instead of the signals directly. The values of the registers can only be updated at the start (CTRL_IDLE) or the end (CTRL_DONE) of the DMA access process, which prevents attackers from changing the PMP address in the middle of the DMA access process.
(good code)
Example Language: SystemVerilog
module dma # (...)(...);
...
input [7:0] [16-1:0] pmpcfg_i;
input logic [16-1:0][53:0] pmpaddr_i;
... reg [7:0] [16-1:0] pmpcfg_reg; reg [16-1:0][53:0] pmpaddr_reg;
...
//// Save the input command
always @ (posedge clk_i or negedge rst_ni)
begin: save_inputs
if (!rst_ni)
begin
... pmpaddr_reg <= 'b0 ; pmpcfg_reg <= 'b0 ;
end
else
begin
if (dma_ctrl_reg == CTRL_IDLE || dma_ctrl_reg == CTRL_DONE)
begin
... pmpaddr_reg <= pmpaddr_i; pmpcfg_reg <= pmpcfg_i;
end
end
end // save_inputs
...
// Load/store PMP check
pmp #(
.XLEN ( 64 ),
.PMP_LEN ( 54 ),
.NR_ENTRIES ( 16 )
) i_pmp_data (
.addr_i ( pmp_addr_reg ),
.priv_lvl_i ( riscv::PRIV_LVL_U ), // we intend to apply filter on
// DMA always, so choose the least privilege
.access_type_i ( pmp_access_type_reg ),
// Configuration
.conf_addr_i ( pmpaddr_reg ),
.conf_i ( pmpcfg_reg ),
.allow_o ( pmp_data_allow )
);
endmodule
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1264: Hardware Logic with Insecure De-Synchronization between Control and Data Channels
Weakness ID: 1264
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware logic for error handling and security checks can incorrectly forward data before the security check is complete.
Extended Description
Many high-performance on-chip bus protocols and processor data-paths employ separate channels for control and data to increase parallelism and maximize throughput. Bugs in the hardware logic that handle errors and security checks can make it possible for data to be forwarded before the completion of the security checks. If the data can propagate to a location in the hardware observable to an attacker, loss of data confidentiality can occur.
'Meltdown' is a concrete example of how de-synchronization between data and permissions checking logic can violate confidentiality requirements. Data loaded from a page marked as privileged was returned to the CPU regardless of current privilege level for performance reasons. The assumption was that the CPU could later remove all traces of this data during the handling of the illegal memory access exception, but this assumption was proven false as traces of the secret data were not removed from the microarchitectural state.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data
Scope: Confidentiality
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Thoroughly verify the data routing logic to ensure that any error handling or security checks effectively block illegal dataflows.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Processor Optimization Removal or Modification of Security-critical Code
Overlaps
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
The weakness can be introduced in the data transfer or bus protocol itself or in the implementation.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
There are several standard on-chip bus protocols used in modern SoCs to allow communication between components. There are a wide variety of commercially available hardware IP implementing the interconnect logic for these protocols. A bus connects components which initiate/request communications such as processors and DMA controllers (bus masters) with peripherals which respond to requests. In a typical system, the privilege level or security designation of the bus master along with the intended functionality of each peripheral determine the security policy specifying which specific bus masters can access specific peripherals. This security policy (commonly referred to as a bus firewall) can be enforced using separate IP/logic from the actual interconnect responsible for the data routing.
(bad code)
Example Language: Other
The firewall and data routing logic becomes de-synchronized due to a hardware logic bug allowing components that should not be allowed to communicate to share data. For example, consider an SoC with two processors. One is being used as a root of trust and can access a cryptographic key storage peripheral. The other processor (application cpu) may run potentially untrusted code and should not access the key store. If the application cpu can issue a read request to the key store which is not blocked due to de-synchronization of data routing and the bus firewall, disclosure of cryptographic keys is possible.
(good code)
Example Language: Other
All data is correctly buffered inside the interconnect until the firewall has determined that the endpoint is allowed to receive the data.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Systems with microprocessors utilizing speculative execution and indirect branch prediction may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis of the data cache.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.9, members of the CWE Hardware SIG are closely analyzing this entry and others to improve CWE's coverage of transient execution weaknesses, which include issues related to Spectre, Meltdown, and other attacks. Additional investigation may include other weaknesses related to microarchitectural state. As a result, this entry might change significantly in CWE 4.10.
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware design contains structures that are interpreted
differently during synthesis than during simulation, which
cause inconsistencies in security-relevant behavior between
the synthesized implementation and the simulation.
Extended Description
Hardware-description-language (HDL) code describes
functionality which can be verified as correct using
simulation tools. Synthesis tools then (automatically) convert
this into a physically-realizable representation. Certain HDL
code structures cannot be exactly represented, or have
multiple valid representations from which the synthesis tool
must choose. This can result in output which behaves
differently to the (functionally-correct) HDL code. These
"simulation/synthesis mismatches" may have security
consequences.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Other
The consequences depend on the affected hardware
behavior. The synthesized implementation may make
different control decisions, incorrectly update protected
state, expose data, or fail to enforce restrictions that
appeared to operate correctly during HDL
simulation.
Potential Mitigations
Phase(s)
Mitigation
Implementation & Physical Design (Hardware)
Establish and enforce HDL coding and review
practices that minimize differences between simulation
semantics and synthesis interpretation. Avoid HDL
constructs, synthesis directives, and tool-dependent
behaviors known to cause simulation/synthesis mismatch,
with particular attention to security-relevant
logic.
Effectiveness: High
Note:
Avoidance of the patterns of code which can
result in these errors removes the opportunity for
error. However, in some cases (notably state machine
encodings) this can be very difficult to achieve
efficiently.
Implementation & Physical Design (Hardware)
For security-critical logic, preserve intentional
redundancy that is required for security. Examples may
include redundant logic, triple modular redundancy (TMR)
structures, Hamming-distance state encodings, or
state-machine recovery logic. Use synthesis constraints,
preservation attributes, carefully controlled structural
implementation, or manual implementation of selected
critical blocks to prevent this redundancy from being
merged, re-encoded, or optimized away.
Effectiveness: High
Note:
This mitigation removes the structures which
cause the problem, at the expense of additional design and
verification effort, and additional risk of inclusion of
other functional errors.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation & Physical Design (Hardware)
This weakness can be introduced when HDL
constructs, assignment ordering, synthesis directives, or
tool-dependent semantics are used whose simulation
behavior may not match synthesis interpretation. These
constructs may behave correctly during HDL simulation but
produce different security-relevant behavior in the
synthesized implementation.
Implementation & Physical Design (Hardware)
This weakness can be introduced or exposed during
synthesis when the synthesis tool applies assumptions,
optimizations, or transformations to HDL structures that
cannot be physically implemented exactly as the simulation
semantics dictate, or that permit multiple (valid)
hardware implementations. The resulting netlist may behave
differently from the model that was verified during
simulation.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Class: Hardware Description Language
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A hardware designer implements an access control
latch which takes in lock and unlock signals (which are
only active for a single cycle) and a reset signal, and
outputs an unlocked state signal. During operation, the
unlocked signal is synchronously set high by the unlock
input and set low by the lock input. The unlocked signal
also intended to be low from startup and set low by
reset.
The following VHDL example is written for VHDL-93
or later.
(bad code)
Example Language: VHDL
library ieee;
use ieee.std_logic_1164.all;
entity lock_control is
port (
clk : in std_logic;
reset : in std_logic;
lock : in std_logic;
unlock : in std_logic;
unlocked : out std_logic
);
end entity lock_control;
architecture behavioral of lock_control is
signal unlocked_reg : std_logic:=’0’;
signal unlocked_next : std_logic;
begin
process(lock, unlock, unlocked_reg)
begin
if reset = '1' then
unlocked_next <= '1';
elsif lock = '1' then
unlocked_next <= '0';
elsif unlock = '1' then
unlocked_next <= '1';
else
unlocked_next <= unlocked_reg;
end if;
end process;
process(clk)
begin
if rising_edge(clk) then
unlocked_reg <= unlocked_next;
end if;
end process;
unlocked <= unlocked_reg;
end architecture behavioral;
The always block is intended to describe
combinational logic for unlocked_next, which depends on
four signals (lock, unlock, unlocked and reset). However,
the sensitivity list is missing reset.
During pre-synthesis RTL simulation, this tells
the simulator not to rerun the block when reset changes
(only when the other signals change). The signal
unlocked_next defaults to 1’b0 so the simulation sees the
expected locked state and so the tests of the state after
reset will pass.
Synthesis tools assume a complete sensitivity
list and will therefore infer logic including the reset
signal. When reset is high, the unlocked _next signal is
(erroneously) set to 1’b1. This is a bug (as reset should
force a non-unlocked state), which would be expected to be
found in simulation. The design uses a two-process state
machine style which masks this bug in the code during
simulation, but allows it to propagate to the synthesized
implementation.
The synthesized hardware exits reset in an
insecure state (with unlocked set to 1’b1) and remains in
that state until one of the lock/unlock signals changes
state. An adversary can take advantage of this by
exploiting whatever logic makes use of this signal to set
itself to a secure state.
(good code)
Example Language: Algorithm
For combinational logic, ensure that simulation is
triggered by every signal read by the block. This can be
done by listing both inputs explicitly, but this is not
recommended.
A safer and more maintainable approach is to use (in
Verilog) always @*, which tells the simulator to include
all signals used inside the block. In SystemVerilog, use
always_comb. In VHDL use process(all).
Example 2
A hardware developer is debugging logic which
requires the system to be in an unprotected mode. In
order to enable their work, they have (temporarily)
removed some code related to the "protected_mode_enabled"
flag in a way that does not cause the simulations to
fail.
(bad code)
Example Language: VHDL
-- The following VHDL example is written for VHDL-93 or later.
signal secure : boolean; -- implicitly initialized to ‘false’
signal policy_ok : boolean;
signal lock_ready : boolean;
...
-- synthesis translate_off
secure <= security_check(policy_ok, lock_ready); -- TODO: restore this after debugging
-- synthesis translate_on
protected_mode_enabled <= secure;
secure = 1'b0; // default value
// synopsys translate_off
secure = security_check(policy_ok, lock_ready); // TODO: restore this after debugging
// synopsys translate_on
end
assign protected_mode_enabled = secure;
The design assigns the security-relevant secure
signal using logic that is hidden from synthesis by
translate_off / translate_on or equivalent synthesis
exclusion directives. Simulation tools treat these
directives as comments and include the enclosed
assignment, so simulation updates secure according to
security_check(policy_ok, lock_ready) and appears to
validate the intended protected-mode behavior.
Synthesis tools omit the code between the
exclusion directives. The synthesized implementation
therefore does not contain the same assignment that was
exercised during simulation. This creates a
simulation/synthesis mismatch in security-relevant
behavior: the HDL model used for verification enables or
disables protected mode using logic that is absent from
the synthesized hardware.
Because the synthesized implementation does not
include the same logic that was present during simulation,
the hardware defaults to an insecure state. An attacker
can take advantage of this to execute activities which
would normally require some form of authorization, even
though simulation results suggested that protected mode
would be enforced.
(good code)
Example Language: Algorithm
Do not place security-relevant assignments inside
synthesis-excluded regions. Any logic that affects
protected-mode behavior should be represented consistently
in both simulation and synthesis.
Limit synthesis translate_off / translate_on regions to
simulation-only code that cannot assign, modify, override,
or mask security-sensitive signals.
Carefully review all uses of translate_on/off directives.
Ensure that developers can efficiently authorize their
activities during development work, to avoid the temptation
to bypass security features in this way.
(good code)
Example Language: VHDL
-- The following VHDL example is written for VHDL-93 or later.
signal secure : boolean; -- implicitly initialized to ‘false’
signal policy_ok : boolean;
signal lock_ready : boolean;
...
secure <= security_check(policy_ok, lock_ready);
protected_mode_enabled <= secure;
A hardware developer is designing a controller that
manages whether protected configuration registers can be
written. The controller includes states for reset handling,
user-level operation, and privileged operation.
(bad code)
Example Language: VHDL
-- The following VHDL example is written for VHDL-93 or later.
type t_priv_state is (RESET, USER_ONLY, PRIVILEGED);
signal priv_state : t_priv_state := RESET;
signal auth_passed : boolean := false;
signal privilege_revoke : boolean := false;
...
process(clk, reset_n)
begin
if reset_n = '0' then
priv_state <= RESET;
elsif rising_edge(clk) then
case priv_state is
when RESET =>
priv_state <= USER_ONLY;
when USER_ONLY =>
if auth_passed then
priv_state <= PRIVILEGED;
end if;
when PRIVILEGED =>
if privilege_revoke then
priv_state <= USER_ONLY;
end if;
when others =>
priv_state <= USER_ONLY; -- intended recovery for unexpected encodings
end case;
end if;
end process;
protected_cfg_write_en <= (priv_state = PRIVILEGED);
priv_state <= USER_ONLY; // intended recovery for unexpected encodings
end
endcase
end
end
assign protected_cfg_write_en = (priv_state == PRIVILEGED);
The design relies on a VHDL others choice or
Verilog default branch to express recovery behavior for
state values not explicitly listed in the state transition
logic. In RTL simulation, the intended behavior is that
unexpected controller states will transition to USER_ONLY,
where protected configuration writes are
blocked.
The error is assuming that this RTL-level
recovery behavior will necessarily be preserved after
synthesis. During synthesis, the state machine may be
encoded, optimized, or transformed based on the states
considered reachable during normal operation. As a result,
logic associated with unused or faulty hardware encodings
may be removed or altered, and the synthesized
implementation may not preserve the same recovery behavior
that appeared in RTL simulation.
If the synthesized implementation does not
preserve the unexpected-state recovery behavior, the
hardware may fail to return to USER_ONLY after a fault,
reset anomaly, voltage glitch, clock disturbance, or other
condition that places the state storage into an unintended
encoding.
An attacker who can induce or influence such
conditions may be able to leave protected configuration
writes enabled, or cause them to become enabled, even
though simulation suggested that unexpected state values
would be forced into a state where those writes are
blocked.
(good code)
Example Language: Algorithm
Do not rely on a VHDL others choice or Verilog default
branch to guarantee post-synthesis recovery behavior for
security-critical state machines. If recovery from
unexpected state encodings affects access to protected
configuration registers, the implementation should not
depend on synthesis inferring and preserving that
behavior from RTL alone.
For this type of security-critical controller, implement
the state machine using a carefully-controlled
structural or hand-synthesized representation where the
relevant state elements, reset behavior, transition
logic, and fail-closed recovery behavior are
explicit. Be careful that the synthesiser does not infer
a state machine from the crafted logic, and “undo” the
work. Review the resulting gate-level or structural
implementation to confirm that unintended encodings are
handled as required.
Perform post-synthesis simulations where faults are
injected into the state registers and confirm the
behavior.
Perform formal analysis to prove that the behavior of
these critical blocks has not been altered by the
synthesis process.
After the implementation is verified and validated,
preserve it during integration so later synthesis or
whole-design optimization does not re-encode, merge,
remove, or otherwise transform the security-critical
recovery logic.
This approach is costly and design-specific, but it is
appropriate when relying on ordinary RTL synthesis would
create unacceptable security risk.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Debug-load requests should return complete load
store unit (LSU) data, but the synthesized netlist returned
incomplete data, potentially causing incorrect interpretation
of memory state.
Instruction execution should update
program-counter state correctly, but the synthesized netlist
produced incomplete or undefined updates, potentially causing
unintended control flow.
The program counter should update when the
next-program-counter value changes, but the synthesized
netlist allowed stale PC state, potentially causing incorrect
instruction fetches or stalls.
Weakness Ordinalities
Ordinality
Description
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
This is a resultant weakness as the primary would be
something like bad RTL coding practices or Synthesis
optimization that then would result in a mismatch.
Detection
Methods
Method
Details
Automated Static Analysis - Source Code
HDL linting, rule-based static analysis, and HDL
checker tools can examine source code for structures that
may be interpreted differently by simulation and synthesis
tools. They may identify synthesis-sensitive coding
patterns associated with this weakness.
Effectiveness: Moderate
Note:
This method can be useful for detecting potential
coding issues, but it may not reveal whether these
constructs result in observable behavioral divergence
after synthesis. Moreover, a user may suppress or bypass
these warnings and still produce the erroneous synthesized
hardware implementation. This method can give false
positives.
Manual Analysis
Synthesis warning review can examine synthesis
logs and reports for tool messages associated with
possible simulation/synthesis mismatch. It may identify
ignored constructs, unsupported HDL semantics, synthesis
assumptions, or optimizations that could affect
security-relevant behavior.
Effectiveness: Limited
Note:
Can reveal potential synthesis issues but relies
on engineers interpreting warnings. Moreover, a user may
suppress or bypass these warnings and still produce the
erroneous synthesized hardware implementation.
Formal Verification
HDL-source-to-netlist formal equivalence checking
can examine the simulated model and synthesized netlist
for behavioral mismatch associated with this weakness. It
may identify non-equivalent outputs, failed
compare-points, state-mapping issues, or counterexamples
under the checked constraints.
Effectiveness: High
Note:
Formal equivalence checking can be effective at
the IP level for identifying mismatches between the
source-code model and synthesized implementation. However,
effectiveness may decrease as design complexity grows,
particularly at the SoC level, due to state-space
expansion and difficulty mapping non-equivalent
points. Synthesis optimizations may merge, eliminate, or
rename signals, which can also produce false positives or
require additional setup to account for expected
transformations.
Simulation / Emulation
Cross-simulation across HDL-source and
post-synthesis models can examine both abstraction levels
for observable behavioral divergence associated with this
weakness. It may identify mismatches when
security-relevant behaviors are explicitly
exercised.
Effectiveness: High
Note:
This method can be useful for detecting
observable behavioral mismatches, but it may not exercise
all execution scenarios and should be combined with other
detection methods to improve coverage.
Fuzzing
Coverage-guided differential fuzzing can examine
HDL source code and synthesized implementation models for
behavioral divergence associated with this weakness. It
may identify generated inputs or state conditions that
expose synthesis-induced mismatches.
Effectiveness: High
Note:
This method can be useful for detecting
previously unknown synthesis-induced behavioral mismatches
by exploring diverse execution paths through
coverage-guided input generation. However, it may not
exercise every reachable design state and should be
combined with other detection methods to improve
coverage.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reasons
Frequently-Resultant,
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Since this entry is often resultant, there might be
other CWEs that are more appropriate as the root cause,
although there might be some gaps. Carefully read both the
name and description to ensure that this mapping is an
appropriate fit. Do not try to 'force' a mapping to a
lower-level Base/Variant simply to comply with this preferred
level of abstraction.
Participated in a series of
meetings betwee March 2026 and September 26, in
which members contributed significant feedback
related to this entry as it evolved before
publication in CWE 5.0.
2026-03-30
(CWE 5.0, 2026-10-28)
MITRE
Guided evolution of the name
and description for this entry, followed by
suggestions for mitigations, demonstrative
examples, and detection methods. Note: some
content development was AI-assisted, with expert
review and editing by MITRE and members of the CWE
Ad Hoc RTL WG.
CWE-1257: Improper Access Control Applied to Mirrored or Aliased Memory Regions
Weakness ID: 1257
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Aliased or mirrored memory regions in hardware designs may have inconsistent read/write permissions enforced by the hardware.
Extended Description
A common security weakness that can exist in such memory mapping is that aliased memory regions could have different read/write access protections enforced by the hardware such that an untrusted agent is blocked from accessing a memory address but is not blocked from accessing the corresponding aliased memory address. Such inconsistency can then be used to bypass the access protection of the primary memory block and read or modify the protected memory.
An untrusted agent could also possibly create memory aliases in the system address map for malicious purposes if it is able to change the mapping of an address region or modify memory region sizes.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: ConfidentialityLikelihood: High
An untrusted agent might be blocked from accessing a memory region, but it is not blocked from accessing the corresponding aliased memory region.
Modify Memory
Scope: IntegrityLikelihood: High
An untrusted agent might be blocked from accessing a memory region, but it is not blocked from accessing the corresponding aliased memory region.
DoS: Instability
Scope: AvailabilityLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
The checks should be applied for consistency access rights between primary memory regions and any mirrored or aliased memory regions. If different memory protection units (MPU) are protecting the aliased regions, their protected range definitions and policies should be synchronized.
Architecture and Design; Implementation
The controls that allow enabling memory aliases or changing the size of mapped memory regions should only be programmable by trusted software components.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Hardware product designs often need to implement memory protection features that enable privileged software to define isolated memory regions and access control (read/write) policies. Isolated memory regions can be defined on different memory spaces in a design (e.g. system physical address, virtual address, memory mapped IO).
Each memory cell should be mapped and assigned a system address that the core software can use to read/write to that memory. It is possible to map the same memory cell to multiple system addresses such that read/write to any of the aliased system addresses would be decoded to the same memory cell.
This is commonly done in hardware designs for redundancy and simplifying address decoding logic. If one of the memory regions is corrupted or faulty, then that hardware can switch to using the data in the mirrored memory region. Memory aliases can also be created in the system address map if the address decoder unit ignores higher order address bits when mapping a smaller address region into the full system address.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Network on Chip Hardware
(Undetermined Prevalence)
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
In a System-on-a-Chip (SoC) design the system fabric uses 16 bit addresses. An IP unit (Unit_A) has 4 kilobytes of internal memory which is mapped into a 16 kilobyte address range in the system fabric address map.
System Address
Mapped to
0x0000 - 0x3FFF
Unit_A registers : 0x0000 - 0x0FFF
0x4000 - 0xFFFF
Other IPs & Memory
To protect the register controls in Unit_A unprivileged software is blocked from accessing addresses between 0x0000 - 0x0FFF.
The address decoder of Unit_A masks off the higher order address bits and decodes only the lower 12 bits for computing the offset into the 4 kilobyte internal memory space.
(bad code)
Example Language: Other
In this design the aliased memory address ranges are these:
0x0000 - 0x0FFF
0x1000 - 0x1FFF
0x2000 - 0x2FFF
0x3000 - 0x3FFF
The same register can be accessed using four different addresses: 0x0000, 0x1000, 0x2000, 0x3000.
The system address filter only blocks access to range 0x0000 - 0x0FFF and does not block access to the aliased addresses in 0x1000 - 0x3FFF range. Thus, untrusted software can leverage the aliased memory addresses to bypass the memory protection.
(good code)
Example Language: Other
In this design the aliased memory addresses (0x1000 - 0x3FFF) could be blocked from all system software access since they are not used by software.
Alternately, the MPU logic can be changed to apply the memory protection policies to the full address range mapped to Unit_A (0x0000 - 0x3FFF).
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1262: Improper Access Control for Register Interface
Weakness ID: 1262
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses memory-mapped I/O registers that act as an interface to hardware functionality from software, but there is improper access control to those registers.
Extended Description
Software commonly accesses peripherals in a System-on-Chip (SoC) or other device through a memory-mapped register interface. Malicious software could tamper with any security-critical hardware data that is accessible directly or indirectly through the register interface, which could lead to a loss of confidentiality and integrity.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data; Modify Memory; Modify Application Data; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Unexpected State; Alter Execution Logic
Scope: Confidentiality, Integrity
Confidentiality of hardware assets may be violated if the protected information can be read out by software through the register interface. Registers storing security state, settings, other security-critical data may be corruptible by software without correctly implemented protections.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Design proper policies for hardware register access from software.
Implementation
Ensure that access control policies for register access are implemented in accordance with the specified design.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness may be exploited if the register interface design does not adequately protect hardware assets from software.
Implementation
Mis-implementation of access control policies may inadvertently allow access to hardware assets through the register interface.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The register interface provides software access to hardware functionality. This functionality is an attack surface. This attack surface may be used to run untrusted code on the system through the register interface. As an example, cryptographic accelerators require a mechanism for software to select modes of operation and to provide plaintext or ciphertext data to be encrypted or decrypted as well as other functions. This functionality is commonly provided through registers.
(bad code)
Example Language: Other
Cryptographic key material stored in registers inside the cryptographic accelerator can be accessed by software.
(good code)
Example Language: Other
Key material stored in registers should never be accessible to software. Even if software can provide a key, all read-back paths to software should be disabled.
Example 2
The example code is taken from the Control/Status Register (CSR) module inside the processor core of the HACK@DAC'19 buggy CVA6 SoC [REF-1340]. In RISC-V ISA [REF-1341], the CSR file contains different sets of registers with different privilege levels, e.g., user mode (U), supervisor mode (S), hypervisor mode (H), machine mode (M), and debug mode (D), with different read-write policies, read-only (RO) and read-write (RW). For example, machine mode, which is the highest privilege mode in a RISC-V system, registers should not be accessible in user, supervisor, or hypervisor modes.
(bad code)
Example Language: SystemVerilog
if (csr_we || csr_read) begin
if ((riscv::priv_lvl_t'(priv_lvl_o & csr_addr.csr_decode.priv_lvl) != csr_addr.csr_decode.priv_lvl) && !(csr_addr.address==riscv::CSR_MEPC)) begin
The vulnerable example code allows the machine exception program counter (MEPC) register to be accessed from a user mode program by excluding the MEPC from the access control check. MEPC as per the RISC-V specification can be only written or read by machine mode code. Thus, the attacker in the user mode can run code in machine mode privilege (privilege escalation).
To mitigate the issue, fix the privilege check so that it throws an Illegal Instruction Exception for user mode accesses to the MEPC register. [REF-1345]
(good code)
Example Language: SystemVerilog
if (csr_we || csr_read) begin
if ((riscv::priv_lvl_t'(priv_lvl_o & csr_addr.csr_decode.priv_lvl) != csr_addr.csr_decode.priv_lvl)) begin
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
virtual interrupt controller in a virtualization product allows crash of host by writing a certain invalid value to a register, which triggers a fatal error instead of returning an error code
Virtualization product does not restrict access to PCI command registers, allowing host crash from the guest.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
This is applicable in the Architecture phase before implementation started. Make sure access policy is specified for the entire memory map. Manual analysis may not ensure the implementation is correct.
Effectiveness: Moderate
Manual Analysis
Registers controlling hardware should have access control implemented. This access control may be checked manually for correct implementation. Items to check consist of how are trusted parties set, how are trusted parties verified, how are accesses verified, etc. Effectiveness of a manual analysis will vary depending upon how complicated the interface is constructed.
Effectiveness: Moderate
Simulation / Emulation
Functional simulation is applicable during the Implementation Phase. Testcases must be created and executed for memory mapped registers to verify adherence to the access control policy. This method can be effective, since functional verification needs to be performed on the design, and verification for this weakness will be included. There can be difficulty covering the entire memory space during the test.
Effectiveness: Moderate
Formal Verification
Formal verification is applicable during the Implementation phase. Assertions need to be created in order to capture illegal register access scenarios and prove that they cannot occur. Formal methods are exhaustive and can be very effective, but creating the cases for large designs may be complex and difficult.
Effectiveness: High
Automated Analysis
Information flow tracking can be applicable during the Implementation phase. Security sensitive data (assets) - for example, as stored in registers - is automatically tracked over time through the design to verify the data doesn't reach illegal destinations that violate the access policies for the memory map. This method can be very effective when used together with simulation and emulation, since detecting violations doesn't rely on specific scenarios or data values. This method does rely on simulation and emulation, so testcases must exist in order to use this method.
Effectiveness: High
Architecture or Design Review
Manual documentation review of the system memory map, register specification, and permissions associated with accessing security-relevant functionality exposed via memory-mapped registers.
Effectiveness: Moderate
Fuzzing
Perform penetration testing (either manual or semi-automated with fuzzing) to verify that access control mechanisms such as the memory protection units or on-chip bus firewall settings adequately protect critical hardware registers from software access.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1274: Improper Access Control for Volatile Memory Containing Boot Code
Weakness ID: 1274
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product conducts a secure-boot process that transfers bootloader code from Non-Volatile Memory (NVM) into Volatile Memory (VM), but it does not have sufficient access control or other protections for the Volatile Memory.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity
Scope: Access Control, IntegrityLikelihood: High
If the volatile-memory-region protections or access controls are insufficient to prevent modifications from an adversary or untrusted agent, the secure boot may be bypassed or replaced with the execution of an adversary's own code.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Ensure that the design of volatile-memory protections is enough to prevent modification from an adversary or untrusted code.
Testing
Test the volatile-memory protections to ensure they are safe from modification or untrusted code.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
As a part of a secure-boot process, the read-only-memory (ROM) code for a System-on-Chip (SoC) or other system fetches bootloader code from Non-Volatile Memory (NVM) and stores the code in Volatile Memory (VM), such as dynamic, random-access memory (DRAM) or static, random-access memory (SRAM). The NVM is usually external to the SoC, while the VM is internal to the SoC. As the code is transferred from NVM to VM, it is authenticated by the SoC's ROM code.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced during hardware architecture or design but can be identified later during testing.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A typical SoC secure boot's flow includes fetching the next piece of code (i.e., the boot loader) from NVM (e.g., serial, peripheral interface (SPI) flash), and transferring it to DRAM/SRAM volatile, internal memory, which is more efficient.
(bad code)
Example Language: Other
The volatile-memory protections or access controls are insufficient.
The memory from where the boot loader executes can be modified by an adversary.
(good code)
Example Language: Other
A good architecture should define appropriate protections or access controls to prevent modification by an adversary or untrusted agent, once the bootloader is authenticated.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Locked memory regions may be modified through other interfaces in a secure-boot-loader image due to improper access control.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Ensure the volatile memory is lockable or has locks. Ensure the volatile memory is locked for writes from untrusted agents or adversaries. Try modifying the volatile memory from an untrusted agent, and ensure these writes are dropped.
Effectiveness: High
Manual Analysis
Analyze the device using the following steps:
Identify all fabric master agents that are active during system Boot Flow when initial code is loaded from Non-volatile storage to volatile memory.
Identify the volatile memory regions that are used for storing loaded system executable program.
During system boot, test programming the identified memory regions in step 2 from all the masters identified in step 1.
Only trusted masters should be allowed to write to the memory regions. For example, pluggable device peripherals should not have write access to program load memory regions.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1317: Improper Access Control in Fabric Bridge
Weakness ID: 1317
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses a fabric bridge for transactions between two Intellectual Property (IP) blocks, but the bridge does not properly perform the expected privilege, identity, or other access control checks between those IP blocks.
Extended Description
For overall system security, it is important that the access-control privileges associated with any fabric transaction are consistently maintained and applied, even when they are routed or translated by a fabric bridge. A bridge that is connected to a fabric without security features forwards transactions to the slave without checking the privilege level of the master and results in a weakness in SoC access-control security. The same weakness occurs if a bridge does not check the hardware identity of the transaction received from the slave interface of the bridge.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Scope: Confidentiality, Integrity, Access Control, AvailabilityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Ensure that the design includes provisions for access-control checks in the bridge for both upstream and downstream transactions.
Implementation
Implement access-control checks in the bridge for both upstream and downstream transactions.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Peripherals, On-chip Fabric, and Interface/IO Problems
Background Details
In hardware designs, different IP blocks are connected through interconnect-bus fabrics (e.g. AHB and OCP). Within a System on Chip (SoC), the IP block subsystems could be using different bus protocols. In such a case, the IP blocks are then linked to the central bus (and to other IP blocks) through a fabric bridge. Bridges are used as bus-interconnect-routing modules that link different protocols or separate, different segments of the overall SoC interconnect.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example is from CVE-2019-6260 [REF-1138]. The iLPC2AHB bridge connects a CPU (with multiple, privilege levels, such as user, superuser, debug, etc.) over AHB interface to an LPC bus. Several peripherals are connected to the LPC bus. The bridge is expected to check the privilege level of the transactions initiated in the core before forwarding them to the peripherals on the LPC bus.
The bridge does not implement the checks and allows reads and writes from all privilege levels.
To address this, designers should implement hardware-based checks that are either hardcoded to block untrusted agents from accessing secure peripherals or implement firmware flows that configure the bridge to block untrusted agents from making arbitrary reads or writes.
Example 2
The example code below is taken from the AES and core local interrupt (CLINT) peripherals of the HACK@DAC'21 buggy OpenPiton SoC. The access to all the peripherals for a given privilege level of the processor is controlled by an access control module in the SoC. This ensures that malicious users with insufficient privileges do not get access to sensitive data, such as the AES keys used by the operating system to encrypt and decrypt information. The security of the entire system will be compromised if the access controls are incorrectly enforced. The access controls are enforced through the interconnect-bus fabrics, where access requests with insufficient access control permissions will be rejected.
The previous code snippet [REF-1382] illustrates an instance of a vulnerable implementation of access control for the CLINT peripheral (see module clint). It also shows a correct implementation of access control for the AES peripheral (see module aes0_wrapper) [REF-1381]. An enable signal (en_o) from the fabric's AXI interface (present in both modules) is used to determine if an access request is made to the peripheral. In the case of the AES peripheral, this en_o signal is first received in a temporary signal en_acct. Then, the access request is enabled (by asserting the en signal) only if the request has sufficient access permissions (i.e., acct_ctrl_i signal should be enabled). However, in the case of the CLINT peripheral, the enable signal, en_o, from the AXI interface, is directly used to enable accesses. As a result, users with insufficient access permissions also get full access to the CLINT peripheral.
To fix this, enable access requests to CLINT [REF-1383] only if the user has sufficient access as indicated by the acct_ctrl_i signal in the boolean && with en_acct.
(good code)
Example Language: SystemVerilog
module clint #(...
) (
...
input logic acct_ctrl_i,
...
);
logic en, en_acct;
...
axi_lite_interface #(...
) axi_lite_interface_i (
...
.en_o ( en_acct ),
...
); assign en = en_acct && acct_ctrl_i;
...
endmodule
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Baseboard Management Controller (BMC) device implements Advanced High-performance Bus (AHB) bridges that do not require authentication for arbitrary read and write access to the BMC's physical address space from the host, and possibly the network [REF-1138].
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Simulation / Emulation
RTL simulation to ensure that bridge-access controls are implemented properly.
Effectiveness: High
Formal Verification
Formal verification of bridge RTL to ensure that access control cannot be bypassed.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1245: Improper Finite State Machines (FSMs) in Hardware Logic
Weakness ID: 1245
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Faulty finite state machines (FSMs) in the hardware logic allow an attacker to put the system in an undefined state, to cause a denial of service (DoS) or gain privileges on the victim's system.
Extended Description
The functionality and security of the system heavily depend on the implementation of FSMs. FSMs can be used to indicate the current security state of the system. Lots of secure data operations and data transfers rely on the state reported by the FSM.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Unexpected State; DoS: Crash, Exit, or Restart; DoS: Instability; Gain Privileges or Assume Identity
Scope: Availability, Access Control
Faulty FSM designs that do not account for all states, either through undefined states (left as don't cares) or through incorrect implementation, might lead an attacker to drive the system into an unstable state from which the system cannot recover without a reset, thus causing a DoS. Depending on what the FSM is used for, an attacker might also gain additional privileges to launch further attacks and compromise the security guarantees.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Define all possible states and handle all unused states through default statements. Ensure that system defaults to a secure state.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The Finite State Machine (FSM) shown in the "bad" code snippet below assigns the output ("out") based on the value of state, which is determined based on the user provided input ("user_input").
3'h0:
3'h1:
3'h2:
3'h3: state = 2'h3;
3'h4: state = 2'h2;
3'h5: state = 2'h1;
endcase
end
out <= {1'h1, state};
endmodule
The case statement does not include a default to handle the scenario when the user provides inputs of 3'h6 and 3'h7. Those inputs push the system to an undefined state and might cause a crash (denial of service) or any other unanticipated outcome.
Adding a default statement to handle undefined inputs mitigates this issue. This is shown in the "Good" code snippet below. The default statement is in bold.
(good code)
Example Language: Verilog
case (user_input)
3'h0:
3'h1:
3'h2:
3'h3: state = 2'h3;
3'h4: state = 2'h2;
3'h5: state = 2'h1;
default: state = 2'h0;
endcase
Weakness Ordinalities
Ordinality
Description
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1332: Improper Handling of Faults that Lead to Instruction Skips
Weakness ID: 1332
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device is missing or incorrectly implements circuitry or sensors that detect and mitigate the skipping of security-critical CPU instructions when they occur.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism; Alter Execution Logic; Unexpected State; Varies by Context
Scope: Confidentiality, Integrity, AuthenticationLikelihood: High
Depending on the context, instruction skipping can
have a broad range of consequences related to the
generic bypassing of security critical code.
Attackers can use fault injection techniques to
alter the operating conditions of hardware so that
security-critical instructions are skipped more
frequently or more reliably than they would in a
"natural" setting.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Design strategies for ensuring safe failure if
inputs, such as Vcc, are modified out of acceptable
ranges.
Architecture and Design
Design strategies for ensuring safe behavior if
instructions attempt to be skipped.
Architecture and Design
Identify mission critical secrets that should
be wiped if faulting is detected, and design a
mechanism to do the deletion.
Implementation
Add redundancy by performing an operation
multiple times, either in space or time, and perform
majority voting. Additionally, make conditional
instruction timing unpredictable.
Implementation
Use redundant operations or canaries to
detect and respond to faults.
Implementation
Ensure that fault mitigations are strong enough
in practice. For example, a low power detection
mechanism that takes 50 clock cycles to trigger at lower
voltages may be an insufficient security mechanism if
the instruction counter has already progressed with no
other CPU activity occurring.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection Against Voltage and Clock Glitches
Background Details
The operating conditions of hardware may change
in ways that cause unexpected behavior to occur,
including the skipping of security-critical CPU
instructions. Generally, this can occur due to
electrical disturbances or when the device operates
outside of its expected conditions.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Failure to design appropriate countermeasures to common fault injection techniques can manifest this weakness.
Implementation
This weakness can arise if the hardware design incorrectly implements countermeasures to prevent fault injection.
In practice, application code may contain
conditional branches that are security-sensitive (e.g.,
accepting or rejecting a user-provided password). These
conditional branches are typically implemented by a
single conditional branch instruction in the program
binary which, if skipped, may lead to effectively
flipping the branch condition - i.e., causing the wrong
security-sensitive branch to be taken.
This affects processes such as
firmware authentication, password
verification, and other security-sensitive
decision points.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A smart card contains authentication credentials that are used as authorization to enter a building. The credentials are only accessible when a correct PIN is presented to the card.
(bad code)
Example Language: Other
The card emits the credentials when a voltage anomaly is injected into the power line to the device at a particular time after providing an incorrect PIN to the card, causing the internal program to accept the incorrect PIN.
There are several ways this weakness could be fixed.
(good code)
Example Language: Other
add an internal filter or internal power supply in series with the power supply pin on the device
add sensing circuitry to reset the device if out of tolerance conditions are detected
add additional execution sensing circuits to monitor the execution order for anomalies and abort the action or reset the device under fault conditions
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis
This weakness can be found using automated static analysis once a developer has indicated which code paths are critical to protect.
Effectiveness: Moderate
Simulation / Emulation
This weakness can be found using automated dynamic analysis. Both emulation of a CPU with instruction skips, as well as RTL simulation of a CPU IP, can indicate parts of the code that are sensitive to faults due to instruction skips.
Effectiveness: Moderate
Manual Analysis
This weakness can be found using manual (static) analysis. The analyst has security objectives that are matched against the high-level code. This method is less precise than emulation, especially if the analysis is done at the higher level language rather than at assembly level.
Effectiveness: Moderate
Functional Areas
Power
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Improper Check or Handling of Exceptional Conditions
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Josep Balasch, Benedikt Gierlichs and Ingrid Verbauwhede. "An In-depth and Black-box Characterization of the Effects of Clock Glitches on 8-bit MCUs". 2011 Workshop on Fault Diagnosis and Tolerance in Cryptography (IEEE). 2011-09.
<https://ieeexplore.ieee.org/document/6076473>.
[REF-1222]
Alexandre Menu, Jean-Max Dutertre, Olivier Potin and Jean-Baptiste Rigaud. "Experimental Analysis of the Electromagnetic Instruction Skip Fault Model". IEEE Xplore. 2020-04-30.
<https://ieeexplore.ieee.org/document/9081261>.
CWE-1351: Improper Handling of Hardware Behavior in Exceptionally Cold Environments
Weakness ID: 1351
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware device, or the firmware running on it, is
missing or has incorrect protection mechanisms to maintain
goals of security primitives when the device is cooled below
standard operating temperatures.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context; Unexpected State
Scope: Integrity, AuthenticationLikelihood: Low
This may result in a weakness when the
starting state of the volatile memory is being
relied upon for a security decision. Consequences
of this weakness are highly contextual.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The system should account for security primitive behavior when cooled outside standard temperatures.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
The hardware designer may improperly anticipate
hardware behavior when exposed to exceptionally cold
conditions. As a result, they may introduce a weakness by not
accounting for the modified behavior of critical components
when in extreme environments.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Embedded
(Undetermined Prevalence)
Class: Microcomputer
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a product in which power loss
does not clear or reset any volatile state when cooled
below standard operating temperatures. For example, a
Physical Unclonable Function (PUF) may be supplied as
a security primitive to improve confidentiality,
authenticity, and integrity guarantees.
(bad code)
Example Language: Algorithm
When the PUF is paired with DRAM, SRAM, or
another temperature-sensitive entropy source,
the system designer may introduce a weakness by
failing to account for the chosen entropy
source's behavior at exceptionally low
temperatures.
In the case of DRAM and SRAM, when power is cycled
at low temperatures, the device will not contain the
bitwise biasing caused by inconsistencies in
manufacturing and will instead contain the data from
previous boot. Should the PUF primitive be used in a
cryptographic construction which does not account
for full adversary control of PUF seed data,
weakness would arise.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Improper Check or Handling of Exceptional Conditions
Vulnerability Mapping Notes
Usage
ALLOWED-WITH-REVIEW
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
This weakness does not cover "Cold Boot
Attacks" wherein RAM or other external storage is
super-cooled and read externally by an
attacker.
Carefully read both the name and description to ensure
that this mapping is an appropriate fit. Do not try to
'force' a mapping to a lower-level Base/Variant simply
to comply with this preferred level of abstraction.
Nikolaos Athanasios Anagnostopoulos, Tolga Arul, Markus Rosenstihl, André Schaller, Sebastian Gabmeyer and Stefan Katzenbeisser. "Low-Temperature Data Remnanence Attacks Against Intrinsic SRAM PUFs". 2018-10-15.
<https://ieeexplore.ieee.org/abstract/document/8491873/>.
[REF-1182]
Yuan Cao, Yunyi Guo, Benyu Liu, Wei Ge, Min Zhu and Chip-Hong Chang. "A Fully Digital Physical Unclonable Function Based Temperature Sensor for Secure Remote Sensing". 2018-10-11.
<https://ieeexplore.ieee.org/abstract/document/8487347/>.
[REF-1183]
Urbi Chatterjee, Soumi Chatterjee, Debdeep Mukhopadhyay and Rajat Subhra Chakraborty. "Machine Learning Assisted PUF Calibration for Trustworthy Proof of Sensor Data in IoT". 2020-06.
<https://dl.acm.org/doi/abs/10.1145/3393628>.
(URL validated: 2023-04-07)
CWE-1260: Improper Handling of Overlap Between Protected Memory Ranges
Weakness ID: 1260
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product allows address regions to overlap, which can result in the bypassing of intended memory protection.
Extended Description
Isolated memory regions and access control (read/write) policies are used by hardware to protect privileged software. Software components are often allowed to change or remap memory region definitions in order to enable flexible and dynamically changeable memory management by system software.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Scope: Confidentiality, Integrity, AvailabilityLikelihood: High
If a software component running at lower privilege can program a memory address region to overlap with other memory regions used by software running at higher privilege, privilege escalation may be available to attackers. The memory protection unit (MPU) logic can incorrectly handle such an address overlap and allow the lower-privilege software to read or write into the protected memory region, resulting in a privilege escalation attack. An address overlap weakness can also be used to launch a denial of service attack on the higher-privilege software memory regions.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Ensure that memory regions are isolated as intended and that access control (read/write) policies are used by hardware to protect privileged software.
Implementation
For all of the programmable memory protection regions, the memory protection unit (MPU) design can define a priority scheme.
For example: if three memory regions can be programmed (Region_0, Region_1, and Region_2), the design can enforce a priority scheme, such that, if a system address is within multiple regions, then the region with the lowest ID takes priority and the access-control policy of that region will be applied. In some MPU designs, the priority scheme can also be programmed by trusted software.
Hardware logic or trusted firmware can also check for region definitions and block programming of memory regions with overlapping addresses.
The memory-access-control-check filter can also be designed to apply a policy filter to all of the overlapping ranges, i.e., if an address is within Region_0 and Region_1, then access to this address is only granted if both Region_0 and Region_1 policies allow the access.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design or implementation and identified later during the Testing phase.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Memory Hardware
(Undetermined Prevalence)
Processor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
For example, consider a design with a 16-bit address that has two software privilege levels: Privileged_SW and Non_privileged_SW. To isolate the system memory regions accessible by these two privilege levels, the design supports three memory regions: Region_0, Region_1, and Region_2.
Each region is defined by two 32 bit registers: its range and its access policy.
Address_range[15:0]: specifies the Base address of the region
Address_range[31:16]: specifies the size of the region
Access_policy[31:0]: specifies what types of software can access a region and which actions are allowed
Certain bits of the access policy are defined symbolically as follows:
Access_policy.read_np: if set to one, allows reads from Non_privileged_SW
Access_policy.write_np: if set to one, allows writes from Non_privileged_SW
Access_policy.execute_np: if set to one, allows code execution by Non_privileged_SW
Access_policy.read_p: if set to one, allows reads from Privileged_SW
Access_policy.write_p: if set to one, allows writes from Privileged_SW
Access_policy.execute_p: if set to one, allows code execution by Privileged_SW
For any requests from software, an address-protection filter checks the address range and access policies for each of the three regions, and only allows software access if all three filters allow access.
Consider the following goals for access control as intended by the designer:
Region_0 & Region_1: registers are programmable by Privileged_SW
Region_2: registers are programmable by Non_privileged_SW
The intention is that Non_privileged_SW cannot modify memory region and policies defined by Privileged_SW in Region_0 and Region_1. Thus, it cannot read or write the memory regions that Privileged_SW is using.
(bad code)
Non_privileged_SW can program the Address_range register for Region_2 so that its address overlaps with the ranges defined by Region_0 or Region_1. Using this capability, it is possible for Non_privileged_SW to block any memory region from being accessed by Privileged_SW, i.e., Region_0 and Region_1.
This design could be improved in several ways.
(good code)
Ensure that software accesses to memory regions are only permitted if all three filters permit access. Additionally, the scheme could define a memory region priority to ensure that Region_2 (the memory region defined by Non_privileged_SW) cannot overlap Region_0 or Region_1 (which are used by Privileged_SW).
Example 2
The example code below is taken from the IOMMU controller module of the HACK@DAC'19 buggy CVA6 SoC [REF-1338]. The static memory map is composed of a set of Memory-Mapped Input/Output (MMIO) regions covering different IP agents within the SoC. Each region is defined by two 64-bit variables representing the base address and size of the memory region (XXXBase and XXXLength).
In this example, we have 12 IP agents, and only 4 of them are called out for illustration purposes in the code snippets. Access to the AES IP MMIO region is considered privileged as it provides access to AES secret key, internal states, or decrypted data.
The vulnerable code allows the overlap between the protected MMIO region of the AES peripheral and the unprotected UART MMIO region. As a result, unprivileged users can access the protected region of the AES IP. In the given vulnerable example UART MMIO region starts at address 64'h1000_0000 and ends at address 64'h1011_1000 (UARTBase is 64'h1000_0000, and the size of the region is provided by the UARTLength of 64'h0011_1000).
On the other hand, the AES MMIO region starts at address 64'h1010_0000 and ends at address 64'h1010_1000, which implies an overlap between the two peripherals' memory regions. Thus, any user with access to the UART can read or write the AES MMIO region, e.g., the AES secret key.
To mitigate this issue, remove the overlapping address regions by decreasing the size of the UART memory region or adjusting memory bases for all the remaining peripherals. [REF-1339]
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
processor design flaw allows ring 0 code to access more privileged rings by causing a register window to overlap a range of protected system RAM [REF-1100]
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Create a high privilege memory block of any arbitrary size. Attempt to create a lower privilege memory block with an overlap of the high privilege memory block. If the creation attempt works, fix the hardware. Repeat the test.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.6, CWE-1260 and CWE-1316 are siblings under view 1000, but CWE-1260 might be a parent of CWE-1316. More analysis is warranted.
CWE-1384: Improper Handling of Physical or Environmental Conditions
Weakness ID: 1384
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not properly handle unexpected physical or environmental conditions that occur naturally or are artificially induced.
Technical Nuance
For example, an unexpected physical or environmental condition may cause the flipping of a bit that is used for an authentication decision. This unexpected condition could occur naturally or be induced artificially by an adversary.
Physical or environmental conditions of concern are:
Atmospheric characteristics: extreme temperature ranges, etc.
Interference: electromagnetic interference (EMI), radio frequency interference (RFI), etc.
Assorted light sources: white light, ultra-violet light (UV), lasers, infrared (IR), etc.
Power variances: under-voltages, over-voltages, under-current, over-current, etc.
Clock variances: glitching, overclocking, clock stretching, etc.
Component aging and degradation
Materials manipulation: focused ion beams (FIB), etc.
Exposure to radiation: x-rays, cosmic radiation, etc.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Property
Improper
Behavior-Type
Handling
Other
Physical or Environmental Conditions
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context; Unexpected State
Scope: Confidentiality, Integrity, Availability
Consequences of this weakness are highly dependent on the role of affected components within the larger product.
Potential Mitigations
Phase(s)
Mitigation
Requirements
In requirements, be specific about expectations for how the product will perform when it exceeds physical and environmental boundary conditions, e.g., by shutting down.
Architecture and Design; Implementation
Where possible, include independent components that can detect excess environmental conditions and have the capability to shut down the product.
Architecture and Design; Implementation
Where possible, use shielding or other materials that can increase the adversary's workload and reduce the likelihood of being able to successfully trigger a security-related failure.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Improper Check or Handling of Exceptional Conditions
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Protection Against Voltage and Clock Glitches
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Faults that Lead to Instruction Skips
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Dimensions: Other: Physical or Environmental Conditions
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware products are typically only guaranteed to behave correctly within certain physical limits or environmental conditions. Such products cannot necessarily control the physical or external conditions to which they are subjected. However, the inability to handle such conditions can undermine a product's security.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
The product's design might not consider checking and handling extreme conditions.
Manufacturing
For hardware manufacturing, sub-par components might be chosen that are not able to handle the expected environmental conditions.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Technologies
Class: System on Chip
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Below is a representative snippet of C code that is part of the secure-boot flow. A signature of the runtime-firmware image is calculated and compared against a golden value. If the signatures match, the bootloader loads runtime firmware. If there is no match, an error halt occurs. If the underlying hardware executing this code does not contain any circuitry or sensors to detect voltage or clock glitches, an attacker might launch a fault-injection attack right when the signature check is happening (at the location marked with the comment), causing a bypass of the signature-checking process.
(bad code)
Example Language: C
...
if (signature_matches) // <-Glitch Here
{
load_runtime_firmware();
}
else
{
do_not_load_runtime_firmware();
}
...
After bypassing secure boot, an attacker can gain access to system assets to which the attacker should not have access.
(good code)
Example Language: Other
If the underlying hardware detects a voltage or clock glitch, the information can be used to prevent the glitch from being successful.
Example 2
In 2016, a security researcher, who was also a patient using a pacemaker, was on an airplane when a bit flip occurred in the pacemaker, likely due to the higher prevalence of cosmic radiation at such heights. The pacemaker was designed to account for bit flips and went into a default safe mode, which still forced the patient to go to a hospital to get it reset. The bit flip also inadvertently enabled the researcher to access the crash file, perform reverse engineering, and detect a hard-coded key. [REF-1101]
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Lack of anti-glitch protections allows an attacker to launch a physical attack to bypass the secure boot and read protected eFuses.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
CWE-1261: Improper Handling of Single Event Upsets
Weakness ID: 1261
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware logic does not effectively handle when single-event upsets (SEUs) occur.
Extended Description
Technology trends such as CMOS-transistor down-sizing, use of
new materials, and system-on-chip architectures continue to increase the
sensitivity of systems to soft errors. These errors are random, and
their causes might be internal (e.g., interconnect coupling) or external
(e.g., cosmic radiation). These soft errors are not permanent in nature
and cause temporary bit flips known as single-event upsets (SEUs).
SEUs are induced errors in circuits caused when charged particles lose
energy by ionizing the medium through which they pass, leaving behind a
wake of electron-hole pairs that cause temporary failures. If these
failures occur in security-sensitive modules in a chip, it might
compromise the security guarantees of the chip. For instance, these
temporary failures could be bit flips that change the privilege of
a regular user to root.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Crash, Exit, or Restart; DoS: Instability; Gain Privileges or Assume Identity; Bypass Protection Mechanism
Scope: Availability, Access Control
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Implement triple-modular redundancy around security-sensitive modules.
Architecture and Design
SEUs mostly affect SRAMs. For SRAMs storing security-critical data, implement Error-Correcting-Codes (ECC) and Address Interleaving.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Improper Handling of Physical or Environmental Conditions
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This is an example from [REF-1089]. See the reference for full details of this issue.
Parity is error detecting but not error correcting.
(bad code)
Example Language: Other
Due to single-event upsets, bits are flipped in memories. As a result, memory-parity checks fail, which results in restart and a temporary denial of service of two to three minutes.
(good code)
Example Language: Other
Using error-correcting codes could have avoided the restart caused by SEUs.
Example 2
In 2016, a security researcher, who was also a patient using a pacemaker, was on an airplane when a bit flip occurred in the pacemaker, likely due to the higher prevalence of cosmic radiation at such heights. The pacemaker was designed to account for bit flips and went into a default safe mode, which still forced the patient to go to a hospital to get it reset. The bit flip also inadvertently enabled the researcher to access the crash file, perform reverse engineering, and detect a hard-coded key. [REF-1101]
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Improper Check or Handling of Exceptional Conditions
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1192: Improper Identifier for IP Block used in System-On-Chip (SOC)
Weakness ID: 1192
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The System-on-Chip (SoC) does not have unique, immutable identifiers for each of its components.
Technical Nuance
There are several variants of this weakness:
A "missing" identifier is when the SoC does not define
any mechanism to uniquely identify the IP.
An "insufficient" identifier might provide
some defenses - for example, against the most common
attacks - but it does not protect against everything
that is intended.
A "misconfigured" mechanism occurs when a mechanism
is available but not implemented correctly.
An "ignored" identifier occurs when the SoC/IP has not applied
any policies or does not act upon the identifier securely.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Strategy: Separation of Privilege
Every identity generated in the SoC should be unique and
immutable in hardware. The actions that an IP is trusted or
not trusted should be clearly defined, implemented,
configured, and tested. If the definition is implemented via a
policy, then the policy should be immutable or protected with
clear authentication and authorization.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
A System-on-Chip (SoC) comprises several components (IP) with varied
trust requirements. It is required that each IP is identified
uniquely and should distinguish itself from other entities in
the SoC without any ambiguity. The unique secured identity is
required for various purposes. Most of the time the identity is used
to route a transaction or perform certain actions, including
resetting, retrieving sensitive information, and acting upon or on
behalf of something else.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Operation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Violation of Secure Design Principles
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1331: Improper Isolation of Shared Resources in Network On Chip (NoC)
Weakness ID: 1331
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The Network On Chip (NoC) does not isolate or incorrectly isolates its on-chip-fabric and internal resources such that they are shared between trusted and untrusted agents, creating timing channels.
Extended Description
Typically, network on chips (NoC) have many internal resources that are shared between packets from different trust domains. These resources include internal buffers, crossbars and switches, individual ports, and channels. The sharing of resources causes contention and introduces interference between differently trusted domains, which poses a security threat via a timing channel, allowing attackers to infer data that belongs to a trusted agent. This may also result in introducing network interference, resulting in degraded throughput and latency.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Resource Consumption (Other); Varies by Context; Other
Scope: Confidentiality, AvailabilityLikelihood: Medium
Attackers may infer data that belongs to a trusted agent. The methods used to perform this attack may result in noticeably increased resource consumption.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Implement priority-based arbitration inside the NoC and have dedicated buffers or virtual channels for routing secret data from trusted agents.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Peripherals, On-chip Fabric, and Interface/IO Problems
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Isolation of Shared Resources on System-on-a-Chip (SoC)
Background Details
"Network-on-chip" (NoC) is a commonly-used term used for hardware interconnect fabrics used by multicore Systems-on-Chip (SoC). Communication between modules on the chip uses packet-based methods, with improved efficiency and scalability compared to bus architectures [REF-1241].
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Security Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a NoC that implements a one-dimensional mesh network with four nodes. This supports two flows: Flow A from node 0 to node 3 (via node 1 and node 2) and Flow B from node 1 to node 2. Flows A and B share a common link between Node 1 and Node 2. Only one flow can use the link in each cycle.
One of the masters to this NoC implements a cryptographic algorithm (RSA), and another master to the NoC is a core that can be exercised by an attacker. The RSA algorithm performs a modulo multiplication of two large numbers and depends on each bit of the secret key. The algorithm examines each bit in the secret key and only performs multiplication if the bit is 1. This algorithm is known to be prone to timing attacks. Whenever RSA performs multiplication, there is additional network traffic to the memory controller. One of the reasons for this is cache conflicts.
Since this is a one-dimensional mesh, only one flow can use the link in each cycle. Also, packets from the attack program and the RSA program share the output port of the network-on-chip. This contention results in network interference, and the throughput and latency of one flow can be affected by the other flow's demand.
(attack code)
The attacker runs a loop program on the core they control, and this causes a cache miss in every iteration for the RSA algorithm. Thus, by observing network-traffic bandwidth and timing, the attack program can determine when the RSA algorithm is doing a multiply operation (i.e., when the secret key bit is 1) and eventually extract the entire, secret key.
There may be different ways to fix this particular weakness.
(good code)
Example Language: Other
Implement priority-based arbitration inside the NoC and have dedicated buffers or virtual channels for routing secret data from trusted agents.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Improper isolation of shared resource in a network-on-chip leads to denial of service
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Providing marker flags to send through the interfaces coupled with examination of which users are able to read or manipulate the flags will help verify that the proper isolation has been achieved and is effective.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Violation of Secure Design Principles
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Hassan M. G. Wassel, Ying Gao, Jason K. Oberg, Tedd Huffmire, Ryan Kastner, Frederic T. Chong, Timothy Sherwood. "SurfNoC: A Low Latency and Provably Non-Interfering Approach to Secure Networks-On-Chip". 2013.
<http://cseweb.ucsd.edu/~kastner/papers/isca13-surfNOC.pdf>.
Subodha Charles and Prabhat Mishra. "A Survey of Network-on-Chip Security Attacks and Countermeasures". ACM Computing Surveys. 2021-05.
<https://dl.acm.org/doi/fullHtml/10.1145/3450964>.
(URL validated: 2025-07-29)
CWE-1189: Improper Isolation of Shared Resources on System-on-a-Chip (SoC)
Weakness ID: 1189
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The System-On-a-Chip (SoC) does not properly isolate shared resources between trusted and untrusted agents.
Extended Description
A System-On-a-Chip (SoC) has a lot of functionality, but it may have a limited number of pins or pads. A pin can only perform one function at a time. However, it can be configured to perform multiple different functions. This technique is called pin multiplexing. Similarly, several resources on the chip may be shared to multiplex and support different features or functions. When such resources are shared between trusted and untrusted agents, untrusted agents may be able to access the assets intended to be accessed only by the trusted agents.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Property
Improper
Behavior-Type
Isolation
Resource-Property
Shared
Resource-Type
Resources
Technology
System-on-a-Chip
Acronym
(SoC)
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access Control
If resources being used by a trusted user are shared with an untrusted user, the untrusted user may be able to modify the functionality of the shared resource of the trusted user.
Quality Degradation
Scope: Integrity
The functionality of the shared resource may be intentionally degraded.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Strategy: Separation of Privilege
When sharing resources, avoid mixing agents of varying trust levels.
Untrusted agents should not share resources with trusted agents.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Non-Transparent Sharing of Microarchitectural Resources
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Isolation of Shared Resources in Network On Chip (NoC)
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the following SoC
design. The Hardware Root of Trust (HRoT) local SRAM is memory mapped in the core{0-N}
address space. The HRoT allows or disallows access to private memory ranges, thus
allowing the sram to function as a mailbox for communication between untrusted and
trusted HRoT partitions.
We assume that the threat is from malicious software in
the untrusted domain. We assume this software has access
to the core{0-N} memory map and can be running at any
privilege level on the untrusted cores. The capability
of this threat in this example is communication to and
from the mailbox region of SRAM modulated by the
hrot_iface. To address this threat, information must not
enter or exit the shared region of SRAM through
hrot_iface when in secure or privileged mode.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Baseboard Management Controller (BMC) device implements Advanced High-performance Bus (AHB) bridges that do not require authentication for arbitrary read and write access to the BMC's physical address space from the host, and possibly the network [REF-1138].
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Dynamic Analysis
Pre-silicon / post-silicon: Test access to shared systems resources (memory ranges, control registers, etc.) from untrusted software to verify that the assets are not incorrectly exposed to untrusted agents. Note that access to shared resources can be dynamically allowed or revoked based on system flows. Security testing should cover such dynamic shared resource allocation and access control modification flows.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Comprehensive Categorization: Violation of Secure Design Principles
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1232: Improper Lock Behavior After Power State Transition
Weakness ID: 1232
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Register lock bit protection disables changes to system configuration once the bit is set. Some of the protected registers or lock bits become programmable after power state transitions (e.g., Entry and wake from low power sleep modes) causing the system configuration to be changeable.
Technical Nuance
Some common weaknesses that can exist in such a protection scheme are that the lock gets cleared, the values of the protected registers get reset, or the lock become programmable.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory
Scope: Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Security Lock bit protections should be reviewed for behavior across supported power state transitions.
Security lock programming flow and lock properties should be tested in pre-silicon and post-silicon testing including testing across power transitions.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Devices may allow device configuration controls that need to be programmed after device power reset via a trusted firmware or software module (commonly set by BIOS/bootloader) and then locked from any further modification. This action is commonly implemented using a programmable lock bit, which, when set, disables writes to a protected set of registers or address regions.
After a power state transition, the lock bit is set to unlocked.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the memory configuration settings of a system that uses DDR3 DRAM memory. Protecting the DRAM memory configuration from modification by software is required to ensure that system memory access control protections cannot be bypassed. This can be done by using lock bit protection that locks all of the memory configuration registers. The memory configuration lock can be set by the BIOS during the boot process.
If such a system also supports a rapid power on mode like hibernate, the DRAM data must be saved to a disk before power is removed and restored back to the DRAM once the system powers back up and before the OS resumes operation after returning from hibernate.
To support the hibernate transition back to the operating state, the DRAM memory configuration must be reprogrammed even though it was locked previously. As the hibernate resume does a partial reboot, the memory configuration could be altered before the memory lock is set. Functionally the hibernate resume flow requires a bypass of the lock-based protection. The memory configuration must be securely stored and restored by trusted system firmware. Lock settings and system configuration must be restored to the same state it was in before the device entered into the hibernate mode.
Example 2
The example code below is taken from the register lock module (reglk_wrapper) of the Hack@DAC'21 buggy OpenPiton System-on-Chip (SoC). Upon powering on, most of the silicon registers are initially unlocked. However, critical resources must be configured and locked by setting the lock bit in a register.
In this module, a set of six memory-mapped I/O registers (reglk_mem) is defined and maintained to control the access control of registers inside different peripherals in the SoC [REF-1432]. Each bit represents a register's read/write ability or sets of registers inside a peripheral. Setting improper lock values after system power transition or system rest would make a temporary window for the attackers to read unauthorized data, e.g., secret keys from the crypto engine, and write illegitimate data to critical registers, e.g., framework data. Furthermore, improper register lock values can also result in DoS attacks.
In this faulty implementation, the locks are disabled, i.e., initialized to zero, at reset instead of setting them to their appropriate values [REF-1433]. Improperly initialized locks might allow unauthorized access to sensitive registers, compromising the system's security.
(bad code)
Example Language: SystemVerilog
module reglk_wrapper #(
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~jtag_unlock && ~rst_9))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'h0;
end
end
...
To resolve this issue, it is crucial to ensure that register locks are correctly initialized during the reset phase of the SoC. Correct initialization values should be established to maintain the system's integrity, security, and predictable behavior and allow for proper control of peripherals. The specifics of initializing register locks and their values depend on the SoC's design and the system's requirements; for example, access to all registers through the user privilege level should be locked at reset. To address the problem depicted in the bad code example [REF-1433], the default value for "reglk_mem" should be set to 32'hFFFFFFFF. This ensures that access to protected data is restricted during power state transition or after reset until the system state transition is complete and security procedures have properly configured the register locks.
(good code)
Example Language: SystemVerilog
module reglk_wrapper #(
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~jtag_unlock && ~rst_9))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'hffffffff;
end
end
...
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1323: Improper Management of Sensitive Trace Data
Weakness ID: 1323
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Trace data collected from several sources on the
System-on-Chip (SoC) is stored in unprotected locations or
transported to untrusted agents.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: Confidentiality
An adversary can read secret values if they are captured in debug traces and stored unsafely. If trace data (such as from debug) is stored in unprotected memory, an
untrusted software debugger can access these traces and
extract secret information. Additionally, if
security-sensitive traces are not tagged as secure, an
untrusted hardware debugger might access them to extract
confidential information.
Potential Mitigations
Phase(s)
Mitigation
Implementation
Since
these traces are collected from several security-sensitive
sources, they must be protected against untrusted
debuggers.
Tag traces to indicate owner and debugging privilege level (designer, OEM, or end user) needed to access that trace.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
To facilitate verification of complex System-on-Chip
(SoC) designs, SoC integrators add specific IP blocks that
trace the SoC's internal signals in real-time. This
infrastructure enables observability of the SoC's internal
behavior, validation of its functional design,
and detection of hardware and software bugs. Such tracing
IP blocks collect traces from several sources on the SoC
including the CPU, crypto coprocessors, and on-chip fabrics. Traces collected from these sources are then
aggregated inside trace IP block and forwarded to trace
sinks, such as debug-trace ports that facilitate debugging by
external hardware and software debuggers.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
In a SoC, traces generated from sources
include security-sensitive IP blocks such as CPU (with
tracing information such as instructions executed and
memory operands), on-chip fabric (e.g., memory-transfer
signals, transaction type and destination, and
on-chip-firewall-error signals), power-management
IP blocks (e.g., clock- and power-gating signals), and
cryptographic coprocessors (e.g., cryptographic keys and
intermediate values of crypto operations), among
other non-security-sensitive IP blocks including timers
and other functional blocks. The collected traces are
then forwarded to the debug and trace interface used by
the external hardware debugger.
(bad code)
Example Language: Other
The traces do
not have any privilege level attached to them. All
collected traces can be viewed by any debugger (i.e., SoC
designer, OEM debugger, or end user).
(good code)
Example Language: Other
Some of the
traces are SoC-design-house secrets, while some are OEM
secrets. Few are end-user secrets and the rest are
not security-sensitive. Tag all traces with the
appropriate, privilege level at the source. The bits
indicating the privilege level must be immutable in
their transit from trace source to the final, trace
sink. Debugger privilege level must be checked before
providing access to traces.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Jerry Backer, David Hely and Ramesh Karri. "Secure and Flexible Trace-Based Debugging of Systems-on-Chip". 2016-12.
<https://dl.acm.org/doi/pdf/10.1145/2994601>.
(URL validated: 2025-07-29)
Content
History
Submissions
Submission Date
Submitter
Organization
2020-07-20
(CWE 4.3, 2020-12-10)
Hareesh Khattri, Parbati K. Manna, and Arun Kanuparthi
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product is designed with access restricted to certain information, but it does not sufficiently protect against an unauthorized actor with physical access to these areas.
Extended Description
The specific requirements around how robust the design of the physical protection mechanism depends on the type of product being protected. Selecting the correct physical protection mechanism and properly enforcing it through implementation and manufacturing are critical to the overall physical security of the product.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Confidentiality, Integrity, Access Control
Sections of a product intended to have restricted access may be inadvertently or intentionally rendered accessible when the implemented physical protections are insufficient.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Specific protection requirements depend strongly on contextual factors including the level of acceptable risk associated with compromise to the product's protection mechanism. Designers could incorporate anti-tampering measures that protect against or detect when the product has been tampered with.
Testing
The testing phase of the lifecycle should establish a method for determining whether the protection mechanism is sufficient to prevent unauthorized access.
Manufacturing
Ensure that all protection mechanisms are fully activated at the time of manufacturing and distribution.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Non-Volatile Information Not Protected During Debug
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can arise if design decisions are made that do not align with the intended physical protection of the product.
Manufacturing
While the architecture and design phase of the product may have accurately met the intended robustness for product physical protections, this phase may introduce the weakness through errors in physically manufacturing the product.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
CWE-1250: Improper Preservation of Consistency Between Independent Representations of Shared State
Weakness ID: 1250
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product has or supports multiple distributed components or sub-systems that are each required to keep their own local copy of shared data - such as state or cache - but the product does not ensure that all local copies remain consistent with each other.
Extended Description
In highly distributed environments, or on systems with distinct physical components that operate independently, there is often a need for each component to store and update its own local copy of key data such as state or cache, so that all components have the same "view" of the overall system and operate in a coordinated fashion. For example, users of a social media service or a massively multiplayer online game might be using their own personal computers while also interacting with different physical hosts in a globally distributed service, but all participants must be able to have the same "view" of the world. Alternately, a processor's Memory Management Unit (MMU) might have "shadow" MMUs to distribute its workload, and all shadow MMUs are expected to have the same accessible ranges of memory.
In such environments, it becomes critical for
the product to ensure that this "shared state" is
consistently modified across all distributed systems.
If state is not consistently maintained across all
systems, then critical transactions might take place
out of order, or some users might not get the same
data as other users. When this inconsistency affects
correctness of operations, it can introduce
vulnerabilities in mechanisms that depend on
consistent state.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Unexpected State
Scope: Other
One or more of the components/sub-systems could
assume that the state is different than it actually
is.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Improper Control of a Resource Through its Lifetime
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Application-Level Admin Tool with Inconsistent View of Underlying Operating System
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Cloud Computing
(Undetermined Prevalence)
Security Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Suppose a processor's Memory Management Unit (MMU) has 5 other shadow MMUs to distribute its workload for its various cores. Each MMU has the start address and end address of "accessible" memory. Any time this accessible range changes (as per the processor's boot status), the main MMU sends an update message to all the shadow MMUs.
Suppose the interconnect fabric does not prioritize such "update" packets over other general traffic packets. This introduces a race condition. If an attacker can flood the target with enough messages so that some of those attack packets reach the target before the new access ranges gets updated, then the attacker can leverage this scenario.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Research Gap
Issues related to state and cache - creation,
preservation, and update - are a significant gap in
CWE that is expected to be addressed in future
versions. It likely has relationships to concurrency
and synchronization, incorrect behavior order, and
other areas that already have some coverage in CWE,
although the focus has typically been on independent
processes on the same operating system - not on
independent systems that are all a part of a larger
system-of-systems.
References
[REF-1069]
Tanakorn Leesatapornwongsa, Jeffrey F. Lukman, Shan Lu and Haryadi S. Gunawi. "TaxDC: A Taxonomy of Non-Deterministic Concurrency Bugs
in Datacenter Distributed Systems". 2016.
<https://ucare.cs.uchicago.edu/pdf/asplos16-TaxDC.pdf>.
CWE-1231: Improper Prevention of Lock Bit Modification
Weakness ID: 1231
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses a trusted lock bit for restricting access to registers, address regions, or other resources, but the product does not prevent the value of the lock bit from being modified after it has been set.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory
Scope: Access ControlLikelihood: High
Design or coding errors in
the implementation of the lock bit protection feature
may allow the lock bit to be modified or cleared by
software after it has been set. Attackers might be able to unlock the system and
features that the bit is intended to protect. Registers protected by tje lock bit can be modified even when the lock is set.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Security lock bit protections must be reviewed for design inconsistency and common weaknesses.
Security lock programming flow and lock properties must be tested in pre-silicon and post-silicon testing.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
In integrated circuits and hardware
intellectual property (IP) cores, device configuration
controls are commonly programmed after a device power
reset by a trusted firmware or software module (e.g.,
BIOS/bootloader) and then locked from any further
modification. This behavior is commonly implemented using a trusted
lock bit. When set, the lock bit disables writes to a protected set of
registers or address regions.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the example design below for a digital thermal sensor that detects overheating of the silicon and triggers system shutdown. The system critical temperature limit (CRITICAL_TEMP_LIMIT) and thermal sensor calibration (TEMP_SENSOR_CALIB) data have to be programmed by firmware, and then the register needs to be locked (TEMP_SENSOR_LOCK).
In this example, note that if the system heats to critical temperature, the response of the system is controlled by the TEMP_HW_SHUTDOWN bit [1], which is not lockable. Thus, the intended security property of the critical temperature sensor cannot be fully protected, since software can misconfigure the TEMP_HW_SHUTDOWN register even after the lock bit is set to disable the shutdown response.
(good code)
Example Language: Other
To fix this weakness, one could change the TEMP_HW_SHUTDOWN field to be locked by TEMP_SENSOR_LOCK.
TEMP_HW_SHUTDOWN
[31:2] Reserved field; Read only; Default 0 [1] Enable hardware shutdown on critical temperature detection; Read-write-Lock; Default 0 [0] Locked by TEMP_SENSOR_LOCK
Example 2
The following example code is a snippet from the register locks inside the buggy OpenPiton SoC of HACK@DAC'21 [REF-1350]. Register locks help prevent SoC peripherals' registers from malicious use of resources. The registers that can potentially leak secret data are locked by register locks.
In the vulnerable code, the reglk_mem is used for locking information. If one of its bits toggle to 1, the corresponding peripheral's registers will be locked. In the context of the HACK@DAC System-on-Chip (SoC), it is pertinent to note the existence of two distinct categories of reset signals.
First, there is a global reset signal denoted as "rst_ni," which possesses the capability to simultaneously reset all peripherals to their respective initial states.
Second, we have peripheral-specific reset signals, such as "rst_9," which exclusively reset individual peripherals back to their initial states. The administration of these reset signals is the responsibility of the reset controller module.
(bad code)
Example Language: SystemVerilog
always @(posedge clk_i)
begin
if(~(rst_ni && ~jtag_unlock && ~rst_9))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'h0;
end
end ...
In the buggy SoC architecture during HACK@DAC'21, a critical issue arises within the reset controller module. Specifically, the reset controller can inadvertently transmit a peripheral reset signal to the register lock within the user privilege domain.
This unintentional action can result in the reset of the register locks, potentially exposing private data from all other peripherals, rendering them accessible and readable.
To mitigate the issue, remove the extra reset signal rst_9 from the register lock if condition. [REF-1351]
(good code)
Example Language: SystemVerilog
always @(posedge clk_i)
begin
if(~(rst_ni && ~jtag_unlock))
begin
for (j=0; j < 6; j=j+1) begin
reglk_mem[j] <= 'h0;
end
end ...
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
chip reset clears critical read/write lock permissions for RSA function
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Set the lock bit. Power cycle the
device. Attempt to clear the lock bit. If the
information is changed, implement a design
fix. Retest. Also, attempt to indirectly clear the lock
bit or bypass it.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1319: Improper Protection against Electromagnetic Fault Injection (EM-FI)
Weakness ID: 1319
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device is susceptible to electromagnetic fault injection attacks, causing device internal information to be compromised or security mechanisms to be bypassed.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Protection
Behavior-Property
Improper
Attack
Electromagnetic Fault Injection
Acronym
(EM-FI)
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands
Electromagnetic fault injection may allow an attacker to locally and dynamically modify the signals (both internal and external) of an integrated circuit. EM-FI attacks consist of producing a local, transient magnetic field near the device, inducing current in the device wires. A typical EMFI setup is made up of a pulse injection circuit that generates a high current transient in an EMI coil, producing an abrupt magnetic pulse which couples to the target producing faults in the device, which can lead to:
Bypassing security mechanisms such as secure JTAG or Secure Boot
Leaking device information
Modifying program flow
Perturbing secure hardware modules (e.g. random number generators)
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
1. Redundancy - By replicating critical operations and comparing the two outputs can help indicate whether a fault has been injected.
2. Error detection and correction codes - Gay, Mael, et al. proposed a new scheme that not only detects faults injected by a malicious adversary but also automatically corrects single nibble/byte errors introduced by low-multiplicity faults.
3. Fail by default coding - When checking conditions (switch or if) check all possible cases and fail by default because the default case in a switch (or the else part of a cascaded if-else-if construct) is used for dealing with the last possible (and valid) value without checking. This is prone to fault injection because this alternative is easily selected as a result of potential data manipulation [REF-1141].
4. Random Behavior - adding random delays before critical operations, so that timing is not predictable.
5. Program Flow Integrity Protection - The program flow can be secured by integrating run-time checking aiming at detecting control flow inconsistencies. One such example is tagging the source code to indicate the points not to be bypassed [REF-1147].
6. Sensors - Usage of sensors can detect variations in voltage and current.
7. Shields - physical barriers to protect the chips from malicious manipulation.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Power Management Hardware
(Undetermined Prevalence)
Processor Hardware
(Undetermined Prevalence)
Test/Debug Hardware
(Undetermined Prevalence)
Sensor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
In many devices, security related information is stored in fuses. These fuses are loaded into shadow registers at boot time. Disturbing this transfer phase with EM-FI can lead to the shadow registers storing erroneous values potentially resulting in reduced security.
Colin O'Flynn has demonstrated an attack scenario [REF-1144] that uses electro-magnetic glitching during booting to bypass security and gain read access to flash, read and erase access to shadow memory area (where the private password is stored). Most devices in the MPC55xx and MPC56xx series that include the Boot Assist Module (BAM) (a serial or CAN bootloader mode) are susceptible to this attack. In this paper, a GM ECU was used as a real life target. While the success rate appears low (less than 2 percent), in practice a success can be found within 1-5 minutes once the EMFI tool is setup. In a practical scenario, the author showed that success can be achieved within 30-60 minutes from a cold start.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: microcontroller system-on-chip uses a register value stored in flash to set product protection state on the memory bus, but it does not contain protection against fault injection (CWE-1319), which leads to an incorrect initialization of the memory bus (CWE-1419), leading the product to be in an unprotected state.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is attack-oriented and may require significant modification in future versions, or even deprecation. It is not clear whether there is really a design "mistake" that enables such attacks, so this is not necessarily a weakness and may be more appropriate for CAPEC.
A. Dehbaoui, J. M. Dutertre, B. Robisson, P. Orsatelli, P. Maurine, A. Tria. "Injection of transient faults using electromagnetic pulses. Practical results on a cryptographic system". 2012.
<https://eprint.iacr.org/2012/123.pdf>.
CWE-1247: Improper Protection Against Voltage and Clock Glitches
Weakness ID: 1247
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device does not contain or contains incorrectly implemented circuitry or sensors to detect and mitigate voltage and clock glitches and protect sensitive information or software contained on the device.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Bypass Protection Mechanism; Read Memory; Modify Memory; Execute Unauthorized Code or Commands
Scope: Confidentiality, Integrity, Availability, Access Control
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
A device needs to guard against fault attacks such as voltage glitches and clock glitches that an attacker may employ in an attempt to compromise the system. At the circuit-level, using Tunable Replica Circuits (TRCs) or special flip-flops such as Razor flip-flops helps mitigate glitch attacks. Working at the SoC or platform base, level sensors may be implemented to detect glitches. Implementing redundancy in security-sensitive code (e.g., where checks are performed)also can help with mitigation of glitch attacks.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Handling of Faults that Lead to Instruction Skips
Background Details
A device might support features such as secure boot, which are supplemented with hardware and firmware support. This involves establishing a chain of trust, starting with an immutable root of trust by checking the signature of the next stage (culminating with the OS and runtime software) against a golden value before transferring control. The intermediate stages typically set up the system in a secure state by configuring several access control settings. Similarly, security logic for exercising a debug or testing interface may be implemented in hardware, firmware, or both.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Operation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: ICS/OT
(Undetermined Prevalence)
Class: System on Chip
(Undetermined Prevalence)
Power Management Hardware
(Undetermined Prevalence)
Clock/Counter Hardware
(Undetermined Prevalence)
Sensor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Below is a representative snippet of C code that is part of the secure-boot flow. A signature of the runtime-firmware image is calculated and compared against a golden value. If the signatures match, the bootloader loads runtime firmware. If there is no match, an error halt occurs. If the underlying hardware executing this code does not contain any circuitry or sensors to detect voltage or clock glitches, an attacker might launch a fault-injection attack right when the signature check is happening (at the location marked with the comment), causing a bypass of the signature-checking process.
(bad code)
Example Language: C
...
if (signature_matches) // <-Glitch Here
{
load_runtime_firmware();
}
else
{
do_not_load_runtime_firmware();
}
...
After bypassing secure boot, an attacker can gain access to system assets to which the attacker should not have access.
(good code)
Example Language: Other
If the underlying hardware detects a voltage or clock glitch, the information can be used to prevent the glitch from being successful.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
IP communication firmware allows access to a boot shell via certain impulses
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Put the processor in an infinite
loop, which is then followed by instructions
that should not ever be executed, since the
loop is not expected to exit. After the loop,
toggle an I/O bit (for oscilloscope monitoring
purposes), print a console message, and
reenter the loop. Note that to ensure that
the loop exit is actually captured, many NOP
instructions should be coded after the loop
branch instruction and before the I/O bit
toggle and the print statement.
Margining the clock consists of varying the clock
frequency until an anomaly occurs. This could be a
continuous frequency change or it could be a single
cycle. The single cycle method is described here. For
every 1000th clock pulse, the clock cycle is shortened by
10 percent. If no effect is observed, the width is
shortened by 20%. This process is continued in 10%
increments up to and including 50%. Note that the cycle
time may be increased as well, down to seconds per
cycle.
Separately, the voltage is margined. Note that
the voltage could be increased or decreased. Increasing
the voltage has limits, as the circuitry may not be able
to withstand a drastically increased voltage. This process
starts with a 5% reduction of the DC supply to the CPU
chip for 5 milliseconds repeated at 1KHz. If this has no
effect, the process is repeated, but a 10% reduction is
used. This process is repeated at 10% increments down to a
50% reduction. If no effects are observed at 5
millisecond, the whole process is repeated using a 10
millisecond pulse. If no effects are observed, the process
is repeated in 10 millisecond increments out to 100
millisecond pulses.
While these are suggested starting points for
testing circuitry for weaknesses, the limits may need to
be pushed further at the risk of device damage. See
[REF-1217] for descriptions of Smart Card attacks against
a clock (section 14.6.2) and using a voltage glitch
(section 15.5.3).
Effectiveness: Moderate
Dynamic Analysis with Manual Results Interpretation
During the implementation phase where actual hardware is available, specialized hardware tools and apparatus such as ChipWhisperer may be used to check if the platform is indeed susceptible to voltage and clock glitching attacks.
Architecture or Design Review
Review if the protections against glitching merely transfer the attack target. For example, suppose a critical authentication routine that an attacker would want to bypass is given the protection of modifying certain artifacts from within that specific routine (so that if the routine is bypassed, one can examine the artifacts and figure out that an attack must have happened). However, if the attacker has the ability to bypass the critical authentication routine, they might also have the ability to bypass the other protection routine that checks the artifacts. Basically, depending on these kinds of protections is akin to resorting to "Security by Obscurity".
Architecture or Design Review
Many SoCs come equipped with a built-in Dynamic Voltage and Frequency Scaling (DVFS) that can control the voltage and clocks via software alone. However, there have been demonstrated attacks (like Plundervolt and CLKSCREW) that target this DVFS [REF-1081] [REF-1082]. During the design and implementation phases, one needs to check if the interface to this power management feature is available from unprivileged SW (CWE-1256), which would make the attack very easy.
Functional Areas
Power
Clock
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Improper Check or Handling of Exceptional Conditions
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Keith Bowman, James Tschanz, Chris Wilkerson, Shih-Lien Lu, Tanay Karnik, Vivek De and Shekhar Borkar. "Circuit Techniques for Dynamic Variation Tolerance". <https://dl.acm.org/doi/10.1145/1629911.1629915>.
(URL validated: 2023-04-07)
[REF-1062]
Dan Ernst, Nam Sung Kim, Shidhartha Das, Sanjay Pant, Rajeev Rao, Toan Pham, Conrad Ziesler, David Blaauw, Todd Austin, Krisztian Flautner and Trevor Mudge. "Razor: A Low-Power Pipeline Based on Circuit-Level Timing Speculation". <https://web.eecs.umich.edu/~taustin/papers/MICRO36-Razor.pdf>.
[REF-1063]
James Tschanz, Keith Bowman, Steve Walstra, Marty Agostinelli, Tanay Karnik and Vivek De. "Tunable Replica Circuits and Adaptive Voltage-Frequency Techniques for Dynamic Voltage, Temperature, and Aging Variation Tolerance". <https://ieeexplore.ieee.org/document/5205410>.
[REF-1064]
Bilgiday Yuce, Nahid F. Ghalaty, Chinmay Deshpande, Conor Patrick, Leyla Nazhandali and Patrick Schaumont. "FAME: Fault-attack Aware Microprocessor Extensions for Hardware Fault Detection and Software Fault Response". <https://dl.acm.org/doi/10.1145/2948618.2948626>.
(URL validated: 2023-04-07)
[REF-1065]
Keith A. Bowman, James W. Tschanz, Shih-Lien L. Lu, Paolo A. Aseron, Muhammad M. Khellah, Arijit Raychowdhury, Bibiche M. Geuskens, Carlos Tokunaga, Chris B. Wilkerson, Tanay Karnik and Vivek De. "A 45 nm Resilient Microprocessor Core for Dynamic Variation Tolerance". <https://ieeexplore.ieee.org/document/5654663>.
CWE-1320: Improper Protection for Outbound Error Messages and Alert Signals
Weakness ID: 1320
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Untrusted agents can disable alerts about signal conditions exceeding limits or the response mechanism that handles such alerts.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Instability; DoS: Crash, Exit, or Restart; Reduce Reliability; Unexpected State
Scope: AvailabilityLikelihood: High
Warning signals that are not properly secured may be disabled or used to generate spurious alerts, causing degraded performance or denial-of-service (DoS).
These alerts may be masked by untrusted software. Examples of these alerts involve thermal and power sensor alerts.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Alert signals generated by critical events should be protected from access by untrusted agents. Only hardware or trusted firmware modules should be able to alter the alert configuration.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Hardware sensors are used to detect whether a device is operating within design limits. The threshold values for these limits are set by hardware fuses or trusted software such as a BIOS.
Modification of these limits may be protected by hardware mechanisms.
When device sensors detect out of bound conditions, alert signals may be generated for remedial action, which may take the form of device shutdown or throttling.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Power Management Hardware
(Undetermined Prevalence)
Processor Hardware
(Undetermined Prevalence)
Test/Debug Hardware
(Undetermined Prevalence)
Sensor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a platform design where a Digital-Thermal Sensor (DTS) is used to monitor temperature and compare that output against a threshold value.
If the temperature output equals or exceeds the threshold value, the DTS unit sends an alert signal to the processor.
The processor, upon getting the alert, input triggers system shutdown. The alert signal is handled as a General-Purpose-I/O (GPIO) pin in input mode.
(bad code)
Example Language: Other
The processor-GPIO controller exposes software-programmable controls that allow untrusted software to reprogram the state of the GPIO pin.
Reprogramming the state of the GPIO pin allows malicious software to trigger spurious alerts or to set the alert pin to a zero value so that thermal sensor alerts are not received by the processor.
(good code)
Example Language: Other
The GPIO alert-signal pin is blocked from untrusted software access and is controlled only by trusted software, such as the System BIOS.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses Addressed by the Top 20 Secure PLC Coding Practices
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Taxonomy
Mappings
Mapped Taxonomy Name
Node ID
Fit
Mapped Node Name
PLC Top 20
8
Validate HMI input variables at the PLC level, not only at HMI
CWE-1300: Improper Protection of Physical Side Channels
Weakness ID: 1300
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device does not contain sufficient protection
mechanisms to prevent physical side channels from exposing
sensitive information due to patterns in physically observable
phenomena such as variations in power consumption,
electromagnetic emissions (EME), or acoustic emissions.
Extended Description
Physical side channels have been well-studied for
decades in the context of breaking implementations of
cryptographic algorithms or other attacks against security
features. These side channels may be easily observed by an
adversary with physical access to the device, or using a
tool that is in close proximity. If the adversary can
monitor hardware operation and correlate its data processing
with power, EME, and acoustic measurements, the adversary
might be able to recover of secret keys and data.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data
Scope: Confidentiality
An adversary could monitor and measure physical
phenomena to detect patterns and make inferences, even if it
is not possible to extract the information in the digital
domain.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Apply blinding or masking techniques to implementations of cryptographic algorithms.
Implementation
Add shielding or tamper-resistant protections to the device to increase the difficulty of obtaining measurements of the side-channel.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a device that checks a
passcode to unlock the screen.
(bad code)
Example Language: Algorithm
As each character of
the PIN number is entered, a correct character
exhibits one current pulse shape while an
incorrect character exhibits a different current
pulse shape.
PIN numbers used to unlock a cell phone
should not exhibit any characteristics about
themselves. This creates a side channel. An
attacker could monitor the pulses using an
oscilloscope or other method. Once the first
character is correctly guessed (based on the
oscilloscope readings), they can then move to the
next character, which is much more efficient than
the brute force method of guessing every possible
sequence of characters.
(good code)
Example Language: Algorithm
Rather than comparing
each character to the correct PIN value as it is
entered, the device could accumulate the PIN in a
register, and do the comparison all at once at the
end. Alternatively, the components for the
comparison could be modified so that the current
pulse shape is the same regardless of the
correctness of the entered
character.
Example 2
Consider the device vulnerability CVE-2021-3011, which affects certain microcontrollers [REF-1221]. The Google Titan Security Key is used for two-factor authentication using cryptographic algorithms. The device uses an internal secret key for this purpose and exchanges information based on this key for the authentication. If this internal secret key and the encryption algorithm were known to an adversary, the key function could be duplicated, allowing the adversary to masquerade as the legitimate user.
(bad code)
Example Language: Other
The local method of extracting the secret key consists of plugging the key into a USB port and using electromagnetic (EM) sniffing tools and computers.
(good code)
Example Language: Other
Several solutions could have been considered by the manufacturer. For example, the manufacturer could shield the circuitry in the key or add randomized delays, indirect calculations with random values involved, or randomly ordered calculations to make extraction much more difficult. The manufacturer could use a combination of these techniques.
Example 3
The code snippet provided here is part of the modular exponentiation module found in the HACK@DAC'21 Openpiton System-on-Chip (SoC), specifically within the RSA peripheral [REF-1368]. Modular exponentiation, denoted as "a^b mod n," is a crucial operation in the RSA public/private key encryption. In RSA encryption, where 'c' represents ciphertext, 'm' stands for a message, and 'd' corresponds to the private key, the decryption process is carried out using this modular exponentiation as follows: m = c^d mod n, where 'n' is the result of multiplying two large prime numbers.
(bad code)
Example Language: SystemVerilog
...
module mod_exp
...
`UPDATE: begin
if (exponent_reg != 'd0) begin
if (exponent_reg[0])
result_reg <= result_next;
base_reg <= base_next;
exponent_reg <= exponent_next;
state <= `UPDATE;
...
endmodule
The vulnerable code shows a buggy implementation of binary exponentiation where it updates the result register (result_reg) only when the corresponding exponent bit (exponent_reg[0]) is set to 1. However, when this exponent bit is 0, the output register is not updated. It's important to note that this implementation introduces a physical power side-channel vulnerability within the RSA core. This vulnerability could expose the private exponent to a determined physical attacker. Such exposure of the private exponent could lead to a complete compromise of the private key.
To address mitigation requirements, the developer can develop the module by minimizing dependency on conditions, particularly those reliant on secret keys. In situations where branching is unavoidable, developers can implement masking mechanisms to obfuscate the power consumption patterns exhibited by the module (see good code example). Additionally, certain algorithms, such as the Karatsuba algorithm, can be implemented as illustrative examples of side-channel resistant algorithms, as they necessitate only a limited number of branch conditions [REF-1369].
(good code)
Example Language: SystemVerilog
...
module mod_exp
...
`UPDATE: begin
if (exponent_reg != 'd0) begin
if (exponent_reg[0]) begin
result_reg <= result_next;
end else begin
mask_reg <= result_next;
end
base_reg <= base_next;
exponent_reg <= exponent_next;
state <= `UPDATE;
...
endmodule
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Crypto hardware wallet's power consumption relates to total number of pixels illuminated, creating a side channel in the USB connection that allows attackers to determine secrets displayed such as PIN numbers and passwords
Chain: microcontroller system-on-chip uses a register value stored in flash to set product protection state on the memory bus, but it does not contain protection against fault injection (CWE-1319), which leads to an incorrect initialization of the memory bus (CWE-1419), leading the product to be in an unprotected state.
message encryption software uses certain instruction sequences that allow RSA key extraction using a chosen-ciphertext attack and acoustic cryptanalysis
power consumption varies based on number of pixels being illuminated in a display, allowing reading of secrets such as the PIN by using the USB interface to measure power consumption
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Perform a set of leakage detection tests such as the procedure outlined in the Test Vector Leakage Assessment (TVLA) test requirements for AES [REF-1230]. TVLA is the basis for the ISO standard 17825 [REF-1229]. A separate methodology is provided by [REF-1228]. Note that sole reliance on this method might not yield expected results [REF-1239] [REF-1240].
Effectiveness: Moderate
Manual Analysis
Post-silicon, perform full side-channel attacks (penetration testing) covering as many known leakage models as possible against test code.
Effectiveness: Moderate
Manual Analysis
Pre-silicon - while the aforementioned TVLA methods can be performed post-silicon, models of device power consumption or other physical emanations can be built from information present at various stages of the hardware design process before fabrication. TVLA or known side-channel attacks can be applied to these simulated traces and countermeasures applied before tape-out. Academic research in this field includes [REF-1231] [REF-1232] [REF-1233].
Effectiveness: Moderate
Functional Areas
Power
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Comprehensive Categorization: Sensitive Information Exposure
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
ISO/IEC. "ISO/IEC 17825:2016: Testing methods for the mitigation of non-invasive attack classes against cryptographic modules". 2016.
<https://www.iso.org/standard/60612.html>.
Danilo Šijaˇci´, Josep Balasch, Bohan Yang, Santosh Ghosh and Ingrid Verbauwhede. "Towards efficient and automated side-channel evaluations at design time". pp. 305-319. Journal of Cryptographic Engineering, 10(4). 2020.
<https://www.esat.kuleuven.be/cosic/publications/article-3204.pdf>.
[REF-1232]
Amit Kumar, Cody Scarborough, Ali Yilmaz and Michael Orshansky. "Efficient simulation of EM side-channel attack resilience". pp. 123-130. IEEE/ACM International Conference on Computer-Aided Design (ICCAD). 2017.
<https://dl.acm.org/doi/pdf/10.5555/3199700.3199717>.
(URL validated: 2025-07-29)
[REF-1233]
Yuan Yao, Tuna Tufan, Tarun Kathuria, Baris Ege, Ulkuhan Guler and Patrick Schaumont. "Pre-silicon Architecture Correlation Analysis (PACA): Identifying and Mitigating the Source of Side-channel Leakage at Gate-level". IACR Cryptology ePrint Archive. 2021-04-21.
<https://eprint.iacr.org/2021/530.pdf>.
François-Xavier Standaert. "How (not) to Use Welch's T-test in Side-Channel Security Evaluations". IACR Cryptology ePrint Archive. 2017-02-15.
<https://eprint.iacr.org/2017/138.pdf>.
[REF-1240]
Carolyn Whitnall and Elisabeth Oswald. "A Critical Analysis of ISO 17825 ('Testing methods for the mitigation of non-invasive attack classes against cryptographic modules')". IACR Cryptology ePrint Archive. 2019-09-10.
<https://eprint.iacr.org/2019/1013.pdf>.
CWE-1338: Improper Protections Against Hardware Overheating
Weakness ID: 1338
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A hardware device is missing or has inadequate protection features to prevent overheating.
Extended Description
Hardware, electrical circuits, and semiconductor silicon have thermal side effects, such that some of the energy consumed by the device gets dissipated as heat and increases the temperature of the device. For example, in semiconductors, higher-operating frequency of silicon results in higher power dissipation and heat. The leakage current in CMOS circuits increases with temperature, and this creates positive feedback that can result in thermal runaway and damage the device permanently.
Any device lacking protections such as thermal sensors, adequate platform cooling, or thermal insulation is susceptible to attacks by malicious software that might deliberately operate the device in modes that result in overheating. This can be used as an effective denial of service (DoS) or permanent denial of service (PDoS) attack.
Depending on the type of hardware device and its expected usage, such thermal overheating can also cause safety hazards and reliability issues. Note that battery failures can also cause device overheating but the mitigations and examples included in this submission cannot reliably protect against a battery failure.
There can be similar weaknesses with lack of protection from attacks based on overvoltage or overcurrent conditions. However, thermal heat is generated by hardware operation and the device should implement protection from overheating.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Protections
Behavior-Property
Improper
Technology
Hardware
Other
Overheating
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Resource Consumption (Other)
Scope: AvailabilityLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Temperature maximum and minimum limits should be enforced using thermal sensors both in silicon and at the platform level.
Implementation
The platform should support cooling solutions such as fans that can be modulated based on device-operation needs to maintain a stable temperature.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Such issues could be introduced during hardware architecture, design or implementation.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Power Management Hardware
(Undetermined Prevalence)
Processor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Malicious software running on a core can execute instructions that consume maximum power or increase core frequency. Such a power-virus program could execute on the platform for an extended time to overheat the device, resulting in permanent damage.
Execution core and platform do not support thermal sensors, performance throttling, or platform-cooling countermeasures to ensure that any software executing on the system cannot cause overheating past the maximum allowable temperature.
The platform and SoC should have failsafe thermal limits that are enforced by thermal sensors that trigger critical temperature alerts when high temperature is detected. Upon detection of high temperatures, the platform should trigger cooling or shutdown automatically.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Dynamic Analysis with Manual Results Interpretation
Dynamic tests should be performed to stress-test temperature controls.
Effectiveness: High
Architecture or Design Review
Power management controls should be part of Architecture and Design reviews.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1476: Improper Request Propagation before Data Reception in Write Transactions in a Bus Architecture
Weakness ID: 1476
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses a multi-manager shared bus architecture
with an on-chip interconnect that speculatively propagates
a request for a write transaction, but it does not ensure
that the remaining steps required by the manager module to
complete the request are fulfilled in a timely manner.
Technical Nuance
Here, the word "speculatively" refers to the fact that the
interconnect propagates the request assuming that the
manager will at some point provide the data, thus
releasing the use of the bus.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Prevent Access
Scope: AvailabilityLikelihood: High
The technical impact could include
Memory-access delays, I/O access delays, deadline
miss, etc.
The attacker can leverage this weakness to
generate unbounded delays and denial of service (DoS)
in the access of shared resources. The system
interconnect might be left in an inconsistent state,
requiring a partial or full reset of the network,
according to the implementation. The scenario may
play out as follows. The interconnect receives a write
request from a controller initiator (e.g., sending the
header to the interconnect for writing N words of
data, with N ranging from 1 to the maximum burst
length allowed). The interconnect then speculatively
propagates the request to the target peripheral
through the shared bus before the corresponding data
are received at the interconnect. Here, the word
"speculatively" refers to the fact that the
interconnect propagates the request, assuming that the
controller will at some point provide the data, thus
releasing the use of the bus. This speculatively
reserves the bus to the manager transaction issuer,
which is left free to delay its data provisioning
phase. This reserves the whole bus path between the
initiator and the target peripheral until all of the
words associated with the request are provided by the
controller. If the interconnect assumes a cooperative
behavior from the controller, it is implicitly
trusting that the controller will complete the
transaction and release the bus for use from the other
controllers. A malicious, faulty, or misbehaving
manager module can generate a denial-of-service
condition in preventing access to the write data link
from all of the other managers in the system, and
unboundedly inhibit the write access to one or
multiple peripherals in the system (i.e., memories,
I/Os, etc.).
SoC architects can use a switching
methodology stopping stalls from being propagated to
the interconnect, such as Cut-and-Forward
[REF-1585][REF-1587] or
Store-and-Forward. Alternatively, a monitoring and
recovery module can be added between the interconnect
and each manager module to detect stalls introduced by
the module and restore a safe state in the
interconnect after a stall has been detected
[REF-1586].
Effectiveness: High
Note:
The architect should evaluate which
methodology better suits the target platform, trading
off performance and resource consumption impact
[REF-1585][REF-1586][REF-1587].
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Peripherals, On-chip Fabric, and Interface/IO Problems
Background Details
Some products may use an architecture with a
shared bus that is accessible by multiple devices, in
which these devices can issue requests that utilize the
shared bus. There may be an on-chip interconnect based
on a protocol that manages the devices' requests to the
bus and enforces the ordering of requests and data. When
a device makes a request, the bus might indefinitely
lock the write access to a shared output link until the
initiating device finishes its transaction. If the
initiating device does not finish the transaction
quickly enough, this can prevent other devices from
using the bus, causing a denial of service.
A "manager module" is a hardware component that
initiates transactions on the interconnect, such as a
processor, DMA engine, or hardware
accelerator.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Hardware Requirements (Hardware)
This occurs if the on-chip communication
interconnect is based on a multi-channel on-chip
communication standard assuming cooperative behavior
among the manager modules AND an unsafe switching
methodology (e.g., cut-through) is in use. Some
switching methodologies may be susceptible to this
weakness in modern on-chip multi-channel communication
standards, such as the cut-through switching policy, a
switching methodology for high performance commonly
implemented at the interconnect level. In cut-through,
a request is propagated independently on the receipt
at the interconnect level of the corresponding
data. If the manager module issuing a write request
delays the provisioning of the corresponding data, the
other manager modules experience delays in accessing
the bus. Such delays are capable of generating denial
of service.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Architectures
ARM
(Undetermined Prevalence)
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Bus/Interface Hardware
(Undetermined Prevalence)
Communication Hardware
(Undetermined Prevalence)
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
In a system-on-chip, multiple hardware
components may communicate with shared resources
through an interconnect. A manager initiates
transactions, while a target is a shared resource such
as memory or a peripheral. A shared write path is the
portion of the interconnect used by multiple managers
to send write data to the same target.
To reduce buffering requirements and
propagation latency, an interconnect may use
cut-through switching. In protocols where the write
request and corresponding write data are transferred
independently, the interconnect can forward the
request before all of the associated write data have
arrived.
(a) Manager A issues a multi-word write
request.
(b) The interconnect forwards the request
to the shared target before receiving all
corresponding write data. The shared write path is
reserved for Manager A until its data transfer
completes.
(c) Manager A delays or stops sending the
remaining data. The transaction remains incomplete,
and the shared write path remains
reserved.
(d) Manager B attempts to use the same shared path but cannot proceed
until Manager A completes the data transfer or a recovery mechanism
safely releases the path.
In these diagrams, "reserved" refers to the
shared write path serving the target, rather than
every operation or route to that target.
The interconnect reserves the shared
write path before the data required to complete the
transaction are available. In the problematic design
shown here, other managers cannot use that shared write
path until the corresponding data transfer
completes. Thus, the interconnect depends on Manager A
to continue making forward progress. If Manager A
stalls, the stall propagates into the shared portion of
the interconnect and prevents competing transactions
from using that shared write path.
(attack code)
A faulty or malicious manager can delay or
stop providing the remaining write data. If the
interconnect does not enforce bounded progress or
provide a recovery mechanism, the manager can hold the
shared write path indefinitely and cause a denial of
service for competing write transactions that require
the same shared write path.
(good code)
Example Language: Other
The interconnect should avoid reserving the
shared write path until the data needed to complete
the forwarded transaction are available.
One approach is store-and-forward switching the
interconnect buffers the request and all corresponding
write data before forwarding the request, preventing a
manager's input-side stall from propagating into the
shared write path. If Manager A delays or stops sending
data, its incomplete transaction remains in the input
buffer, and the shared write path remains available to
transactions from other managers.
(a) Manager A issues a multi-word write
request.
(b) The interconnect buffers the request
and waits for all corresponding write data. The
request has not been forwarded, and the shared write
path is not yet reserved for Manager A.
(c) After all data have been received and
buffered, the interconnect forwards the request to
the shared target.
(d) The interconnect forwards the buffered
data without waiting for additional data from
Manager A. Completion of the data transfer releases
the shared write path. The target completes the
write and returns a response through the
interconnect to Manager A.
Store-and-forward requires storage for an
entire transaction, increasing buffer capacity and
hardware area. It also adds buffering latency because
forwarding begins only after all corresponding data
have arrived. [REF-1585]
(good code)
Example Language: Other
Cut-and-forward is a second preventive approach. It divides a
transaction into smaller transactions and forwards each only after all
data for that chunk have been buffered. Like store-and-forward, it
prevents a manager's data-provisioning stall from reserving the shared
write path. [REF-1585]
Cut-and-forward applies the same principle at a smaller chunk
granularity. In Figure 3, a four-word write is divided into two
chunks of two words each. The interconnect creates the shorter
transactions and combines their responses, so Manager A continues to
issue and receive a response for the original transaction. [REF-1585]
(a) Manager A issues a four-word write
request.
(b) The interconnect buffers the request
and begins receiving the corresponding write
data. The request has not been forwarded, so the
shared write path is not yet reserved for this
transaction.
(c) After the first two words have been
buffered, the interconnect creates a two-word write
request and forwards it with the complete first
chunk to the shared target. While forwarding this
chunk, the interconnect can receive and buffer the
next two words.
(d) After the remaining two words have
been buffered, the interconnect creates and forwards
a second two-word write transaction with the
complete second chunk.
(e) The shared target completes the two
shorter transactions and returns a separate response
for each one.
(f) The interconnect waits for both
responses, combines them into the single response
expected for the original transaction, and returns
that response to Manager A.
The shared write path is reserved only when a
complete chunk is ready. If Manager A delays data for
a later chunk, the incomplete chunk remains in the
input buffer; the path is not held while waiting for
those data and remains available to other
managers. Smaller chunks reduce buffering requirements
and forwarding delay but increase target-side
transaction and response overhead. Larger chunks
reduce that overhead but require more buffering and
increase the delay before forwarding
begins. [REF-1585]
(good code)
Example Language: Other
A watchdog with protocol-aware recovery is a third,
separate mitigation approach. It limits the duration
of a stall by restoring the shared path to a usable
state. It does not prevent the stall from entering the
shared path: other managers may remain blocked until
detection and recovery complete. Detection alone does
not release the path. [REF-1586]
The behavior illustrated here has been
demonstrated in AXI-based interconnects. The weakness
is not inherently specific to AXI and can arise in
other interconnect protocols with equivalent
request/data separation, ordering,
resource-commitment, and progress properties. The
diagrams omit signal-level details to focus on the
shared write path and transaction
sequence. [REF-1585][REF-1586]
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Certain commercial AXI interconnect IPs
could allow a manager to cause bus stalls.
Detection
Methods
Method
Details
Architecture or Design Review
Instances of this issue can be detected by
manual review of the switching policy implemented in
the interconnect and the deployed on-chip
communication standard.
Effectiveness: Opportunistic
Note:
Manual review requires to have a full
description of the architecture of the
interconnect. This information might not be available
when a third-party interconnect is used.
Formal Verification
Instances of this issue can be found in
manager modules by using property-based verification
specifically targeting the detection of stalls
propagated to the shared resources
[REF-1588].
Effectiveness: High
Simulation / Emulation
Instances of this issue can be found in
simulation by synthetically generating stalls at the
input of the interconnect and evaluating if the
interconnect propagates the stalls at the output or
not.
Effectiveness: Moderate
Note:
Simulations should be capable of triggering
the stalls. Not all of the Verification IP for on-chip
communications might be capable of triggering this
issue.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Insufficient Control Flow Management
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
References
[REF-1585]
Francesco Restuccia and Ryan Kastner. "Cut and Forward: Safe and Secure Communication for FPGA System on Chips". 2022.
<https://ieeexplore.ieee.org/document/9852740>.
(URL validated: 2026-10-22)
Francesco Restuccia, Alessandro Biondi, Mauro Marinoni and Giorgio Buttazzo. "Safely Preventing Unbounded Delays During Bus Transactions in FPGA-based SoC". 2020.
<https://ieeexplore.ieee.org/abstract/document/9114758>.
(URL validated: 2026-10-22)
Thomas Benz, Alessandro Ottaviano, Robert Balas, Angelo Garofalo, Francesco Restuccia, Alessandro Biondi and Luca Benini. "[AXI-REALM: A lightweight and modular interconnect extension for traffic regulation and monitoring of heterogeneous real-time SoCs". 2024.
<https://ieeexplore.ieee.org/document/10546511>.
(URL validated: 2026-10-22)
CWE-1259: Improper Restriction of Security Token Assignment
Weakness ID: 1259
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The System-On-A-Chip (SoC) implements a Security Token mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Tokens are improperly protected, such as improperly restricting the assignment to trusted components.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Files or Directories; Execute Unauthorized Code or Commands; Bypass Protection Mechanism; Gain Privileges or Assume Identity; Modify Memory; Modify Memory; DoS: Crash, Exit, or Restart
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
An improperly protected Security Token may be able to be programmed by a malicious agent (i.e., the Security Token is mutable) to spoof the action as if it originated from a trusted agent.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Since the Security Tokens are integral for the maintenance of security in an SoC, they need to be protected properly.
Security Token assignment review checks for design inconsistency and common weaknesses.
Security-Token definition and programming flow is tested in both pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Comparison Logic is Vulnerable to Power Side-Channel Attacks
Background Details
Systems-On-A-Chip (Integrated circuits and hardware engines) implement Security Tokens to differentiate and identify which actions originated from which agent. These actions may be one of the directives: 'read', 'write', 'program', 'reset', 'fetch', 'compute', etc. Security Tokens are assigned to every agent in the System that is capable of generating an action or receiving an action from another agent. Multiple Security Tokens may be assigned to an agent and may be unique based on the agent's trust level or allowed privileges.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware Class: Not Technology-Specific
(Undetermined Prevalence)
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
For example, consider a system with a register for storing an AES key for encryption and decryption. The key is of 128 bits implemented as a set of four 32-bit registers. The key register assets have an associated control register, AES_KEY_ACCESS_POLICY, which provides the necessary access controls. This access-policy register defines which agents may engage in a transaction, and the type of transaction, with the AES-key registers. Each bit in this 32-bit register defines a security Token. There could be a maximum of 32 security Tokens that are allowed access to the AES-key registers. The number of the bit when set (i.e., "1") allows respective action from an agent whose identity matches the number of the bit and, if "0" (i.e., Clear), disallows the respective action to that corresponding agent.
Let's assume the system has two agents: a Main-controller and an Aux-controller. The respective Security Tokens are "1" and "2".
Register
Description
Default
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption
0x00000000
AES_ENC_DEC_KEY_3
AES key [96:127] for encryption or decryption
0x00000000
AES_KEY_ACCESS_POLICY
AES key access register [31:0]
0x00000002
An agent with Security Token "1" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_3 registers. As per the above access policy, the AES-Key-access policy allows access to the AES-key registers if the security Token is "1".
(bad code)
Example Language: Other
The Aux-controller could program its Security Token to "1" from "2".
The SoC does not properly protect the Security Token of the agents, and, hence, the Aux-controller in the above example can spoof the transaction (i.e., send the transaction as if it is coming from the Main-controller to access the AES-Key registers)
(good code)
Example Language: Other
The SoC needs to protect the Security Tokens. None of the agents in the SoC should have the ability to change the Security Token.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements. Currently it is expressed as a general absence of a protection mechanism as opposed to a specific mistake, and the entry's name and description could be interpreted as applying to software.
CWE-1256: Improper Restriction of Software Interfaces to Hardware Features
Weakness ID: 1256
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product provides software-controllable
device functionality for capabilities such as power and
clock management, but it does not properly limit
functionality that can lead to modification of
hardware memory or register bits, or the ability to
observe physical side channels.
Extended Description
It is frequently assumed that physical attacks
such as fault injection and side-channel analysis
require an attacker to have physical access to the
target device. This assumption may be false if the
device has improperly secured power management features,
or similar features. For mobile devices, minimizing
power consumption is critical, but these devices run a
wide variety of applications with different performance
requirements. Software-controllable mechanisms to
dynamically scale device voltage and frequency and
monitor power consumption are common features in today's
chipsets, but they also enable attackers to mount fault
injection and side-channel attacks without having
physical access to the device.
Fault injection attacks involve strategic
manipulation of bits in a device to achieve a desired
effect such as skipping an authentication step,
elevating privileges, or altering the output of a
cryptographic operation. Manipulation of the device
clock and voltage supply is a well-known technique to
inject faults and is cheap to implement with physical
device access. Poorly protected power management
features allow these attacks to be performed from
software. Other features, such as the ability to write
repeatedly to DRAM at a rapid rate from unprivileged
software, can result in bit flips in other memory
locations (Rowhammer, [REF-1083]).
Side channel analysis requires gathering
measurement traces of physical quantities such as power
consumption. Modern processors often include power
metering capabilities in the hardware itself (e.g.,
Intel RAPL) which if not adequately protected enable
attackers to gather measurements necessary for
performing side-channel attacks from software.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Ensure proper access control mechanisms protect software-controllable features altering physical operating conditions such as clock frequency and voltage.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
An architect may initiate introduction of
this weakness via exacting requirements for
software accessible power/clock management
requirements
Implementation
An implementer may introduce this weakness
by assuming there are no consequences to unbounded
power and clock management for secure components
from untrusted ones.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Memory Hardware
(Undetermined Prevalence)
Power Management Hardware
(Undetermined Prevalence)
Clock/Counter Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example considers the Rowhammer problem [REF-1083]. The Rowhammer issue was caused by a program in a tight loop writing repeatedly to a location to which the program was allowed to write but causing an adjacent memory location value to change.
(bad code)
Example Language: Other
Continuously writing the same value to the same address causes the value of an adjacent location to change value.
Preventing the loop required to defeat the Rowhammer exploit is not always possible:
(good code)
Example Language: Other
Redesign the RAM devices to reduce inter capacitive coupling making the Rowhammer exploit impossible.
While the redesign may be possible for new devices, a redesign is not possible in existing devices. There is also the possibility that reducing capacitance with a relayout would impact the density of the device resulting in a less capable, more costly device.
Example 2
Suppose a hardware design implements a set of software-accessible registers for scaling clock frequency and voltage but does not control access to these registers. Attackers may cause register and memory changes and race conditions by changing the clock or voltage of the device under their control.
Example 3
Consider the following SoC
design. Security-critical settings for scaling clock
frequency and voltage are available in a range of
registers bounded by [PRIV_END_ADDR : PRIV_START_ADDR]
in the tmcu.csr module in the HW Root of Trust. These
values are writable based on the lock_bit register in
the same module. The lock_bit is only writable by
privileged software running on the tmcu.
We assume that untrusted software running on any of the
Core{0-N} processors has access to the input and output
ports of the hrot_iface. If untrusted software can clear
the lock_bit or write the clock frequency and voltage
registers due to inadequate protection, a fault
injection attack could be performed.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Plundervolt: Improper conditions check in voltage settings for some Intel(R) Processors may allow a privileged user to potentially enable escalation of privilege and/or information disclosure via local access [REF-1081].
NaCl in 2015 allowed the CLFLUSH instruction, making Rowhammer attacks possible.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Perform a security evaluation of system-level
architecture and design with software-aided physical attacks
in scope.
Automated Dynamic Analysis
Use custom software to change registers that control clock settings or power settings to try to bypass security locks, or repeatedly write DRAM to try to change adjacent locations. This can be effective in extracting or changing data. The drawback is that it cannot be run before manufacturing, and it may require specialized software.
Effectiveness: Moderate
Functional Areas
Power
Clock
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Yoongu Kim, Ross Daly, Jeremie Kim, Ji Hye Lee, Donghyuk Lee, Chris Wilkerson, Konrad Lai and Onur Mutlu. "Flipping Bits in Memory Without Accessing Them: An Experimental Study of DRAM Disturbance Errors". <https://users.ece.cmu.edu/~yoonguk/papers/kim-isca14.pdf>.
CWE-1224: Improper Restriction of Write-Once Bit Fields
Weakness ID: 1224
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware design control register "sticky bits" or write-once bit fields are improperly implemented, such that they can be reprogrammed by software.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Restriction
Behavior-Property
Improper
Resource-Type
Bit Fields
Resource-Property
Write-Once
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context; Modify Memory
Scope: Confidentiality, Integrity, Availability, Access Control
System configuration cannot be programmed in a secure way. Failure to implement write-once restrictions in hardware design can expose such registers to being re-programmed by software and written multiple times. For example, write-once fields could be implemented to only be write-protected if they have been set to value "1", wherein they would work as "write-1-once" and not "write-once".
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
During hardware design, all register write-once or sticky fields must be evaluated for proper configuration.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Integrated circuits and hardware IP software programmable controls and settings are commonly stored in register circuits. These register contents have to be initialized at hardware reset to define default values that are hard coded in the hardware description language (HDL) code of the hardware unit.
A common security protection mechanism used to protect register settings from modification by software is to make the settings write-once or "sticky." This allows writing to such registers only once, whereupon they become read-only. This is useful to allow initial boot software to configure systems settings to secure values while blocking runtime software from modifying such hardware settings.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Such issues could be introduced during implementation of hardware design, since IP parameters and defaults are defined in HDL code and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the example design module system verilog code shown below. register_write_once_example module is an example of register that has a write-once field defined. Bit 0 field captures the write_once_status value. This implementation can be for a register that is defined by specification to be a write-once register, since the write_once_status field gets written by input data bit 0 on first write.
The above example only locks further writes if write_once_status bit is written to one. So it acts as write_1-Once instead of the write-once attribute.
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Analysis
Use automated tools to test that values are not reprogrammable and that write-once fields lock on writing zeros.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1266: Improper Scrubbing of Sensitive Data from Decommissioned Device
Weakness ID: 1266
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not properly provide a capability for the product administrator to remove sensitive data at the time the product is decommissioned. A scrubbing capability could be missing, insufficient, or incorrect.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data
Scope: Confidentiality
Improper scrubbing of sensitive data from a decommissioned device leaves that data vulnerable to acquisition by a malicious actor. Sensitive data may include, but is not limited to, device/manufacturer proprietary information, user/device credentials, network configurations, and other forms of sensitive data.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Functionality to completely scrub data from a product at the conclusion of its lifecycle should be part of the design phase. Trying to add this function on top of an existing architecture could lead to incomplete removal of sensitive information/data.
Policy
The manufacturer should describe the location(s) where sensitive data is stored and the policies and procedures for its removal. This information may be conveyed, for example, in an Administrators Guide or a Statement of Volatility.
Implementation
If the capability to wipe sensitive data isn't built-in, the manufacturer may need to provide a utility to scrub sensitive data from storage if that data is located in a place which is non-accessible by the administrator. One example of this could be when sensitive data is stored on an EEPROM for which there is no user/admin interface provided by the system.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
When a product is decommissioned - i.e., taken out of service - best practices or regulatory requirements may require the administrator to remove or overwrite sensitive data first, i.e. "scrubbing."
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Policy
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
CWE-1315: Improper Setting of Bus Controlling Capability in Fabric End-point
Weakness ID: 1315
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The bus controller enables bits in the fabric end-point to allow responder devices to control transactions on the fabric.
Extended Description
To support reusability, certain fabric interfaces and end points provide a configurable register bit that allows IP blocks connected to the controller to access other peripherals connected to the fabric. This allows the end point to be used with devices that function as a controller or responder. If this bit is set by default in hardware, or if firmware incorrectly sets it later, a device intended to be a responder on a fabric is now capable of controlling transactions to other devices and might compromise system security.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
For responder devices, the register bit in the fabric end-point that enables the bus controlling capability must be set to 0 by default. This bit should not be set during secure-boot flows. Also, writes to this register must be access-protected to prevent malicious modifications to obtain bus-controlling capability.
Implementation
For responder devices, the register bit in the fabric end-point that enables the bus controlling capability must be set to 0 by default. This bit should not be set during secure-boot flows. Also, writes to this register must be access-protected to prevent malicious modifications to obtain bus-controlling capability.
System Configuration
For responder devices, the register bit in the fabric end-point that enables the bus controlling capability must be set to 0 by default. This bit should not be set during secure-boot flows. Also, writes to this register must be access-protected to prevent malicious modifications to obtain bus-controlling capability.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Peripherals, On-chip Fabric, and Interface/IO Problems
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
System Configuration
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A typical, phone platform consists of the main, compute core or CPU, a DRAM-memory chip, an audio codec, a baseband modem, a power-management-integrated circuit ("PMIC"), a connectivity (WiFi and Bluetooth) modem, and several other analog/RF components. The main CPU is the only component that can control transactions, and all the other components are responder-only devices. All the components implement a PCIe end-point to interface with the rest of the platform. The responder devices should have the bus-control-enable bit in the PCIe-end-point register set to 0 in hardware to prevent the devices from controlling transactions to the CPU or other peripherals.
The audio-codec chip does not have the bus-controller-enable-register bit hardcoded to 0. There is no platform-firmware flow to verify that the bus-controller-enable bit is set to 0 in all responders.
Audio codec can now master transactions to the CPU and other platform components. Potentially, it can modify assets in other platform components to subvert system security.
Platform firmware includes a flow to check the configuration of bus-controller-enable bit in all responder devices. If this register bit is set on any of the responders, platform firmware sets it to 0. Ideally, the default value of this register bit should be hardcoded to 0 in RTL. It should also have access control to prevent untrusted entities from setting this bit to become bus controllers.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1311: Improper Translation of Security Attributes by Fabric Bridge
Weakness ID: 1311
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The fabric bridge incorrectly translates security attributes from either trusted to untrusted or from untrusted to trusted when converting from one fabric protocol to another.
Extended Description
A weakness can arise if the bridge IP block, which translates the signals from the protocol used in the IP block endpoint to the protocol used by the central bus, does not properly translate the security attributes.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands
Scope: Confidentiality, Integrity, Access Control
The identity of the initiator could be translated from untrusted to trusted or vice-versa. This could result in access-control bypass, privilege escalation, or denial of service.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The translation must map signals in such a way that untrusted agents cannot map to trusted agents or vice-versa.
Implementation
Ensure that the translation maps signals in such a way that untrusted agents cannot map to trusted agents or vice-versa.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Peripherals, On-chip Fabric, and Interface/IO Problems
Background Details
A bridge allows IP blocks supporting different fabric protocols to be integrated into the system. Fabric end-points or interfaces usually have dedicated signals to transport security attributes, such as HPROT signals in AHB, AxPROT signals in AXI, and MReqInfo and SRespInfo signals in OCP.
The values on these signals are used to indicate the security attributes of the transaction. These include the immutable hardware identity of the controller initiating the transaction, privilege level, and type of transaction (e.g., read/write, cacheable/non-cacheable, posted/non-posted).
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The bridge interfaces between OCP and AHB end points. OCP uses MReqInfo signal to indicate security attributes, whereas AHB uses HPROT signal to indicate the security attributes. The width of MReqInfo can be customized as needed. In this example, MReqInfo is 5-bits wide and carries the privilege level of the OCP controller.
The values 5'h11, 5'h10, 5'h0F, 5'h0D, 5'h0C, 5'h0B, 5'h09, 5'h08, 5'h04, and 5'h02 in MReqInfo indicate that the request is coming from a privileged state of the OCP bus controller. Values 5'h1F, 5'h0E, and 5'h00 indicate untrusted, privilege state.
Though HPROT is a 5-bit signal, we only consider the lower, two bits in this example. HPROT values 2'b00 and 2'b10 are considered trusted, and 2'b01 and 2'b11 are considered untrusted.
The OCP2AHB bridge is expected to translate trusted identities on the controller side to trusted identities on the responder side. Similarly, it is expected to translate untrusted identities on the controller side to untrusted identities on the responder side.
(bad code)
Example Language: Verilog
module ocp2ahb
(
ahb_hprot,
ocp_mreqinfo
);
output [1:0] ahb_hprot; // output is 2 bit signal for AHB HPROT
input [4:0] ocp_mreqinfo; // input is 5 bit signal from OCP MReqInfo
wire [6:0] p0_mreqinfo_o_temp; // OCP signal that transmits hardware identity of bus controller
wire y;
reg [1:0] ahb_hprot;
// hardware identity of bus controller is in bits 5:1 of p0_mreqinfo_o_temp signal
assign p0_mreqinfo_o_temp[6:0] = {1'b0, ocp_mreqinfo[4:0], y};
Logic in the case statement only checks for MReqInfo bits 4:2, i.e., hardware-identity bits 3:1. When ocp_mreqinfo is 5'h1F or 5'h0E, p0_mreqinfo_o_temp[2] will be 1. As a result, untrusted IDs from OCP 5'h1F and 5'h0E get translated to trusted ahb_hprot values 2'b00.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1246: Improper Write Handling in Limited-write Non-Volatile Memories
Weakness ID: 1246
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not implement or incorrectly implements wear leveling operations in limited-write non-volatile memories.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Instability
Scope: Availability
If wear leveling is improperly implemented, attackers may be able to programmatically cause the storage to become unreliable within a much shorter time than would normally be expected.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Include secure wear leveling algorithms and ensure they may not be bypassed.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Non-volatile memories such as NAND Flash, EEPROM, etc. have individually erasable segments, each of which can be put through a limited number of program/erase or write cycles. For example, the device can only endure a limited number of writes, after which the device becomes unreliable. In order to wear out the cells in a uniform manner, non-volatile memory and storage products based on the above-mentioned technologies implement a technique called wear leveling. Once a set threshold is reached, wear leveling maps writes of a logical block to a different physical block. This prevents a single physical block from prematurely failing due to a high concentration of writes.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Memory Hardware
(Undetermined Prevalence)
Storage Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
An attacker can render a memory line unusable by repeatedly causing a write to the memory line.
Below is example code from [REF-1058] that the user can execute repeatedly to cause line failure. W is the maximum associativity of any cache in the system; S is the size of the largest cache in the system.
(attack code)
Example Language: C++
// Do aligned alloc of (W+1) arrays each of size S
while(1) {
for (ii = 0; ii < W + 1; ii++)
array[ii].element[0]++;
}
Without wear leveling, the above attack will be successful. Simple randomization of blocks will not suffice as instead of the original physical block, the randomized physical block will be worn out.
(good code)
Example Language: Other
Wear leveling must be used to even out writes to the device.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1239: Improper Zeroization of Hardware Register
Weakness ID: 1239
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
VariantVariant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The hardware product does not properly clear sensitive information from built-in registers when the user of the hardware block changes.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Confidentiality
The consequences will depend on the information disclosed due to the vulnerability. When a different entity obtains access to the IP due to a change in operating mode or conditions, the new entity can extract information belonging to the previous user if no mechanisms are in place to clear register contents.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
It is important to clear information stored in the hardware if a physical attack on the product is detected, or if the user of the hardware block changes. Every register potentially containing sensitive information must have a policy specifying how and when information is cleared, in addition to clarifying if it is the responsibility of the hardware logic or IP user to initiate the zeroization procedure at the appropriate time.
Note: Unfortunately, data disclosure can occur even after information has been overwritten/zeroized from the digital perspective. Physical characteristics of the memory can reveal the history of previously written data. For example, if the same value is written repeatedly to a memory location, the corresponding memory cells can become physically altered to a degree that even if the original data is erased it can still be recovered through physical characterization of the memory cells [REF-1055].
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information Uncleared Before Debug/Power State Transition
CanAlsoBe
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Hardware logic operates on data stored in registers local to the hardware block. Most hardware IPs, including cryptographic accelerators, rely on registers to buffer I/O, store intermediate values, and interface with software. The result of this is that sensitive information, such as passwords or encryption keys, can exist in locations that are not transparent to the user of the hardware logic.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Lack of hardware mechanisms to zeroize or clear registers in the design or specification.
Implementation
Mechanisms to zeroize and clear registers are in the design but implemented incorrectly.
Operation
Hardware-provided zeroization mechanisms are not used appropriately by the IP user (ex. firmware), or data remanence issues are not taken into account.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Suppose a hardware IP for implementing an encryption routine works as expected, but it leaves the intermediate results in some registers that can be accessed. Exactly why this access happens is immaterial - it might be unintentional or intentional, where the designer wanted a "quick fix" for something.
Example 2
The example code below [REF-1379] is taken from the SHA256 Interface/wrapper controller module of the HACK@DAC'21 buggy OpenPiton SoC. Within the wrapper module there are a set of 16 memory-mapped registers referenced data[0] to data[15]. These registers are 32 bits in size and are used to store the data received on the AXI Lite interface for hashing. Once both the message to be hashed and a request to start the hash computation are received, the values of these registers will be forwarded to the underlying SHA256 module for processing. Once forwarded, the values in these registers no longer need to be retained. In fact, if not cleared or overwritten, these sensitive values can be read over the AXI Lite interface, potentially compromising any previously confidential data stored therein.
In the previous code snippet [REF-1379] there is the lack of a data clearance mechanism for the memory-mapped I/O registers after their utilization. These registers get cleared only when a reset condition is met. This condition is met when either the global negative-edge reset input signal (rst_ni) or the dedicated reset input signal for SHA256 peripheral (rst_3) is active. In other words, if either of these reset signals is true, the registers will be cleared. However, in cases where there is not a reset condition these registers retain their values until the next hash operation. It is during the time between an old hash operation and a new hash operation that that data is open to unauthorized disclosure.
To correct the issue of data persisting between hash operations, the memory mapped I/O registers need to be cleared once the values written in these registers are propagated to the SHA256 module. This could be done for example by adding a new condition to zeroize the memory mapped I/O registers once the hash value is computed, i.e., hashValid signal asserted, as shown in the good code example below [REF-1380]. This fix will clear the memory-mapped I/O registers after the data has been provided as input to the SHA engine.
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Variant level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Terminology
The process of clearing register contents in a hardware
IP is referred to as zeroization in standards for
cryptographic hardware modules such as FIPS-140-2
[REF-267].
CWE-1304: Improperly Preserved Integrity of Hardware Configuration State During a Power Save/Restore Operation
Weakness ID: 1304
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product performs a power save/restore
operation, but it does not ensure that the integrity of
the configuration state is maintained and/or verified between
the beginning and ending of the operation.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Instability; DoS: Crash, Exit, or Restart; DoS: Resource Consumption (Other); Gain Privileges or Assume Identity; Bypass Protection Mechanism; Alter Execution Logic; Quality Degradation; Unexpected State; Reduce Maintainability; Reduce Performance; Reduce Reliability
Scope: Confidentiality, IntegrityLikelihood: High
During the power-down process,
an attacker with access to the persistent storage may
alter the current state to a configuration that could potentially
modify privileges, disable protections, and/or cause
damage to the hardware. If the IP does not validate
the configuration state stored in persistent memory,
upon regaining power or becoming operational again,
the IP could be compromised through the activation of
an unwanted/harmful configuration.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Inside the IP, incorporate integrity checking
on the configuration state via a cryptographic
hash. The hash can be protected inside the IP such as
by storing it in internal registers which never lose
power. Before powering down, the IP performs a hash of
the configuration and saves it in these persistent
registers. Upon restore, the IP performs a hash of the
saved configuration and compares it with the
saved hash. If they do not match, then the IP should
not trust the configuration.
Integration
Outside the IP, incorporate integrity checking
of the configuration state via a trusted agent. Before
powering down, the trusted agent performs a hash of the
configuration and saves the hash in persistent storage.
Upon restore, the IP requests the trusted agent
validate its current configuration. If the
configuration hash is invalid, then the IP should not
trust the configuration.
Integration
Outside the IP, incorporate a protected
environment that prevents undetected modification of
the configuration state by untrusted agents. Before
powering down, a trusted agent saves the IP's
configuration state in this protected location that
only it is privileged to. Upon restore, the trusted
agent loads the saved state into the IP.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Uninitialized Value on Reset for Registers Holding Security Settings
Background Details
Before powering down, the Intellectual
Property (IP) saves current state (S) to persistent
storage such as flash or always-on memory in order to
optimize the restore operation.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Weakness introduced via missing internal integrity guarantees during power save/restore
Integration
Weakness introduced via missing external integrity verification during power save/restore
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following pseudo code demonstrates the
power save/restore workflow which may lead to weakness
through a lack of validation of the config state after
restore.
The following pseudo-code is the proper workflow for the integrity checking mitigation:
(good code)
Example Language: C
void save_config_state()
{
void* cfg;
void* sha;
cfg = get_config_state();
save_config_state(cfg);
// save hash(cfg) to trusted location
sha = get_hash_of_config_state(cfg);
save_hash(sha);
go_to_sleep();
}
void restore_config_state()
{
void* cfg;
void* sha_1, sha_2;
cfg = get_config_file();
// restore hash of config from trusted memory
sha_1 = get_persisted_sha_value();
sha_2 = get_hash_of_config_state(cfg);
if (sha_1 != sha_2)
assert_error_and_halt();
load_config_file(cfg);
}
It must be noted that in the previous example of
good pseudo code, the memory (where the hash of the
config state is stored) must be trustworthy while the
hardware is between the power save and restore states.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Functional Areas
Power
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1242: Inclusion of Undocumented Features or Chicken Bits
Weakness ID: 1242
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device includes chicken bits or undocumented features that can create entry points for unauthorized actors.
Extended Description
A common design practice is to use undocumented bits on a device that can be used to disable certain functional security features. These bits are commonly referred to as "chicken bits". They can facilitate quick identification and isolation of faulty components, features that negatively affect performance, or features that do not provide the required controllability for debug and test. Another way to achieve this is through implementation of undocumented features.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism
Scope: Confidentiality, Integrity, Availability, Access Control
An attacker might exploit these interfaces for unauthorized access.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
The implementation of chicken bits in a released product is highly discouraged. If implemented at all, ensure that they are disabled in production devices. All interfaces to a device should be documented.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Documentation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a device that comes with various security measures, such as secure boot. The secure-boot process performs firmware-integrity verification at boot time, and this code is stored in a separate SPI-flash device. However, this code contains undocumented "special access features" intended to be used only for performing failure analysis and intended to only be unlocked by the device designer.
(bad code)
Example Language: Other
Attackers dump the code from the device and then perform reverse engineering to analyze the code. The undocumented, special-access features are identified, and attackers can activate them by sending specific commands via UART before secure-boot phase completes. Using these hidden features, attackers can perform reads and writes to memory via the UART interface. At runtime, the attackers can also execute arbitrary code and dump the entire memory contents.
Remove all chicken bits and hidden features that are exposed to attackers. Add authorization schemes that rely on cryptographic primitives to access any features that the manufacturer does not want to expose. Clearly document all interfaces.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1296: Incorrect Chaining or Granularity of Debug Components
Weakness ID: 1296
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product's debug components contain incorrect chaining or granularity of debug components.
Extended Description
Logic errors during design or synthesis could misconfigure the interconnection of the debug components, which could allow unintended access permissions.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands; Modify Memory; Modify Files or Directories
Scope: Confidentiality, Integrity, Access Control, Authentication, Authorization, Availability, AccountabilityLikelihood: Medium
Depending on the access to debug component(s) erroneously granted, an attacker could use the debug component to gain additional understanding about the system to further an attack and/or execute other commands. This could compromise any security property, including the ones listed above.
Potential Mitigations
Phase(s)
Mitigation
Implementation
Ensure that debug components are properly chained and their granularity is maintained at different authentication levels.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
For debugging and troubleshooting a chip, several hardware design elements are often implemented, including:
Various Test Access Ports (TAPs) allow boundary scan commands to be executed.
For scanning the internal components of a chip, there are scan cells that allow the chip to be used as a "stimulus and response" mechanism.
Chipmakers might create custom methods to observe the internal components of their chips by placing various tracing hubs within their chip and creating hierarchical or interconnected structures among those hubs.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Logic errors during design or synthesis could misconfigure the interconnection of the debug components, which could allow unintended access permissions.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following example shows how an attacker can take advantage of incorrect chaining or missing granularity of debug components.
In a System-on-Chip (SoC), the user might be able to access the SoC-level TAP with a certain level of authorization. However, this access should not also grant access to all of the internal TAPs (e.g., Core). Separately, if any of the internal TAPs is also stitched to the TAP chain when it should not be because of a logic error, then an attacker can access the internal TAPs as well and execute commands there.
As a related example, suppose there is a hierarchy of TAPs (TAP_A is connected to TAP_B and TAP_C, then TAP_B is connected to TAP_D and TAP_E, then TAP_C is connected to TAP_F and TAP_G, etc.). Architecture mandates that the user have one set of credentials for just accessing TAP_A, another set of credentials for accessing TAP_B and TAP_C, etc. However, if, during implementation, the designer mistakenly implements a daisy-chained TAP where all the TAPs are connected in a single TAP chain without the hierarchical structure, the correct granularity of debug components is not implemented and the attacker can gain unauthorized access.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Incorrect access control in RDP Level 1 on STMicroelectronics STM32F0 series devices allows physically present attackers to extract the device's protected firmware via a special sequence of Serial Wire Debug (SWD) commands because there is a race condition between full initialization of the SWD interface and the setup of flash protection.
There is an improper authorization vulnerability in several smartphones. The system has a logic-judging error, and, under certain scenarios, a successful exploit could allow the attacker to switch to third desktop after a series of operations in ADB mode. (Vulnerability ID: HWPSIRT-2019-10114).
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Appropriate Post-Si tests should be carried out at various authorization levels to ensure that debug components are properly chained and accessible only to users with appropriate credentials.
Effectiveness: High
Dynamic Analysis with Manual Results Interpretation
Appropriate Post-Si tests should be carried out at various authorization levels to ensure that debug components are properly chained and accessible only to users with appropriate credentials.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product's comparison logic is performed over a series of steps rather than across the entire string in one operation. If there is a comparison logic failure on one of these steps, the operation may be vulnerable to a timing attack that can result in the interception of the process for nefarious purposes.
Extended Description
Comparison logic is used to compare a variety of objects including passwords, Message
Authentication Codes (MACs), and responses to verification challenges. When comparison logic is
implemented at a finer granularity (e.g., byte-by-byte comparison) and breaks in the case of a
comparison failure, an attacker can exploit this implementation to identify when exactly
the failure occurred. With multiple attempts, the attacker may be able to guesses the correct
password/response to challenge and elevate their privileges.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Confidentiality, Authorization
Potential Mitigations
Phase(s)
Mitigation
Implementation
The hardware designer should ensure that comparison logic is implemented so as to compare in one operation instead in smaller chunks.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Password-checking function in router terminates validation of a password entry when it encounters the first incorrect character, which allows remote attackers to obtain passwords via a brute-force attack that relies on timing differences in responses to incorrect password guesses, aka a timing side-channel attack.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Sensitive Information Exposure
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
CWE 4.16 removed a demonstrative example for a hardware module because it was inaccurate and unable to be adapted. The CWE team is developing an alternative.
CWE-1292: Incorrect Conversion of Security Identifiers
Weakness ID: 1292
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product implements a conversion mechanism to map certain bus-transaction signals to security identifiers, but this conversion between protocols is incorrectly implemented.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Quality Degradation
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
An untrusted agent may gain unauthorized access to an asset
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Security identifier decoders must be reviewed for design inconsistency and common weaknesses.
Implementation
Access and programming flows must be tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
In a System-On-Chip (SoC), various integrated circuits and hardware engines generate transactions such as to access (reads/writes) assets or perform certain actions (e.g., reset, fetch, compute, etc.). Among various types of message information, a typical transaction is comprised of source identity (to identify the originator of the transaction) and a destination identity (to route the transaction to the respective entity). Sometimes the transactions are qualified with a security identifier. This security identifier helps the destination agent decide on the set of allowed actions (e.g., access an asset for read and writes).
A typical bus connects several leader and follower agents. Some follower agents implement bus protocols differently from leader agents. A protocol conversion happens at a bridge to seamlessly connect different protocols on the bus. One example is a system that implements a leader with the Advanced High-performance Bus (AHB) protocol and a follower with the Open-Core Protocol (OCP). A bridge AHB-to-OCP is needed to translate the transaction from one form to the other.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design, then identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during hardware implementation, then identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Bus/Interface Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a system that supports AHB. Let us assume we have a follower agent that only understands OCP. To connect this follower to the leader, a bridge is introduced, i.e., AHB to OCP.
The follower has assets to protect accesses from untrusted leaders, and it employs access controls based on policy, (e.g., AES-Key registers for encryption or decryption). The key is 128 bits implemented as a set of four 32-bit registers. The key registers are assets, and register AES_KEY_ACCESS_POLICY is defined to provide the necessary access controls.
The AES_KEY_ACCESS_POLICY access-policy register defines which agents with a security identifier in the transaction can access the AES-key registers. The implemented AES_KEY_ACCESS_POLICY has 4 bits where each bit when "Set" allows access to the AES-Key registers to the corresponding agent that has the security identifier. The other bits from 31 through 4 are reserved and not used.
Register
Field Description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_3
AES key [96:127] for encryption or decryption Default 0x00000000
AES_KEY_ACCESS_POLICY
[31:4] Default 0x000000 [3:0] - 0x02 agent with Security Identifier "1" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_4 registers
During conversion of the AHB-to-OCP transaction, the security identifier information must be preserved and passed on to the follower correctly.
(bad code)
Example Language: Other
In AHB-to-OCP bridge, the security identifier information conversion is done incorrectly.
Because of the incorrect conversion, the security identifier information is either lost or could be modified in such a way that an untrusted leader can access the AES-Key registers.
(good code)
Example Language: Other
The conversion of the signals from one protocol (AHB) to another (OCP) must be done while preserving the security identifier correctly.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1290: Incorrect Decoding of Security Identifiers
Weakness ID: 1290
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product implements a decoding mechanism to decode certain bus-transaction signals to security identifiers, but it decodes an untrusted agent's security identifier into a trusted agent's security identifier.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Decoding
Behavior-Property
Incorrect
Resource-Type
Security Identifiers
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Quality Degradation
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
If the decoding of an untrusted agent's identifier produces the security identifier of a trusted agent, then the untrusted agent can gain unauthorized access to the asset.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Security identifier decoders must be reviewed for design consistency and common weaknesses.
Implementation
Access and programming flows must be tested in pre-silicon and post-silicon testing in order to check for this weakness.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
In a System-On-Chip (SoC), various integrated circuits and hardware engines generate transactions such as to access (reads/writes) assets or perform certain actions (e.g., reset, fetch, compute, etc.). Among various types of message information, a typical transaction is comprised of source identity (to identify the originator of the transaction) and a destination identity (to route the transaction to the respective entity). Sometimes the transactions are qualified with a security identifier. The security identifier helps the destination agent decide on the set of allowed actions (e.g., access an asset for read and writes). A decoder decodes the bus transactions to map security identifiers into necessary access-controls/protections.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Bus/Interface Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a system that has four bus masters and a decoder. The decoder is supposed to decode every bus transaction and assign a corresponding security identifier. The security identifier is used to determine accesses to the assets. The bus transaction that contains the security information is Bus_transaction [15:14], and the bits 15 through 14 contain the security identifier information. The table below provides bus masters as well as their security identifiers and trust assumptions:
Bus Master
Security Identifier Decoding
Trust Assumptions
Master_0
"00"
Untrusted
Master_1
"01"
Trusted
Master_2
"10"
Untrusted
Master_3
"11"
Untrusted
The assets are the AES-Key registers for encryption or decryption. The key is 128 bits implemented as a set of four 32-bit registers. The AES_KEY_ACCESS_POLICY is used to define which agents with a security identifier in the transaction can access the AES-key registers. The size of the security identifier is 4 bits (i.e., bit 3 through 0). Each bit in these 4 bits defines a security identifier. There are only 4 security identifiers that are allowed accesses to the AES-key registers. The number of the bit when set (i.e., "1") allows respective action from an agent whose identity matches the number of the bit. If clear (i.e., "0"), disallows the respective action to that corresponding agent.
Register
Field description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_3
AES key [96:127] for encryption or decryption Default 0x00000000
AES_KEY_ACCESS_POLCY
[31:4] Default 0x00000000 [3:0]-0x01 agent with Security Identified "1" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_3 registers
The following Pseudo code outlines the process of checking the value of the Security Identifier within the AES_KEY_ACCESS_POLICY register:
(informative)
Example Language: Other
If (AES_KEY_ACCESS_POLICY[Security_Identifier] == "1")
Allow access to AES-Key registers
Else
Deny access to AES-Key registers
Below is a decoder's Pseudo code that only checks for bit [14] of the bus transaction to determine what Security Identifier it must assign.
(bad code)
Example Language: Other
If (Bus_transaction[14] == "1")
Security_Identifier == "1"
Else
Security_Identifier == "0"
The security identifier is two bits, but the decoder code above only checks the value of one bit. Two Masters have their bit 0 set to "1" - Master_1 and Master_3. Master_1 is trusted, while Master_3 is not. The code above would therefore allow an untrusted agent, Master_3, access to the AES-Key registers in addition to intended trusted Master_1.
The decoder should check for the entire size of the security identifier in the bus-transaction signal to assign a corresponding security identifier. The following is good Pseudo code:
(good code)
Example Language: Other
If (Bus_transaction[15:14] == "00")
Security_Identifier == "0"
If (Bus_transaction[15:14] == "01")
Security_Identifier == "1"
If (Bus_transaction[15:14] == "10")
Security_Identifier == "2"
If (Bus_transaction[15:14] == "11")
Security_Identifier == "3"
Weakness Ordinalities
Ordinality
Description
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Content
History
Submissions
Submission Date
Submitter
Organization
2020-04-29
(CWE 4.2, 2020-08-20)
Arun Kanuparthi, Hareesh Khattri, Parbati Kumar Manna
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
During installation, installed file permissions are set to allow anyone to modify those files.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data; Modify Application Data
Scope: Confidentiality, Integrity
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Operation
The architecture needs to access and modification attributes for files to only those users who actually require those actions.
Architecture and Design
Strategy: Separation of Privilege
Compartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area.
Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Relevant to the view "Weaknesses for Simplified Mapping of Published Vulnerabilities" (View-1003)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Installation; Operation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Likelihood Of Exploit
Medium
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
SEI CERT Oracle Secure Coding Standard for Java - Guidelines 13. Input Output (FIO)
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
ICS Engineering (Construction/Deployment): Security Gaps in Commissioning
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
OWASP Top Ten 2025 Category A01:2025 - Broken Access Control
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.19, this entry is
being considered for deprecation or significant
revision. Its name and description are inconsistent. The
name is more general, and the description is more
specific. The description emphasizes the installation
phase only; mentions only files; and emphasizes
modification of those files. The name applies to any type
of resource, does not mention the specific permissions,
and could be relevant to any SDLC phase.
Taxonomy
Mappings
Mapped Taxonomy Name
Node ID
Fit
Mapped Node Name
PLOVER
Insecure Default Permissions
CERT C Secure Coding
FIO06-C
Create files with appropriate access permissions
The CERT Oracle Secure Coding Standard for Java (2011)
Mark Dowd, John McDonald and Justin Schuh. "The Art of Software Security Assessment". Chapter 3, "Insecure Defaults", Page 69. 1st Edition. Addison Wesley. 2006.
CWE-1221: Incorrect Register Defaults or Module Parameters
Weakness ID: 1221
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Hardware description language code incorrectly defines register defaults or hardware Intellectual Property (IP) parameters to insecure values.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Confidentiality, Integrity, Availability, Access Control
The system security settings of a hardware design can be affected by incorrectly defined default values or IP parameters. The hardware IP would be in an insecure state at power reset, and this can be exposed or exploited by untrusted software running on the system. Degradation of system functionality or loss of access control enforcement can occur.
Reduce Maintainability
Scope: Other
Both register defaults and parameters are hardcoded values, which cannot be changed using software or firmware patches but must be changed in hardware silicon. Thus, such security issues are considerably more difficult to address later in the lifecycle.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
During hardware design, all the system parameters and register defaults must be reviewed to identify security sensitive settings.
Implementation
The default values of these security sensitive settings need to be defined as part of the design review phase.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Integrated circuits and hardware IP software programmable controls and settings are commonly stored in register circuits. These register contents have to be initialized at hardware reset to defined default values that are hard coded in the hardware description language (HDL) code of the hardware unit. Hardware description languages also support definition of parameter variables, which can be defined in code during instantiation of the hardware IP module. Such parameters are generally used to configure a specific instance of a hardware IP in the design.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Such issues could be introduced during implementation of hardware design, since IP parameters and defaults are defined in HDL code and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider example design module system verilog code shown below. The register_example module is an example parameterized module that defines two parameters, REGISTER_WIDTH and REGISTER_DEFAULT. Register_example module defines a Secure_mode setting, which when set makes the register content read-only and not modifiable by software writes. register_top module instantiates two registers, Insecure_Device_ID_1 and Insecure_Device_ID_2. Generally, registers containing device identifier values are required to be read only to prevent any possibility of software modifying these values.
(bad code)
Example Language: Verilog
// Parameterized Register module example
// Secure_mode : REGISTER_DEFAULT[0] : When set to 1 register is read only and not writable//
module register_example
#(
parameter REGISTER_WIDTH = 8, // Parameter defines width of register, default 8 bits
parameter [REGISTER_WIDTH-1:0] REGISTER_DEFAULT = 2**REGISTER_WIDTH -2 // Default value of register computed from Width. Sets all bits to 1s except bit 0 (Secure _mode)
)
(
input [REGISTER_WIDTH-1:0] Data_in,
input Clk,
input resetn,
input write,
output reg [REGISTER_WIDTH-1:0] Data_out
);
reg Secure_mode;
always @(posedge Clk or negedge resetn)
if (~resetn)
begin
Data_out <= REGISTER_DEFAULT; // Register content set to Default at reset
Secure_mode <= REGISTER_DEFAULT[0]; // Register Secure_mode set at reset
These example instantiations show how, in a hardware design, it would be possible to instantiate the register module with insecure defaults and parameters.
In the example design, both registers will be software writable since Secure_mode is defined as zero.
(good code)
Example Language: Verilog
register_example #(
.REGISTER_WIDTH (32),
.REGISTER_DEFAULT (1225) // Correct default value set, to enable Secure_mode
The example code is taken from the fuse memory inside the buggy OpenPiton SoC of HACK@DAC'21 [REF-1356]. Fuse memory can be used to store key hashes, password hashes, and configuration information. For example, the password hashes of JTAG and HMAC are stored in the fuse memory in the OpenPiton design.
During the firmware setup phase, data in the Fuse memory are transferred into the registers of the corresponding SoC peripherals for initialization. However, if the offset to access the password hash is set incorrectly, programs cannot access the correct password hash from the fuse memory, breaking the functionalities of the peripherals and even exposing sensitive information through other peripherals.
The following vulnerable code accesses the JTAG password hash from the fuse memory. However, the JTAG_OFFSET is incorrect, and the fuse memory outputs the wrong values to jtag_hash_o. Moreover, setting incorrect offset gives the ability to attackers to access JTAG by knowing other low-privileged peripherals' passwords.
To mitigate this, change JTAG_OFFSET to the correct address of the JTAG key [REF-1357].
The following example code is excerpted from the Access Control module, acct_wrapper, in the Hack@DAC'21 buggy OpenPiton System-on-Chip (SoC). Within this module, a set of memory-mapped I/O registers, referred to as acct_mem, each 32-bit wide, is utilized to store access control permissions for peripherals [REF-1437]. Access control registers are typically used to define and enforce permissions and access rights for various system resources.
However, in the buggy SoC, these registers are all enabled at reset, i.e., essentially granting unrestricted access to all system resources [REF-1438]. This will introduce security vulnerabilities and risks to the system, such as privilege escalation or exposing sensitive information to unauthorized users or processes.
(bad code)
Example Language: SystemVerilog
module acct_wrapper #(
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~rst_6))
begin
for (j=0; j < AcCt_MEM_SIZE; j=j+1)
begin
acct_mem[j] <= 32'hffffffff;
end
end
...
To fix this issue, the access control registers must be properly initialized during the reset phase of the SoC. Correct initialization values should be established to maintain the system's integrity, security, predictable behavior, and allow proper control of peripherals. The specifics of what values should be set depend on the SoC's design and the requirements of the system. To address the problem depicted in the bad code example [REF-1438], the default value for "acct_mem" should be set to 32'h00000000 (see good code example [REF-1439]). This ensures that during startup or after any reset, access to protected data is restricted until the system setup is complete and security procedures properly configure the access control settings.
(good code)
Example Language: SystemVerilog
module acct_wrapper #(
...
always @(posedge clk_i)
begin
if(~(rst_ni && ~rst_6))
begin
for (j=0; j < AcCt_MEM_SIZE; j=j+1)
begin
acct_mem[j] <= 32'h00000000;
end
end
...
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Analysis
Use automated tools to test that values are configured per design specifications. Hardware designs can have a large number of such parameters and register defaults settings, and it is important to have design tool support to check these settings in an automated way and be able to identify which settings are security sensitive.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The logic level used to set a system to a secure state relies on a fuse being unblown.
Extended Description
Fuses are often used to store secret data, including security configuration data. When not blown, a fuse is considered to store a logic 0, and, when blown, it indicates a logic 1. Fuses are generally considered to be one-directional, i.e., once blown to logic 1, it cannot be reset to logic 0.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Selection
Behavior-Property
Incorrect
Info-Type
Fuse Values
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism; Gain Privileges or Assume Identity
Scope: Access Control, Authorization
If the logic used to determine system-security state (by leveraging the values sensed from the fuses) uses negative logic, an attacker might blow the fuse and drive the system to an insecure state.
DoS: Crash, Exit, or Restart
Scope: Availability
Read Memory
Scope: Confidentiality
Modify Memory; Execute Unauthorized Code or Commands
Scope: Integrity
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Logic should be designed in a way that blown fuses do not put the product into an insecure state that can be leveraged by an attacker.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A chip implements a secure boot and uses the sensed value of a fuse
"do_secure_boot" to determine whether to perform a secure boot or not. If this fuse
value is "0", the system performs secure boot. Otherwise, it does not perform secure
boot.
An attacker blows the "do_secure_boot" fuse to "1". After reset, the attacker loads a custom
bootloader, and, since the fuse value is now "1", the system does not perform secure boot,
and the attacker can execute their custom firmware image.
Since by default, a fuse-configuration value is a "0", an attacker can blow it to a "1" with
inexpensive hardware.
If the logic is reversed, an attacker cannot easily reset the fuse. Note that, with
specialized and expensive equipment, an attacker with full physical access might be able to "unblow" the fuse
value to a "0".
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
CWE-1342: Information Exposure through Microarchitectural State after Transient Execution
Weakness ID: 1342
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The processor does not properly clear microarchitectural state after incorrect microcode assists or speculative execution, resulting in transient execution.
Extended Description
In many processor architectures an exception, mis-speculation, or microcode assist results in a flush operation to clear results that are no longer required. This action prevents these results from influencing architectural state that is intended to be visible from software. However, traces of this transient execution may remain in microarchitectural buffers, resulting in a change in microarchitectural state that can expose sensitive information to an attacker using side-channel analysis. For example, Load Value Injection (LVI) [REF-1202] can exploit direct injection of erroneous values into intermediate load and store buffers.
Several conditions may need to be fulfilled for a successful attack:
incorrect transient execution that results in remanence of sensitive information;
attacker has the ability to provoke microarchitectural exceptions;
operations and structures in victim code that can be exploited must be identified.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Execute Unauthorized Code or Commands
Scope: Confidentiality, IntegrityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Requirements
Hardware ensures that no illegal data flows from faulting micro-ops exists at the microarchitectural level.
Effectiveness: High
Note: Being implemented in silicon it is expected to fully address the known weaknesses with limited performance impact.
Build and Compilation
Include instructions that explicitly remove traces of unneeded computations from software interactions with microarchitectural elements e.g. lfence, sfence, mfence, clflush.
Effectiveness: High
Note: This effectively forces the processor to complete each memory access before moving on to the next operation. This may have a large performance impact.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Requirements
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Workstation
(Undetermined Prevalence)
x86
(Undetermined Prevalence)
ARM
(Undetermined Prevalence)
Other
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Faulting loads in a victim domain may trigger incorrect transient forwarding, which leaves secret-dependent traces in the microarchitectural state. Consider this example from [REF-1203].
A processor with this weakness will store the value of untrusted_arg (which may be provided by an attacker) to the stack, which is trusted memory. Additionally, this store operation will save this value in some microarchitectural buffer, e.g. the store queue.
In this code gadget,
trusted_ptr is dereferenced while the attacker forces a page fault. The faulting load causes the processor to mis-speculate by forwarding untrusted_arg as the (speculative) load result. The processor then uses untrusted_arg for the pointer dereference. After the fault has been handled and the load has been re-issued with the correct argument, secret-dependent information stored at the address of trusted_ptr remains in microarchitectural state and can be extracted by an attacker using a code gadget.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Load value injection in some processors utilizing speculative execution may allow an authenticated user to enable information disclosure via a side-channel with local access.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Relationship
CWE-1342 differs from CWE-1303, which is related to misprediction and biasing microarchitectural components, while CWE-1342 addresses illegal data flows and retention. For example, Spectre is an instance of CWE-1303 biasing branch prediction to steer the transient execution indirectly.
Maintenance
As of CWE 4.9, members of the CWE Hardware SIG are closely analyzing this entry and others to improve CWE's coverage of transient execution weaknesses, which include issues related to Spectre, Meltdown, and other attacks. Additional investigation may include other weaknesses related to microarchitectural state. As a result, this entry might change significantly in CWE 4.10.
Jo Van Bulck, Daniel Moghimi, Michael Schwarz, Moritz Lipp, Marina Minkin, Daniel Genkin, Yuval Yarom, Berk Sunar, Daniel Gruss, and Frank Piessens. "LVI - Hijacking Transient Execution with Load Value Injection". 2020.
<https://lviattack.eu/>.
[REF-1203]
Jo Van Bulck, Daniel Moghimi, Michael Schwarz, Moritz Lipp, Marina Minkin, Daniel Genkin, Yuval Yarom, Berk Sunar, Daniel Gruss, and Frank Piessens. "LVI: Hijacking Transient Execution through Microarchitectural Load Value Injection". 2020-01-09.
<https://lviattack.eu/lvi.pdf>.
Stephan van Schaik, Marina Minkin, Andrew Kwong, Daniel Genkin, Yuval Yarom. "CacheOut: Leaking Data on Intel CPUs via Cache Evictions". 2020-12-28.
<https://cacheoutattack.com/files/CacheOut.pdf>.
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The System-on-Chip (SoC) implements a Security Identifier mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity. However, the Security Identifiers are not correctly implemented.
Technical Nuance
A broad class of flaws can exist in the Security
Identifier process, including but not limited to missing
security identifiers, improper conversion of security
identifiers, incorrect generation of security identifiers,
etc.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Quality Degradation
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Security Identifier Decoders must be reviewed for design inconsistency and common weaknesses.
Implementation
Access and programming flows must be tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Systems-On-Chip (Integrated circuits and hardware
engines) implement Security Identifiers to
differentiate/identify actions originated from various
agents. These actions could be 'read', 'write', 'program',
'reset', 'fetch', 'compute', etc. Security identifiers are
generated and assigned to every agent in the System (SoC)
that is either capable of generating an action or receiving
an action from another agent. Every agent could be assigned
a unique, Security Identifier based on its trust level or
privileges.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design, then identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during hardware implementation, then identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Bus/Interface Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reason
Abstraction
Rationale
This CWE entry is a Class and might have Base-level children that would be more appropriate
Comments
Examine children of this entry to see if there is a better fit
Notes
Research Gap
Research could be conducted to better understand the different kinds of weaknesses that constitute an "insecure" Security Identifier mechanism. See Technical_Nuance.
Maintenance
This entry is still under development and will continue to see updates and content improvements.
CWE-1220: Insufficient Granularity of Access Control
Weakness ID: 1220
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product implements access controls via a policy or other feature with the intention to disable or restrict accesses (reads and/or writes) to assets in a system from untrusted agents. However, implemented access controls lack the required granularity
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Access Control
Behavior-Property
Insufficient Granularity
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Other
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
A common weakness that can exist in such protection schemes is that access controls or policies are not granular enough, which renders the control policy too broad, because it allows accesses from unauthorized agents to security-sensitive assets.
This condition allows agents beyond trusted agents to access assets and could lead to a loss of functionality or the ability to set up the device securely. This further results in security risks from leaked, sensitive, key material to modification of device configuration.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Access-control-policy protections must be reviewed for design inconsistency and common weaknesses.
Access-control-policy definition and programming flow must be tested in pre-silicon, post-silicon testing.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient Granularity of Address Regions Protected by Register Locks
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Integrated circuits and hardware engines can expose accesses to assets (device configuration, keys, etc.) to trusted firmware or a software module (commonly set by BIOS/bootloader). This access is typically access-controlled. Upon a power reset, the hardware or system usually starts with default values in registers, and the trusted firmware (Boot firmware) configures the necessary access-control protection.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during hardware implementation and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a system with a register for storing AES key for encryption or decryption. The key is 128 bits, implemented as a set of four 32-bit registers. The key registers are assets and registers, AES_KEY_READ_POLICY and AES_KEY_WRITE_POLICY, and are defined to provide necessary access controls.
The read-policy register defines which agents can read the AES-key registers, and write-policy register defines which agents can program or write to those registers. Each register is a 32-bit register, and it can support access control for a maximum of 32 agents. The number of the bit when set (i.e., "1") allows respective action from an agent whose identity matches the number of the bit and, if "0" (i.e., Clear), disallows the respective action to that corresponding agent.
(bad code)
Example Language: Other
Register
Field description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption Default 0x00000000
AES_ENC_DEC_KEY_4
AES key [96:127] for encryption or decryption Default 0x00000000
AES_KEY_READ_WRITE_POLICY
[31:0] Default 0x00000006 - meaning agent with identities "1" and "2" can both read from and write to key registers
In the above example, there is only one policy register that controls access to both read and write accesses to the AES-key registers, and thus the design is not granular enough to separate read and writes access for different agents. Here, agent with identities "1" and "2" can both read and write.
A good design should be granular enough to provide separate access controls to separate actions. Access control for reads should be separate from writes. Below is an example of such implementation where two policy registers are defined for each of these actions. The policy is defined such that: the AES-key registers can only be read or used by a crypto agent with identity "1" when bit #1 is set. The AES-key registers can only be programmed by a trusted firmware with identity "2" when bit #2 is set.
(good code)
Example Language: Other
AES_KEY_READ_POLICY
[31:0] Default 0x00000002 - meaning only Crypto engine with identity "1" can read registers: AES_ENC_DEC_KEY_0, AES_ENC_DEC_KEY_1, AES_ENC_DEC_KEY_2, AES_ENC_DEC_KEY_3
AES_KEY_WRITE_POLICY
[31:0] Default 0x00000004 - meaning only trusted firmware with identity "2" can program registers: AES_ENC_DEC_KEY_0, AES_ENC_DEC_KEY_1, AES_ENC_DEC_KEY_2, AES_ENC_DEC_KEY_3
Example 2
Within the AXI node interface wrapper module in the RISC-V AXI module of the HACK@DAC'19 CVA6 SoC [REF-1346], an access control mechanism is employed to regulate the access of different privileged users to peripherals.
The AXI ensures that only users with appropriate privileges can access specific peripherals. For instance, a ROM module is accessible exclusively with Machine privilege, and AXI enforces that users attempting to read data from the ROM must possess machine privilege; otherwise, access to the ROM is denied. The access control information and configurations are stored in a ROM.
However, in the example code above, while assigning distinct privileges to AXI manager and subordinates, both the Platform-Level Interrupt Controller Specification (PLIC) and the Core-local Interrupt Controller (CLINT) (which are peripheral numbers 6 and 7 respectively) utilize the same access control configuration. This common configuration diminishes the granularity of the AXI access control mechanism.
In certain situations, it might be necessary to grant higher privileges for accessing the PLIC than those required for accessing the CLINT. Unfortunately, this differentiation is overlooked, allowing an attacker to access the PLIC with lower privileges than intended.
As a consequence, unprivileged code can read and write to the PLIC even when it was not intended to do so. In the worst-case scenario, the attacker could manipulate interrupt priorities, potentially modifying the system's behavior or availability.
To address the aforementioned vulnerability, developers must enhance the AXI access control granularity by implementing distinct access control entries for the Platform-Level Interrupt Controller (PLIC) and the Core-local Interrupt Controller (CLINT). By doing so, different privilege levels can be defined for accessing PLIC and CLINT, effectively thwarting the potential attacks previously highlighted. This approach ensures a more robust and secure system, safeguarding against unauthorized access and manipulation of interrupt priorities. [REF-1347]
Consider the following SoC
design. The sram in HRoT has an address range that is readable and writable by unprivileged
software and it has an area that is only readable by unprivileged software. The tbus
interconnect enforces access control for subordinates on the bus but uses only one bit to control
both read and write access. Address 0xA0000000 - 0xA000FFFF is readable and writable
by the untrusted cores core{0-N} and address 0xA0010000 - 0xA001FFFF is only
readable by the untrusted cores core{0-N}.
The security policy access control is not granular enough, as it uses one bit to enable both
read and write access. This gives write access to an area that should only be readable
by unprivileged agents.
Access control logic should differentiate between read and write access and to have
sufficient address granularity.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
A form hosting website only checks the session authentication status for a single form, making it possible to bypass authentication when there are multiple forms
An operating system has an overly permissive Access Control List on some system files, including those related to user passwords
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1222: Insufficient Granularity of Address Regions Protected by Register Locks
Weakness ID: 1222
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
VariantVariant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product defines a large address region protected from modification by the same register lock control bit. This results in a conflict between the functional requirement that some addresses need to be writable by software during operation and the security requirement that the system configuration lock bit must be set during the boot process.
Extended Description
A problem can arise wherein the protected region definition is not granular enough. After the programmable lock bit has been set, then this new functionality cannot be implemented without changing the hardware design.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Other
Scope: Access Control
System security configuration cannot be defined in a way that does not conflict with functional requirements of device.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The defining of protected locked registers should be reviewed or tested early in the design phase with software teams to ensure software flows are not blocked by the security locks.
As an alternative to using register lock control bits and fixed access control regions, the hardware design could use programmable security access control configuration so that device trusted firmware can configure and change the protected regions based on software usage and security models.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Integrated circuits and hardware IPs can expose the device configuration controls that need to be programmed after device power reset by a trusted firmware or software module (commonly set by BIOS/bootloader) and then locked from any further modification. In hardware design, this is commonly implemented using a programmable lock bit that enables/disables writing to a protected set of registers or address regions. When the programmable lock bit is set, the relevant address region can be implemented as a hardcoded value in hardware logic that cannot be changed later.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues are introduced during hardware architecture and design since software controls and configuration are defined during these phases and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
For example, consider a hardware unit with a 32 kilobyte configuration address space where the first 8 kilobyte address contains security sensitive controls that must only be writable by device bootloader. One way to protect the security configuration could be to define a 32 bit system configuration locking register (SYS_LOCK) where each bit lock locks the corresponding 1 kilobyte region.
(bad code)
Example Language: Other
Address
Register
0x0000
SYS_LOCK: 32 bit system configuration lock register, each bit is write-1-once
0x0004
SECURITY_FEATURE_ENABLE: 32 bit register controlling enabling of security features
...
0x0310
SW_MODE: 32 bit Software Mode indication register
Address region
Lock bit
0x0000 - 0x03FF
SYS_LOCK[0]
0x0400 - 0x07FF
SYS_LOCK[1]
...
0x7C00 - 0x7FFF
SYS_LOCK[31]
If a register exists within the first kilobyte address range (e.g. SW_MODE, address 0x310) and needs to be software writable at runtime, then this register cannot be written in a securely configured system since SYS_LOCK register lock bit 0 must be set to protect other security settings (e.g. SECURITY_FEATURE_ENABLE, address 0x0004). The only fix would be to change the hardware logic or not set the security lock bit.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Variant level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1301: Insufficient or Incomplete Data Removal within Hardware Component
Weakness ID: 1301
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product's data removal process does not completely delete all data and potentially sensitive information within hardware components.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Application Data
Scope: Confidentiality
Recovering data after erasure or overwriting is possible due to a phenomenon called data remanence. For example, if the same value is written repeatedly to a memory location, the corresponding memory cells can become physically altered to a degree such that even after the original data is erased, that data can still be recovered through physical characterization of the memory cells.
Physical properties of hardware devices, such as remanence of magnetic media, residual charge of ROMs/RAMs, or screen burn-in, may still retain sensitive data after a data removal process has taken place and power is removed.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Apply blinding or masking techniques to implementations of cryptographic algorithms.
Implementation
Alter the method of erasure, add protection of media, or destroy the media to protect the data.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information in Resource Not Removed Before Reuse
ParentOf
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Firmware Data Deletion Vulnerability in which a base station factory reset might not delete all user information. The impact of this enables a new owner of a used device that has been "factory-default reset" with a vulnerable firmware version can still retrieve, at least, the previous owner's wireless network name, and the previous owner's wireless security (such as WPA2) key. This issue was addressed with improved, data deletion.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not contain sufficient
technical or engineering documentation (whether on paper or
in electronic form) that contains descriptions of all of the
relevant software/hardware elements of the product.
Technical Nuance
Documentation elements might include the product's usage,
structure, architectural components, interfaces, design,
implementation, configuration, operation, etc.
Hardware-related documentation may include engineering artifacts such as hardware description language (HDLs), netlists, Gerber files, Bills of Materials, EDA (Electronic Design Automation) tool files, etc.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Without a method of verification, one cannot be sure that everything only functions as expected. When technical documentation is limited or lacking, products are more difficult to maintain. This indirectly affects security by making it more difficult or time-consuming to find and/or fix vulnerabilities.
When using time-limited or labor-limited third-party/in-house security consulting services (such as threat modeling, vulnerability discovery, or pentesting), insufficient documentation can force those consultants to invest unnecessary time in learning how the product is organized, instead of focusing their expertise on finding the flaws or suggesting effective mitigations.
With respect to hardware design, the lack of a formal, final manufacturer reference can make it difficult or impossible to evaluate the final product, including post-manufacture verification. One cannot ensure that design functionality or operation is within acceptable tolerances, conforms to specifications, and is free from unexpected behavior.
Potential Mitigations
Phase(s)
Mitigation
Documentation; Architecture and Design
Ensure that design documentation is detailed enough to allow for post-manufacturing verification.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Documentation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
A wireless access point manual specifies that the only method of configuration is via web interface (CWE-1059), but there is an undisclosed telnet server that was activated by default (CWE-912).
Weakness Ordinalities
Ordinality
Description
Indirect
(where the weakness is a quality issue that might indirectly make it easier to introduce security-relevant weaknesses or make them more difficult to detect)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
FDA. "Cybersecurity in Medical Devices: Quality System Considerations and Content of Premarket Submissions Draft Guidance for Industry and Food and Drug Administration Staff (DRAFT GUIDANCE)". 2022-04-08.
<https://www.fda.gov/media/119933/download>.
Content
History
Submissions
Submission Date
Submitter
Organization
2018-07-02
(CWE 3.2, 2019-01-03)
CWE Content Team
MITRE
Entry derived from Common Quality Enumeration (CQE) Draft 0.9.
Contributions
Contribution Date
Contributor
Organization
2023-04-25
(CWE 4.11, 2023-04-27)
"Mapping CWE to 62443" Sub-Working Group
CWE-CAPEC ICS/OT SIG
Suggested mappings to ISA/IEC 62443.
2021-06-11
(CWE 4.7, 2022-04-28)
Paul A. Wortman
Wells Fargo
Submitted hardware-specific information about a "golden standard" that was integrated into this entry
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are those that arise due to integration of multiple hardware Intellectual Property (IP) cores, from System-on-a-Chip (SoC) subsystem interactions, or from hardware platform subsystem interactions.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1244: Internal Asset Exposed to Unsafe Debug Access Level or State
Weakness ID: 1244
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses physical debug or test
interfaces with support for multiple access levels, but it
assigns the wrong debug access level to an internal asset,
providing unintended access to the asset from untrusted debug
agents.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory
Scope: Confidentiality
If a protection mechanism does not ensure that
internal assets have the correct debug access level during
each boot stage or change in system state, an attacker could
obtain sensitive information from the internal asset using a
debugger.
Modify Memory
Scope: Integrity
Gain Privileges or Assume Identity; Bypass Protection Mechanism
Scope: Authorization, Access Control
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
For security-sensitive assets accessible over debug/test interfaces, only allow trusted agents.
Effectiveness: High
Architecture and Design
Apply blinding [REF-1219] or masking techniques in strategic areas.
Effectiveness: Limited
Implementation
Add shielding or tamper-resistant protections to the device, which increases the difficulty and cost for accessing debug/test interfaces.
Effectiveness: Limited
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Debug authorization can have multiple levels of
access, defined such that different system internal assets
are accessible based on the current authorized debug
level. Other than debugger authentication (e.g., using
passwords or challenges), the authorization can also be
based on the system state or boot stage. For example, full
system debug access might only be allowed early in boot
after a system reset to ensure that previous session data is
not accessible to the authenticated debugger.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The JTAG interface is used to perform debugging and provide CPU core access for developers. JTAG-access protection is implemented as part of the JTAG_SHIELD bit in the hw_digctl_ctrl register. This register has no default value at power up and is set only after the system boots from ROM and control is transferred to the user software.
(bad code)
Example Language: Other
1 bit
0x0 = JTAG debugger is enabled (default)
JTAG_SHIELD
0x1 = JTAG debugger is disabled
This means that since the end user has access to JTAG at system reset and during ROM code execution before control is transferred to user software, a JTAG user can modify the boot flow and subsequently disclose all CPU information, including data-encryption keys.
(informative)
The default value of this register bit should be set to 1 to prevent the JTAG from being enabled at system reset.
Example 2
The example code below is taken from the CVA6 processor core of the HACK@DAC'21 buggy OpenPiton SoC. Debug access allows users to access internal hardware registers that are otherwise not exposed for user access or restricted access through access control protocols. Hence, requests to enter debug mode are checked and authorized only if the processor has sufficient privileges. In addition, debug accesses are also locked behind password checkers. Thus, the processor enters debug mode only when the privilege level requirement is met, and the correct debug password is provided.
The following code [REF-1377] illustrates an instance of a vulnerable implementation of debug mode. The core correctly checks if the debug requests have sufficient privileges and enables the debug_mode_d and debug_mode_q signals. It also correctly checks for debug password and enables umode_i signal.
(bad code)
Example Language: SystemVerilog
module csr_regfile #(
...
// check that we actually want to enter debug depending on the privilege level we are currently in
unique case (priv_lvl_o)
However, it grants debug access and changes the privilege level, priv_lvl_o, even when one of the two checks is satisfied and the other is not. Because of this, debug access can be granted by simply requesting with sufficient privileges (i.e., debug_mode_q is enabled) and failing the password check (i.e., umode_i is disabled). This allows an attacker to bypass the debug password checking and gain debug access to the core, compromising the security of the processor.
A fix to this issue is to only change the privilege level of the processor when both checks are satisfied, i.e., the request has enough privileges (i.e., debug_mode_q is enabled) and the password checking is successful (i.e., umode_i is enabled) [REF-1378].
(good code)
Example Language: SystemVerilog
module csr_regfile #(
...
// check that we actually want to enter debug depending on the privilege level we are currently in
unique case (priv_lvl_o)
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
After ROM code execution, JTAG access is disabled. But before the ROM code is executed, JTAG access is possible, allowing a user full system access. This allows a user to modify the boot flow and successfully bypass the secure-boot process.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Check 2 devices for their passcode to authenticate access to JTAG/debugging ports. If the passcodes are missing or the same, update the design to fix and retest. Check communications over JTAG/debugging ports for encryption. If the communications are not encrypted, fix the design and retest.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Relationship
CWE-1191 and CWE-1244 both involve physical debug access,
but the weaknesses are different. CWE-1191 is effectively
about missing authorization for a debug interface,
i.e. JTAG. CWE-1244 is about providing internal assets with
the wrong debug access level, exposing the asset to
untrusted debug agents.
CWE Grouping: Manufacturing and Life Cycle Management Concerns
Grouping ID: 1195
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are root-caused to defects that arise in the semiconductor-manufacturing process or during the life cycle and supply chain.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are typically associated with memory (e.g., DRAM, SRAM) and storage technologies (e.g., NAND Flash, OTP, EEPROM, and eMMC).
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product's architecture mirrors regions without ensuring that their contents always stay in sync.
Extended Description
In the interest of increased performance, one might need to duplicate a resource. A cache memory is a common example of this concept, which keeps a "local" copy of a data element in the high speed cache memory. Unfortunately, this speed improvement comes with a downside, since the product needs to ensure that the local copy always mirrors the original copy truthfully. If they get out of sync, the computational result is no longer true.
During hardware design, memory is not the only item that gets mirrored. There are many other entities that get mirrored, as well: registers, memory regions, and, in some cases, even whole computational units. For example, within a multi-core processor, if all memory accesses for each and every core goes through a single Memory-Management Unit (MMU) then the MMU will become a performance bottleneck. In such cases, duplicating local MMUs that will serve only a subset of the cores rather than all of them may resolve the performance issue. These local copies are also called "shadow copies" or "mirrored copies."
If the original resource never changed, local duplicate copies getting out of sync would never be an issue. However, the values of the original copy will sometimes change. When the original copy changes, the mirrored copies must also change, and change fast.
This situation of shadow-copy-possibly-out-of-sync-with-original-copy might occur as a result of multiple scenarios, including the following:
After the values in the original copy change, due to some reason the original copy does not send the "update" request to its shadow copies.
After the values in the original copy change, the original copy dutifully sends the "update" request to its shadow copies, but due to some reason the shadow copy does not "execute" this update request.
After the values in the original copy change, the original copy sends the "update" request to its shadow copies, and the shadow copy executes this update request faithfully. However, during the small time period when the original copy has "new" values and the shadow copy is still holding the "old" values, an attacker can exploit the old values. Then it becomes a race condition between the attacker and the update process of who can reach the target, shadow copy first, and, if the attacker reaches first, the attacker wins.
The attacker might send a "spoofed" update request to the target shadow copy, pretending that this update request is coming from the original copy. This spoofed request might cause the targeted shadow copy to update its values to some attacker-friendly values, while the original copies remain unchanged by the attacker.
Suppose a situation where the original copy has a system of reverting back to its original value if it does not hear back from all the shadow copies that such copies have successfully completed the update request. In such a case, an attack might occur as follows: (1) the original copy might send an update request; (2) the shadow copy updates it; (3) the shadow copy sends back the successful completion message; (4) through a separate issue, the attacker is able to intercept the shadow copy's completion message. In this case, the original copy thinks that the update did not succeed, hence it reverts to its original value. Now there is a situation where the original copy has the "old" value, and the shadow copy has the "new" value.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Having mirrored regions with different values might result in the exposure of sensitive information or possibly system compromise.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Whenever there are multiple, physically different copies of the same value that might change and the process to update them is not instantaneous and atomic, it is impossible to assert that the original and shadow copies will always be in sync - there will always be a time period when they are out of sync. To mitigate the consequential risk, the recommendations essentially are:
Make this out-of-sync time period as small as possible, and
Make the update process as robust as possible.
Effectiveness: Moderate
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Protection for Mirrored Regions in On-Chip Fabric Firewall
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
VHDL
(Undetermined Prevalence)
Verilog
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Suppose a processor's Memory Management Unit (MMU) has 5 other shadow MMUs to distribute its workload for its various cores. Each MMU has the start address and end address of "accessible" memory. Any time this accessible range changes (as per the processor's boot status), the main MMU sends an update message to all the shadow MMUs.
Suppose the interconnect fabric does not prioritize such "update" packets over other general traffic packets. This introduces a race condition. If an attacker can flood the target with enough messages so that some of those attack packets reach the target before the new access ranges gets updated, then the attacker can leverage this scenario.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Research Gap
Issues related to state and cache - creation, preservation, and update - are a significant gap in CWE that is expected to be addressed in future versions. It has relationships to concurrency and synchronization, incorrect behavior order, and other areas that already have some coverage in CWE, although the focus has typically been on independent processes on the same operating system - not on independent systems that are all a part of a larger system-of-systems.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Missing an ability to patch ROM code may leave a System or System-on-Chip (SoC) in a vulnerable state.
Extended Description
A System or System-on-Chip (SoC) that implements a boot process utilizing security mechanisms such as Root-of-Trust (RoT) typically starts by executing code from a Read-only-Memory (ROM) component.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context; Reduce Maintainability
Scope: OtherLikelihood: High
Because the code in ROM is immutable, the ROM does not have the ability to patch after the system gets shipped. Hence any security vulnerabilities discovered in the ROM code can never be fixed for the systems that are already in use. Thus the system can be left in a vulnerable state where an adversary can compromise the SoC..
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Secure patch support to allow ROM code to be patched on the next boot.
Effectiveness: Moderate
Note:
Some parts of the hardware initialization or signature verification done to authenticate patches will always be "not patchable."
Architecture and Design; Implementation
Support patches that can be programmed in-field or during manufacturing through hardware fuses. This feature can be used for limited patching of devices after shipping, or for the next batch of silicon devices manufactured, without changing the full device ROM.
Effectiveness: Moderate
Note:
Patches that use hardware fuses will have limitations in terms of size and the number of patches that can be supported. Note that some parts of the hardware initialization or signature verification done to authenticate patches will always be "not patchable."
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This issue could be introduced during hardware architecture and design and can be identified later during Testing.
Implementation
This issue could be introduced during implementation and can be identified later during Testing.
Integration
This issue could be introduced during integration and can be identified later during Testing.
Manufacturing
This issue could be introduced during manufacturing and can be identified later during Testing.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A System-on-Chip (SOC) implements a Root-of-Trust (RoT) in ROM to boot secure code. However, at times this ROM code might have security vulnerabilities and need to be patched. Since ROM is immutable, it can be impossible to patch.
ROM does not have built-in application-programming interfaces (APIs) to patch if the code is vulnerable. Implement mechanisms to patch the vulnerable ROM code.
Example 2
The example code is taken from the SoC peripheral wrapper inside the buggy OpenPiton SoC of HACK@DAC'21. The wrapper is used for connecting the communications between SoC peripherals, such as crypto-engines, direct memory access (DMA), reset controllers, JTAG, etc. The secure implementation of the SoC wrapper should allow users to boot from a ROM for Linux (i_bootrom_linux) or from a patchable ROM (i_bootrom_patch) if the Linux bootrom has security or functional issues.The example code is taken from the SoC peripheral wrapper inside the buggy OpenPiton SoC of HACK@DAC'21. The wrapper is used for connecting the communications between SoC peripherals, such as crypto-engines, direct memory access (DMA), reset controllers, JTAG, etc. The secure implementation of the SoC wrapper should allow users to boot from a ROM for Linux (i_bootrom_linux) or from a patchable ROM (i_bootrom_patch) if the Linux bootrom has security or functional issues.
The above implementation causes the ROM data to be hardcoded for the linux system (rom_rdata_linux) regardless of the value of ariane_boot_sel_i. Therefore, the data (rom_rdata_patch) from the patchable ROM code is never used [REF-1396].
This weakness disables the ROM's ability to be patched. If attackers uncover security vulnerabilities in the ROM, the users must replace the entire device. Otherwise, the weakness exposes the system to a vulnerable state forever.
A fix to this issue is to enable rom_rdata to be selected from the patchable rom (rom_rdata_patch) [REF-1397].
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not implement a required step in a cryptographic algorithm, resulting in weaker encryption than advertised by the algorithm.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access Control
Read Application Data; Modify Application Data
Scope: Confidentiality, Integrity
Hide Activities
Scope: Accountability, Non-Repudiation
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Use of a Cryptographic Primitive with a Risky Implementation
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Driving Intermediate Cryptographic State/Results to Hardware Module Outputs
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Developers sometimes omit "expensive" (resource-intensive) steps in order to improve performance, especially in devices with limited memory or slower CPUs. This step may be taken under a mistaken impression that the step is unnecessary for the cryptographic algorithm.
Requirements
This issue may happen when the requirements for the cryptographic algorithm are not clearly stated.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The example code is taken from the HMAC engine inside the buggy OpenPiton SoC of HACK@DAC'21 [REF-1358]. HMAC is a message authentication code (MAC) that uses both a hash and a secret crypto key. The HMAC engine in HACK@DAC SoC uses the SHA-256 module for the calculation of the HMAC for 512 bits messages.
However, this HMAC engine cannot handle messages that are longer than 512 bits. Moreover, a complete HMAC will contain an iterate hash function that breaks up a message into blocks of a fixed size and iterates over them with a compression function (e.g., SHA-256). Therefore, the implementation of the HMAC in OpenPiton SoC is incomplete. Such HMAC engines will not be used in real-world applications as the messages will usually be longer than 512 bits. For instance, OpenTitan offers a comprehensive HMAC implementation that utilizes a FIFO for temporarily storing the truncated message, as detailed in [REF-1359].
To mitigate this, implement the iterative function to break up a message into blocks of a fixed size.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Missing challenge-response step allows authentication bypass using public key.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Functional Areas
Cryptography
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
OWASP Top Ten 2007 Category A9 - Insecure Communications
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
OWASP Top Ten 2025 Category A04:2025 - Cryptographic Failures
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not have documentation that represents how it is designed.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
This issue can make it more difficult to understand and maintain the product. It can make it more difficult and time-consuming to detect and/or fix vulnerabilities.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Documentation
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Indirect
(where the weakness is a quality issue that might indirectly make it easier to introduce security-relevant weaknesses or make them more difficult to detect)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
CWE-1326: Missing Immutable Root of Trust in Hardware
Weakness ID: 1326
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A missing immutable root of trust in the hardware results in the ability to bypass secure boot or execute untrusted or adversarial boot code.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Execute Unauthorized Code or Commands; Modify Memory
Scope: Authentication, AuthorizationLikelihood: High
If the memory contents (i.e., RoT) are mutable, then an adversary can modify the RoT to execute their choice of code, resulting in a compromised secure boot.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
When architecting the system, the RoT should be designated for storage in a memory that does not allow further programming/writes. Note that, for components like ROM, secure patching/update features should be supported to allow authenticated and authorized updates in the field.
Implementation
During implementation and test, the RoT memory location should be demonstrated to not allow further programming/writes.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
A System-on-Chip (SoC) implements secure boot by verifying or authenticating signed boot code. The signing of the code is achieved by an entity that the SoC trusts. Before executing the boot code, the SoC verifies that the code (or the public key with which the code has been signed) has not been tampered with. The other data upon which the SoC depends are system-hardware settings in fuses, such as whether "Secure Boot is enabled". These data play a crucial role in establishing a Root of Trust (RoT) to execute secure-boot flows.
One of the many ways RoT is achieved is by storing the code and data in memory or fuses. This memory should be immutable, i.e., once the RoT is programmed/provisioned in memory, that memory should be locked and prevented from further programming or writes.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Such issues could be introduced during policy definition, hardware architecture, design, manufacturing, and/or provisioning. They can be identified later during testing or system configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Security Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The RoT is stored in memory. This memory can be modified by an adversary. For example, if an SoC implements "Secure Boot" by storing the boot code in an off-chip/on-chip flash, the contents of the flash can be modified by using a flash programmer. Similarly, if the boot code is stored in ROM (Read-Only Memory) but the public key or the hash of the public key (used to enable "Secure Boot") is stored in Flash or a memory that is susceptible to modifications or writes, the implementation is vulnerable.
In general, if the boot code, key materials and data that enable "Secure Boot" are all mutable, the implementation is vulnerable.
Good architecture defines RoT as immutable in hardware. One of the best ways to achieve immutability is to store boot code, public key or hash of the public key and other relevant data in Read-Only Memory (ROM) or One-Time Programmable (OTP) memory that prevents further programming or writes.
Example 2
The example code below is a snippet from the bootrom of the HACK@DAC'19 buggy OpenPiton SoC [REF-1348]. The contents of the bootrom are critical in implementing the hardware root of trust.
It performs security-critical functions such as defining the system's device tree, validating the hardware cryptographic accelerators in the system, etc. Hence, write access to bootrom should be strictly limited to authorized users or removed completely so that bootrom is immutable. In this example (see the vulnerable code source), the boot instructions are stored in bootrom memory, mem. This memory can be read using the read address, addr_i, but write access should be restricted or removed.
(bad code)
Example Language: SystemVerilog
...
always_ff @(posedge clk_i) begin
if (req_i) begin
if (!we_i) begin
raddr_q <= addr_i[$clog2(RomSize)-1+3:3];
end else begin
mem[addr_i[$clog2(RomSize)-1+3:3]] <= wdata_i;
end
end
end
...
// this prevents spurious Xes from propagating into the speculative fetch stage of the core
The vulnerable code shows an insecure implementation of the bootrom where bootrom can be written directly by enabling write enable, we_i, and using write address, addr_i, and write data, wdata_i.
To mitigate this issue, remove the write access to bootrom memory. [REF-1349]
(good code)
Example Language: SystemVerilog
...
always_ff @(posedge clk_i) begin
if (req_i) begin
raddr_q <= addr_i[$clog2(RomSize)-1+3:3];
end
end
...
// this prevents spurious Xes from propagating into the speculative fetch stage of the core
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Dynamic Analysis
Automated testing can verify that RoT components are immutable.
Effectiveness: High
Architecture or Design Review
Root of trust elements and memory should be part of architecture and design reviews.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1278: Missing Protection Against Hardware Reverse Engineering Using Integrated Circuit (IC) Imaging Techniques
Weakness ID: 1278
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Information stored in hardware may be recovered by an attacker with the capability to capture and analyze images of the integrated circuit using techniques such as scanning electron microscopy.
Extended Description
These secrets may be stored in non-volatile memory or in the circuit netlist. Memory technologies such as masked ROM make it easier to extract secrets than One-time Programmable (OTP) memory.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Protection
Behavior-Property
Missing
Technology
Hardware
Attack
Reverse Engineering
Technology
Integrated Circuit
Acronym
(IC)
Attack
Imaging Techniques
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Confidentiality
A common goal of malicious actors who reverse engineer ICs is to produce and sell counterfeit versions of the IC.
The physical structure of a device, viewed at high enough magnification, can reveal the information stored inside. Typical steps in IC reverse engineering involve removing the chip packaging (decapsulation), then using various imaging techniques ranging from high resolution x-ray microscopy to invasive techniques involving removing IC layers and imaging each layer using a scanning electron microscope.
The goal of such activities is to recover secret keys, unique device identifiers, and proprietary code and circuit designs embedded in hardware that the attacker has been unsuccessful at accessing through other means.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The cost of secret extraction via IC reverse engineering should outweigh the potential value of the secrets being extracted. Threat model and value of secrets should be used to choose the technology used to safeguard those secrets. Examples include IC camouflaging and obfuscation, tamper-proof packaging, active shielding, and physical tampering detection information erasure.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider an SoC design that embeds a secret key in read-only memory (ROM). The key is baked into the design logic and may not be modified after fabrication causing the key to be identical for all devices. An attacker in possession of the IC can decapsulate and delayer the device. After imaging the layers, computer vision algorithms or manual inspection of the circuit features locate the ROM and reveal the value of the key bits as encoded in the visible circuit structure of the ROM.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements. It is more attack-oriented, so it might be more suited for CAPEC.
Shahed E. Quadir, Junlin Chen, Domenic Forte, Navid Asadizanjani, Sina Shahbazmohamadi, Lei Wang, John Chandy and Mark Tehranipoor. "A Survey on Chip to System Reverse Engineering". <https://dl.acm.org/doi/pdf/10.1145/2755563>.
(URL validated: 2023-04-07)
CWE-1312: Missing Protection for Mirrored Regions in On-Chip Fabric Firewall
Weakness ID: 1312
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The firewall in an on-chip fabric protects the main addressed region, but it does not protect any mirrored memory or memory-mapped-IO (MMIO) regions.
Extended Description
Few fabrics mirror memory and address ranges, where mirrored regions contain copies of the original data. This redundancy is used to achieve fault tolerance. Whatever protections the fabric firewall implements for the original region should also apply to the mirrored regions. If not, an attacker could bypass existing read/write protections by reading from/writing to the mirrored regions to leak or corrupt the original data.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
The fabric firewall should apply the same protections as the original region to the mirrored regions.
Implementation
The fabric firewall should apply the same protections as the original region to the mirrored regions.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Peripherals, On-chip Fabric, and Interface/IO Problems
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A memory-controller IP block is connected to the on-chip fabric in a System on Chip (SoC). The memory controller is configured to divide the memory into four parts: one original and three mirrored regions inside the memory. The upper two bits of the address indicate which region is being addressed. 00 indicates the original region and 01, 10, and 11 are used to address the mirrored regions. All four regions operate in a lock-step manner and are always synchronized. The firewall in the on-chip fabric is programmed to protect the assets in the memory.
The firewall only protects the original range but not the mirrored regions.
The attacker (as an unprivileged user) sends a write transaction to the mirrored region. The mirrored region has an address with the upper two bits set to "10" and the remaining bits of the address pointing to an asset. The firewall does not block this write transaction. Once the write is successful, contents in the protected-memory region are also updated. Thus, the attacker can bypass existing, memory protections.
Firewall should protect mirrored regions.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Dynamic Analysis
Using an external debugger, send write transactions to mirrored regions to test if original, write-protected regions are modified. Similarly, send read transactions to mirrored regions to test if the original, read-protected signals can be read.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1299: Missing Protection Mechanism for Alternate Hardware Interface
Weakness ID: 1299
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The lack of protections on alternate paths to access
control-protected assets (such as unprotected shadow registers
and other external facing unguarded interfaces) allows an
attacker to bypass existing protections to the asset that are
only performed against the primary path.
Extended Description
An asset inside a chip might have access-control
protections through one interface. However, if all paths to
the asset are not protected, an attacker might compromise
the asset through alternate paths. These alternate paths
could be through shadow or mirror registers inside the IP
core, or could be paths from other external-facing
interfaces to the IP core or SoC.
Consider an SoC with various interfaces such as UART,
SMBUS, PCIe, USB, etc. If access control is implemented for
SoC internal registers only over the PCIe interface, then
an attacker could still modify the SoC internal registers
through alternate paths by coming through interfaces such
as UART, SMBUS, USB, etc.
Alternatively, attackers might be able to bypass
existing protections by exploiting unprotected, shadow
registers. Shadow registers and mirror registers typically
refer to registers that can be accessed from multiple
addresses. Writing to or reading from the aliased/mirrored
address has the same effect as writing to the address of
the main register. They are typically implemented within an
IP core or SoC to temporarily hold certain data. These data
will later be updated to the main register, and both
registers will be in synch. If the shadow registers are not
access-protected, attackers could simply initiate
transactions to the shadow registers and compromise system
security.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Alter Execution Logic; Bypass Protection Mechanism; Quality Degradation
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Requirements
Protect assets from accesses against all potential interfaces and alternate paths.
Effectiveness: Defense in Depth
Architecture and Design
Protect assets from accesses against all potential interfaces and alternate paths.
Effectiveness: Defense in Depth
Implementation
Protect assets from accesses against all potential interfaces and alternate paths.
Effectiveness: Defense in Depth
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Authentication Bypass Using an Alternate Path or Channel
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
On-Chip Debug and Test Interface With Improper Access Control
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Write Protection for Parametric Data Values
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Register SECURE_ME is located at address 0xF00. A
mirror of this register called COPY_OF_SECURE_ME is
at location 0x800F00. The register SECURE_ME is
protected from malicious agents and only allows
access to select, while COPY_OF_SECURE_ME is not.
Access control is implemented using an allowlist (as
indicated by acl_oh_allowlist). The identity of the
initiator of the transaction is indicated by the
one hot input, incoming_id. This is checked against
the acl_oh_allowlist (which contains a list of
initiators that are allowed to access the asset).
Though this example is shown in Verilog, it will
apply to VHDL as well.
The bugged line of code is repeated in the Bad
example above. The weakness arises from the fact that the
SECURE_ME register can be modified by writing to the
shadow register COPY_OF_SECURE_ME. The address of
COPY_OF_SECURE_ME should also be included in the check.
That buggy line of code should instead be replaced as
shown in the Good Code Snippet below.
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
When the internal flash is protected by blocking access on the Data Bus (DBUS), it can still be indirectly accessed through the Instruction Bus (IBUS).
When GPIO is protected by blocking access
to corresponding GPIO resource registers,
protection can be bypassed by writing to the
corresponding banked GPIO registers instead.
monitor device allows access to physical UART debug port without authentication
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1429: Missing Security-Relevant Feedback for Unexecuted Operations in Hardware Interface
Weakness ID: 1429
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product has a hardware interface that silently discards operations
in situations for which feedback would be security-relevant, such as
the timely detection of failures or attacks.
Extended Description
While some systems intentionally withhold feedback as a security
measure, this approach must be strictly controlled to ensure it does
not obscure operational failures that require prompt detection and
remediation. Without these essential confirmations, failures go
undetected, increasing the risk of data loss, security
vulnerabilities, and overall system instability. Even when withholding
feedback is an intentional part of a security policy designed, for
example, to prevent attackers from gleaning sensitive internal
details, the absence of expected feedback becomes a critical weakness
when it masks operational failures that require prompt detection and
remediation.
For instance, certain encryption algorithms always return ciphertext
regardless of errors to prevent attackers from gaining insight into
internal state details. However, if such an algorithm fails to
generate the expected ciphertext and provides no error feedback, the
system cannot distinguish between a legitimate output and a
malfunction. This can lead to undetected cryptographic failures,
potentially compromising data security and system reliability. Without
proper notification, a critical failure might remain hidden,
undermining both the reliability and security of the process.
Therefore, this weakness captures issues across various hardware
interfaces where operations are discarded without any feedback, error
handling, or logging. Such omissions can lead to data loss, security
vulnerabilities, and system instability, with potential impacts
ranging from minor to catastrophic.
For some kinds of hardware products, some errors may be correctly
identified and subsequently discarded, and the lack of feedback may
have been an intentional design decision. However, this could result
in a weakness if system operators or other authorized entities are not
provided feedback about security-critical operations or failures that
could prevent the operators from detecting and responding to an
attack.
For example:
In a System-on-Chip (SoC) platform, write operations to reserved
memory addresses might be correctly identified as invalid and
subsequently discarded. However, if no feedback is provided to
system operators, they may misinterpret the device's state, failing
to recognize conditions that could lead to broader failures or
security vulnerabilities. For example, if an attacker attempts
unauthorized writes to protected regions, the system may silently
discard these writes without alerting security mechanisms. This lack
of feedback could obscure intrusion attempts or misconfigurations,
increasing the risk of unnoticed system compromise
Microcontroller Interrupt Systems: When interrupts are silently
ignored due to priority conflicts or internal errors without
notifying higher-level control, it becomes challenging to diagnose
system failures or detect potential security breaches in a timely
manner.
Network Interface Controllers: Dropping packets - perhaps due to
buffer overflows - without any error feedback can not only cause data
loss but may also contribute to exploitable timing discrepancies
that reveal sensitive internal processing details.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Read Files or Directories
Scope: ConfidentialityLikelihood: Medium
Critical data may be exposed if operations are unexecuted or
discarded silently, allowing attackers to exploit the lack of
feedback.
Modify Memory; Modify Files or Directories
Scope: IntegrityLikelihood: Medium
Operations may proceed based on incorrect assumptions,
potentially causing data corruption or incorrect system behavior. In
integrity-sensitive contexts, failing to signal that an operation did
not occur as expected can mask errors that disrupt data
consistency. Without feedback, the mitigation measures that should
ensure updates have been performed cannot be verified, leaving the
system vulnerable to both accidental and malicious data alterations.
DoS: Resource Consumption (Memory); DoS: Crash, Exit, or Restart
Scope: AvailabilityLikelihood: High
Unhandled discarded operations can lead to resource exhaustion,
triggering system crashes or denial of service. For availability,
consistent feedback is crucial. Without proper notification of
discarded operations, administrators or other authorized entities
might miss early warning signs of resource imbalances. This delayed
detection could allow a DoS condition to develop, compromising the
system's ability to serve legitimate requests and maintain continuous
operations.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Incorporate logging and feedback mechanisms during the
design phase to ensure proper handling of discarded operations.
Effectiveness: High
Note:
Addressing the issue at the design stage prevents
the weakness from manifesting later.
Implementation
Developers should ensure that every critical operation
includes proper logging or error feedback mechanisms.
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can be introduced during the architecture and
design phase when the system does not incorporate proper mechanisms
for error reporting or feedback for discarded operations, such as when
handling reserved addresses or unexecuted instructions.
Implementation
It can also arise during implementation if developers fail to
include appropriate feedback or logging for critical operations. This
leads to silent failures in certain scenarios like interrupt handling
or network buffer overflows.
Requirements
A further layer of complexity emerges when considering
specifications. The weakness may stem either from ambiguous product
design specifications that fail to delineate when feedback should
occur or from implementations that do not adhere to existing
requirements. In either case, the result is the same: feedback that is
critical for detecting operational failures or security breaches is
missing.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
C
(Undetermined Prevalence)
C++
(Undetermined Prevalence)
Verilog
(Undetermined Prevalence)
Class: Hardware Description Language
(Undetermined Prevalence)
Class: Not Language-Specific
(Undetermined Prevalence)
This code creates an interrupt handler. If the interrupt's priority
is lower than the currently active one, the interrupt is discarded
without any feedback, perhaps due to resource constraints.
(bad code)
Example Language: C
void interrupt_handler(int irq) {
if (irq_priority[irq] < current_priority) {
return;
}
process_interrupt(irq);
}
The omission of feedback for the dropped lower-priority interrupt can
cause developers to misinterpret the state of the system, leading to
incorrect assumptions and potential system failures, such as missed
sensor readings.
Attackers might leverage this lack of visibility to induce conditions
that lead to timing side-channels. For example, an attacker could
intentionally flood the system with high-priority interrupts, forcing
the system to discard lower-priority interrupts consistently. If these
discarded interrupts correspond to processes executing critical
security functions (e.g., cryptographic key handling), an attacker
might measure system timing variations to infer when and how those
functions are executing. This creates a timing side channel that could
be used to extract sensitive information. Moreover, since these
lower-priority interrupts are not reported, the system remains unaware
that critical tasks such as sensor data collection or maintenance
routines, are being starved of execution. Over time, this can lead to
functional failures or watchdog time resets in real-time systems.
One way to address this problem could be to use structured logging to
provide visibility into discarded interrupts. This allows
administrators, developers, or other authorized entities to track
missed interrupts and optimize the system.
(good code)
Example Language: C
// Priority threshold for active interrupts
int current_priority = 3;
// Simulated priority levels for different IRQs
int irq_priority[5] = {1, 2, 3, 4, 5};
void process_interrupt(int irq) {
printf("Processing interrupt %d\n", irq);
}
void interrupt_handler(int irq) {
if (irq_priority[irq] < current_priority) {
// Log the dropped interrupt using structured feedback
fprintf(stderr, "Warning: Interrupt %d dropped (Priority: %d < Current: %d)\n",
irq, irq_priority[irq], current_priority);
exit(EXIT_FAILURE); // Exit with failure status to indicate a critical issue.
}
process_interrupt(irq);
}
Example 2
Consider a SoC design with these component IPs:
IP 1. Execution Core <--> IP 2 SoC Fabric (NoC, tile etc. ) <--> IP 3 Memory Controller <--> External/ internal memory.
The Core executes operations that trigger transactions that traverse
the HW fabric links to read/write to the final memory module.
There can be unexpected errors in each link. For adding reliability
and redundancy, features like ECCs are used in these
transactions. Error correction capabilities have to define how many
error bits can be detected and which errors can be corrected, and
which are uncorrectable errors. In design, often the severity level
and response on different errors is allowed to be configured by system
firmware modules like BIOS.
(bad code)
Example Language: Other
If an uncorrectable error occurs, the design does not explicitly
trigger an alert back to the execution core.
For system security, if an uncorrectable error occurs but is not
reported to the execution core and handled before the core attempts to
consume the data that is read/written through the corrupted
transactions, then this could enable silent data corruption (SDC)
attacks.
In the case of confidential compute technologies where system firmware
is not a trusted component, error handling controls can be
misconfigured to trigger this weakness and attack the assets protected
by confidential compute.
(good code)
Example Language: Other
Modify the design so that any uncorrectable error triggers an alert
back to the execution core and gets handled before the core can
consume the data read/written through the corrupted transactions.
Update design access control policies to ensure that alerts sent to
execution core on uncorrectable errors cannot be disabled or masked by
untrusted software/firmware.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Open source silicon root of trust (RoT) product does not immediately report when an integrity check fails for memory requests, causing the product to accept and continue processing data [REF-1468]
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis - Source Code
Scans code for missing error handling or feedback mechanisms.
Effectiveness: High
Note:
This identifies common issues early in the development phase.
Manual Static Analysis - Source Code
Experts manually inspect the code for unhandled operations.
Effectiveness: Moderate
Note:
Useful for identifying design-level omissions.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1302: Missing Source Identifier in Entity Transactions on a System-On-Chip (SOC)
Weakness ID: 1302
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product implements a security identifier mechanism to differentiate what actions are allowed or disallowed when a transaction originates from an entity, but the entity does not consistently include the necessary Security Identifier with a security-critical transaction.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Crash, Exit, or Restart; Bypass Protection Mechanism; Gain Privileges or Assume Identity; Execute Unauthorized Code or Commands
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
If the Security Identifier is missing, the destination agent might drop the message (resulting in an inadvertent Denial-of-Service (DoS)) or take inappropriate action by default in its attempt to execute the transaction, resulting in privilege escalation or provision of unintended access.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Transaction details must be reviewed for design inconsistency and common weaknesses.
Implementation
Security identifier definition and programming flow must be tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
In a System-On-Chip (SoC), various integrated circuits and hardware engines generate transactions such as to access (reads/writes) assets or perform certain actions (e.g., reset, fetch, compute). A typical transaction is comprised of source identity (to identify the originator of the transaction) and a destination identity (to route the transaction to the respective entity) in addition to much more information in the message. Sometimes the transactions are qualified with a Security Identifier. This Security Identifier helps the destination agent decide on the set of allowed or disallowed actions.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a system with a register for storing AES key for encryption or decryption. The key is of 128 bits implemented as a set of four 32-bit registers. The key registers are assets, and the register AES_KEY_ACCESS_POLICY is defined to provide the necessary access controls.
The access-policy register defines which agents with a security identifier in the transaction can access the AES-key registers. Each bit in this 32-bit register defines a security identifier. There could be a maximum of 32 security identifiers that are allowed accesses to the AES-key registers. The number of the bit when set (i.e., "1") allows for a respective action from an agent whose identity matches the number of the bit; if set to "0" (i.e., Clear), it disallows the respective action to that corresponding agent.
(bad code)
Example Language: Other
Register
Field description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_4
AES key [96:127] for encryption or decryption, Default 0x00000000
AES_KEY_ACCESS_POLICY
[31:0] Default 0x00000004 - agent with Security Identifier "2" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_4 registers
The originator sends a transaction with no security identifier, i.e., meaning the value is "0" or NULL. The AES-Key-access register does not allow the necessary action and drops the transaction because the originator failed to include the required security identifier.
(good code)
Example Language: Other
Register
Field description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_4
AES key [96:127] for encryption or decryption, Default 0x00000000
AES_KEY_ACCESS_POLICY
[31:0] Default 0x00000002 - agent with security identifier "2" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_4 registers
The originator should send a transaction with Security Identifier "2" which will allow access to the AES-Key-access register and allow encryption and decryption operations.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1318: Missing Support for Security Features in On-chip Fabrics or Buses
Weakness ID: 1318
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
On-chip fabrics or buses either do not support or are not configured to support privilege separation or other security features, such as access control.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Property
Missing
Behavior-Type
Support
Other
Security Features
Technology
Fabrics or Buses
Other
On-chip
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Crash, Exit, or Restart; Read Memory; Modify Memory
Scope: Confidentiality, Integrity, Access Control, AvailabilityLikelihood: Medium
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Such fabrics or buses should not be used to transport any security attribute coming from the bus master. In general, peripherals with security assets should not be connected to such buses before the transaction from the bus master reaches the bus, unless some form of access control is performed at a fabric bridge or another intermediate module.
If the fabric does not support security features, implement security checks in a bridge or any component that is between the master and the fabric. Alternatively, connect all fabric slaves that do not have any security assets under one such fabric and connect peripherals with security assets to a different fabric that supports security features.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Certain on-chip fabrics and buses, especially simple and low-power buses, do not support security features. Apart from data transfer and addressing ports, some fabrics and buses do not have any interfaces to transfer privilege, immutable identity, or any other security attribute coming from the bus master. Similarly, they do not have dedicated signals to transport security-sensitive data from slave to master, such as completions for certain types of transactions. Few other on-chip fabrics and buses support security features and define specific interfaces/signals for transporting security attributes from master to slave or vice-versa. However, including these signals is not mandatory and could be left unconfigured when generating the register-transfer-level (RTL) description for the fabric.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Several systems on chips (SoCs) use the Advanced-Microcontroller Bus Architecture (AMBA) Advanced-Peripheral Bus (APB) protocol. APB is a simple, low-power bus and uses the PPROT[2:0] bits to indicate the security state of the bus masters ;PPROT[0] indicates privilege, PPROT[1] indicates secure/non-secure transaction, and PPROT[2] indicates instruction/data. Assume that there is no fabric bridge in the SoC. One of the slaves, the power-management unit, contains registers that store the thermal-shutdown limits.
The APB bus is used to connect several bus masters, each with a unique and immutable hardware identity, to several slaves. For a CPU supporting 8 potential identities (each with varying privilege levels), 16 types of outgoing transactions can be made--8 read transactions with each supported privilege level and 8 write transactions with each supported privilege level.
Since APB PPROT can only support up to 8 transaction types, access-control checks cannot be performed on transactions going to the slaves at the right granularity for all possible transaction types. Thus, potentially, user code running on the CPU could maliciously corrupt the thermal-shutdown-configuration registers to burn the device, resulting in permanent denial of service.
In this scenario, only peripherals that need access protection from 8 of the 16 possible transaction types can be connected to the APB bus. Peripherals that require protection from the remaining 8 transaction types can be connected to a different APB bus. Alternatively, a bridge could be implemented to handle such complex scenarios before forwarding traffic to the APB bus.
Example 2
The Open-Core-Protocol (OCP) fabric supports two configurable, width-optional signals for transporting security attributes: MReqInfo and SRespInfo. MReqInfo is used to transport security attributes from bus master to slave, and SRespInfo is used to transport security attributes from slave to bus master. An SoC uses OCP to connect several bus masters, each with a unique and immutable hardware identity, to several slaves. One of the bus masters, the CPU, reports the privilege level (user or superuser) in addition to the unique identity. One of the slaves, the power-management unit, contains registers that store the thermal-shutdown limits.
Since MReqInfo and SRespInfo are not mandatory, these signals are not configured when autogenerating RTL for the OCP fabric. Thus, the fabric cannot be used to transport security attributes from bus masters to slave.
Code running at user-privilege level on the CPU could maliciously corrupt the thermal-shutdown-configuration registers to burn the device and cause permanent denial of service.
To address this, configure the fabric to include MReqInfo and SRespInfo signals and use these to transport security identity and privilege level to perform access-control checks at the slave interface.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Review the fabric specification and ensure that it contains signals to transfer security-sensitive signals.
Effectiveness: High
Manual Static Analysis - Source Code
Lack of security features can also be confirmed through manual RTL review of the fabric RTL.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1314: Missing Write Protection for Parametric Data Values
Weakness ID: 1314
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device does not write-protect the parametric data values for sensors that scale the sensor value, allowing untrusted software to manipulate the apparent result and potentially damage hardware or cause operational failure.
Extended Description
The limit values are generally programmed in standard units for the type of value being read. However, the hardware-sensor blocks may report the settings in different units depending upon sensor design and operation. The raw sensor output value is converted to the desired units using a scale conversion based on the parametric data programmed into the sensor. The final converted value is then compared with the previously programmed limits.
While the limit values are usually protected, the sensor parametric data values may not be. By changing the parametric data, safe operational limits may be bypassed.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Sensor value manipulation, particularly thermal or power, may allow physical damage to occur or disabling of the device by a false fault shutdown causing a Denial-Of-Service.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Access controls for sensor blocks should ensure that only trusted software is allowed to change threshold limits and sensor parametric data.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Protection Mechanism for Alternate Hardware Interface
Background Details
Various sensors are used by hardware to detect any devices operating outside of the design limits. The threshold limit values are set by hardware fuses or trusted software such as the BIOS. These limits may be related to thermal, power, voltage, current, and frequency. Hardware mechanisms may be used to protect against alteration of the threshold limit values by untrusted software.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
The lack of a requirement to protect parametric values may contribute to this weakness.
Implementation
The lack of parametric value protection may be a cause of this weakness.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Sensor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Malicious software executes instructions to increase power consumption to the highest possible level while causing the clock frequency to increase to its maximum value.
Such a program executing for an extended period of time would likely overheat the device, possibly resulting in permanent damage to the device.
A ring, oscillator-based temperature sensor will generally report the sensed value as
oscillator frequency rather than degrees centigrade. The temperature sensor will have
calibration values that are used to convert the detected frequency into the corresponding temperature in degrees centigrade.
Consider a SoC design where the critical maximum temperature limit is set in fuse values to 100C and
is not modifiable by software. If the scaled thermal sensor output equals or exceeds this limit, the system is commanded to shut itself down.
The thermal sensor calibration values are programmable through registers that are exposed to system software.
These registers allow software to affect the converted temperature output such that the output will never exceed the maximum temperature limit.
(bad code)
Example Language: Other
The sensor frequency value is scaled by applying the function:
Sensed Temp = a + b * Sensor Freq
where a and b are the programmable calibration data coefficients. Software sets a and b to zero ensuring the sensed
temperature is always zero.
This weakness may be addressed by preventing access to a and b.
(good code)
Example Language: Other
The sensor frequency value is scaled by applying the function:
Sensed Temp = a + b * Sensor Freq
where a and b are the programmable calibration data coefficients. Untrusted software is prevented from changing the values of either a or b,
preventing this method of manipulating the temperature.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Kernel can inject faults in computations during the execution of TrustZone leading to information disclosure in Snapdragon Auto, Snapdragon Compute, Snapdragon Connectivity, Snapdragon Consumer Electronics Connectivity, Snapdragon Consumer IOT, Snapdragon Industrial IOT, Snapdragon IoT, Snapdragon Mobile, Snapdragon Voice and Music, Snapdragon Wearables, Snapdragon Wired Infrastructure and Networking.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1283: Mutable Attestation or Measurement Reporting Data
Weakness ID: 1283
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The register contents used for attestation or measurement reporting data to verify boot flow are modifiable by an adversary.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Modify Application Data
Scope: Integrity
An adversary could spoof the measurement.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Measurement data should be stored in registers that are read-only or otherwise have access controls that prevent modification by an untrusted agent.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
A System-on-Chip (SoC) implements secure boot or verified boot. During this boot flow, the SoC often measures the code that it authenticates. The measurement is usually done by calculating the one-way hash of the code binary and extending it to the previous hash. The hashing algorithm should be a Secure One-Way hash function. The final hash, i.e., the value obtained after the completion of the boot flow, serves as the measurement data used in reporting or in attestation. The calculated hash is often stored in registers that can later be read by the party of interest to determine tampering of the boot flow.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues can be introduced during hardware architecture or design and can be identified later during Testing or System Configuration phases.
Implementation
If the access-controls which protecting the reporting registers are misconfigured during implementation, this weakness can arise.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The SoC extends the hash and stores the results in registers. Without protection, an adversary can write their chosen hash values to these registers. Thus, the attacker controls the reported results.
To prevent the above scenario, the registers should have one or more of the following properties:
Should be Read-Only with respect to an adversary
Cannot be extended or modifiable either directly or indirectly (using a trusted agent as proxy) by an adversary
Should have appropriate access controls or protections
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still in development and will continue to see updates and content improvements.
CWE-1303: Non-Transparent Sharing of Microarchitectural Resources
Weakness ID: 1303
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Hardware structures shared across execution contexts (e.g., caches and branch predictors) can violate the expected architecture isolation between contexts.
Extended Description
Modern processors use techniques such as out-of-order execution, speculation, prefetching, data forwarding, and caching to increase performance. Details about the implementation of these techniques are hidden from the programmer's view. This is problematic when the hardware implementation of these techniques results in resources being shared across supposedly isolated contexts. Contention for shared resources between different contexts opens covert channels that allow malicious programs executing in one context to recover information from another context.
Some examples of shared micro-architectural resources that have been used to leak information between contexts are caches, branch prediction logic, and load or store buffers. Speculative and out-of-order execution provides an attacker with increased control over which data is leaked through the covert channel.
If the extent of resource sharing between contexts in the design microarchitecture is undocumented, it is extremely difficult to ensure system assets are protected against disclosure.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data; Read Memory
Scope: Confidentiality
Microarchitectural side-channels have been used to leak specific information such as cryptographic keys, and Address Space Layout Randomization (ALSR) offsets as well as arbitrary memory.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Microarchitectural covert channels can be addressed using a mixture of hardware and software mitigation techniques. These include partitioned caches, new barrier and flush instructions, and disabling high resolution performance counters and timers.
Requirements
Microarchitectural covert channels can be addressed using a mixture of hardware and software mitigation techniques. These include partitioned caches, new barrier and flush instructions, and disabling high resolution performance counters and timers.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
On some processors the hardware indirect branch predictor is shared between execution contexts, for example, between sibling SMT threads. When SMT thread A executes an indirect branch to a target address X, this target may be temporarily stored by the indirect branch predictor. A subsequent indirect branch mis-prediction for SMT thread B could speculatively execute instructions at X (or at a location in B's address space that partially aliases X). Even though the processor rolls back the architectural effects of the mis-predicted indirect branch, the memory accesses alter data cache state, which is not rolled back after the indirect branch is resolved.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Violation of Secure Design Principles
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.9, members of the CWE Hardware SIG are closely analyzing this entry and others to improve CWE's coverage of transient execution weaknesses, which include issues related to Spectre, Meltdown, and other attacks. Additional investigation may include other weaknesses related to microarchitectural state. Finally, this entry's demonstrative example might not be appropriate. As a result, this entry might change significantly in CWE 4.10.
Moritz Lipp, Michael Schwarz, Daniel Gruss, Thomas Prescher, Werner Haas, Anders Fogh, Jann Horn, Stegfan Mangard, Paul Kocher, Daniel Genkin, Yuval Yarom and Mike Hamberg. "Meltdown: Reading Kernel Memory from User Space". 2018-01-03.
<https://meltdownattack.com/meltdown.pdf>.
[REF-1122]
Moritz Lipp, Michael Schwarz, Daniel Gruss, Thomas Prescher, Werner Haas, Anders Fogh, Jann Horn, Stegfan Mangard, Paul Kocher, Daniel Genkin, Yuval Yarom and Mike Hamberg. "Spectre Attacks: Exploiting Speculative Execution". 2018-01-03.
<https://spectreattack.com/spectre.pdf>.
Qian Ge, Yuval Yarom, David Cock and Gernot Heiser. "A Survey of Microarchitectural Timing Attacks and Countermeasures on Contemporary Hardware". 2016-10-24.
<https://eprint.iacr.org/2016/613.pdf>.
Content
History
Submissions
Submission Date
Submitter
Organization
2020-05-08
(CWE 4.2, 2020-08-20)
Nicole Fern
Cycuity (originally submitted as Tortuga Logic)
Contributions
Contribution Date
Contributor
Organization
2026-04-16
(CWE 5.0, 2026-10-28)
Jason Oberg
Arteris
Suggested additional HW relationships to help
distinguish between different HW CWEs, and/or expose the user to
alternatives.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product behaves differently or sends different responses under different circumstances in a way that is observable to an unauthorized actor.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Property
Discrepancy
Behavior-Property
Observable
Alternate Terms
Side Channel Attack
Observable Discrepancies are at the root of side channel attacks.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
An attacker can gain access to sensitive information about the system, including authentication information that may allow an attacker to gain access to the system. Other security-relevant information about the operation or internal state of the product may be revealed to an unauthorized actor, such as whether a particular operation was successful or not.
Read Application Data
Scope: Confidentiality
In some cases, discrepancies can be used by attackers to form a side channel. When cryptographic primitives are vulnerable to side-channel attacks, this could be used to reveal unencrypted plaintext in the worst case.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Strategy: Separation of Privilege
Compartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area.
Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.
Implementation
Ensure that error messages only contain minimal details that are useful to the intended audience and no one else. The messages need to strike the balance between being too cryptic (which can confuse users) or being too detailed (which may reveal more than intended). The messages should not reveal the methods that were used to determine the error. Attackers can use detailed information to refine or optimize their original attack, thereby increasing their chances of success.
If errors must be captured in some detail, record them in log messages, but consider what could occur if the log messages can be viewed by attackers. Highly sensitive information such as passwords should never be saved to log files.
Avoid inconsistent messaging that might accidentally tip off an attacker about internal state, such as whether a user account exists or not.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Exposure of Sensitive Information to an Unauthorized Actor
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Non-Transparent Sharing of Microarchitectural Resources
Relevant to the view "Weaknesses for Simplified Mapping of Published Vulnerabilities" (View-1003)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Discrepancies may be observable based on timing, control flow, communications (such as replies or requests), or general behavior.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following code checks validity of the supplied username and password and notifies the user of a successful or failed login.
(bad code)
Example Language: Perl
my $username=param('username');
my $password=param('password');
if (IsValidUsername($username) == 1)
{
if (IsValidPassword($username, $password) == 1)
{
print "Login Successful";
}
else
{
print "Login Failed - incorrect password";
}
}
else
{
print "Login Failed - unknown username";
}
In the above code, there are different messages for when an incorrect username is supplied, versus when the username is correct but the password is wrong. This difference enables a potential attacker to understand the state of the login function, and could allow an attacker to discover a valid username by trying different values until the incorrect password message is returned. In essence, this makes it easier for an attacker to obtain half of the necessary authentication credentials.
While this type of information may be helpful to a user, it is also useful to a potential attacker. In the above example, the message for both failed cases should be the same, such as:
(result)
"Login Failed - incorrect username or password"
Example 2
In this example, the attacker observes how long an authentication takes when the user types in the correct password.
When the attacker tries their own values, they can first try strings of various length. When they find a string of the right length, the computation will take a bit longer, because the for loop will run at least once. Additionally, with this code, the attacker can possibly learn one character of the password at a time, because when they guess the first character right, the computation will take longer than a wrong guesses. Such an attack can break even the most sophisticated password with a few hundred guesses.
(bad code)
Example Language: Python
def validate_password(actual_pw, typed_pw):
if len(actual_pw) <> len(typed_pw):
return 0
for i in len(actual_pw):
if actual_pw[i] <> typed_pw[i]:
return 0
return 1
Note that in this example, the actual password must be handled in constant time as far as the attacker is concerned, even if the actual password is of an unusual length. This is one reason why it is good to use an algorithm that, among other things, stores a seeded cryptographic one-way hash of the password, then compare the hashes, which will always be of the same length.
Example 3
Non-uniform processing time causes a timing channel.
(bad code)
Example Language: Algorithm
Suppose an algorithm for implementing an encryption routine works fine per se, but the time taken to output the result of the encryption routine depends on a relationship between the input plaintext and the key (e.g., suppose, if the plaintext is similar to the key, it would run very fast).
In the example above, an attacker may vary the inputs, then observe differences between processing times (since different plaintexts take different time). This could be used to infer information about the key.
(good code)
Example Language: Algorithm
Artificial delays may be added to ensure that all calculations take equal time to execute.
Example 4
Suppose memory access patterns for an encryption routine are dependent on the secret key.
An attacker can recover the key by knowing if specific memory locations have been accessed or not. The value stored at those memory locations is irrelevant. The encryption routine's memory accesses will affect the state of the processor cache. If cache resources are shared across contexts, after the encryption routine completes, an attacker in different execution context can discover which memory locations the routine accessed by measuring the time it takes for their own memory accesses to complete.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Crypto hardware wallet's power consumption relates to total number of pixels illuminated, creating a side channel in the USB connection that allows attackers to determine secrets displayed such as PIN numbers and passwords
Bulletin Board displays different error messages when a user exists or not, which makes it easier for remote attackers to identify valid users and conduct a brute force password guessing attack.
Operating System, when direct remote login is disabled, displays a different message if the password is correct, which allows remote attackers to guess the password via brute force methods.
Product sets a different TTL when a port is being filtered than when it is not being filtered, which allows remote attackers to identify filtered ports by comparing TTLs.
Version control system allows remote attackers to determine the existence of arbitrary files and directories via the -X command for an alternate history file, which causes different error messages to be returned.
FTP server generates an error message if the user name does not exist instead of prompting for a password, which allows remote attackers to determine valid usernames.
SSL implementation does not perform a MAC computation if an incorrect block cipher padding is used, which causes an information leak (timing discrepancy) that may make it easier to launch cryptographic attacks that rely on distinguishing between padding and MAC verification errors, possibly leading to extraction of the original plaintext, aka the "Vaudenay timing attack."
Virtual machine allows malicious web site operators to determine the existence of files on the client by measuring delays in the execution of the getSystemResource method.
Product uses a shorter timeout for a non-existent user than a valid user, which makes it easier for remote attackers to guess usernames and conduct brute force password guessing.
FTP server responds in a different amount of time when a given username exists, which allows remote attackers to identify valid usernames by timing the server response.
Browser allows remote attackers to determine the existence of arbitrary files by setting the src property to the target filename and using Javascript to determine if the web page immediately stops loading, which indicates whether the file exists or not.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
OWASP Top Ten 2004 Category A7 - Improper Error Handling
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Comprehensive Categorization: Sensitive Information Exposure
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1191: On-Chip Debug and Test Interface With Improper Access Control
Weakness ID: 1191
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The chip does not implement or does not correctly perform access control to check whether users are authorized to access internal registers and test modes through the physical debug/test interface.
Extended Description
If authorization, authentication, or some other form of access control is not implemented or not implemented correctly, a user may be able to bypass on-chip protection mechanisms through the debug interface.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Access Control
Behavior-Property
Improper
Technology
On-Chip Debug and Test Interface
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data
Scope: ConfidentialityLikelihood: High
Read Memory
Scope: ConfidentialityLikelihood: High
Execute Unauthorized Code or Commands
Scope: AuthorizationLikelihood: High
Modify Memory
Scope: IntegrityLikelihood: High
Modify Application Data
Scope: IntegrityLikelihood: High
Bypass Protection Mechanism
Scope: Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Strategy: Separation of Privilege
If feasible, the manufacturer should disable the JTAG interface or implement authentication and authorization for the JTAG interface. If authentication logic is added, it should be resistant to timing attacks. Security-sensitive data stored in registers, such as keys, etc. should be cleared when entering debug mode.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Missing Protection Mechanism for Alternate Hardware Interface
Background Details
A device's internal information may be accessed through a scan chain of interconnected internal registers, usually through a JTAG interface. The JTAG interface provides access to these registers in a serial fashion in the form of a scan chain for the purposes of debugging programs running on a device. Since almost all information contained within a device may be accessed over this interface, device manufacturers typically insert some form of authentication and authorization to prevent unintended use of this sensitive information. This mechanism is implemented in addition to on-chip protections that are already present.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Sometimes, designers choose not to expose the debug pins on the motherboard. Instead, they choose to hide these pins in the intermediate layers of the board. This is primarily done to work around the lack of debug authorization inside the chip. In such a scenario (without debug authorization), when the debug interface is exposed, chip internals are accessible to an attacker.
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A home, WiFi-router device implements a login prompt which prevents an unauthorized user from issuing any commands on the device until appropriate credentials are provided. The credentials are protected on the device and are checked for strength against attack.
(bad code)
Example Language: Other
If the JTAG interface on this device is not hidden by the manufacturer, the interface may be identified using tools such as JTAGulator. If it is hidden but not disabled, it can be exposed by physically wiring to the board.
By issuing a "halt" command before the OS starts, the unauthorized user pauses the watchdog timer and prevents the router from restarting (once the watchdog timer would have expired). Having paused the router, an unauthorized user is able to execute code and inspect and modify data in the device, even extracting all of the router's firmware. This allows the user to examine the router and potentially exploit it.
JTAG is useful to chip and device manufacturers during design, testing, and production and is included in nearly every product. Without proper authentication and authorization, the interface may allow tampering with a product.
(good code)
Example Language: Other
In order to prevent exposing the debugging interface, manufacturers might try to obfuscate the JTAG interface or blow device internal fuses to disable the JTAG interface. Adding authentication and authorization to this interface makes use by unauthorized individuals much more difficult.
Example 2
The following example code is a snippet from the JTAG wrapper module in the RISC-V debug module of the HACK@DAC'21 Openpiton SoC [REF-1355]. To make sure that the JTAG is accessed securely, the developers have included a primary authentication mechanism based on a password.
The developers employed a Finite State Machine (FSM) to implement this authentication. When a user intends to read from or write to the JTAG module, they must input a password.
In the subsequent state of the FSM module, the entered password undergoes Hash-based Message Authentication Code (HMAC) calculation using an internal HMAC submodule. Once the HMAC for the entered password is computed by the HMAC submodule, the FSM transitions to the next state, where it compares the computed HMAC with the expected HMAC for the password.
If the computed HMAC matches the expected HMAC, the FSM grants the user permission to perform read or write operations on the JTAG module. [REF-1352]
(bad code)
Example Language: SystemVerilog
...
PassChkValid: begin
if(hashValid) begin
if(exp_hash == pass_hash) begin
pass_check = 1'b1;
end else begin
pass_check = 1'b0;
end
state_d = Idle;
end else begin
state_d = PassChkValid;
end
end
...
However, in the given vulnerable part of the code, the JTAG module has not defined a limitation for several continuous wrong password attempts. This omission poses a significant security risk, allowing attackers to carry out brute-force attacks without restrictions.
Without a limitation on wrong password attempts, an attacker can repeatedly guess different passwords until they gain unauthorized access to the JTAG module. This leads to various malicious activities, such as unauthorized read from or write to debug module interface.
To mitigate the mentioned vulnerability, developers need to implement a restriction on the number of consecutive incorrect password attempts allowed by the JTAG module, which can achieve by incorporating a mechanism that temporarily locks the module after a certain number of failed attempts.[REF-1353][REF-1354]
(good code)
Example Language: SystemVerilog
...
case (state_q)
Idle: begin
...
else if ( (dm::dtm_op_e'(dmi.op) == dm::DTM_PASS) && (miss_pass_check_cnt_q != 2'b11) )
begin
The example code below is taken from the JTAG access control mechanism of the HACK@DAC'21 buggy OpenPiton SoC [REF-1364]. Access to JTAG allows users to access sensitive information in the system. Hence, access to JTAG is controlled using cryptographic authentication of the users. In this example (see the vulnerable code source), the password checker uses HMAC-SHA256 for authentication. It takes a 512-bit secret message from the user, hashes it using HMAC, and compares its output with the expected output to determine the authenticity of the user.
The vulnerable code shows an incorrect implementation of the HMAC authentication where it only uses the least significant 32 bits of the secret message for the authentication (the remaining 480 bits are hard coded as zeros). As a result, the system is susceptible to brute-force attacks on the access control mechanism of JTAG, where the attacker only needs to determine 32 bits of the secret message instead of 512 bits.
To mitigate this issue, remove the zero padding and use all 512 bits of the secret message for HMAC authentication [REF-1365].
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: JTAG interface is not disabled (CWE-1191) during ROM code execution, introducing a race condition (CWE-362) to extract encryption keys
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Dynamic Analysis with Manual Results Interpretation
Authentication and authorization of debug and test interfaces should be part of the architecture and design review process. Withholding of private register documentation from the debug and test interface public specification ("Security by obscurity") should not be considered as sufficient security.
Dynamic Analysis with Manual Results Interpretation
Dynamic tests should be done in the pre-silicon and post-silicon stages to verify that the debug and test interfaces are not open by default.
Fuzzing
Tests that fuzz Debug and Test Interfaces should ensure that no access without appropriate authentication and authorization is possible.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Relationship
CWE-1191 and CWE-1244 both involve physical debug access,
but the weaknesses are different. CWE-1191 is effectively
about missing authorization for a debug interface,
i.e. JTAG. CWE-1244 is about providing internal assets with
the wrong debug access level, exposing the asset to
untrusted debug agents.
Gopal Vishwakarma and Wonjun Lee. "Exploiting JTAG and Its Mitigation in IOT: A Survey". 2018-12-03.
<https://www.mdpi.com/1999-5903/10/12/121/pdf>.
(URL validated: 2023-04-07)
[REF-1084]
Gopal Vishwakarma and Wonjun Lee. "JTAG Explained (finally!): Why "IoT", Software Security Engineers, and Manufacturers Should Care". <https://www.mdpi.com/1999-5903/10/12/121/pdf>.
(URL validated: 2023-04-07)
CWE Grouping: Peripherals, On-chip Fabric, and Interface/IO Problems
Grouping ID: 1203
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to hardware
security problems that apply to peripheral devices, IO
interfaces, on-chip interconnects, network-on-chip (NoC),
and buses. For example, this category includes issues
related to design of hardware interconnect and/or protocols
such as PCIe, USB, SMBUS, general-purpose IO pins, and
user-input peripherals such as mouse and keyboard.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to concerns of physical access.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1268: Policy Privileges are not Assigned Consistently Between Control and Data Agents
Weakness ID: 1268
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product's hardware-enforced access control for a particular resource improperly accounts for privilege discrepancies between control and write policies.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; DoS: Crash, Exit, or Restart; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Read Files or Directories; Reduce Reliability
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
Resources that include agents in their control policy but not in their write policy could unintentionally allow an untrusted agent to insert itself in the write policy register. Inclusion in the write policy register could allow a malicious or misbehaving agent write access to resources. This action could result in security compromises including leaked information, leaked encryption keys, or modification of device configuration.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Access-control-policy definition and programming flow must be sufficiently tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Integrated circuits and hardware engines may provide access to resources (device-configuration, encryption keys, etc.) belonging to trusted firmware or software modules (commonly set by a BIOS or a bootloader). These accesses are typically controlled and limited by the hardware.
Hardware design access control is sometimes implemented using a policy. A policy defines which entity or agent may or may not be allowed to perform an action. When a system implements multiple levels of policies, a control policy may allow direct access to a resource as well as changes to the policies themselves.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness may be introduced during the design of a device when the architect does not comprehensively specify all of the policies required by an agent.
Implementation
This weakness may be introduced during implementation if device policy restrictions do not sufficiently constrain less-privileged clients.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a product that stores a 128-bit AES key in four 32-bit registers, collectively called the AES key registers.
Three additional 32-bit registers are used to define the hardware enforced access control for the AES key registers. Collectively these registers are referred to as the AES Policy registers, and their functions are explained in the following table:
(informative)
AES Policy Registers
Register
Permission granted
AES_KEY_CONTROL_POLICY
Defines which agents can write to both AES_KEY_READ_POLICY and AES_KEY_WRITE_POLICY registers.
AES_KEY_READ_POLICY
Defines which agents can read the AES key registers.
AES_KEY_WRITE_POLICY
Defines which agents can write the AES key registers.
Each AES policy register uses one bit per agent to specify whether that agent has the permission defined by the register. Bit 0 corresponds to Agent 0, bit 1 to Agent 1, and so on. A value of 1 grants permission; 0 denies it. For example, setting bit 0 of AES_KEY_READ_POLICY to 1 allows Agent 0 to read the AES key registers.
The following initial configuration for the AES policy registers illustrates these permissions for four agents, numbered 0 through 3. The table shows only bits 3 through 0, with bit 0 on the right. All higher bits are 0.
(bad code)
Example Language: Other
Register
Initial value (hexadecimal)
Bits 3 2 1 0 (binary)
Agents granted permission
AES_KEY_READ_POLICY
0x00000001
0001b
Agent 0
AES_KEY_WRITE_POLICY
0x00000002
0010b
Agent 1
AES_KEY_CONTROL_POLICY
0x0000000C
1100b
Agents 2 and 3
Agents 0, 1, and 3 are trusted. Agent 2 is untrusted and should not have access to the AES key or its access policies. The initial values of the three AES policy registers shown above result in the permissions summarized below.
(informative)
Agent
Read AES key
Write AES key
Modify AES key access policies
Agent 0
Allowed
Not Allowed
Not Allowed
Agent 1
Not Allowed
Allowed
Not Allowed
Agent 2 (untrusted)
Not Allowed
Not Allowed
Allowed
Agent 3
Not Allowed
Not Allowed
Allowed
The initial configuration denies untrusted Agent 2 direct access to the AES key but allows it to modify the policies that enforce this restriction.
For example, Agent 2 can change AES_KEY_WRITE_POLICY from its initial value of 0x00000002 (0010b) to 0x00000006 (0110b). This sets bit 2 while preserving bit 1, granting Agent 2 write access to the AES key registers while retaining Agent 1’s write access.
To prevent this, grant permission to modify the access policies only to agents trusted to manage access to the key. Setting the initial value of AES_KEY_CONTROL_POLICY to 0x00000008 (1000b) allows only trusted Agent 3 to write to AES_KEY_READ_POLICY and AES_KEY_WRITE_POLICY. Untrusted Agent 2 can no longer modify either policy to grant itself access to the AES key registers. The initial policy register values should therefore be as follows:
(good code)
Example Language: Other
Register
Initial value (hexadecimal)
Bits 3 2 1 0 (binary)
Agents granted permission
AES_KEY_READ_POLICY
0x00000001
0001b
Agent 0
AES_KEY_WRITE_POLICY
0x00000002
0010b
Agent 1
AES_KEY_CONTROL_POLICY
0x00000008
1000b
Agent 3
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses an encoding mechanism that is no longer trusted, i.e., an obsolete encoding, to implement access controls.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory; Modify Files or Directories; Read Files or Directories; DoS: Resource Consumption (Other); Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Bypass Protection Mechanism; Reduce Reliability
Scope: Confidentiality, Integrity, Availability, Access ControlLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Security Token Decoders should be reviewed for design inconsistency and common weaknesses.
Access and programming flows should be tested in both pre-silicon and post-silicon testing.
Effectiveness: High
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Within a System-On-a-Chip (SoC), various circuits and hardware engines generate transactions for the purpose of accessing (read/write) assets or performing various actions (e.g., reset, fetch, compute, etc.). Among various types of message information, a typical transaction is comprised of source identity (identifying the originator of the transaction) and a destination identity (routing the transaction to the respective entity). Sometimes the transactions are qualified with a Security Token. This Security Token helps the destination agent decide on the set of allowed actions (e.g., access to an asset for reads and writes).
A policy encoder is used to map the bus transactions to Security Tokens that in turn are used as access-controls/protection mechanisms.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
For example, consider a system that has four bus masters. The table below provides bus masters, their Security Tokens, and trust assumptions.
Bus Master
Security Token Decoding
Trust Assumptions
Master_0
"00"
Untrusted
Master_1
"01"
Trusted
Master_2
"10"
Untrusted
Master_3
"11"
Untrusted
The policy encoding is to be defined such that Security Token will be used in implemented access-controls. The bits in the bus transaction that contain Security-Token information are Bus_transaction [15:11]. The assets are the AES-Key registers for encryption or decryption. The key of 128 bits is implemented as a set of four, 32-bit registers.
Register
Field description
AES_ENC_DEC_KEY_0
AES key [0:31] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_1
AES key [32:63] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_2
AES key [64:95] for encryption or decryption, Default 0x00000000
AES_ENC_DEC_KEY_4
AES key [96:127] for encryption or decryption, Default 0x00000000
Below is an example of a policy encoding scheme inherited from a previous project where all "ODD" numbered Security Tokens are trusted.
(bad code)
Example Language: Pseudocode
If (Bus_transaction[14] == "1")
Trusted = "1"
Else
Trusted = "0"
If (trusted)
Allow access to AES-Key registers
Else
Deny access to AES-Key registers
The inherited policy encoding is obsolete and does not work for the new system where an untrusted bus master with an odd Security Token exists in the system, i.e., Master_3 whose Security Token is "11". Based on the old policy, the untrusted bus master (Master_3) has access to the AES-Key registers. To resolve this, a register AES_KEY_ACCESS_POLICY can be defined to provide necessary, access controls:
New Policy:
AES_KEY_ACCESS_POLICY
[31:0] Default 0x00000002 - agent with Security Token "1" has access to AES_ENC_DEC_KEY_0 through AES_ENC_DEC_KEY_4 registers
The AES_KEY_ACCESS_POLICY register defines which agents with a Security Token in the transaction can access the AES-key registers. Each bit in this 32-bit register defines a Security Token. There could be a maximum of 32 security Tokens that are allowed access to the AES-key registers. The number of the bit when set (i.e., "1") allows respective action from an agent whose identity matches the number of the bit and, if "0" (i.e., Clear), disallows the respective action to that corresponding agent. Thus, any bus master with Security Token "01" is allowed access to the AES-Key registers. Below is the Pseudo Code for policy encoding:
(good code)
Example Language: Pseudocode
Security_Token[4:0] = Bus_transaction[15:11]
If (AES_KEY_ACCESS_POLICY[Security_Token] == "1")
Allow access to AES-Key registers
Else
Deny access to AES-Key registers
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE Grouping: Power, Clock, Thermal, and Reset Concerns
Grouping ID: 1206
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to system power, voltage, current, temperature, clocks, system state saving/restoring, and resets at the platform and SoC level.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1193: Power-On of Untrusted Execution Core Before Enabling Fabric Access Control
Weakness ID: 1193
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product enables components that contain untrusted firmware before memory and fabric access controls have been enabled.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access ControlLikelihood: High
If untrusted IPs or peripheral microcontrollers
are enabled too soon, then the untrusted component can master
transactions on the hardware bus and target memory or other assets to
compromise the SoC boot firmware.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The boot sequence should enable fabric access controls and memory protections before enabling third-party hardware IPs and peripheral microcontrollers that use untrusted firmware.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
After initial reset, System-on-Chip (SoC) fabric access controls and other
security features need to be programmed by trusted firmware as part
of the boot sequence.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Insufficient Control Flow Management
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE Grouping: Privilege Separation and Access Control Issues
Grouping ID: 1198
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to features and mechanisms providing hardware-based isolation and access control (e.g., identity, policy, locking control) of sensitive shared hardware resources such as registers and fuses.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1269: Product Released in Non-Release Configuration
Weakness ID: 1269
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product released to market is released in pre-production or manufacturing configuration.
Technical Nuance
Products in the pre-production or manufacturing stages are configured to have many debug hooks and debug capabilities, including but not limited to:
Ability to override/bypass various cryptographic checks (including authentication, authorization, and integrity)
Ability to read/write/modify/dump internal state (including registers and memory)
Ability to change system configurations
Ability to run hidden or private commands that are not allowed during production (as they expose IP).
The above is by no means an exhaustive list, but it alludes to the greater capability and the greater state of vulnerability of a product during its preproduction or manufacturing state.
Complexity increases when multiple parties are involved in executing the tests before the final production version. For example, a chipmaker might fabricate a chip and run its own preproduction tests, following which the chip would be delivered to the Original Equipment Manufacturer (OEM), who would now run a second set of different preproduction tests on the same chip. Only after both of these sets of activities are complete, can the overall manufacturing phase be called "complete" and have the "Manufacturing Complete" fuse blown. However, if the OEM forgets to blow the Manufacturing Complete fuse, then the system remains in the manufacturing stage, rendering the system both exposed and vulnerable.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Ensure that there exists a marker for denoting the Manufacturing Complete stage and that the Manufacturing Complete marker gets updated at the Manufacturing Complete stage (i.e., the Manufacturing Complete fuse gets blown).
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Integration
Manufacturing
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
VHDL
(Undetermined Prevalence)
Verilog
(Undetermined Prevalence)
Class: Compiled
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Other
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example shows what happens when a preproduction system is made available for production.
(bad code)
Example Language: Other
Suppose the chipmaker has a way of scanning all the internal memory (containing chipmaker-level secrets) during the manufacturing phase, and the way the chipmaker or the Original Equipment Manufacturer (OEM) marks the end of the manufacturing phase is by blowing a Manufacturing Complete fuse. Now, suppose that whoever blows the Manufacturing Complete fuse inadvertently forgets to execute the step to blow the fuse.
An attacker will now be able to scan all the internal memory (containing chipmaker-level secrets).
(good code)
Example Language: Other
Blow the Manufacturing Complete fuse.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Regarding SSA-686531, a hardware based manufacturing access on S7-1200 and
S7-200 SMART has occurred. A vulnerability has been identified in SIMATIC S7-1200 CPU family (incl. SIPLUS variants) (All versions), SIMATIC S7-200 SMART CPU family (All versions). There is an access mode used during manufacturing of S7-1200 CPUs that allows additional diagnostic functionality. The security vulnerability could be exploited by an attacker with physical access to the UART interface during boot process. At the time of advisory publication, no public exploitation of this security vulnerability was known.
Laptops with Intel chipsets were found to be running in Manufacturing Mode. After this information was reported to the OEM, the vulnerability (CVE-2018-4251) was patched disallowing access to the interface.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1291: Public Key Re-Use for Signing both Debug and Production Code
Weakness ID: 1291
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The same public key is used for signing both debug and production code.
Extended Description
A common usage of public-key cryptography is to verify the integrity and authenticity of another entity (for example a firmware binary). If a company wants to ensure that its firmware runs only on its own hardware, before the firmware runs, an encrypted hash of the firmware image will be decrypted with the public key and then verified against the now-computed hash of the firmware image. This means that the public key forms the root of trust, which necessitates that the public key itself must be protected and used properly.
During the development phase, debug firmware enables many hardware debug hooks, debug modes, and debug messages for testing. Those debug facilities provide significant, additional views about the firmware's capability and, in some cases, additional capability into the chip or SoC. If compromised, these capabilities could be exploited by an attacker to take full control of the system.
Once the product exits the manufacturing stage and enters production, it is good practice to use a different public key. Debug firmware images are known to leak. With the debug key being reused as the production key, the debug image will also work on the production image. Thus, it will open all the internal, debug capabilities to the attacker.
If a different public key is used for the production image, even if the attacker gains access to the debug firmware image, they will not be able to run it on a production machine. Thus, damage will be limited to the intellectual property leakage resulting from the debug image.
Dimensions
The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.
Type
Value
Behavior-Type
Re-Use
Resource-Type
Key
Resource-Property
Public
Behavior-Type
Signing
Code-Type
Code
Code-Property
Debug and Production
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Memory; Modify Memory; Execute Unauthorized Code or Commands; Gain Privileges or Assume Identity; Varies by Context
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example illustrates the danger of using the same public key for debug and production.
(bad code)
Example Language: Other
Suppose the product design requires frugality of silicon real estate. Assume that originally the architecture allows just enough storage for two 2048-bit RSA keys in the fuse: one to be used for debug and the other for production. However, in the meantime, a business decision is taken to make the security future-proof beyond 2030, which means the architecture needs to use the NIST-recommended 3072-bit keys instead of the originally-planned 2048-bit keys. This means that, at most, one key can be fully stored in the fuses, not two. So the product design team decides to use the same public key for debug and production.
(informative)
Example Language: Other
Increase the storage so that two different keys of the required size can be stored.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Compare the debug key with the production key to make sure that they are not the same.
Effectiveness: High
Dynamic Analysis with Manual Results Interpretation
Compare the debug key with the production key to make sure that they are not the same.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1223: Race Condition for Write-Once Attributes
Weakness ID: 1223
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
A write-once register in hardware design is programmable by an untrusted software component earlier than the trusted software component, resulting in a race condition issue.
Extended Description
Implementation issues in hardware design of such controls can expose such registers to a race condition security flaw.
For example, consider a hardware design that has two different software/firmware modules executing in parallel. One module is trusted (module A) and another is untrusted (module B). In this design, it could be possible for Module B to send write cycles to the write-once register before Module A. Since the field is write-once, the programmed value from Module A will be ignored and the pre-empted value programmed by Module B will be used by hardware.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Bypass Protection Mechanism
Scope: Access Control
System configuration cannot be programmed in a secure way.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
During hardware design, all register write-once or sticky fields must be evaluated for proper configuration.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Integrated circuits and hardware IP software programmable controls and settings are commonly stored in register circuits. These register contents have to be initialized at hardware reset to defined default values that are hard coded in the hardware description language (HDL) code of the hardware unit.
To protect register settings from modification by software, a common security protection mechanism is to make them write-once. This means the hardware implementation only allows writing to such registers once, and the registers become read-only after having been written once by software. This is useful to allow initial boot software to configure systems settings to secure values while blocking runtime software from modifying such hardware settings.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness can appear in designs that use register write-once attributes with two or more software/firmware modules with varying levels of trust executing in parallel.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the example design module system Verilog code shown below. register_write_once_example module is an example of register that has a write-once field defined. Bit 0 field captures the write_once_status value.
always @(posedge Clk or negedge ip_resetn)
if (~ip_resetn)
begin
Data_out <= 16'h0000;
Write_once_status <= 1'b0;
end
else if (write & ~Write_once_status)
begin
Data_out <= Data_in & 16'hFFFE; // Input data written to register after masking bit 0
Write_once_status <= 1'b1; // Write once status set after first write.
The first system component that sends a write cycle to this register can program the value. This could result in a race condition security issue in the SoC design, if an untrusted agent is running in the system in parallel with the trusted component that is expected to program the register.
(good code)
Example Language: Other
Trusted firmware or software trying to set the write-once field:
Must confirm the Write_once_status (bit 0) value is zero, before programming register. If another agent has programmed the register before, then Write_once_status value will be one.
After writing to the register, the trusted software can issue a read to confirm that the valid setting has been programmed.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Analysis
The testing phase should use automated tools to test that values are not reprogrammable and that write-once fields lock on writing zeros.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1329: Reliance on Component That is Not Updateable
Weakness ID: 1329
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product contains a component that cannot be updated or patched in order to remove vulnerabilities or significant bugs.
Extended Description
If the component is discovered to contain a vulnerability or critical bug, but the issue cannot be fixed using an update or patch, then the product's owner will not be able to protect against the issue. The only option might be replacement of the product, which could be too financially or operationally expensive for the product owner. As a result, the inability to patch or update can leave the product open to attacker exploitation or critical operation failures. This weakness can be especially difficult to manage when using ROM, firmware, or similar components that traditionally have had limited or no update capabilities.
In industries such as healthcare, "legacy"
devices can be operated for decades. As a
US task force report [REF-1197] notes, "the inability
to update or replace equipment has both
large and small health care delivery
organizations struggle with numerous
unsupported legacy systems that cannot
easily be replaced (hardware, software, and
operating systems) with large numbers of
vulnerabilities and few modern
countermeasures."
While hardware can be prone to this weakness, software systems can also be affected, such as when a third-party driver or library is no longer actively maintained or supported but is still critical for the required functionality.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands; DoS: Crash, Exit, or Restart; Quality Degradation; Reduce Maintainability
Scope: Confidentiality, Integrity, Access Control, Authentication, Authorization, Other
If an attacker can identify an exploitable vulnerability in one product that has no means of patching, the attack may be used against all affected versions of that product.
Potential Mitigations
Phase(s)
Mitigation
Requirements
Specify requirements that each component should be updateable, including ROM, firmware, etc.
Architecture and Design
Design the product to allow for updating of its components. Include the external infrastructure that might be necessary to support updates, such as distribution servers.
Architecture and Design; Implementation
With hardware, support patches that can be programmed in-field or during manufacturing through hardware fuses. This feature can be used for limited patching of devices after shipping, or for the next batch of silicon devices manufactured, without changing the full device ROM.
Effectiveness: Moderate
Note:
Some parts of the hardware initialization or signature verification done to authenticate patches will always be "not patchable." Hardware-fuse-based patches will also have limitations in terms of size and the number of patches that can be supported.
Implementation
Implement the necessary functionality to allow each component to be updated.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Improper Control of a Resource Through its Lifetime
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Requirements
Requirements development might not consider the importance of updates over the lifetime of the product or might intentionally exclude this capability due to concerns such as expense or speed to market.
Architecture and Design
Lack of planning during architecture development and design, or external pressures such as speed to market, could ignore the capability to update.
Architecture and Design
Designers might omit capabilities for updating a component due to time pressures to release the product or assumptions about the stability of the component.
Implementation
The weakness can appear through oversight during implementation.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A refrigerator has an Internet interface for the official purpose of alerting the manufacturer when that refrigerator detects a fault. Because the device is attached to the Internet, the refrigerator is a target for hackers who may wish to use the device other potentially more nefarious purposes.
(bad code)
Example Language: Other
The refrigerator has no means of patching and is hacked, becoming a spewer of email spam.
(good code)
Example Language: Other
The device automatically patches itself and provides considerable more protection against being hacked.
Example 2
A System-on-Chip (SOC) implements a Root-of-Trust (RoT) in ROM to boot secure code. However, at times this ROM code might have security vulnerabilities and need to be patched. Since ROM is immutable, it can be impossible to patch.
ROM does not have built-in application-programming interfaces (APIs) to patch if the code is vulnerable. Implement mechanisms to patch the vulnerable ROM code.
Example 3
The example code is taken from the JTAG module of the buggy OpenPiton SoC of HACK@DAC'21. JTAG is protected with a password checker. Access to JTAG operations will be denied unless the correct password is provided by the user. This user-provided password is first sent to the HMAC module where it is hashed with a secret crypto key. This user password hash (pass_hash) is then compared with the hash of the correct password (exp_hash). If they match, JTAG will then be unlocked.
(bad code)
Example Language: SystemVerilog
module dmi_jtag(...)(...);
...
PassChkValid: begin
if(hashValid) begin
if(exp_hash == pass_hash) begin
pass_check = 1'b1;
end else begin
pass_check = 1'b0;
end
state_d = Idle;
end else begin
state_d = PassChkValid;
end
end
...
hmac hmac(
...
.key_i(256'h24e6fa2254c2ff632a41b...),
...
);
...
endmodule
However, the SoC's crypto key is hardcoded into the design and cannot be updated [REF-1387]. Therefore, if the key is leaked somehow, there is no way to reprovision the key without having the device replaced.
To fix this issue, a local register should be used (hmac_key_reg) to store the crypto key. If designers need to update the key, they can upload the new key through an input port (hmac_key_i) to the local register by enabling the patching signal (hmac_patch_en) [REF-1388].
always_ff @(posedge tck_i or negedge trst_ni) begin
... if (hmac_patch_en)
hmac_key_reg <= hmac_key_i;
...
end
...
hmac hmac(
... .key_i(hmac_key_reg),
...
);
...
endmodule
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: network-attached storage (NAS) device has a critical OS command injection (CWE-78) vulnerability that is actively exploited to place IoT devices into a botnet, but some products are "end-of-support" and cannot be patched (CWE-1277). [REF-1097]
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Check the consumer or maintainer documentation, the architecture/design documentation, or the original requirements to ensure that the documentation includes details for how to update the firmware.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
OWASP Top Ten 2025 Category A03:2025 - Software Supply Chain Failures
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1357: Reliance on Insufficiently Trustworthy Component
Weakness ID: 1357
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product is built from multiple separate components, but it uses a component that is not sufficiently trusted to meet expectations for security, reliability, updateability, and maintainability.
Technical Nuance
Note that a component might not be trustworthy even if it is owned by the product vendor, such as a software component whose source code is lost and was built by developers who left the company, or a component that was developed by a separate company that was acquired and brought into the product's own company.
There can be disagreement as to whether a component is sufficiently trustworthy, since trust is ultimately subjective. Different stakeholders (e.g., customers, vendors, governments) have various threat models and ways to assess trust, and design/architecture choices might make tradeoffs between security, reliability, safety, privacy, cost, and other characteristics.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Reduce Maintainability; Unexpected State; Varies by Context
Scope: Other
If a component is not trustworthy, it can produce significant risks for the overall product, such as vulnerabilities that cannot be patched fast enough (if at all); hidden functionality such as malware; inability to update or replace the component if needed for security purposes; hardware components built from parts that do not meet specifications in ways that can lead to weaknesses; etc.
Potential Mitigations
Phase(s)
Mitigation
Requirements; Architecture and Design; Implementation
Regardless of the source, each component should be sufficiently trusted to ensure correct, secure operation of the product.
For each component, ensure that its supply chain is well-controlled with sub-tier suppliers using best practices. For third-party software components such as libraries, ensure that they are developed and actively maintained by reputable vendors.
Architecture and Design; Implementation; Integration; Manufacturing
Maintain a Bill of Materials for all components and sub-components of the product. For software, maintain a Software Bill of Materials (SBOM). According to [REF-1247], "An SBOM is a formal, machine-readable inventory of software components and dependencies, information about those components, and their hierarchical relationships."
Operation; Patching and Maintenance
Continue to monitor changes in each of the product's components, especially when the changes indicate new vulnerabilities, end-of-life (EOL) plans, supplier practices that affect trustworthiness, etc.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Requirements
Requirements might include criteria for which the only available solutions are provided by insufficiently trusted components.
Architecture and Design
Many modern hardware and software products are built by combining multiple smaller components together into one larger entity, often during the design or architecture phase. For example, a hardware component might be built by a separate supplier, or the product might use an open-source software library from a third party.
An insufficiently trusted component might be selected because it is less expensive to do in-house; requires expertise that is not available in-house; or might allow the product to reach the market faster.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Class: ICS/OT
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A refrigerator has an Internet interface for the official purpose of alerting the manufacturer when that refrigerator detects a fault. Because the device is attached to the Internet, the refrigerator is a target for hackers who may wish to use the device other potentially more nefarious purposes.
(bad code)
Example Language: Other
The refrigerator has no means of patching and is hacked, becoming a spewer of email spam.
(good code)
Example Language: Other
The device automatically patches itself and provides considerable more protection against being hacked.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: network-attached storage (NAS) device has a critical OS command injection (CWE-78) vulnerability that is actively exploited to place IoT devices into a botnet, but some products are "end-of-support" and cannot be patched (CWE-1277). [REF-1097]
Weakness Ordinalities
Ordinality
Description
Indirect
(where the weakness is a quality issue that might indirectly make it easier to introduce security-relevant weaknesses or make them more difficult to detect)
Detection
Methods
Method
Details
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reason
Abstraction
Rationale
This CWE entry is a Class and might have Base-level children that would be more appropriate
Comments
Examine children of this entry to see if there is a better fit
Notes
Maintenance
As of CWE 4.10, the name and description for this entry has undergone significant change and is still under public discussion, especially by members of the HW SIG.
CWE-1330: Remanent Data Readable after Memory Erase
Weakness ID: 1330
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
VariantVariant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Confidential information stored in memory circuits is readable or recoverable after being cleared or erased, i.e., there is data remanence.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory; Read Memory
Scope: Confidentiality
Data remanence occurs when stored memory content is not fully lost after a memory-clear or memory-erase operation. Confidential memory contents can still be readable through data remanence in the hardware. Confidential data are readable to untrusted agent.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Support for secure-erase commands that apply multiple cycles of overwriting memory with known patterns and of erasing actual content.
Support for cryptographic erase in self-encrypting, memory devices.
External, physical tools to erase memory such as ultraviolet-rays-based erase of Electrically erasable, programmable, read-only memory (EEPROM).
Physical destruction of media device. This is done for repurposed or scrapped devices that are no longer in use.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design; Implementation
Data remanence can occur because of performance optimization or memory organization during 'clear' or 'erase' operations, like a design that allows the memory-organization metadata (e.g., file pointers) to be erased without erasing the actual memory content. To protect against this weakness, memory devices will often support different commands for optimized memory erase and explicit secure erase.
Data remanence can also happen because of the physical properties of memory circuits in use. For example, static, random-access-memory (SRAM) and dynamic, random-access-memory (DRAM) data retention is based on the charge retained in the memory cell, which depends on factors such as power supply, refresh rates, and temperature.
Architecture and Design
Other than explicit erase commands, secure-memory devices that self-encrypt can also support secure erase through cryptographic erase commands. In such designs, only the decryption keys for encrypted data stored on the device are erased. That is, the stored data are always remanant in the media after a cryptographic erase. However, only the encrypted data can be extracted. Thus, protection against data recovery in such designs relies on the strength of the encryption algorithm.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Security Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider a device that uses flash memory for non-volatile-data storage. To optimize flash-access performance or reliable-flash lifetime, the device might limit the number of flash writes/erases by maintaining some state in internal SRAM and only committing changes to flash memory periodically.
The device also supports user reset to factory defaults with the expectation that all personal information is erased from the device after this operation. On factory reset, user files are erased using explicit, erase commands supported by the flash device.
In the given, system design, the flash-file system can support performance-optimized erase such that only the file metadata are erased and not the content. If this optimized erase is used for files containing user data during factory-reset flow, then device, flash memory can contain remanent data from these files.
On device-factory reset, the implementation might not erase these copies, since the file organization has changed and the flash file system does not have the metadata to track all previous copies.
A flash-memory region that is used by a flash-file system should be fully erased as part of the factory-reset flow. This should include secure-erase flow for the flash media such as overwriting patterns multiple times followed by erase.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Firmware Data Deletion Vulnerability in which a base station factory reset might not delete all user information. The impact of this enables a new owner of a used device that has been "factory-default reset" with a vulnerable firmware version can still retrieve, at least, the previous owner's wireless network name, and the previous owner's wireless security (such as WPA2) key. This issue was addressed with improved, data deletion.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Testing of memory-device contents after clearing or erase commands.
Dynamic analysis of memory contents during device operation to detect specific, confidential assets.
Architecture and design analysis of memory clear and erase operations.
Dynamic Analysis with Manual Results Interpretation
Testing of memory-device contents after clearing or erase commands.
Dynamic analysis of memory contents during device operation to detect specific, confidential assets.
Architecture and design analysis of memory clear and erase operations.
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Variant level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to improper design of full-system security flows, including but not limited to secure boot, secure update, and hardware-device attestation.
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE Grouping: Security Primitives and Cryptography Issues
Grouping ID: 1205
Vulnerability Mapping:PROHIBITEDThis CWE ID must not be used to map to real-world vulnerabilities
Summary
Weaknesses in this category are related to hardware implementations of cryptographic protocols and other hardware-security primitives such as physical unclonable functions (PUFs) and random number generators (RNGs).
Membership
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
(this CWE ID must not be used to map to real-world vulnerabilities)
Reason
Grouping
Rationale
This entry is a Grouping. Using groupings for mapping has been discouraged since 2019. They are informal organizational groupings of weaknesses that can help CWE users with data aggregation, navigation, and browsing. However, they are not weaknesses in themselves.
CWE-1328: Security Version Number Mutable to Older Versions
Weakness ID: 1328
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The security version number in the hardware product is mutable, resulting in the ability to downgrade (roll-back) the boot firmware to vulnerable code versions.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Other; Alter Execution Logic; Unexpected State
Scope: Confidentiality, Integrity, Authentication, AuthorizationLikelihood: High
If the security version number is modifiable by an adversary, this allows attacks like downgrading to a previous version that contains vulnerabilities. Once downgraded to a previous version, an adversary can launch exploits on the SoC and thus compromise the security of the SoC. These downgrade attacks are also referred to as roll-back attacks.
Other; Alter Execution Logic; Unexpected State
Scope: Availability
An adversary could prevent upgrades, casing a denial of service.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
The security version number must be stored securely and persistently across power-on resets. When architecting the system, security version data should be designated for storage in registers that are either read-only or have access controls that prevent modification by an untrusted agent.
Implementation
During implementation and test, security version data should be demonstrated to be read-only and access controls should be validated.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
A System-on-Chip (SoC) implements secure boot or verified boot. It might support a security version number, which prevents downgrading the current firmware to a vulnerable version.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Such issues could be introduced during hardware architecture and design, and can be identified later during testing or system configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Security Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A new version of firmware is signed with a security version number higher than the previous version. During the firmware update process the SoC checks for the security version number and upgrades the SoC firmware with the latest version. This security version number is stored in persistent memory upon successful upgrade for use across power-on resets.
In general, if the security version number is mutable, the implementation is vulnerable. A mutable security version number allows an adversary to change the security version to a lower value to allow roll-back or to a higher value to prevent future upgrades.
The security version number should be stored in immutable hardware such as fuses, and the writes to these fuses should be highly access-controlled with appropriate authentication and authorization protections.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Automated Dynamic Analysis
Mutability of stored security version numbers and programming with older firmware images should be part of automated testing.
Effectiveness: High
Architecture or Design Review
Anti-roll-back features should be reviewed as part of Architecture or Design review.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1233: Security-Sensitive Hardware Controls with Missing Lock Bit Protection
Weakness ID: 1233
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product uses a register lock bit protection mechanism, but it does not ensure that the lock bit prevents modification of system registers or controls that perform changes to important hardware system configuration.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Modify Memory
Scope: Access Control
System Configuration protected by the lock bit can be modified even when the lock is set. If the lock bit does not effectively write-protect all system registers or controls that could modify the protected system configuration, then an adversary may be able to use software to access the registers/controls and modify the protected hardware configuration.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation; Testing
Security lock bit protections must be reviewed for design inconsistency and common weaknesses.
Security lock programming flow and lock properties must be tested in pre-silicon and post-silicon testing.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Integrated circuits and hardware intellectual properties (IPs) might provide device configuration controls that need to be programmed after device power reset by a trusted firmware or software module, commonly set by BIOS/bootloader. After reset, there can be an expectation that the controls cannot be used to perform any further modification. This behavior is commonly implemented using a trusted lock bit, which can be set to disable writes to a protected set of registers or address regions. The lock protection is intended to prevent modification of certain system configuration (e.g., memory/memory protection unit configuration).
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Such issues could be introduced during hardware architecture and design and identified later during Testing or System Configuration phases.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Consider the example design below for a digital thermal sensor that detects overheating of the silicon and triggers system shutdown. The system critical temperature limit (CRITICAL_TEMP_LIMIT) and thermal sensor calibration (TEMP_SENSOR_CALIB) data have to be programmed by the firmware.
In this example note that only the CRITICAL_TEMP_LIMIT register is protected by the TEMP_SENSOR_LOCK bit, while the security design intent is to protect any modification of the critical temperature detection and response.
The response of the system, if the system heats to a critical temperature, is controlled by TEMP_HW_SHUTDOWN bit [1], which is not lockable. Also, the TEMP_SENSOR_CALIB register is not protected by the lock bit.
By modifying the temperature sensor calibration, the conversion of the sensor data to a degree centigrade can be changed, such that the current temperature will never be detected to exceed critical temperature value programmed by the protected lock.
Similarly, by modifying the TEMP_HW_SHUTDOWN.Enable bit, the system response detection of the current temperature exceeding critical temperature can be disabled.
(good code)
Example Language: Other
Change TEMP_HW_SHUTDOWN and TEMP_SENSOR_CALIB controls to be locked by TEMP_SENSOR_LOCK.
TEMP_SENSOR_CALIB
[31:0] Thermal sensor calibration data. A slope value used to map sensor reading to a degree Centigrade. Read-write-Lock; Default 25; Locked by TEMP_SENSOR_LOCK bit[0]
TEMP_HW_SHUTDOWN
[31:2] Reserved field; Read only; Default 0[1] Enable hardware shutdown on critical temperature detection; Read-write-Lock; Default 0; Locked by TEMP_SENSOR_LOCK bit[0]
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Chain: chipset has a race condition (CWE-362) between when an interrupt handler detects an attempt to write-enable the BIOS (in violation of the lock bit), and when the handler resets the write-enable bit back to 0, allowing attackers to issue BIOS writes during the timing window [REF-1237].
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Set the lock bit. Attempt to modify the
information protected by the lock bit. If the information
is changed, implement a design fix. Retest. Also, attempt
to indirectly clear the lock bit or bypass
it.
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1248: Semiconductor Defects in Hardware Logic with Security-Sensitive Implications
Weakness ID: 1248
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The security-sensitive hardware module contains semiconductor defects.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
DoS: Instability
Scope: Availability, Access Control
Semiconductor defects manifest as faults on chip-internal signals or registers, have the effect of inputs, outputs, or intermediate signals being always 0 or always 1, and do not switch as expected. If such faults occur in security-sensitive hardware modules, the security objectives of the hardware module may be compromised.
Potential Mitigations
Phase(s)
Mitigation
Testing
While semiconductor-manufacturing companies implement several mechanisms to continuously improve the semiconductor manufacturing process to ensure reduction of defects, some defects can only be fixed after manufacturing. Post-manufacturing testing of silicon die is critical. Fault models such as stuck-at-0 or stuck-at-1 must be used to develop post-manufacturing test cases and achieve good coverage. Once the silicon packaging is done, extensive post-silicon testing must be performed to ensure that hardware logic implementing security functionalities is defect-free.
Operation
Operating the hardware outside device specification, such as at extremely high temperatures, voltage, etc., accelerates semiconductor degradation and results in defects. When these defects manifest as faults in security-critical, hardware modules, it results in compromise of security guarantees. Thus, operating the device within the specification is important.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
A semiconductor device can fail for various reasons. While some are manufacturing and packaging defects, the rest are due to prolonged use or usage under extreme conditions. Some mechanisms that lead to semiconductor defects include encapsulation failure, die-attach failure, wire-bond failure, bulk-silicon defects, oxide-layer faults, aluminum-metal faults (including electromigration, corrosion of aluminum, etc.), and thermal/electrical stress.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Manufacturing
May be introduced due to issues in the manufacturing environment or improper handling of components, for example.
Operation
May be introduced by improper handling or usage outside of rated operating environments (temperature, humidity, etc.)
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The network-on-chip implements a firewall for access control to peripherals from all IP cores capable of mastering transactions.
(bad code)
Example Language: Other
A manufacturing defect in this logic manifests itself as a logical fault, which always sets the output of the filter to "allow" access.
Post-manufacture testing must be performed to ensure that hardware logic implementing security functionalities is defect-free.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-226: Sensitive Information in Resource Not Removed Before Reuse
Weakness ID: 226
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product releases a resource such as memory or a file so that it can be made available for reuse, but it does not clear or "zeroize" the information contained in the resource before the product performs a critical state transition or makes the resource available for reuse by other entities.
Extended Description
When resources are released, they can be made available for reuse. For example, after memory is de-allocated, an operating system may make the memory available to another process, or disk space may be reallocated when a file is deleted. Since removing information requires time and additional resources, operating systems do not usually clear the previously written information.
Even when the resource is reused by the same process, this weakness can arise when new data is not as large as the old data, which leaves portions of the old data still available. Equivalent errors can occur in other situations where the length of data is variable but the associated data structure is not. If memory is not cleared after use, the information may be read by less trustworthy parties when the memory is reallocated.
This weakness can apply in hardware, such as when a device or system switches between power, sleep, or debug states during normal operation, or when execution changes to different users or privilege levels.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data
Scope: Confidentiality
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
During critical state transitions, information not needed in the next state should be removed or overwritten with fixed patterns (such as all 0's) or random data, before the transition to the next state.
Effectiveness: High
Architecture and Design; Implementation
When releasing, de-allocating, or deleting a resource, overwrite its data and relevant metadata with fixed patterns or random data. Be cautious about complex resource types whose underlying representation might be non-contiguous or change at a low level, such as how a file might be split into different chunks on a file system, even though "logical" file positions are contiguous at the application layer. Such resource types might require invocation of special modes or APIs to tell the underlying operating system to perform the necessary clearing, such as SDelete (Secure Delete) on Windows, although the appropriate functionality might not be available at the application layer.
Effectiveness: High
Implementation
Be careful using vfork() and fork() in security sensitive code. The process state will not be cleaned up and will contain traces of data from past use.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Removal of Sensitive Information Before Storage or Transfer
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information Uncleared Before Debug/Power State Transition
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient or Incomplete Data Removal within Hardware Component
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Information Exposure through Microarchitectural State after Transient Execution
CanPrecede
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example shows how an attacker can take advantage of an incorrect state transition.
Suppose a device is transitioning from state A to state B. During state A, it can read certain private keys from the hidden fuses that are only accessible in state A but not in state B. The device reads the keys, performs operations using those keys, then transitions to state B, where those private keys should no longer be accessible.
(bad code)
Example Language: Other
During the transition from A to B, the device does not scrub the memory.
After the transition to state B, even though the private keys are no longer accessible directly from the fuses in state B, they can be accessed indirectly by reading the memory that contains the private keys.
(good code)
Example Language: Other
For transition from state A to state B, remove information which should not be available once the transition is complete.
Example 2
The following code calls realloc() on a buffer containing sensitive data:
There is an attempt to scrub the sensitive data from memory, but realloc() is used, so it could return a pointer to a different part of memory. The memory that was originally allocated for cleartext_buffer could still contain an uncleared copy of the data.
Example 3
The following example code is excerpted from the AES wrapper/interface, aes0_wrapper, module of
one of the AES engines (AES0) in the Hack@DAC'21 buggy OpenPiton System-on-Chip (SoC). Note that
this SoC contains three distinct AES engines. Within this wrapper module, four 32-bit registers are
utilized to store the message intended for encryption, referred to as p_c[i]. Using the AXI Lite
interface, these registers are filled with the 128-bit message to be encrypted.
The above code snippet [REF-1402] illustrates an instance of a vulnerable implementation of the AES
wrapper module, where p_c[i] registers are cleared at reset. Otherwise, p_c[i]registers either
maintain their old values (if reglk_ctrl_i[3]is true) or get filled through the AXI signal wdata. Note
that p_c[i]registers can be read through the AXI Lite interface (not shown in snippet). However,
p_c[i] registers are never cleared after their usage once the AES engine has completed the encryption
process of the message. In a multi-user or multi-process environment, not clearing registers may result
in the attacker process accessing data left by the victim, leading to data leakage or unintentional
information disclosure.
To fix this issue, it is essential to ensure that these internal registers are cleared in a timely manner after
their usage, i.e., the encryption process is complete. This is illustrated below by monitoring the assertion
of the cipher text valid signal, ct_valid [REF-1403].
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Write a known pattern into each sensitive location. Trigger the release of the resource or cause the desired state transition to occur. Read data back from the sensitive locations. If the reads are successful, and the data is the same as the pattern that was originally written, the test fails and the product needs to be fixed. Note that this test can likely be automated.
Effectiveness: High
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Effectiveness: High
Functional Areas
Memory Management
Networking
Affected Resources
Memory
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
Weaknesses in the 2025 CWE Most Important Hardware Weaknesses List
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Relationship
There is a close association between CWE-226 and CWE-212. The difference is partially that of perspective. CWE-226 is geared towards the final stage of the resource lifecycle, in which the resource is deleted, eliminated, expired, or otherwise released for reuse. Technically, this involves a transfer to a different control sphere, in which the original contents of the resource are no longer relevant. CWE-212, however, is intended for sensitive data in resources that are intentionally shared with others, so they are still active. This distinction is useful from the perspective of the CWE research view (CWE-1000).
Research Gap
This is frequently found for network packets, but it can also exist in local memory allocation, files, etc.
Maintenance
This entry needs modification to clarify the differences with CWE-212. The description also combines two problems that are distinct from the CWE research perspective: the inadvertent transfer of information to another sphere, and improper initialization/shutdown. Some of the associated taxonomy mappings reflect these different uses.
Taxonomy
Mappings
Mapped Taxonomy Name
Node ID
Fit
Mapped Node Name
PLOVER
Sensitive Information Uncleared Before Use
CERT C Secure Coding
MEM03-C
Clear sensitive information stored in reusable resources returned for reuse
CWE-1272: Sensitive Information Uncleared Before Debug/Power State Transition
Weakness ID: 1272
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product performs a power or debug state transition, but it does not clear sensitive information that should no longer be accessible due to changes to information access restrictions.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
If there is information available in the previous state which should not be available in the next state and is not properly removed before the transition into the next state, sensitive information may leak from the system. The sensitive information may be used to unlock additional capabilities of the device and take advantage of hidden functionalities which could be used to compromise device security.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
During state transitions, information not needed in the next state should be removed before the transition to the next state.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Sensitive Information in Resource Not Removed Before Reuse
ParentOf
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Exposure of Sensitive System Information Due to Uncleared Debug Information
CanAlsoBe
Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
A device or system frequently employs many power and sleep states during its normal operation (e.g., normal power, additional power, low power, hibernate, deep sleep, etc.). A device also may be operating within a debug condition. State transitions can happen from one power or debug state to another.
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
VHDL
(Undetermined Prevalence)
Verilog
(Undetermined Prevalence)
Class: Hardware Description Language
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
This example shows how an attacker can take advantage of an incorrect state transition.
Suppose a device is transitioning from state A to state B. During state A, it can read certain private keys from the hidden fuses that are only accessible in state A but not in state B. The device reads the keys, performs operations using those keys, then transitions to state B, where those private keys should no longer be accessible.
(bad code)
Example Language: Other
During the transition from A to B, the device does not scrub the memory.
After the transition to state B, even though the private keys are no longer accessible directly from the fuses in state B, they can be accessed indirectly by reading the memory that contains the private keys.
(good code)
Example Language: Other
For transition from state A to state B, remove information which should not be available once the transition is complete.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
Product software does not set a flag as per TPM specifications, thereby preventing a failed authorization attempt from being recorded after a loss of power.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Manual Analysis
Write a known pattern into each sensitive location. Enter the power/debug state in question. Read data back from the sensitive locations. If the reads are successful, and the data is the same as the pattern that was originally written, the test fails and the device needs to be fixed. Note that this test can likely be automated.
Effectiveness: High
Functional Areas
Power
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1243: Sensitive Non-Volatile Information Not Protected During Debug
Weakness ID: 1243
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Access to security-sensitive information stored in fuses is not limited during debug.
Extended Description
Several security-sensitive values are programmed into fuses to be used during early-boot flows or later at runtime. Examples of these security-sensitive values include root keys, encryption keys, manufacturing-specific information, chip-manufacturer-specific information, and original-equipment-manufacturer (OEM) data. After the chip is powered on, these values are sensed from fuses and stored in temporary locations such as registers and local memories. These locations are typically access-control protected from untrusted agents capable of accessing them. Even to trusted agents, only read-access is provided.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
If these locations are not blocked during debug operations, it can allow a user to access this sensitive information.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
Disable access to security-sensitive information stored in fuses directly and also reflected from temporary storage locations when in debug mode.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Sensitive manufacturing data (such as die information) are stored in fuses. When the chip powers on, these values are read from the fuses and stored in microarchitectural registers. These registers are only given read access to trusted software running on the core. Untrusted software running on the core is not allowed to access these registers.
(bad code)
Example Language: Other
All microarchitectural registers in this chip can be accessed through the debug interface. As a result, even an untrusted debugger can access this data and retrieve sensitive manufacturing data.
(good code)
Example Language: Other
Registers used to store sensitive values read from fuses should be blocked during debug. These registers should be disconnected from the debug interface.
Example 2
The example code below is taken from one of the AES cryptographic accelerators of the HACK@DAC'21 buggy OpenPiton SoC [REF-1366]. The operating system (OS) uses three AES keys to encrypt and decrypt sensitive data using this accelerator. These keys are sensitive data stored in fuses. The security of the OS will be compromised if any of these AES keys are leaked. During system bootup, these AES keys are sensed from fuses and stored in temporary hardware registers of the AES peripheral. Access to these temporary registers is disconnected during the debug state to prevent them from leaking through debug access. In this example (see the vulnerable code source), the registers key0, key1, and key2 are used to store the three AES keys (which are accessed through key_big0, key_big1, and key_big2 signals). The OS selects one of these three keys through the key_big signal, which is used by the AES engine.
The above code illustrates an instance of a vulnerable implementation for blocking AES key mechanism when the system is in debug mode (i.e., when debug_mode_i is asserted). During debug mode, key accesses through key_big0 and key_big1 are effectively disconnected, as their values are set to zero. However, the key accessed via the key_big2 signal remains accessible, creating a potential pathway for sensitive fuse data leakage, specifically AES key2, during debug mode. Furthermore, even though it is not strictly necessary to disconnect the key_big signal when entering debug mode (since disconnecting key_big0, key_big1, and key_big2 will inherently disconnect key_big), it is advisable, in line with the defense-in-depth strategy, to also sever the connection to key_big. This additional security measure adds an extra layer of protection and safeguards the AES keys against potential future modifications to the key_big logic.
To mitigate this, disconnect access through key_big2 and key_big during debug mode [REF-1367].
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1281: Sequence of Processor Instructions Leads to Unexpected Behavior
Weakness ID: 1281
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Specific combinations of processor instructions lead to undesirable behavior such as locking the processor until a hard reset performed.
Extended Description
If the instruction set architecture (ISA) and processor logic are not designed carefully and tested thoroughly, certain combinations of instructions may lead to locking the processor or other unexpected and undesirable behavior. Upon encountering unimplemented instruction opcodes or illegal instruction operands, the processor should throw an exception and carry on without negatively impacting security. However, specific combinations of legal and illegal instructions may cause unexpected behavior with security implications such as allowing unprivileged programs to completely lock the CPU.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Varies by Context
Scope: Integrity, Availability
Potential Mitigations
Phase(s)
Mitigation
Testing
Implement a rigorous testing strategy that incorporates randomization to explore instruction sequences that are unlikely to appear in normal workloads in order to identify halt and catch fire instruction sequences.
Patching and Maintenance
Patch operating system to avoid running Halt and Catch Fire type sequences or to mitigate the damage caused by unexpected behavior. See [REF-1108].
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Unexpected behavior from certain instruction combinations can arise from bugs in the ISA
Implementation
Unexpected behavior from certain instruction combinations can arise because of implementation details such as speculative execution, caching etc.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Processor Hardware
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The Pentium F00F bug is a real-world example of how a sequence of instructions can lock a processor. The "cmpxchg8b" instruction compares contents of registers with a memory location. The operand is expected to be a memory location, but in the bad code snippet it is the eax register. Because the specified operand is illegal, an exception is generated, which is the correct behavior and not a security issue in itself. However, when prefixed with the "lock" instruction, the processor deadlocks because locked memory transactions require a read and write a pair of transactions to occur before the lock on the memory bus is released. The exception causes a read to occur but there is no corresponding write, as there would have been if a legal operand had been supplied to the cmpxchg8b instruction. [REF-1331]
(bad code)
Example Language: x86 Assembly
lock cmpxchg8b eax
Example 2
The Cyrix Coma bug was capable of trapping a Cyrix 6x86, 6x86L, or 6x86MX processor in an infinite loop. An infinite loop on a processor is not necessarily an issue on its own, as interrupts could stop the loop. However, on select Cyrix processors, the x86 Assembly 'xchg' instruction was designed to prevent interrupts. On these processors, if the loop was such that a new 'xchg' instruction entered the instruction pipeline before the previous one exited, the processor would become deadlocked. [REF-1323]
Example 3
The Motorola MC6800 microprocessor contained the first documented instance of a Halt and Catch Fire instruction - an instruction that causes the normal function of a processor to stop. If the MC6800 was given the opcode 0x9D or 0xDD, the processor would begin to read all memory very quickly, in sequence, and without executing any other instructions. This will cause the processor to become unresponsive to anything but a hard reset. [REF-1324]
Example 4
The example code is taken from the commit stage inside the processor core of the HACK@DAC'19 buggy CVA6 SoC [REF-1342]. To ensure the correct execution of atomic instructions, the CPU must guarantee atomicity: no other device overwrites the memory location between the atomic read starts and the atomic write finishes. Another device may overwrite the memory location only before the read operation or after the write operation, but never between them, and finally, the content will still be consistent.
Atomicity is especially critical when the variable to be modified is a mutex, counting semaphore, or similar piece of data that controls access to shared resources. Failure to ensure atomicity may result in two processors accessing a shared resource simultaneously, permanent lock-up, or similar disastrous behavior.
(bad code)
Example Language: SystemVerilog
if (csr_exception_i.valid && csr_exception_i.cause[63] && commit_instr_i[0].fu != CSR) begin
The above vulnerable code checks for CSR interrupts and gives them precedence over any other exception. However, the interrupts should not occur when the processor runs a series of atomic instructions. In the above vulnerable code, the required check must be included to ensure the processor is not in the middle of a series of atomic instructions.
Refrain from interrupting if the intention is to commit an atomic instruction that should not be interrupted. This can be done by adding a condition to check whether the current committing instruction is atomic. [REF-1343]
(good code)
Example Language: SystemVerilog
if (csr_exception_i.valid && csr_exception_i.cause[63] && !amo_valid_commit_o && commit_instr_i[0].fu != CSR) begin
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
A bug in some Intel Pentium processors allow DoS (hang) via an invalid "CMPXCHG8B" instruction, causing a deadlock
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Comprehensive Categorization: Insufficient Control Flow Management
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1334: Unauthorized Error Injection Can Degrade Hardware Redundancy
Weakness ID: 1334
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
An unauthorized agent can inject errors into a redundant block to deprive the system of redundancy or put the system in a degraded operating mode.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
This redundant block can be prevented from performing as intended if the design allows unauthorized agents to inject errors into it. In this way, a path with injected errors may become unavailable to serve as a redundant channel. This may put the system into a degraded mode of operation which could be exploited by a subsequent attack.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Ensure the design does not allow error injection in modes intended for normal run-time operation. Provide access controls on interfaces for injecting errors.
Implementation
Disallow error injection in modes which are expected to be used for normal run-time operation. Provide access controls on interfaces for injecting errors.
Integration
Add an access control layer atop any unprotected interfaces for injecting errors.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Pillar - a weakness that is the most abstract type of weakness and represents a theme for all class/base/variant weaknesses related to it. A Pillar is different from a Category as a Pillar is still technically a type of weakness that describes a mistake, while a Category represents a common characteristic used to group related things.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
To ensure the performance and functional reliability of certain components, hardware designers can implement hardware blocks for redundancy in the case that others fail.
Implementation
Such issues could be introduced during implementation and identified later during Testing or System Configuration phases.
Integration
Such issues could be introduced during integration and identified later during Testing or System Configuration phases.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
CWE-1271: Uninitialized Value on Reset for Registers Holding Security Settings
Weakness ID: 1271
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
Security-critical logic is not set to a known value on reset.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
When the device is first brought out of reset, the state of registers will be indeterminate if they have not been initialized by the logic. Before the registers are initialized, there will be a window during which the device is in an insecure state and may be vulnerable to attack.
Potential Mitigations
Phase(s)
Mitigation
Implementation
Design checks should be performed to identify any uninitialized flip-flops used for security-critical functions.
Architecture and Design
All registers holding security-critical information should be set to a specific value on reset.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improperly Preserved Integrity of Hardware Configuration State During a Power Save/Restore Operation
Modes
Of Introduction
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Shown below is a positive clock edge triggered flip-flop used to implement a lock bit for test and debug interface. When the circuit is first brought out of reset, the state of the flip-flop will be unknown until the enable input and D-input signals update the flip-flop state. In this example, an attacker can reset the device until the test and debug interface is unlocked and access the test interface until the lock signal is driven to a known state by the logic.
(bad code)
Example Language: Verilog
always @(posedge clk) begin
if (en) lock_jtag <= d;
end
The flip-flop can be set to a known value (0 or 1) on reset, but requires that the logic explicitly update the output of the flip-flop if the reset signal is active.
(good code)
Example Language: Verilog
always @(posedge clk) begin
if (~reset) lock_jtag <= 0;
else if (en) lock_jtag <= d;
end
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry is still under development and will continue to see updates and content improvements.
Vulnerability Mapping:ALLOWEDThis CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review
(with careful review of mapping notes)
Abstraction:
ClassClass - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product receives a request, message, or directive from an upstream component, but the product does not sufficiently preserve the original source of the request before forwarding the request to an external actor that is outside of the product's control sphere.
Alternate Terms
Confused Deputy
Roles: Common-Name
This weakness is sometimes referred to as the "Confused deputy" problem, in which an attacker misuses the authority of one victim (the "confused deputy") to use that victim's legitimate (restricted) capabilities to target another victim.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Hide Activities; Execute Unauthorized Code or Commands; Bypass Protection Mechanism
Scope: Non-Repudiation, Access Control
If an attacker cannot directly contact a target, but the product has access to the target, then the attacker can send a request to the product and have it be forwarded to the target. The source of this request would appear to be coming from the product's system, not the attacker's system, leading the product/system to act as a proxy or other intermediary between the upstream component and the external actor. As a result, the attacker can bypass access controls (such as firewalls) or hide the source of malicious requests, since the requests would not be coming directly from the attacker.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
Enforce the use of strong mutual authentication mechanism between the two parties.
Architecture and Design
Whenever a product is an intermediary or proxy for
transactions between two other components, the proxy core
should not drop the identity of the initiator of the
transaction. The immutability of the identity of the
initiator must be maintained and should be forwarded all the
way to the target.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Externally Controlled Reference to a Resource in Another Sphere
ParentOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Restriction of Rendered UI Layers or Frames
PeerOf
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Improper Restriction of XML External Entity Reference
CanPrecede
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
REALIZATION: This weakness is caused during implementation of an architectural security tactic.
Architecture and Design
Since proxy functionality and message-forwarding often serve a legitimate purpose, this issue only becomes a vulnerability when:
The product runs with different privileges or on a different system, or otherwise has different levels of access than the upstream component;
The attacker is prevented from making the request directly to the target; and
The attacker can create a request that the proxy does not explicitly intend to be forwarded on the behalf of the requester. Such a request might point to an unexpected hostname, port number, hardware IP, or service. Or, the request might be sent to an allowed service, but the request could contain disallowed directives, commands, or resources.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
A SoC contains a microcontroller (running ring-3
(least trusted ring) code), a Memory Mapped Input Output
(MMIO) mapped IP core (containing design-house secrets),
and a Direct Memory Access (DMA) controller, among several
other compute elements and peripherals. The SoC implements
access control to protect the registers in the IP core
(which registers store the design-house secrets) from
malicious, ring-3 (least trusted ring) code executing on
the microcontroller. The DMA controller, however, is not
blocked off from accessing the IP core for functional
reasons.
(bad code)
Example Language: Other
The code in ring-3 (least trusted ring) of the
microcontroller attempts to directly read the protected
registers in IP core through MMIO transactions. However,
this attempt is blocked due to the implemented access
control. Now, the microcontroller configures the DMA core
to transfer data from the protected registers to a memory
region that it has access to. The DMA core, which is
acting as an intermediary in this transaction, does not
preserve the identity of the microcontroller and, instead,
initiates a new transaction with its own identity. Since
the DMA core has access, the transaction (and hence, the
attack) is successful.
The weakness here is that the intermediary or the
proxy agent did not ensure the immutability of the
identity of the microcontroller initiating the
transaction.
(good code)
Example Language: Other
The DMA
core forwards this transaction with the identity of the
code executing on the microcontroller, which is the
original initiator of the end-to-end transaction. Now the
transaction is blocked, as a result of forwarding the
identity of the true initiator which lacks the permission
to access the confidential MMIO mapped IP core.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
FTP bounce attack. The design of the protocol allows an attacker to modify the PORT command to cause the FTP server to connect to other machines besides the attacker's.
URL-downloading library automatically follows redirects to file:// and scp:// URLs
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Automated Static Analysis
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)
Effectiveness: High
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
OWASP Top Ten 2025 Category A01:2025 - Broken Access Control
Vulnerability Mapping Notes
Usage
ALLOWED-WITH-REVIEW
(this CWE ID could be used to map to real-world vulnerabilities in limited situations requiring careful review)
Reason
Abstraction
Rationale
This CWE entry is a Class and might have Base-level children that would be more appropriate
Comments
Examine children of this entry to see if there is a better fit
Notes
Relationship
This weakness has a chaining relationship with CWE-668 (Exposure of Resource to Wrong Sphere) because the proxy effectively provides the attacker with access to the target's resources that the attacker cannot directly obtain.
Theoretical
It could be argued that the "confused deputy" is a fundamental aspect of most vulnerabilities that require an active attacker. Even for common implementation issues such as buffer overflows, SQL injection, OS command injection, and path traversal, the vulnerable program already has the authorization to run code or access files. The vulnerability arises when the attacker causes the program to run unexpected code or access unexpected files.
Maintenance
This could possibly be considered as an emergent resource.
Per Intel Corporation suggestion, added language to be inclusive to hardware: updated Demonstrative_Examples, Description, Extended_Description, Applicable_Platforms, Potential_Mitigation, Common_Consequences, References
CWE-1297: Unprotected Confidential Information on Device is Accessible by OSAT Vendors
Weakness ID: 1297
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The product does not adequately protect confidential information on the device from being accessed by Outsourced Semiconductor Assembly and Test (OSAT) vendors.
Extended Description
To counter this, the chipmaker often requires the OSAT partner to enter into restrictive non-disclosure agreements (NDAs).
Nonetheless, OSAT vendors likely have many customers, which increases the risk of accidental sharing of information. There may also be a security vulnerability in the information technology (IT) system of the OSAT facility. Alternatively, a malicious insider at the OSAT facility may carry out an insider attack.
Logic errors during design or synthesis could misconfigure the interconnection of the debug components, which could provide improper authorization to sensitive information.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Gain Privileges or Assume Identity; Bypass Protection Mechanism; Execute Unauthorized Code or Commands; Modify Memory; Modify Files or Directories
The impact depends on the confidential information itself and who is inadvertently granted access. For example, if the confidential information is a key that can unlock all the parts of a generation, the impact could be severe.
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design
It behooves the chipmaker to minimize any confidential information in the device that may be accessible to the OSAT vendor.
a
Ensure that when an OSAT vendor is allowed to access test interfaces necessary for preproduction and returned parts, the vendor only pulls the minimal information necessary. Also, architect the product in such a way that, when an "unlock device" request comes, it only unlocks that specific part and not all the parts for that product line.
Ensure that the product's non-volatile memory (NVM) is scrubbed of all confidential information and secrets before handing it over to an OSAT.
Arrange to secure all communication between an OSAT facility and the chipmaker.
Effectiveness: Moderate
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Implementation
In contrast to complete vertical integration of architecting, designing, manufacturing, assembling, and testing chips all within a single organization, an organization can choose to simply architect and design a chip before outsourcing the rest of the process to OSAT entities (e.g., external foundries and test houses).
Testing
With test houses, the device enters an OSAT facility in a much more vulnerable pre-production stage where many debug and test modes are accessible. Therefore, the chipmaker must place a certain level of trust with the OSAT.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Verilog
(Undetermined Prevalence)
VHDL
(Undetermined Prevalence)
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Processor Hardware
(Undetermined Prevalence)
Class: Not Technology-Specific
(Undetermined Prevalence)
Demonstrative Examples
Example 1
The following example shows how an attacker can take advantage of a piece of confidential information that has not been protected from the OSAT.
Suppose the preproduction device contains NVM (a storage medium that by definition/design can retain its data without power), and this NVM contains a key that can unlock all the parts for that generation. An OSAT facility accidentally leaks the key.
Compromising a key that can unlock all the parts of a generation can be devastating to a chipmaker.
The likelihood of such a compromise can be reduced by ensuring all memories on the preproduction device are properly scrubbed.
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Resultant
(where the weakness is typically related to the presence of some other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Appropriate Post-Si tests should be carried out to ensure that residual confidential information is not left on parts leaving one facility for another facility.
Effectiveness: High
Dynamic Analysis with Manual Results Interpretation
Appropriate Post-Si tests should be carried out to ensure that residual confidential information is not left on parts leaving one facility for another facility.
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
This entry might be subject to CWE Scope Exclusion SCOPE.SITUATIONS (Focus on situations in which weaknesses may appear); SCOPE.HUMANPROC (Human/organizational process; and/or SCOPE.CUSTREL (Not customer-relevant).
Maintenance
This entry is still under development and will continue to see updates and content improvements.
Exploiting Incorrectly Configured Access Control Security Levels
References
[REF-1113]
Muhammad Yasin, Abhrajit Sengupta, Mohammed Thari Nabeel, Mohammed Ashraf, Jeyavijayan (JV) Rajendran and Ozgur Sinanoglu. "Provably-Secure Logic Locking: From Theory To Practice". <https://dl.acm.org/doi/10.1145/3133956.3133985>.
(URL validated: 2023-04-07)
CWE-1240: Use of a Cryptographic Primitive with a Risky Implementation
Weakness ID: 1240
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
To fulfill the need for a cryptographic primitive, the product implements a cryptographic algorithm using a non-standard, unproven, or disallowed/non-compliant cryptographic implementation.
Extended Description
Cryptographic protocols and systems depend on cryptographic primitives (and associated algorithms) as their basic building blocks. Some common examples of primitives are digital signatures, one-way hash functions, ciphers, and public key cryptography; however, the notion of "primitive" can vary depending on point of view. See "Terminology Notes" for further explanation of some concepts.
Cryptographic primitives are defined to accomplish one very specific task in a precisely defined and mathematically reliable fashion. For example, suppose that for a specific cryptographic primitive (such as an encryption routine), the consensus is that the primitive can only be broken after trying out N different inputs (where the larger the value of N, the stronger the cryptography). For an encryption scheme like AES-256, one would expect N to be so large as to be infeasible to execute in a reasonable amount of time.
If a vulnerability is ever found that shows that one can break a cryptographic primitive in significantly less than the expected number of attempts, then that primitive is considered weakened (or sometimes in extreme cases, colloquially it is "broken"). As a result, anything using this cryptographic primitive would now be considered insecure or risky. Thus, even breaking or weakening a seemingly small cryptographic primitive has the potential to render the whole system vulnerable, due to its reliance on the primitive. A historical example can be found in TLS when using DES. One would colloquially call DES the cryptographic primitive for transport encryption in this version of TLS. In the past, DES was considered strong, because no weaknesses were found in it; importantly, DES has a key length of 56 bits. Trying N=2^56 keys was considered impractical for most actors. Unfortunately, attacking a system with 56-bit keys is now practical via brute force, which makes defeating DES encryption practical. It is now practical for an adversary to read any information sent under this version of TLS and use this information to attack the system. As a result, it can be claimed that this use of TLS is weak, and that any system depending on TLS with DES could potentially render the entire system vulnerable to attack.
Cryptographic primitives and associated algorithms are only considered safe after extensive research and review from experienced cryptographers from academia, industry, and government entities looking for any possible flaws. Furthermore, cryptographic primitives and associated algorithms are frequently reevaluated for safety when new mathematical and attack techniques are discovered. As a result and over time, even well-known cryptographic primitives can lose their compliance status with the discovery of novel attacks that might either defeat the algorithm or reduce its robustness significantly.
If ad-hoc cryptographic primitives are implemented, it is almost certain that the implementation will be vulnerable to attacks that are well understood by cryptographers, resulting in the exposure of sensitive information and other consequences.
This weakness is even more difficult to manage for hardware-implemented deployment of cryptographic algorithms. First, because hardware is not patchable as easily as software, any flaw discovered after release and production typically cannot be fixed without a recall of the product. Secondly, the hardware product is often expected to work for years, during which time computation power available to the attacker only increases. Therefore, for hardware implementations of cryptographic primitives, it is absolutely essential that only strong, proven cryptographic primitives are used.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data
Scope: ConfidentialityLikelihood: High
Incorrect usage of crypto primitives could render the supposedly encrypted data as unencrypted plaintext in the worst case.
Potential Mitigations
Phase(s)
Mitigation
Requirements
Require compliance with the strongest-available recommendations from trusted parties, and require that compliance must be kept up-to-date, since recommendations evolve over time. For example, US government systems require FIPS 140-3 certification, which supersedes FIPS 140-2 [REF-1192] [REF-267].
Effectiveness: High
Architecture and Design
Ensure that the architecture/design uses the strongest-available primitives and algorithms from trusted parties. For example, US government systems require FIPS 140-3 certification, which supersedes FIPS 140-2 [REF-1192] [REF-267].
Effectiveness: High
Architecture and Design
Do not develop custom or private cryptographic algorithms. They will likely be exposed to attacks that are well-understood by cryptographers. As with all cryptographic mechanisms, the source code should be available for analysis. If the algorithm may be compromised when attackers find out how it works, then it is especially weak.
Effectiveness: Discouraged Common Practice
Architecture and Design
Try not to use cryptographic algorithms in novel ways or with new modes of operation even when you "know" it is secure. For example, using SHA-2 chaining to create a 1-time pad for encryption might sound like a good idea, but one should not do this.
Effectiveness: Discouraged Common Practice
Architecture and Design
Ensure that the design can replace one cryptographic primitive or algorithm with another in the next generation ("cryptographic agility"). Where possible, use wrappers to make the interfaces uniform. This will make it easier to upgrade to stronger algorithms. This is especially important for hardware, which can be more difficult to upgrade quickly than software; design the hardware at a replaceable block level.
Effectiveness: Defense in Depth
Architecture and Design
Do not use outdated or non-compliant cryptography algorithms. Some older algorithms, once thought to require a billion years of computing time, can now be broken in days or hours. This includes MD4, MD5, SHA1, DES, and other algorithms that were once regarded as strong [REF-267].
Effectiveness: Discouraged Common Practice
Architecture and Design; Implementation
Do not use a linear-feedback shift register (LFSR) or other legacy methods as a substitute for an accepted and standard Random Number Generator.
Effectiveness: Discouraged Common Practice
Architecture and Design; Implementation
Do not use a checksum as a substitute for a cryptographically generated hash.
Effectiveness: Discouraged Common Practice
Architecture and Design
Strategy: Libraries or Frameworks
Use a vetted cryptographic library or framework. Industry-standard implementations will save development time and are more likely to avoid errors that can occur during implementation of cryptographic algorithms. However, the library/framework could be used incorrectly during implementation.
Effectiveness: High
Architecture and Design; Implementation
When using industry-approved techniques, use them correctly. Don't cut corners by skipping resource-intensive steps (CWE-325). These steps are often essential for the prevention of common attacks.
Effectiveness: Moderate
Architecture and Design; Implementation
Do not store keys in areas accessible to untrusted agents. Carefully manage and protect the cryptographic keys (see CWE-320). If the keys can be guessed or stolen, then the strength of the cryptography algorithm is irrelevant.
Effectiveness: Moderate
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
This weakness is primarily introduced during the architecture and design phase as risky primitives are included.
Implementation
Even in cases where the Architectural phase properly specifies a cryptographically secure design, the design may be changed during implementation due to unforeseen constraints.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Languages
Class: Not Language-Specific
(Undetermined Prevalence)
Operating Systems
Class: Not OS-Specific
(Undetermined Prevalence)
Architectures
Class: Not Architecture-Specific
(Undetermined Prevalence)
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Re-using random values may compromise security.
(bad code)
Example Language: Other
Suppose an Encryption algorithm needs a random value for a key. Instead of using a DRNG (Deterministic Random Number Generator), the designer uses a linear-feedback shift register (LFSR) to generate the value.
While an LFSR may provide pseudo-random number generation service, the entropy (measure of randomness) of the resulting output may be less than that of an accepted DRNG (like that used in dev/urandom). Thus, using an LFSR weakens the strength of the cryptographic system, because it may be possible for an attacker to guess the LFSR output and subsequently the encryption key.
(good code)
Example Language: Other
If a cryptographic algorithm expects a random number as its input, provide one. Do not provide a pseudo-random value.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
SSL/TLS library generates 16-byte nonces but reduces them to 12 byte nonces for the ChaCha20-Poly1305 cipher, converting them in a way that violates the cipher's requirements for unique nonces.
Recommendation for Dual_EC_DRBG algorithm contains point Q constants that could simplify decryption
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Detection
Methods
Method
Details
Architecture or Design Review
Review requirements, documentation, and product design to ensure that primitives are consistent with the strongest-available recommendations from trusted parties. If the product appears to be using custom or proprietary implementations that have not had sufficient public review and approval, then this is a significant concern.
Effectiveness: High
Manual Analysis
Analyze the product to ensure that implementations for each primitive do not contain any known vulnerabilities and are not using any known-weak algorithms, including MD4, MD5, SHA1, DES, etc.
Effectiveness: Moderate
Dynamic Analysis with Manual Results Interpretation
For hardware, during the implementation (pre-Silicon / post-Silicon) phase, dynamic tests should be done to ensure that outputs from cryptographic routines are indeed working properly, such as test vectors provided by NIST [REF-1236].
Effectiveness: Moderate
Dynamic Analysis with Manual Results Interpretation
It needs to be determined if the output of a cryptographic primitive is lacking entropy, which is one clear sign that something went wrong with the crypto implementation. There exist many methods of measuring the entropy of a bytestream, from sophisticated ones (like calculating Shannon's entropy of a sequence of characters) to crude ones (by compressing it and comparing the size of the original bytestream vs. the compressed - a truly random byte stream should not be compressible and hence the uncompressed and compressed bytestreams should be nearly identical in size).
Effectiveness: Moderate
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
View - a subset of CWE entries that provides a way of examining CWE content. The two main view structures are Slices (flat lists) and Graphs (containing relationships between entries).
OWASP Top Ten 2025 Category A04:2025 - Cryptographic Failures
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Terminology
Terminology for cryptography varies widely, from informal and colloquial to mathematically-defined, with different precision and formalism depending on whether the stakeholder is a developer, cryptologist, etc. Yet there is a need for CWE to be self-consistent while remaining understandable and acceptable to multiple audiences.
As of CWE 4.6, CWE terminology around "primitives" and "algorithms" is emerging as shown by the following example, subject to future consultation and agreement within the CWE and cryptography communities. Suppose one wishes to send encrypted data using a CLI tool such as OpenSSL. One might choose to use AES with a 256-bit key and require tamper protection (GCM mode, for instance). For compatibility's sake, one might also choose the ciphertext to be formatted to the PKCS#5 standard. In this case, the "cryptographic system" would be AES-256-GCM with PKCS#5 formatting. The "cryptographic function" would be AES-256 in the GCM mode of operation, and the "algorithm" would be AES. Colloquially, one would say that AES (and sometimes AES-256) is the "cryptographic primitive," because it is the algorithm that realizes the concept of symmetric encryption (without modes of operation or other protocol related modifications). In practice, developers and architects typically refer to base cryptographic algorithms (AES, SHA, etc.) as cryptographic primitives.
Maintenance
Since CWE 4.4, various cryptography-related entries, including CWE-327 and CWE-1240, have been slated for extensive research, analysis, and community consultation to define consistent terminology, improve relationships, and reduce overlap or duplication. As of CWE 4.6, this work is still ongoing.
CWE-1241: Use of Predictable Algorithm in Random Number Generator
Weakness ID: 1241
Vulnerability Mapping:ALLOWEDThis CWE ID may be used to map to real-world vulnerabilities Abstraction:
BaseBase - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
View customized information:
Shows the description and diagram, platforms, mitigations, consequences, relationships, memberships, and content history.For users who are interested in more notional aspects of a weakness. Example: educators, technical writers, and project/program managers.For users who are concerned with the practical application and details about the nature of a weakness and how to prevent it from happening. Example: tool developers, security researchers, pen-testers, incident response analysts.For users who are mapping an issue to CWE/CAPEC IDs, i.e., finding the most appropriate CWE for a specific issue (e.g., a CVE record). Example: tool developers, security researchers.For users who wish to see all available information for the CWE/CAPEC entry.For users who want to customize what details are displayed.
×
Edit Custom Filter
More information is available — Please edit the custom filter or select a different filter.
Description
The device uses an algorithm that is predictable and generates a pseudo-random number.
Extended Description
Pseudo-random number generator algorithms are predictable because their registers have a finite number of possible states, which eventually lead to repeating patterns. As a result, pseudo-random number generators (PRNGs) can compromise their randomness or expose their internal state to various attacks, such as reverse engineering or tampering.
Common Consequences
This table specifies different individual consequences
associated with the weakness. The Scope identifies the application security area that is
violated, while the Impact describes the negative technical impact that arises if an
adversary succeeds in exploiting this weakness. The Likelihood provides information about
how likely the specific consequence is expected to be seen relative to the other
consequences in the list. For example, there may be high likelihood that a weakness will be
exploited to achieve a certain impact, but a low likelihood that it will be exploited to
achieve a different impact.
Impact
Details
Read Application Data
Scope: ConfidentialityLikelihood: High
Potential Mitigations
Phase(s)
Mitigation
Architecture and Design; Implementation
It is highly recommended to use a true random number generator (TRNG) to ensure the security of encryption schemes. Hardware-based TRNGs generate unpredictable, unbiased, and independent random numbers because they employ physical phenomena, e.g., electrical noise, as sources to generate random numbers.
Relationships
This table shows the weaknesses and high level categories that are related to this
weakness. These relationships are defined as ChildOf, ParentOf, MemberOf and give insight to
similar items that may exist at higher and lower levels of abstraction. In addition,
relationships such as PeerOf, Overlaps, and CanAlsoBe are defined to show similar weaknesses that the user
may want to explore.
Relevant to the view "Complete Weakness Hierarchy" (View-1000)
Nature
Type
ID
Name
ChildOf
Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
The different Modes of Introduction provide information
about how and when this
weakness may be introduced. The Phase identifies a point in the life cycle at which
introduction
may occur, while the Note provides a typical scenario related to introduction during the
given
phase.
Phase(s)
Note
Architecture and Design
Implementation
In many cases, the design originally defines a cryptographically secure random number generator, but is then changed during implementation due to unforeseen constraints.
Applicable Platforms
This listing shows possible areas for which the given
weakness could appear. These
may be for specific named Languages, Operating Systems, Architectures, Paradigms,
Technologies,
or a class of such platforms. The platform is listed along with how frequently the given
weakness appears for that instance.
Type
Applicable Platforms
Notes
Technologies
Class: System on Chip
(Undetermined Prevalence)
Demonstrative Examples
Example 1
Suppose a cryptographic function expects random value to be supplied for the crypto algorithm.
During the implementation phase, due to space constraint, a cryptographically secure random-number-generator could not be used, and instead of using a TRNG (True Random Number Generator), a LFSR (Linear Feedback Shift Register) is used to generate a random value. While an LFSR will provide a pseudo-random number, its entropy (measure of randomness) is insufficient for a cryptographic algorithm.
Example 2
The example code is taken from the PRNG inside the buggy OpenPiton SoC of HACK@DAC'21 [REF-1370]. The SoC implements a pseudo-random number generator using a Linear Feedback Shift Register (LFSR).
An example of LFSR with the polynomial function P(x) = x6+x4+x3+1 is shown in the figure.
A LFSR's input bit is determined by the output of a linear function of two or more of its previous states. Therefore, given a long cycle, a LFSR-based PRNG will enter a repeating cycle, which is predictable.
Selected Observed
Examples
Note: this is a curated list of examples for users to understand the variety of ways in which this
weakness can be introduced. It is not a complete list of all CVEs that are related to this CWE entry.
PHP framework uses mt_rand() function (Marsenne Twister) when generating tokens
Weakness Ordinalities
Ordinality
Description
Primary
(where the weakness exists independent of other weaknesses)
Memberships
This MemberOf Relationships table shows additional CWE Categories and Views that
reference this weakness as a member. This information is often useful in understanding where a
weakness fits within the context of external information sources.
Nature
Type
ID
Name
MemberOf
Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
OWASP Top Ten 2025 Category A04:2025 - Cryptographic Failures
Vulnerability Mapping Notes
Usage
ALLOWED
(this CWE ID may be used to map to real-world vulnerabilities)
Reason
Acceptable-Use
Rationale
This CWE entry is at the Base level of abstraction, which is a preferred level of abstraction for mapping to the root causes of vulnerabilities.
Comments
Carefully read both the name and description to ensure that this mapping is an appropriate fit. Do not try to 'force' a mapping to a lower-level Base/Variant simply to comply with this preferred level of abstraction.
Notes
Maintenance
As of CWE 4.5, terminology related to randomness, entropy, and
predictability can vary widely. Within the developer and other
communities, "randomness" is used heavily. However, within
cryptography, "entropy" is distinct, typically implied as a
measurement. There are no commonly-used definitions, even within
standards documents and cryptography papers. Future versions of
CWE will attempt to define these terms and, if necessary,
distinguish between them in ways that are appropriate for
different communities but do not reduce the usability of CWE for
mapping, understanding, or other scenarios.


 Objective

 Grouping - a CWE entry that contains a set of other entries that share a common characteristic.
Manufacturing and Life Cycle Management Concerns
- (1195)

 Class - a weakness that is described in a very abstract fashion, typically independent of any specific language or technology. More specific than a Pillar Weakness, but more general than a Base Weakness. Class level weaknesses typically describe issues in terms of 1 or 2 of the following dimensions: behavior, property, and resource.
Insufficient Technical Documentation
- (1059)
 Base - a weakness that is still mostly independent of a resource or technology, but with sufficient details to provide specific methods for detection and prevention. Base level weaknesses typically describe issues in terms of 2 or 3 of the following dimensions: behavior, property, technology, language, and resource.
Semiconductor Defects in Hardware Logic with Security-Sensitive Implications
- (1248)
 Variant - a weakness that is linked to a certain type of product, typically involving a specific language or technology. More specific than a Base weakness. Variant level weaknesses typically describe issues in terms of 3 to 5 of the following dimensions: behavior, property, technology, language, and resource.
Insufficient Granularity of Address Regions Protected by Register Locks
- (1222)
 The Dimensions table provides information about the
different dimensions associated with this weakness. The Type identifies the dimension type,
while the Value provides the specific value for that dimension.